 jsa2/caoptics
CA Optics - Azure AD 조건부 액세스 격차 분석기

개발 우선순위 변경과 커뮤니티 활동을 다른 영역(PoC, 기타 도구, 데모/발표)으로 재조정함에 따라 프로젝트가 보관 처리되었으며, 프로젝트는 읽기 전용으로 설정되었습니다.
Azure AD Conditional Access Gap Analyzer는 복잡한 Azure Active Directory Conditional Access 정책 구성 내에 존재할 수 있는 갭을 스캔하는 솔루션입니다.
Conditional Access가 처음이라면 다음 Microsoft 문서를 검토할 것을 권장합니다: https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/overview
이 도구를 실행하는 한 줄 명령: (이 부분만 읽을 계획이고 설치를 완료한 경우)
node ./ca/main.js --mapping --skipObjectId=259fcf40-ff7c-4625-9b78-cd11793f161f --clearPolicyCache --clearTokenCache --clearMappingCache
사전 요구 사항을 완료하고 이 readme 파일을 읽은 후 다음 사항을 고려하세요:
reportOnly 정책은 종료(terminating) 정책으로 간주되지 않습니다:
참조: scope
각 스캔을 --clearPolicyCache와 함께 실행하세요
정책과 관련된 그룹/사용자에 변경이 있는 경우 각 스캔을 --clearMappingCache와 함께 실행하세요
사용자와 앱을 대상으로 하는 정책만 범위에 포함됩니다(가장 일반적인 범위이지만, 예를 들어 보안 등록 정책은 평가되지 않는다는 의미입니다)
참조: scope
도구 작동 방식에 대한 경험을 쌓고 기대치를 설정할 수 있도록 테스트 환경에서 시작하세요
정책에서 제외된 알려진 그룹이나 사용자가 있다면, 제외를 확인하려는 것이 아닌 한 --skipObjectIds로 스캔에서 제외할 객체를 정의하세요
여러 환경에서 스캔을 실행하는 경우, 새 스캔을 실행하기 전에 로그인과 캐시가 제거되었는지 확인하세요
참조:매개변수
az account clear로 AZ CLI 캐시를 지운 후 az login으로 스캔하려는 환경에 새로 로그인하세요기타 중요한 참고 사항을 참조하세요
Release notes: 0.7.1
- Updated depedencies and report text outputs
Release notes: 0.7
- Uses beta endpoint now by default, --expand option now expands the results to report regardless of the use of --allTerminations
Release notes: 0.6.9
- using --expand=9c06d103-f5b0-4404-bb25-aec4636912cd,47087cd3-64e9-470b-980a-5662f498e016 and expand 10 group members to for separate inspection.
Release notes: 0.6.8
- When you update policy with any guest conditions in GUI that policy will be only available from the beta endpoint after the update (during preview).
- This update brings normalization for policies that are transfered to beta endpoint due to this behavior.
- The policy will be evaluated like the previous guest conditions, as long as the following conditions are included "internalGuest,b2bCollaborationGuest,b2bCollaborationMember" and no tenants are excluded from the policy. In order to evaluate transferred policies,
- use '--allowPreviewPolicies' when running CaOptics to account for this behavior

Release notes: 0.6.6-7 beta
- Allow use of different login endpoints for login and graph with params: --altLogin --altGraph
- Allow use of custom filtering for policies (this only recommended, when the policies do not adhere to expected schema)

Release notes: 0.6.5 beta
- Added counter to reporting when high number of permutations is also added to report (default is to add only unterminated)
- Minor code fixes changing <var> to <let>
- Report filename now includes day, month, year and tenantId e.g. report_day_4_month_9_year_2022-tenant_48f55450-183a-45d6-a9ce-68f3cbc68947.csv

Release notes: 0.6.4 beta
- Get more groups per single call (less batching)
- Fix race condition detected when generally using for await loops
- Enclose values with "" between delimitters (CSV)

Release notes: 0.6.3 beta
- Optimizations to way the mapped objects are handled.
  - Mapped objects are cached. You can recreate the object mapping by using parama 'clearMappingCache'
  - Lookup keys will start from 'user/group/role' conditions always first
  - Added possibility to populate usermap with random UUID's to test for performance impact (this just debug option, and not really something that would be in non-beta versions)

Release notes: 0.6.2 beta
- Separated cache params into separate functions -> (clearTokenCache and ClearPolicyCache)
- Added possibility of running pre-optimized algorithm on permutations with param --aggressive (High memory consumption, only here for A/B testing)
- merge completed.

Release notes: 0.6.1 beta
- Basic version of CSV reporting added
- Streamlined permutation generation to ensure essential permutations are generated, and some permutations are are terminated earlier on the lookups

Release notes: 0.6 beta (first non "silent" release)
- App displayNames added to MD report. Object type added to the user type

Release notes: 0.5.2,0.5.1,0.5 beta  (see previous branches for release notes)
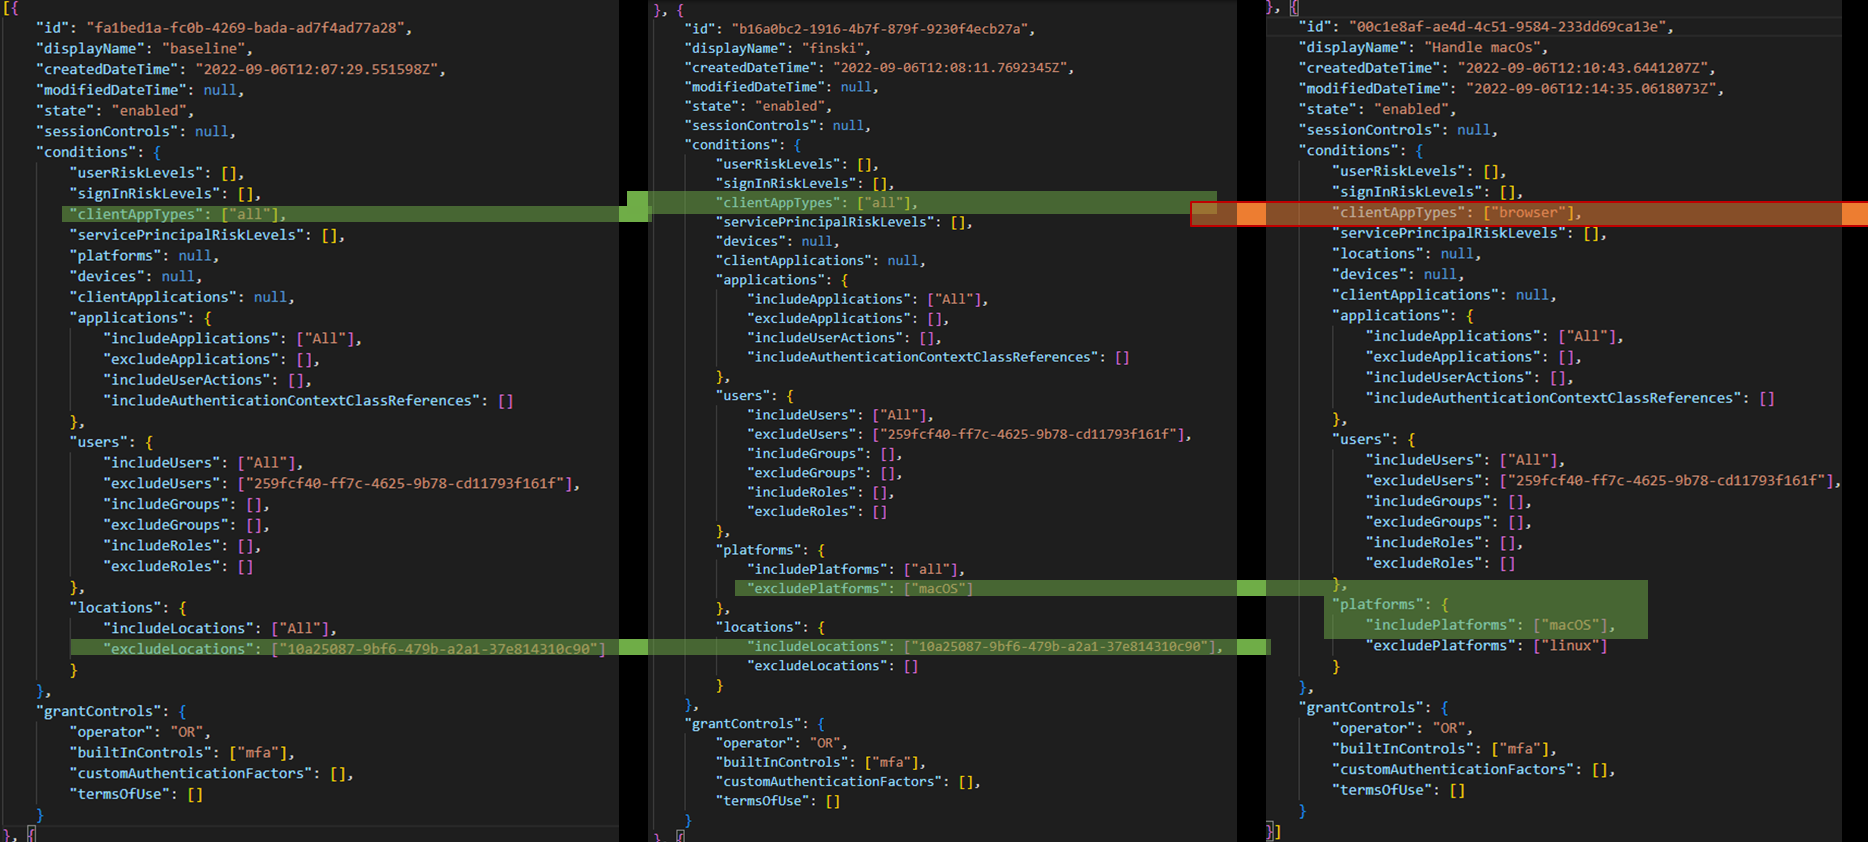
정책 간 탐지 예시
❌ 값이 0인 순열은 해당 특정 조건 조합에 대해 종료된 정책이 없음을 의미합니다.
| 정책 | 종료 | 조회 |
|---|---|---|
| All | 0 | Applications:88cc92be-d474-4d95-a57d-7b3ef701f510 -> Locations:finland -> users:GuestsOrExternalUsers |
| All | 0 | Applications:88cc92be-d474-4d95-a57d-7b3ef701f510 -> Locations:finland -> users:Jane Doe |
| All | 0 | Applications:88cc92be-d474-4d95-a57d-7b3ef701f510 -> Locations:finland -> users:John Doe |
✅ 탐지에 대한 자세한 설명은 docs/example.md에서 참조하세요.
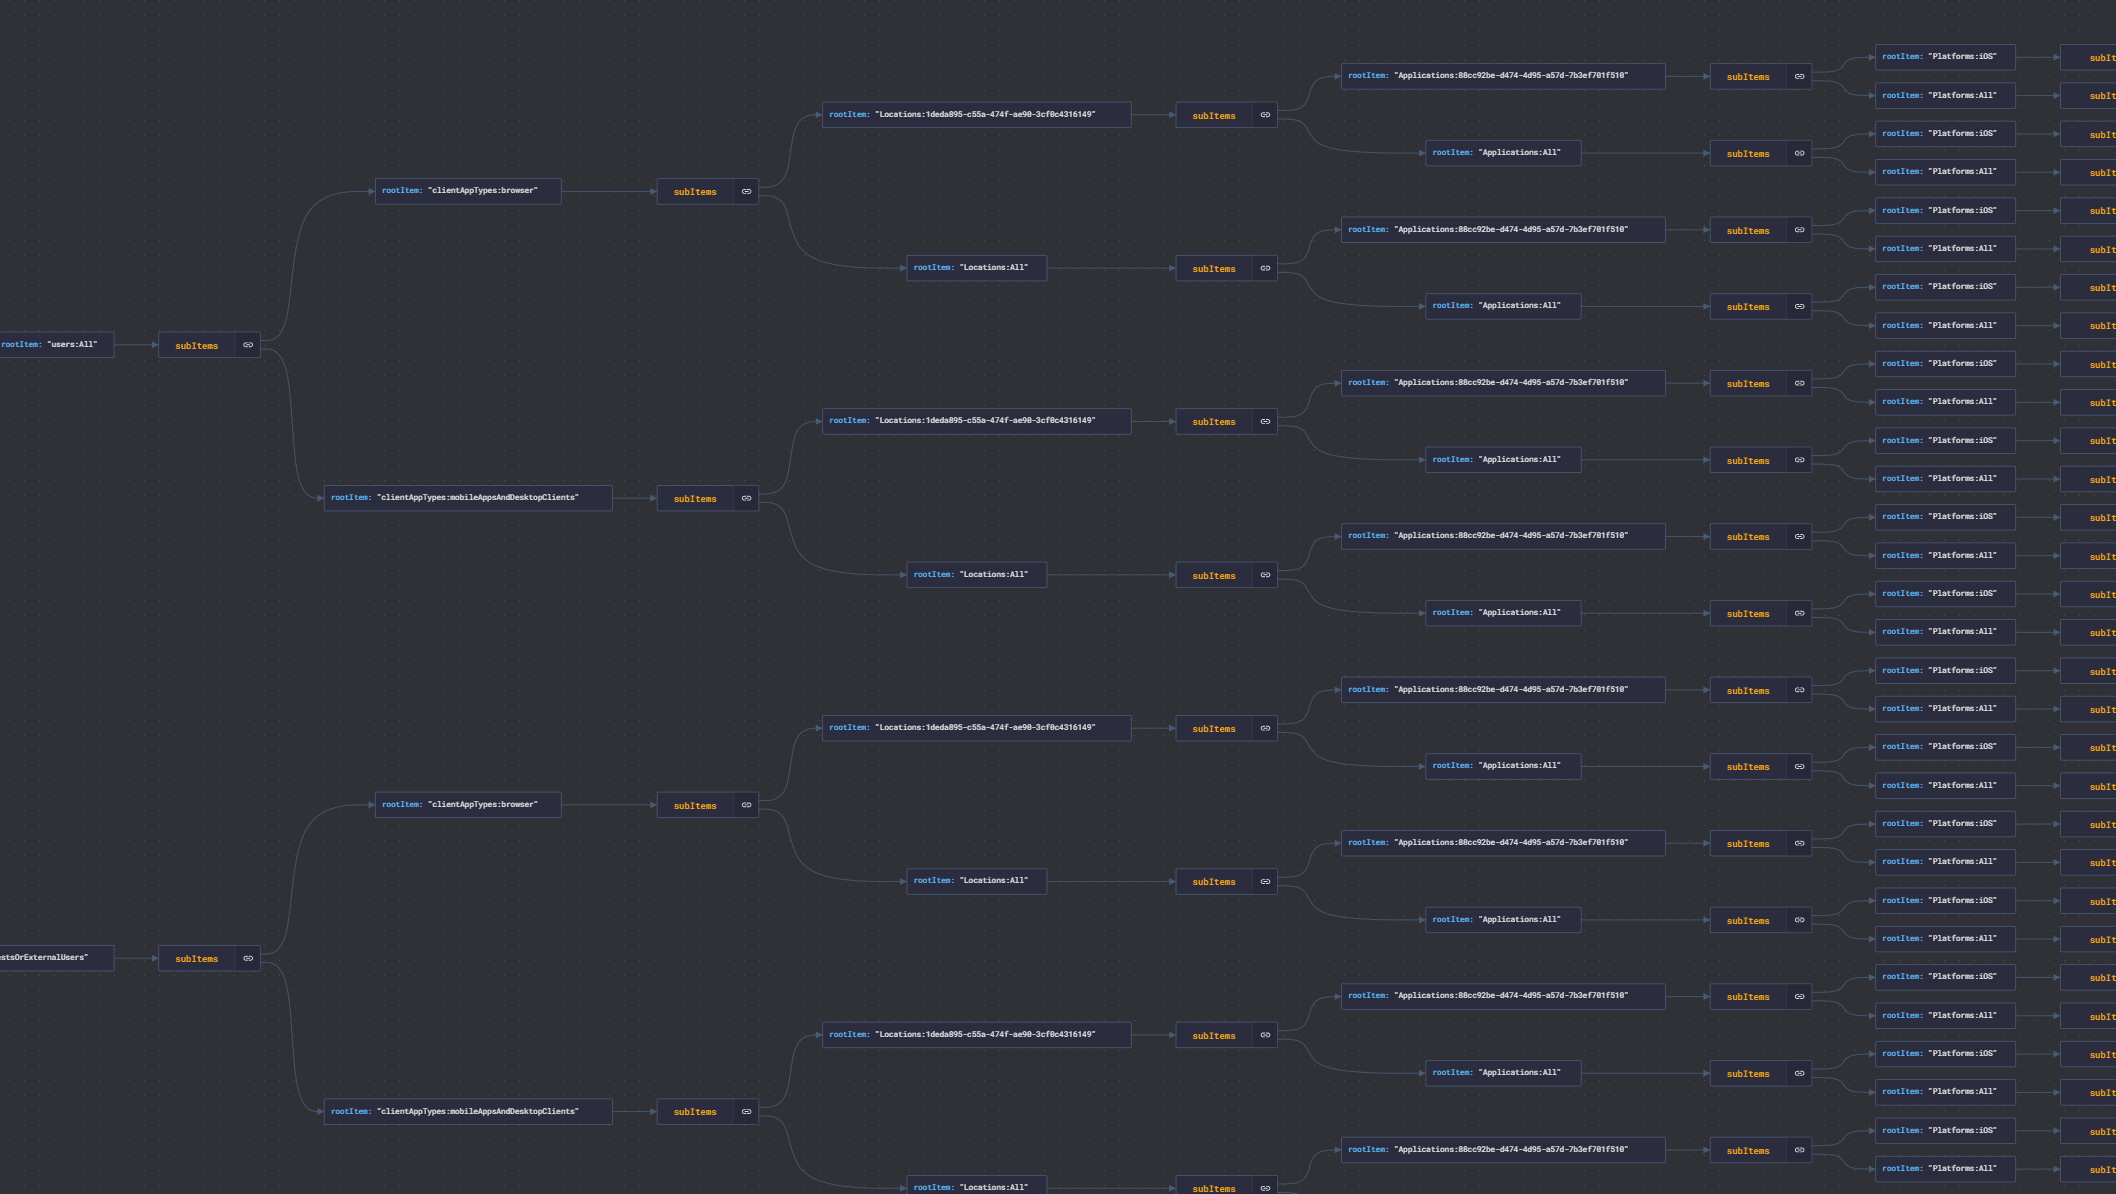
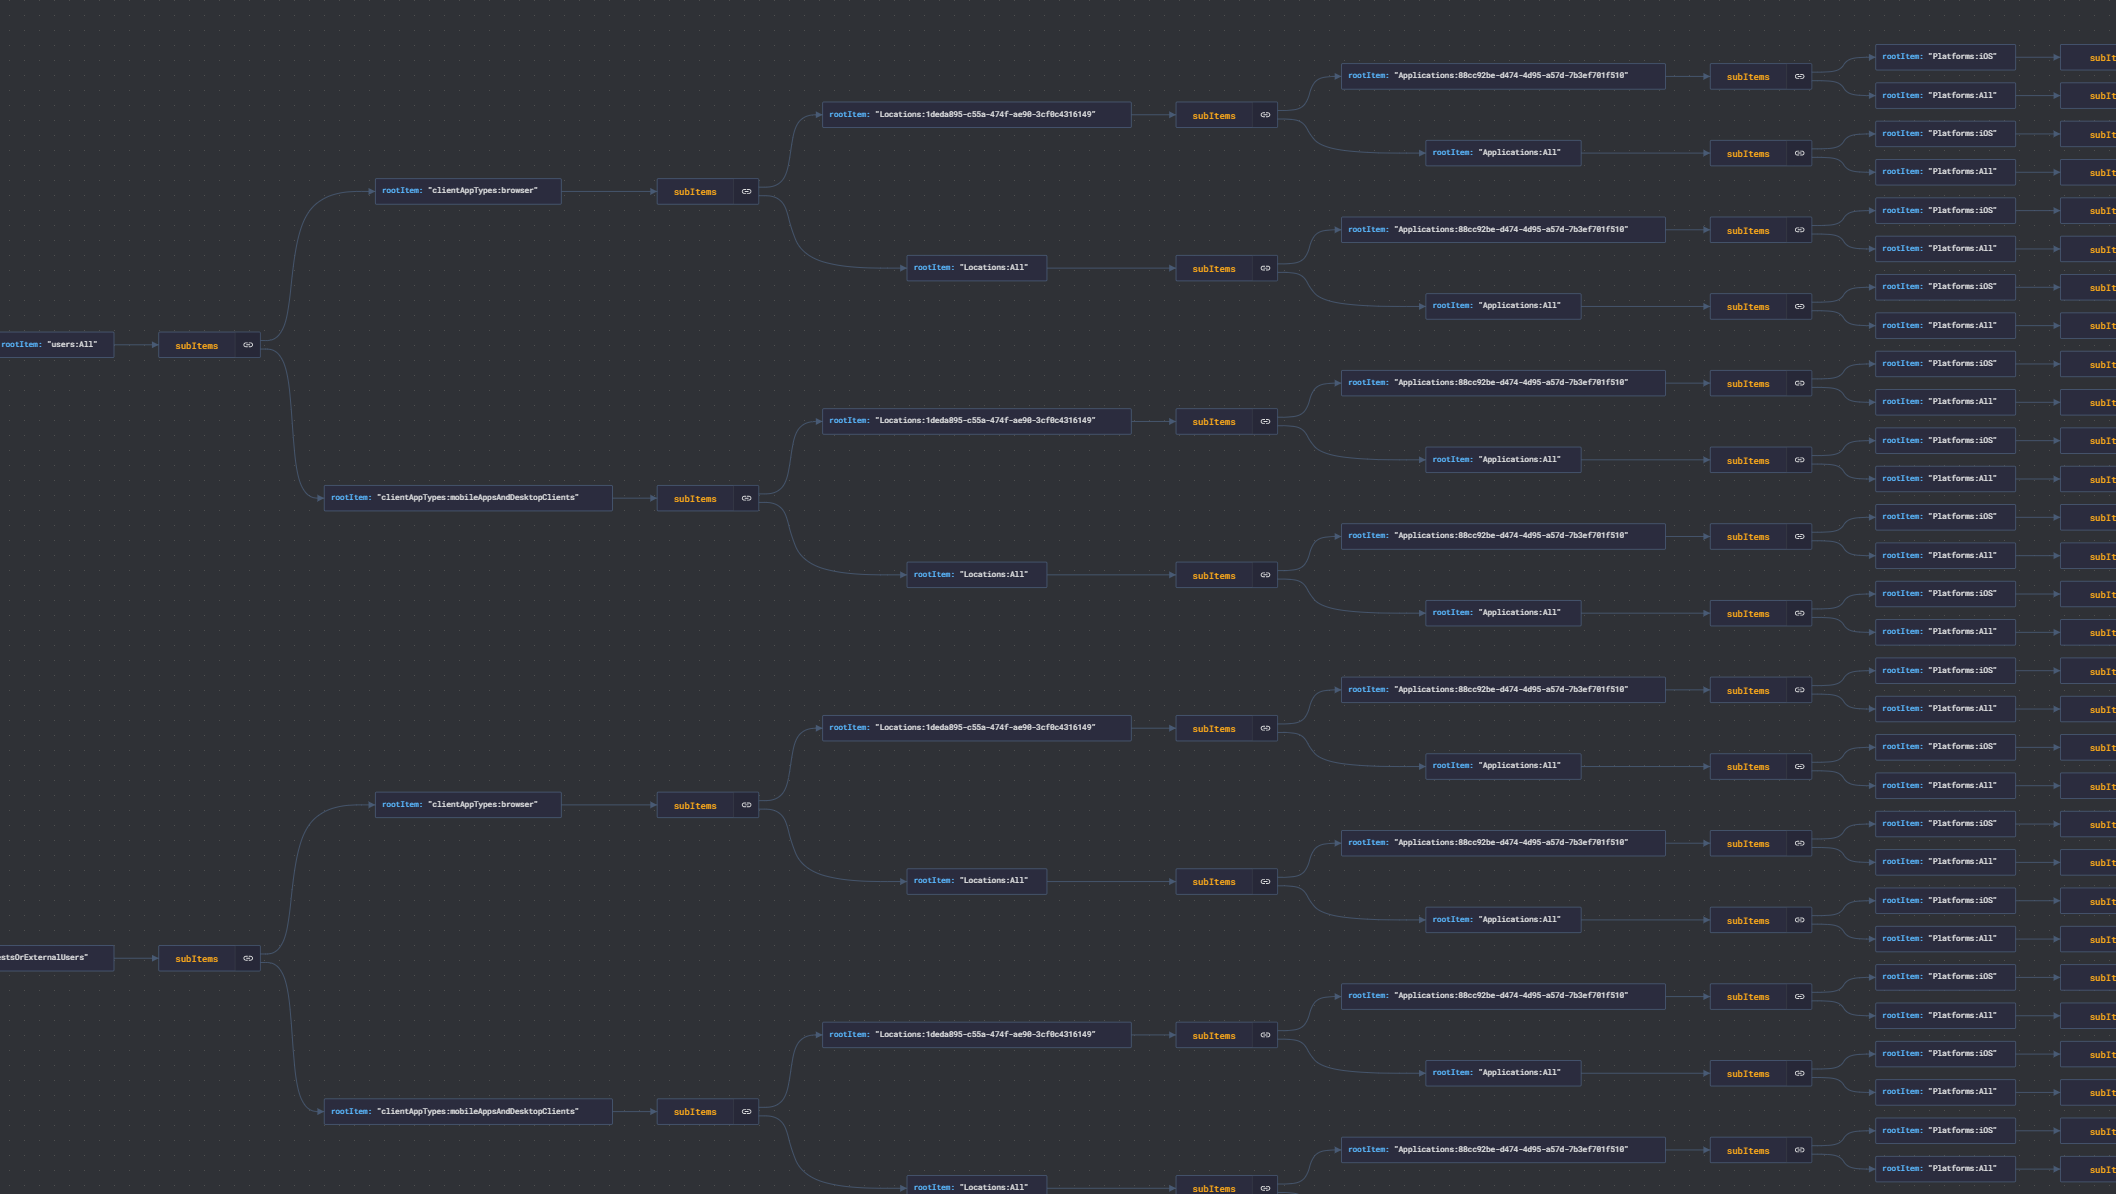
순열은 getPol2.js에 의해 생성됩니다.
순열은 JSON Crack 서비스로 시각화할 수 있습니다:
(시각화: https://jsoncrack.com/)
런타임