 happy0717/cve-2023-27704
Void Tools Everything 1.4.1.1022 미만 버전의 ReDoS 취약점인 CVE-2023-27704에 대한 문서 및 개념 증명(PoC)으로, 재현 단계와 수정 참조가 포함되어 있습니다.

CVE-2023-27704 Void Tools Everything lower than v1.4.1.1022 was discovered to contain a Regular Expression Denial of Service (ReDoS)
fix at Everything 1.5 alpha
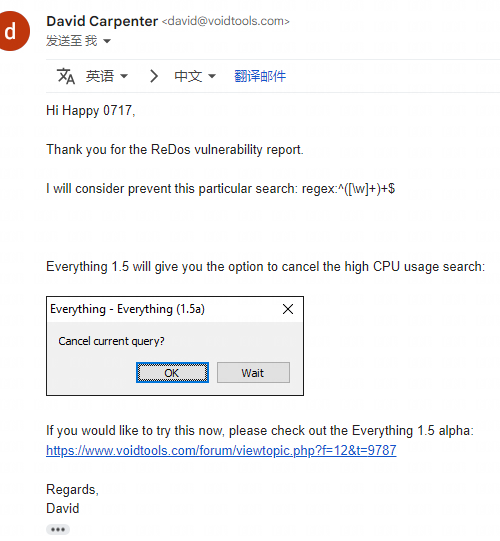
[Suggested description] Void Tools Everything lower than v1.4.1.1022 was discovered to contain a Regular Expression Denial of Service (ReDoS).
[Additional Information] 자세한 재현 과정은 이 링크에 있습니다: https://drive.google.com/drive/folders/1BmHAGSugrFo0whDEmg6nnbaOkvE21X-p?usp=sharing
[VulnerabilityType Other] Regular expression Denial of Service
[Vendor of Product] https://www.voidtools.com/
[Affected Product Code Base] Everything - lower than 1.4.1.1022 (x64)
[Affected Component] Everything installed version lower than 1.4.1.1022 (x64)
[Attack Type] Local
[Impact Denial of Service] true
[Attack Vectors] I discovered a ReDos vulnerability in everything Version 1.4.1.1015 (x64)
ReDos 취약점 트리거는 대략 다음과 같습니다: "^([\w]+)+$"
재현 과정:
그러면 작업 관리자에서 CPU 사용량이 매우 높아져 90% 이상에 도달하고 Everything이 응답하지 않게 됩니다.
자세한 재현 과정은 이 링크에 있습니다: https://drive.google.com/drive/folders/1BmHAGSugrFo0whDEmg6nnbaOkvE21X-p?usp=sharing
[Reference] https://drive.google.com/drive/folders/1BmHAGSugrFo0whDEmg6nnbaOkvE21X-p?usp=sharing https://www.voidtools.com/en-us/downloads/
[Discoverer] happy0717
