 hahwul/urx
OSINT 아카이브에서 URL을 추출하여 보안 인사이트를 제공합니다

보안 인사이트를 위해 OSINT 아카이브에서 URL을 추출합니다.



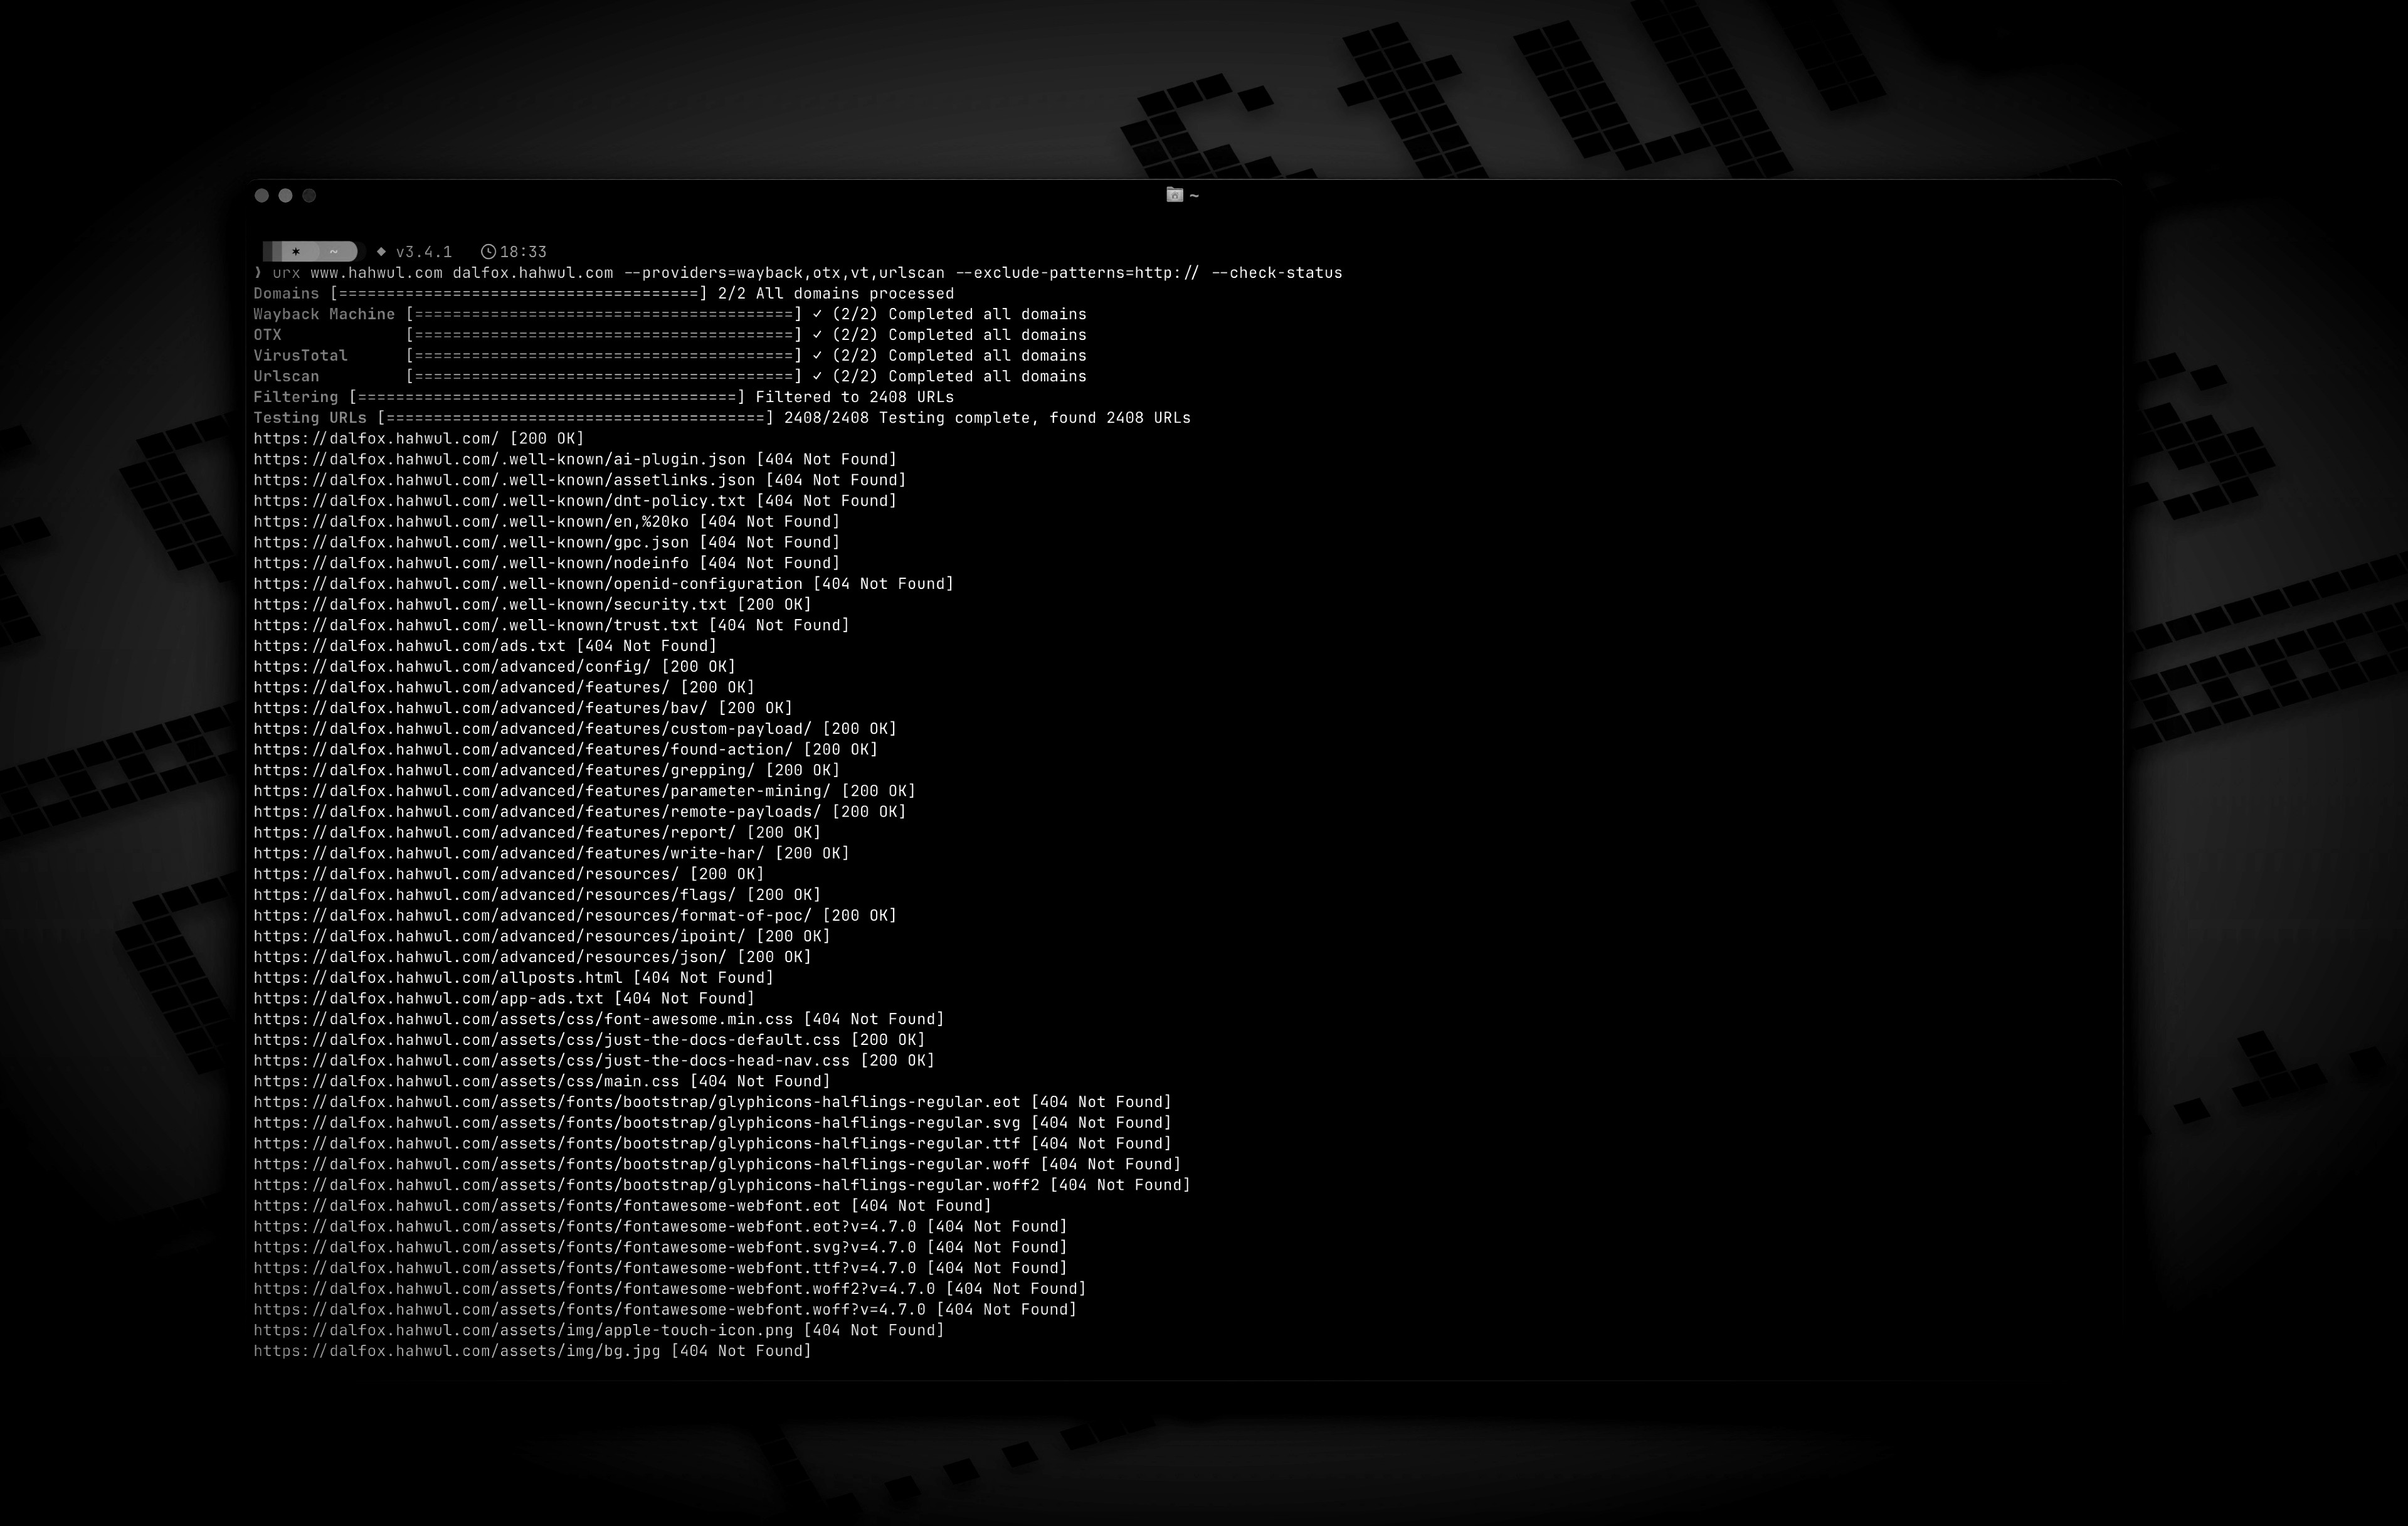
Urx는 Wayback Machine과 Common Crawl 같은 OSINT 아카이브에서 도메인의 URL을 수집합니다. 모든 소스를 병렬로 쿼리한 다음, 보안 작업을 위해 결과를 필터링, 테스트, 포맷합니다.
--cdx-endpoint를 통한 기타 모든 CDX 서버 (pywb, OutbackCDX, 국립 아카이브)--from/--to, --archive-status, --archive-mime)는 CDX 쿼리 내부에서 실행됨--meta-*): 캡처 날짜, MIME 타입, 상태urx example.com/shop) 및 버그 바운티 스코프 파일 (--scope-file)--match-regex, --filter-regex) 및 프리셋 (no-images, only-js, only-secrets, only-backup, only-config, only-api, only-tokens)을 통한 필터링, 그리고 설정 파일에 정의한 사용자 지정 프리셋--normalize-url, --merge-endpoint, --dedup-similarwordlist 형식으로 출력; --stream은 URL이 도착하는 대로 기록--params, --params-by-endpoint, --fuzz-placeholder FUZZfirst_seen, last_seen, mime, archive_status, digest--files) 또는 stdin으로부터의 입력--check-status, --check-title, --extract-links, --extract-js-endpoints--archive-body는 더 이상 존재하지 않는 페이지에서 링크를 마이닝하며, 고유 본문당 한 번의 요청을 수행하고 --archive-body-dir는 이를 보관함--expand-specs): OpenAPI 3.x, Swagger 2.0, GraphQL 인트로스펙션--archived-discovery)-H, --cookie, --user-agent), 아카이브에는 절대 전송되지 않음--features redis-cache 빌드 필요), --incremental 스캔, urx cache 유지보수, --notify 웹훅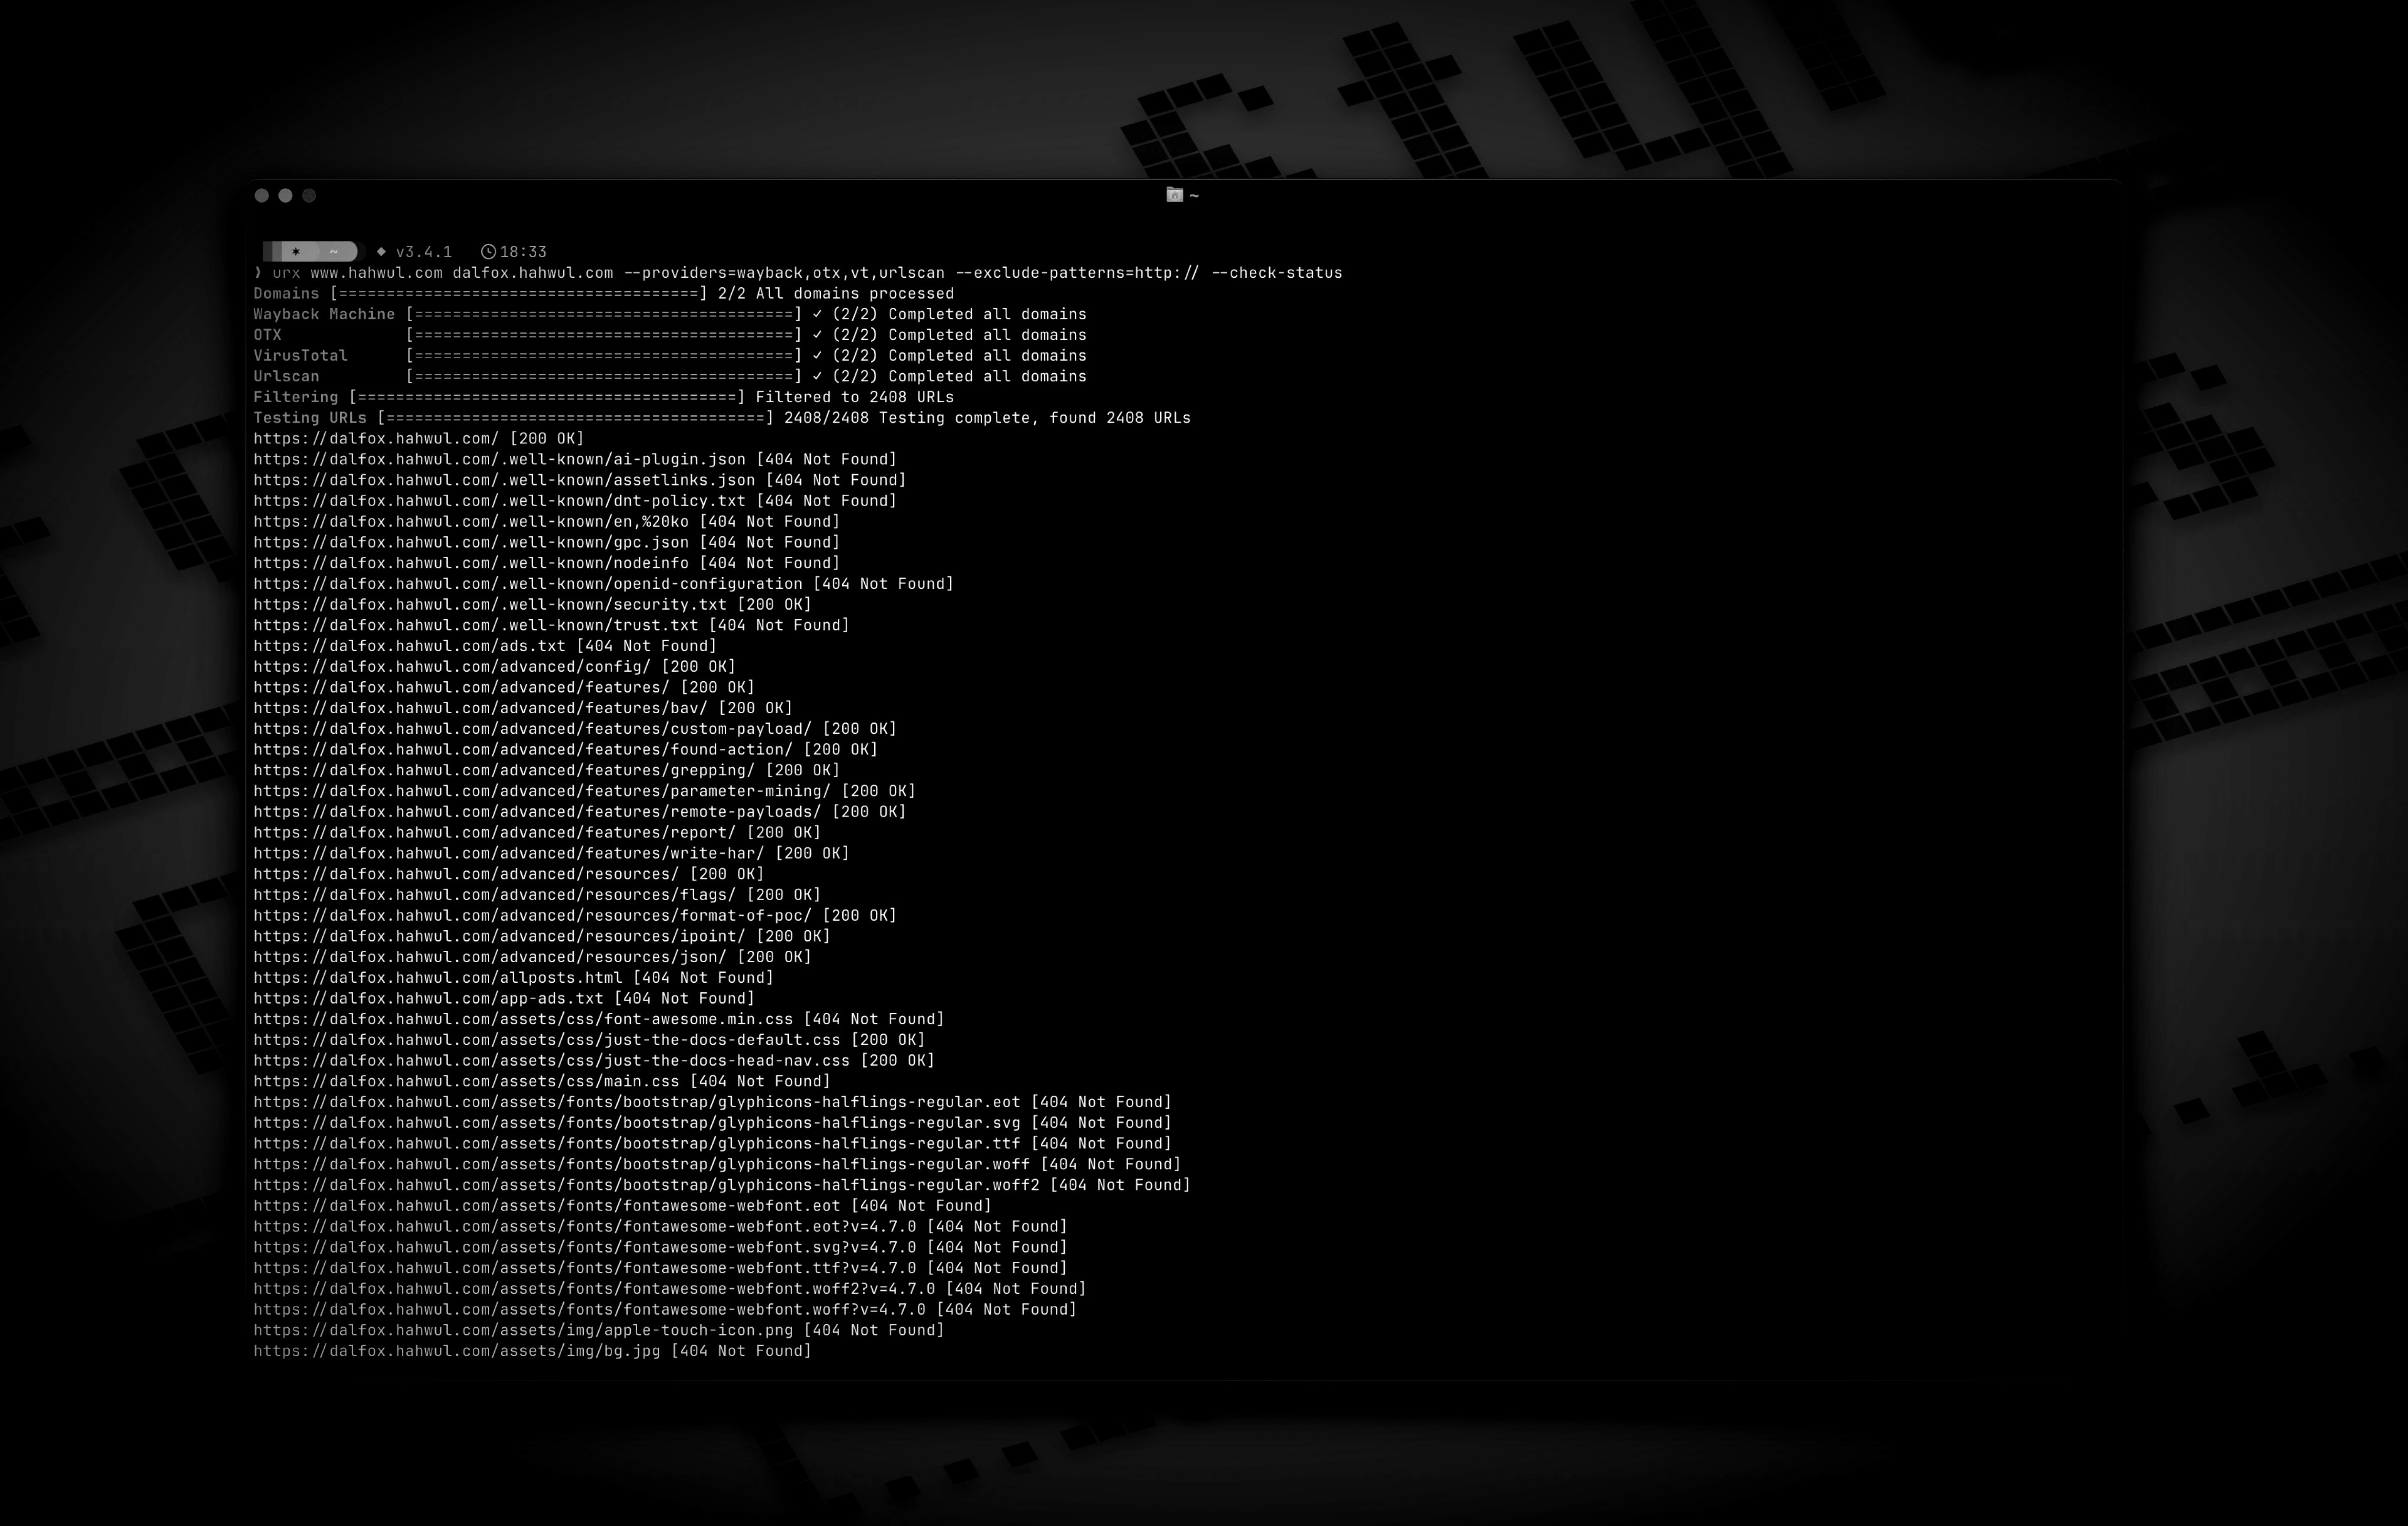
cargo install urx       # https://crates.io/crates/urx
brew install urx        # https://formulae.brew.sh/formula/urx
yay -S urx              # AUR
choco install urx       # Chocolatey (Windows)
소스에서 (target/release/urx의 바이너리):
git clone https://github.com/hahwul/urx.git
cd urx
cargo build --release
Docker(ghcr.io/hahwul/urx). 이미지에는 엔트리포인트가 없으므로 이미지 이름 뒤에 ./urx를 붙입니다:
docker run --rm ghcr.io/hahwul/urx:latest ./urx example.com
Linux, macOS 및 Windows용 사전 빌드된 바이너리는 각각 .sha256과 함께 릴리스 페이지에서 제공됩니다.
셸 자동 완성(bash, zsh, fish, powershell, elvish) 및 man 페이지:
urx --completions zsh > ~/.zfunc/_urx        # ~/.zfunc must be on $fpath
urx --completions bash > ~/.local/share/bash-completion/completions/urx
urx --completions fish > ~/.config/fish/completions/urx.fish
urx --manpage > ~/.local/share/man/man1/urx.1
urx example.com                 # one domain
urx example.com example.org     # several domains
cat domains.txt | urx           # domains from stdin
Usage: urx [OPTIONS] [DOMAINS]... [COMMAND]

Commands:
  cache  Inspect and maintain the URL cache: stats, list, prune, drop <DOMAIN>..., clear

Arguments:
  [DOMAINS]...  Domains to fetch URLs for

Options:
  -c, --config <CONFIG>           Config file to load
      --provider-config <PATH>    Separate provider config file holding only API keys (default: ~/.config/urx/provider-config.toml; %APPDATA%\urx\ on Windows). CLI/env > provider-config > main config.
      --completions <SHELL>       Print a shell completion script (bash, zsh, fish, powershell, elvish) to stdout and exit
      --manpage                   Print the roff man page to stdout and exit
  -h, --help             Print help
  -V, --version          Print version

Input Options:
      --files <FILES>...        Read URLs directly from files (supports WARC, URLTeam compressed, and text files)
      --domain-list <PATH>      File of newline-separated domains to scan (repeatable; merged with positional DOMAINS; stdin is read only when they name no domains; `#` comments allowed) [alias: --dL]

Output Options:
  -o, --output <OUTPUT>          Output file to write results
      --output-dir <PATH>        Write one file per URL host into this directory (extension matches --format). Coexists with --output / stdout. [alias: --oD]
  -f, --format <FORMAT>          Output format: "plain", "json" (one array), "jsonl" (one JSON object per line), "csv", "wordlist" (path segments and parameter names, deduplicated and sorted); anything else is a usage error [default: plain]
      --stream           Write URLs as each provider reports them instead of once at the end (unsorted; bypasses cache; rejects options needing the full result set)
      --merge-endpoint   Merge endpoints with the same path and merge URL parameters
      --normalize-url    Normalize URLs for better deduplication (sorts query parameters, removes trailing slashes)
      --dedup-similar    Collapse URLs that differ only in variable data (numeric ids, UUIDs, hashes, dates, query values)
      --params           Replace the URL list with every query parameter name the run saw, once each
      --params-by-endpoint
                         One line per endpoint: the endpoint and the comma-separated union of the parameter names seen on it (id-looking path segments collapse to `{id}`)
      --fuzz-placeholder <VALUE>
                         Replace every query parameter value with VALUE, keeping one URL per parameter signature — output you can feed straight to ffuf or dalfox






