
 dozermx/argus
도메인, IP, ASN, 클라우드 자산, CVE를 CVSS 점수 및 규정 준수 매핑과 함께 지식 그래프로 매핑하는 다단계 정찰 및 공격 표면 스캐너입니다.





보안 인텔리전스 프레임워크
Argus는 전문적인 침투 테스트와 공격 표면 평가를 위해 구축된 다단계 보안 정찰 및 분석 프레임워크입니다. 완전 자동으로 작동합니다 — API 키가 필요 없고, 외부 서비스가 필요 없으며, 계정도 필요 없습니다. 단일 명령으로 조직의 외부 노출에 대한 완전한 그림을 생성합니다.
argus/
├── sources/          Certificate Transparency, passive DNS, brute force
├── correlators/      DNS resolution, CDN bypass, port scanning
├── intelligence/     43 analysis modules
│   ├── Core          TLS, HTTP, email, content discovery, JS secrets
│   ├── Graph         Attack paths, compliance, CVE, anomaly detection
│   ├── Advanced      SSRF chains, OAuth/GraphQL/WebSocket, BGP, stealth
│   └── Intelligence  Deep CVE, API enumeration, cloud storage, threat intel
├── ontology/         Knowledge graph (NetworkX), entity model, pivot engine
├── output/           HTML report, executive report, CSV, JSON, terminal
└── web/              FastAPI real-time dashboard with WebSocket
엔진은 발견된 모든 엔티티(도메인, IP, 인증서, 조직, 기술, 열린 포트)와 그 관계를 연결하는 Knowledge Graph(지식 그래프) 를 구축합니다. 모든 발견 사항은 CVSS 3.1 점수, 공격 경로 연결 및 규정 준수 매핑이 포함된 그래프 노드에 연결된 이상 징후입니다.
| 범위 | 카테고리 | 세부 내용 |
|---|---|---|
| 1–9 | 정찰 | CT 로그 수집, 패시브 DNS, AXFR, 서브도메인 무차별 대입(2,500+ 단어 + 변형), DNS 해석, IPv6, ASN 인텔리전스, CDN 오리진 우회 |
| 10–17 | 표면 분석 | TLS 핑거프린팅, HTTP 헤더 분석, 콘텐츠 발견(100+ 경로), JavaScript 시크릿 스캐닝, 공급망 CVE, 캐시 포이즈닝, CORS, HTTP 스머글링 프로브 |
| 18–30 | 인텔리전스 | 이메일 보안(SPF/DMARC/DKIM), Wayback Machine, 역방향 IP, JARM C2 핑거프린팅, 이상 징후 탐지, CVSS 3.1 점수 산정, 공격 경로 합성, 규정 준수 매핑(OWASP/GDPR/ISO 27001/NIST/PCI-DSS), CVE 연관 분석, 그래프 분석, 스캔 차이 비교 |
| 31–35 | 능동 테스트 | HTTP 요청 스머글링(CL.TE/TE.CL/TE.TE), 조직 간 연관 분석, GNN 서브도메인 예측, 인증 분석(폼/JWT/Basic Auth), 파라미터 퍼징(SQLi/XSS/SSRF/IDOR/경로 탐색) |
| 36–39 | 고급 | BGP/AS 경로 + 클라우드 공급자 연관 분석, SSRF 체인 피보팅(클라우드 메타데이터, 내부 서비스, Gopher), OAuth/GraphQL/WebSocket 프로토콜 퍼징, 허니팟 탐지 |
| 40–43 | 인텔리전스+ | 딥 CVE 핑거프린팅(22개 기술), API/OpenAPI/Swagger 열거, 클라우드 스토리지 열거(S3/Azure/GCS/DO), 위협 인텔리전스(DNS 블랙리스트, Tor 종료 노드, ASN 평판) |
요구 사항: Python 3.9+, Linux/macOS/Termux
git clone https://github.com/DozerMx/Argus
cd Argus
pip install -r requirements.txt
웹 UI(선택 사항):
pip install fastapi uvicorn websockets
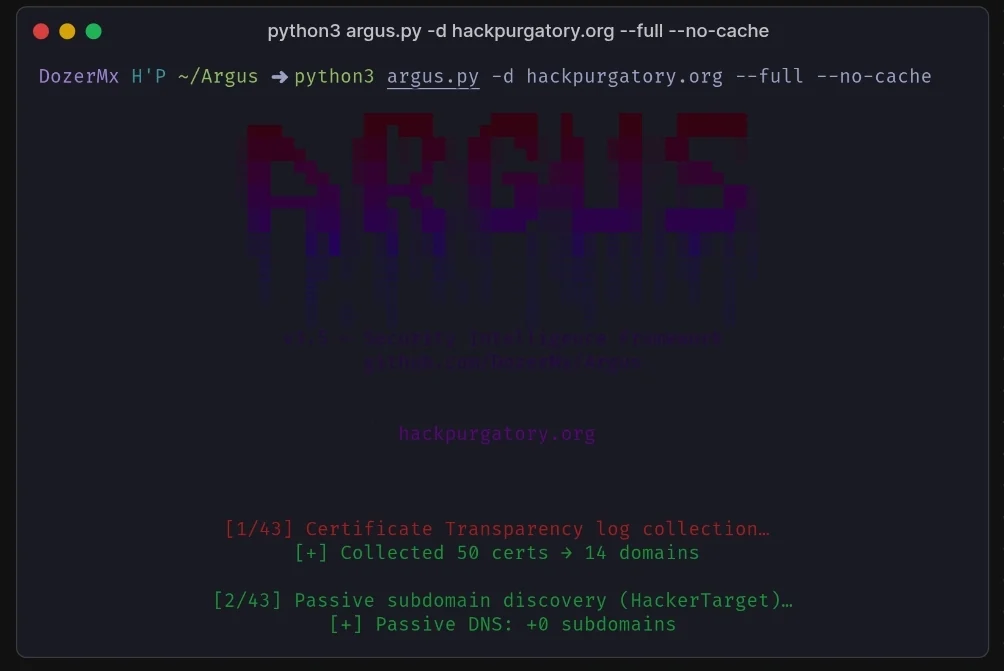
python argus.py -d TARGET [OPTIONS]
# CT log collection + DNS resolution + anomaly detection
python argus.py -d target.com

# Full 43-phase scan
python argus.py -d target.com --full

# Full scan with executive report
python argus.py -d target.com --full --output executive

# Full scan with authentication and fuzzing
python argus.py -d target.com --full --fuzz --auth

# Scan with known credentials
python argus.py -d target.com --full --auth --user admin --password admin123
# Subdomain brute force + AXFR
python argus.py -d target.com --brute --axfr

# Deep infrastructure: ASN + CDN bypass + ports
python argus.py -d target.com --deep --cdn-bypass --ports

# Stealth scan (paranoid jitter profile)
python argus.py -d target.com --full --stealth-profile paranoid

# Through Tor
python argus.py -d target.com --full --proxy socks5://127.0.0.1:9050
# Bulk scan from file
python argus.py -f targets.txt --full --output json

# Continuous monitoring with Slack alerts
python argus.py -d target.com --daemon --webhook https://hooks.slack.com/...

# Web UI dashboard
python argus.py --serve --ui-port 8080
Target:
  -d DOMAIN             Single target domain
  -f FILE               File with one domain per line

Scan Modules:
  --full                Enable all modules
  --deep                ASN, cloud detection, Wayback, reverse IP
  --brute               Subdomain brute force + permutations
  --axfr                DNS zone transfer
  --cdn-bypass          CDN/WAF origin IP discovery
  --ports               TCP port scan + banner grab (178 ports)
  --jarm                JARM TLS fingerprinting
  --fuzz                Parameter fuzzing (SQLi, XSS, SSRF, IDOR, traversal)
  --auth                Authentication analysis
  --user USER           Username for authenticated scanning
  --password PASS       Password for authenticated scanning

Output:
  --output FORMAT       terminal | html | executive | json | csv
  --outfile PATH        Output file path
  -v                    Verbose logging
  -q                    Quiet mode

Performance:
  --threads N           Concurrent threads (default: 30)
  --timeout N           Request timeout in seconds (default: 10)
  --proxy URL           Proxy (socks5://host:port or http://host:port)
  --no-cache            Disable disk cache
  --stealth-profile     paranoid | careful | normal | aggressive

Web UI:
  --serve               Launch real-time web dashboard
  --ui-port N           Web UI port (default: 8080)

Daemon:
  --daemon              Continuous monitoring mode
  --webhook URL         Webhook URL for alerts (Slack/Telegram)
  --interval N          Scan interval in hours (default: 6)
전체 인프라의 대화형 그래프 시각화와 함께 발견 사항, 위험 점수 및 관계 매핑을 제공합니다. 단일 자체 포함 파일입니다.
공격 경로 설명, 프레임워크별 규정 준수 위반 사항, 우선순위가 지정된 수정 로드맵 및 위험 매트릭스를 포함한 비즈니스 언어 요약입니다.
전체 지식 그래프, CVSS 점수가 포함된 모든 이상 징후, 공격 경로 및 스캔 메타데이터를 포함한 완전한 머신 판독 가능 출력입니다. SIEM, 티켓팅 시스템 또는 맞춤형 도구와의 통합에 적합합니다.
콘텐츠 발견
각 활성 도메인에 대해 100개 이상의 경로를 테스트합니다. .env 파일, Git 저장소, 관리자 패널, 백업 아카이브, 데이터베이스 덤프, Spring Actuator 엔드포인트, GraphQL 인터페이스 등을 탐지합니다. SPA/CDN catch-all 탐지를 포함합니다 — 모든 URL에 200으로 응답하는 호스트는 패턴 검증을 통해 올바르게 처리되어 오탐을 제거합니다.
퍼저 컨텍스트를 인식하는 파라미터 퍼징입니다. 페이로드를 선택하기 전에 파라미터 유형(숫자, 문자열, 경로, URL)을 추론합니다. SQLi(50개 페이로드, 오류 기반 및 시간 기반), XSS(39개 페이로드), SSRF(45개 페이로드, AWS/GCP/Azure 메타데이터 포함), 경로 탐색(33개 페이로드), 오픈 리다이렉트 및 IDOR을 테스트합니다. 3단계 우회를 지원하는 WAF 탐지를 포함합니다.
인증 로그인 폼을 발견하고, CSRF 토큰을 자동으로 추출하며, CAPTCHA를 감지하여 건너뜁니다. 공급업체 기본값, 침해로 유출된 비밀번호 및 도메인별 변형을 포함한 132가지 자격 증명 조합을 테스트합니다. 약한 시크릿에 대한 HMAC 무차별 대입을 통한 JWT 분석을 수행합니다. OAuth/SSO 엔드포인트 탐지를 포함합니다.
SSRF 체인 단일 엔드포인트 탐지를 넘어섭니다. 확인된 SSRF를 사용하여 피보팅합니다: AWS IAM 자격 증명, GCP 서비스 계정 토큰, Azure 관리 ID 토큰을 열거하고 내부 서비스(Redis, Elasticsearch, Consul, Prometheus, Tomcat)를 프로브합니다. Redis 쓰기 액세스를 위한 Gopher 프로토콜을 테스트합니다.

