
 arpsyndicate/puncia
Panthera(P.)uncia - Subdomain Center 및 Exploit Observer를 위한 공식 CLI 유틸리티.


Puncia는 두 가지 A.R.P. Syndicate 인텔리전스 API를 위한 공식 커맨드라인 클라이언트입니다. 도메인, 브랜드 또는 취약점 ID를 지정하면 브라우저 없이 몇 초 만에 구조화된 JSON을 반환합니다:
$ puncia subdomain arpsyndicate.io
╭──────────────────────────────────────────────────────────────────────╮
│ Panthera(P.)uncia v0.38                                              │
│ subdomain recon · brand impersonation · exploit intel · sbom analysis│
│ A.R.P. Syndicate — https://www.arpsyndicate.io                       │
╰──────────────────────────────────────────────────────────────────────╯
[
  "advisories.arpsyndicate.io",
  "asm.arpsyndicate.io",
  "blog.arpsyndicate.io",
  ...
]

$ puncia sbom bom.json ./out
puncia ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100% (128/128) 0:00:41
이 결과들은 때때로 상당히 부정확하고 신뢰할 수 없을 수 있으며, 자체 개선 기능으로 인해 시점에 따라 크게 달라질 수 있다는 점을 유의하시기 바랍니다.
API 키를 사용하면 공격적인 속도 제한을 피할 수 있습니다: https://www.arpsyndicate.io/pricing.html
pip3 install punciapip3 install .pip3 install puncia
# subdomain footprint of a target (shadow IT / attack surface / takeover recon)
puncia subdomain example.com
# lookalike / typosquat / brand-impersonation domains
puncia replica example.com
# what's known about a CVE
puncia exploit CVE-2021-44228
puncia <mode> <query> [output] [--match M] [--domain D] [--limit N] [--offset N]
                               [--crawl] [--api-key K] [--concurrency N]
                               [--timeout S] [--retries N] [--quiet]
전체 참조는 puncia --help를 실행하세요. 결과는 stdout으로 출력되며,
배너, 진행 표시줄, 경고 및 오류는 모두 stderr로 전달되므로
puncia subdomain example.com > out.json은 항상 깔끔하고 유효한 JSON을 생성합니다.
종료 코드: 0 성공 · 1 요청 또는 입력 오류 · 2 사용법 오류.
(유료) API 키 저장(storekey) - puncia storekey <api-key>
~/.puncia에 0600 권한으로 저장됩니다. $PUNCIA_API_KEY가 이를 재정의하며,
이는 일반적으로 CI에서 원하는 방식입니다.(프리미엄) 도메인 쿼리, 도메인별 클러스터링(subdomain / cuttlefish 엔진) - puncia subdomain <domain> <output-file>
subdomain/replica/keyword는 모든 페이지를 순회하며
이를 병합합니다. 재개 가능하거나 스트리밍 방식의 순회를 위해
직접 하나의 원시 페이지를 가져오려면 --offset을(--limit과 함께 또는 없이) 전달하세요:
puncia subdomain bigco.com --limit 50000 --offset 0
# stderr prints: note: more results available — continue with --offset 50000
puncia subdomain bigco.com --limit 50000 --offset 50000
import asyncio
import puncia

async def main():
   # Without an API key (ratelimited)
   print(await puncia.query_api("exploit", "CVE-2021-3450"))
   print(await puncia.query_api("subdomain", "arpsyndicate.io"))

   # With an API key
   await puncia.store_key("ARPS-xxxxxxxxxx")
   api_key = await puncia.read_key()
   print(await puncia.query_api("subdomain", "arpsyndicate.io", apikey=api_key))
   print(await puncia.query_api("replica", "arpsyndicate.io", match="exact", apikey=api_key))
   print(await puncia.query_api("enrich", "CVE-2021-3450", apikey=api_key))
   print(await puncia.query_api("noncve", "exploitable", apikey=api_key))

   # Static endpoints (unauthenticated, unlimited)
   print(await puncia.query_api("subdomain", "^HEALTH"))
   print(await puncia.query_api("exploit", "^STATS"))

   # Live crawl, with the outcome surfaced via a callback
   await puncia.query_api(
       "subdomain", "bigco.com", apikey=api_key, crawl=True,
       on_crawl=lambda h: print("crawl status:", h.get("X-Crawl-Status")),
   )

   # Write straight to disk
   await puncia.query_api("subdomain", "arpsyndicate.io", "out.json", apikey=api_key)

asyncio.run(main())
실패 시 puncia.PunciaError가 발생하며, 빈 결과({} / [])는
오류로 처리되지 않고 그대로 반환됩니다. process_bulk()가 하는 것과
정확히 동일하게 session=과 공유 limiter=를 전달하여 여러 쿼리에 걸쳐
하나의 세션을 재사용하세요.
from puncia import PunciaError, query_api

try:
    data = await query_api("exploit", "CVE-2021-3450", apikey=api_key)
except PunciaError as exc:
    print(f"lookup failed: {exc}")
git clone https://github.com/ARPSyndicate/puncia && cd puncia
pip install --upgrade pip     # editable installs need pip >= 21.3
pip install -e ".[dev]"
pytest                        # 42 offline tests, no API calls or network access
테스트 스위트는 완전히 오프라인입니다. 네트워크에 접속하지 않고 URL 구성, 출력 경로 격리, SBOM 파싱, 대량 계획 및 속도 제한기 타이밍을 다루므로 어떤 환경에서도 안전하게 실행할 수 있습니다.
--limit--offset--crawl은 저장된 결과에
실시간 발견 패스를 보충합니다. 주어진 도메인은 약 6시간에 한 번만 실제로
재크롤되며, 그 시간 내의 요청은 캐시된 크롤 결과를
즉시 받습니다. Puncia는 stderr에 결과를 보고합니다:
crawl: fresh, 12 newly discovered name(s) (partial / cooldown /
disabled도 있음).
puncia subdomain bigco.com --crawl
(프리미엄) 복제 도메인 쿼리, 브랜드별 클러스터링(replica / octopus 엔진) - puncia replica <domain> --match <prefix|exact|substring> <output-file>
(프리미엄) 키워드로 쿼리, 키워드별 클러스터링(keyword / ammonites 엔진) - puncia keyword <keyword> --match <exact|prefix> <output-file>
--domain으로 키워드를 단일 도메인으로 범위를 지정할 수 있습니다:
puncia keyword blog --domain bandcamp.com익스플로잇 및 취약점 식별자 쿼리(exploit)
puncia exploit ^WATCHLIST_IDES <output-file>puncia exploit ^WATCHLIST_INFO <output-file>puncia exploit ^WATCHLIST_TECH <output-file>puncia exploit ^STATS <output-file>puncia exploit ^HEALTH <output-file>puncia exploit <eoidentifier> --match <substring|prefix|exact> <output-file>(프리미엄) CVE/GHSA 식별자 보강(enrich) - puncia enrich <cve-id/ghsa-id> <output-file>
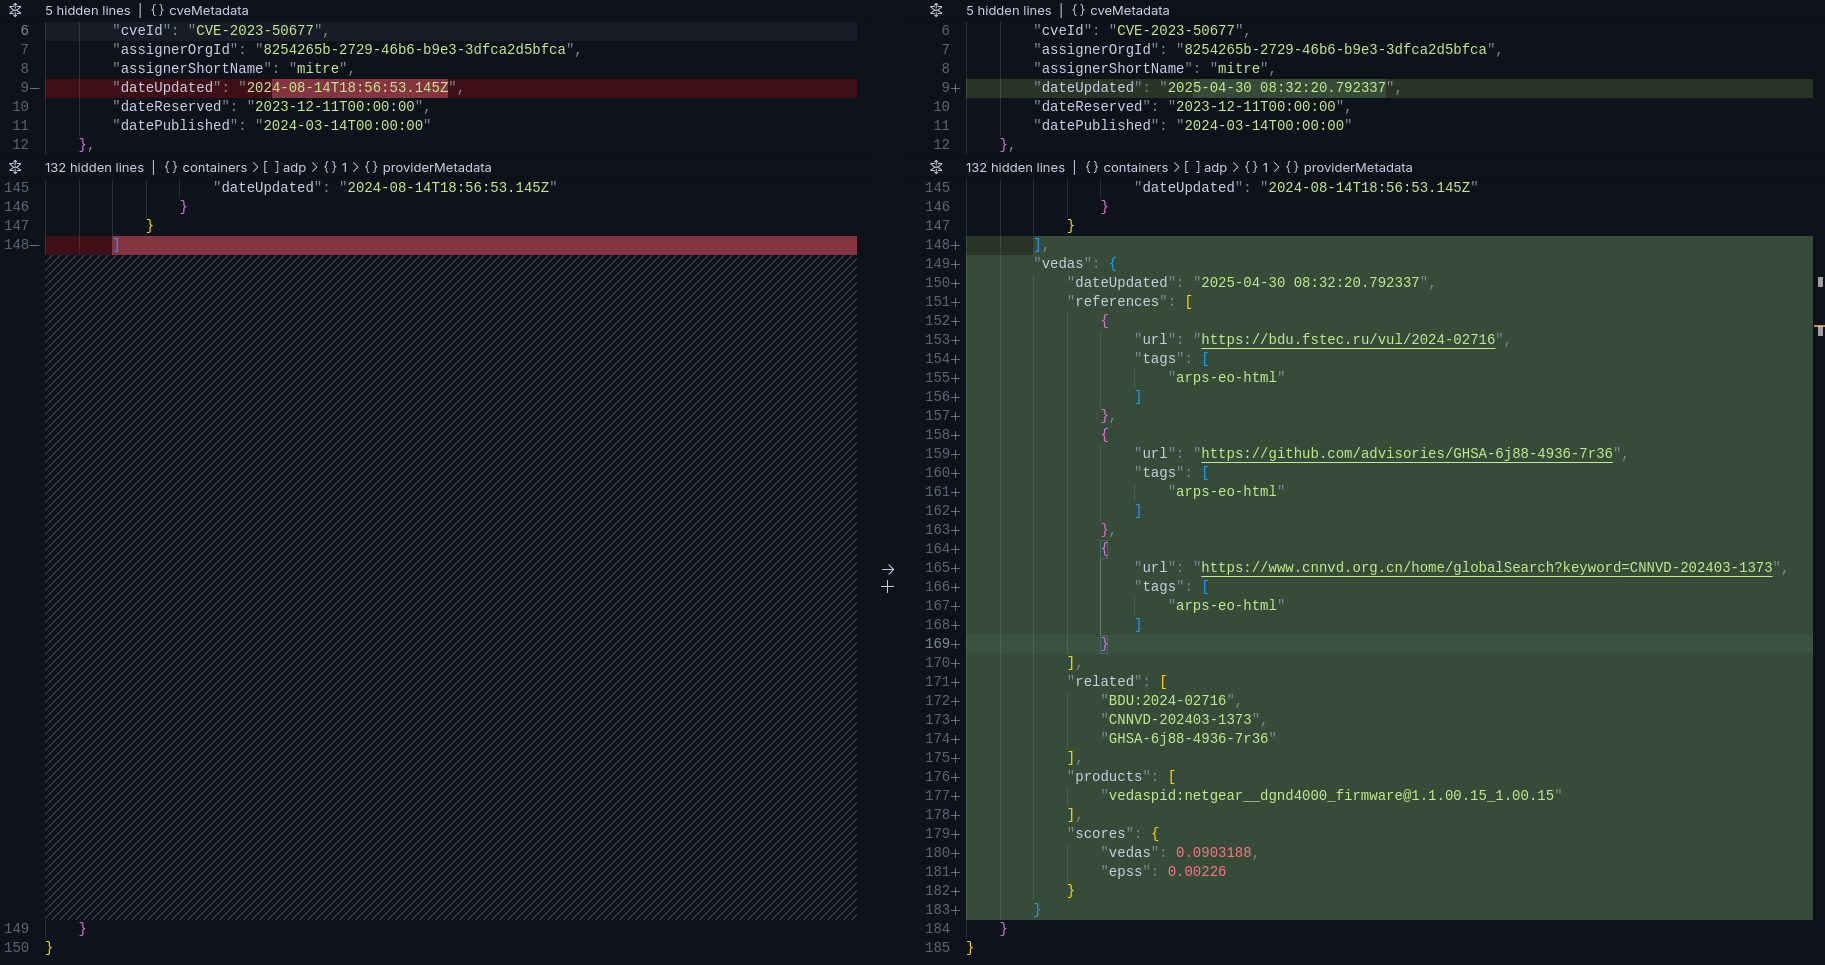
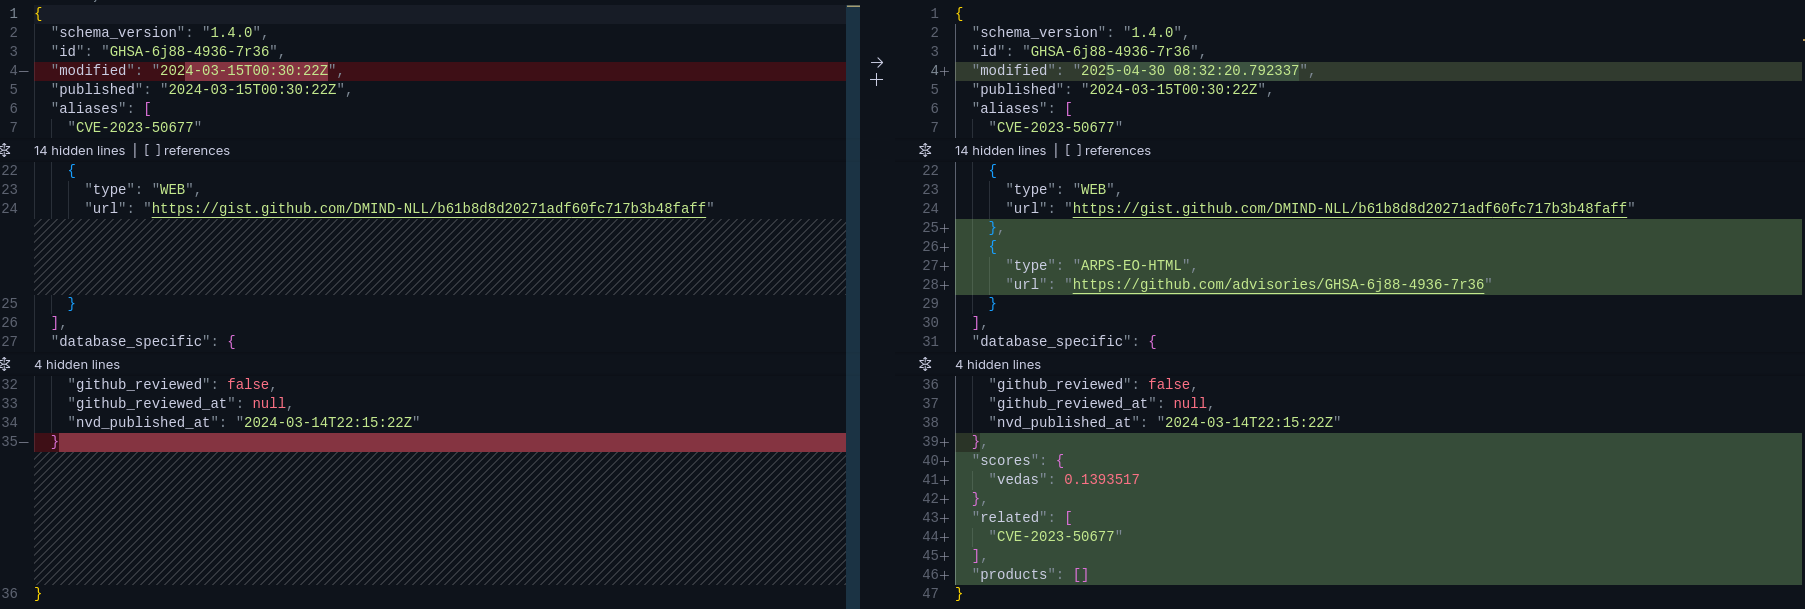
enrich=true는 CVE-/GHSA- 식별자에만 적용되며, 전체 업스트림 권고
레코드를 EPSS + VEDAS 점수와 병합합니다.(유료) VEDAS 그룹별 비CVE 식별자(noncve) - puncia noncve <browser/china/russia/europe/exploitable> <output-file>
(무료) Subdomain Center 서비스 상태(^HEALTH) - puncia subdomain ^HEALTH <output-file>
다중 쿼리(bulk/sbom)
puncia bulk <json-file> <output-directory>
{
    "subdomain": [
        "domainA.com",
        "domainB.com"
    ],
    "replica": [
        "domainA.com",
        "domainB.com"
    ],
    "keyword": [
        "keywordA",
        "keywordB"
    ],
    "exploit": [
        "eoidentifierA",
        "eoidentifierB"
    ],
    "enrich": [
        "eoidentifierA",
        "eoidentifierB"
    ]
}
puncia sbom <json-file> <output-directory>Bulk 및 SBOM 실행은 쿼리를 중복 제거하고, 병렬성을 --concurrency
(기본값 10)로 제한하며, API 키가 없을 때는 무료 티어 예산 내에
머물도록 요청 속도를 자동으로 조절합니다.
(프리미엄) 외부 임포트
