Skip to content
KitploitKITPLOIT
도구블로그
Log in
제출
도구블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

··피드·문의·개인정보·© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Bug-Bounty — Bug Bounty ~ Awesomes | 서적 | 치트시트 | 체크리스트 | 도구 | 워드리스트 | 더 보기 | Kitploit
도구/GitHubGitHub/anlominus/bug-bounty
ReconnaissanceVulnerability AnalysisWeb SecurityCTFPenetration TestingLearning & EducationCurated ResourcesLabs & Practice
GitHubanlominus/bug-bounty

Bug-Bounty

Bug Bounty ~ Awesomes | 서적 | 치트시트 | 체크리스트 | 도구 | 워드리스트 | 더 보기

저장소 보기
6511082411개월 전Kitploit 검토 완료

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →
공유

בס״ד

⚜️ Aภl๏miuภuຮ ⚜️

⫷ HacKingPro ⫸
⫷ TryHackMe | KoTH ⫸
⫷ Privilege-Escalation⫸
⫷ ScanPro | Linfo | Diablo ⫸
⫷ Offensive-Security | PenTest ⫸
⫷ Goals | Studies | HacKing | AnyTeam ⫸
image


버그 바운티

  • Awesomes
  • 도서
  • 치트시트
  • 체크리스트
  • 도구
  • 워드리스트
  • 기타

GitHub 바운티

GitHub 보안 버그 바운티

소프트웨어 보안 연구원들은 점점 더 인터넷 기업들과 협력하여 취약점을 찾고 있습니다.

우리의 바운티 프로그램은 이러한 연구원들에게 경의를 표하며, 중요한 취약점에 대해 $30,000 이상의 보상을 제공합니다.

Awesomes

  • Awesome Bug Bounty Tools

    다양한 버그 바운티 도구를 모아 놓은 선별된 목록

    https://github.com/vavkamil/awesome-bugbounty-tools

  • Awesome Bug Bounty

    버그 바운티 프로그램과 버그 바운티 헌터들의 write-up을 종합적으로 정리해 놓은 선별된 목록입니다.

  • Awesome CTF

    Capture The Flag(CTF) 프레임워크, 라이브러리, 리소스, 소프트웨어, 튜토리얼을 모아 놓은 선별된 목록입니다. 이 목록은 초보자와 숙련된 CTF 플레이어 모두가 CTF와 관련된 모든 것을 한곳에서 찾을 수 있도록 돕는 것을 목표로 합니다.

  • Awesome Bug Bounty Builder

    Awesome Bug bounty builder 프로젝트 - 취약점을 찾기 위한 모든 일반적인 도구.

    image


도서

  • Hacking-Books 여기 인기 있는 해킹 PDF 파일들이 있습니다.

  • The Threat Hunter Playbook ~ The Threat Hunter Playbook

  • image

    The Threat Hunter Playbook은 커뮤니티 주도형 오픈소스 프로젝트로, 탐지 로직, 적의 전술(Tradecraft), 리소스를 공유하여 탐지 개발을 더 효율적으로 만들기 위해 만들어졌습니다. 이 프로젝트의 모든 탐지 문서는 MITRE ATT&CK 구조를 따라 구성되어 있으며, 전술 그룹별로 사후 침해 행위를 분류하고 대화형 노트북(interactive notebooks) 형태로 제공합니다. 노트북을 사용하면 텍스트, 쿼리, 예상 출력뿐만 아니라 BinderHub 클라우드 컴퓨팅 환경을 통해 로컬 또는 원격으로 사전 녹화된 보안 데이터 세트에 대한 탐지 로직을 실행할 수 있는 코드도 공유할 수 있습니다.


치트시트

  • Bug Bounty Cheat Sheet

    버그 바운티 헌터를 위한 흥미로운 페이로드, 팁, 트릭 목록입니다.

  • Bug Bounty Cheat Sheet

    버그 바운티 헌터를 위한 흥미로운 페이로드, 팁, 트릭 목록입니다.


체크리스트

  • Galaxy-Bugbounty-Checklist

    버그 바운티와 침투 테스트를 위한 팁과 튜토리얼입니다.


도구

  • Bug Bounty Methodology & Tools

다음은 Twitch에서 Live Recon Passive ONLY를 수행할 때 사용하는 도구 중 일부입니다:

  1. Recon-ng https://github.com/lanmaster53/recon-ng
  2. httpx https://github.com/projectdiscovery/httpx
  3. isup.sh https://github.com/gitnepal/isup
  4. Arjun https://github.com/s0md3v/Arjun
  5. jSQL https://github.com/ron190/jsql-injection
  6. Smuggler https://github.com/defparam/smuggler
  7. Sn1per https://github.com/1N3/Sn1per
  8. Spiderfoot https://github.com/smicallef/spiderfoot
  9. Nuclei https://github.com/projectdiscovery/nuclei
  10. Jaeles https://github.com/jaeles-project/jaeles
  11. ChopChop https://github.com/michelin/ChopChop
  12. Inception https://github.com/proabiral/inception
  13. Eyewitness https://github.com/FortyNorthSecurity/EyeWitness
  14. Meg https://github.com/tomnomnom/meg
  15. Gau - Get All Urls https://github.com/lc/gau
  16. Snallygaster https://github.com/hannob/snallygaster
  17. NMAP https://github.com/nmap/nmap
  18. Waybackurls https://github.com/tomnomnom/waybackurls
  19. Gotty https://github.com/yudai/gotty
  20. GF https://github.com/tomnomnom/gf
  21. GF Patterns https://github.com/1ndianl33t/Gf-Patterns
  22. Paramspider https://github.com/devanshbatham/ParamSpider
  23. XSSER https://github.com/epsylon/xsser
  24. UPDOG https://github.com/sc0tfree/updog
  25. JSScanner https://github.com/dark-warlord14/JSScanner
  26. Takeover https://github.com/m4ll0k/takeover
  27. Keyhacks https://github.com/streaak/keyhacks
  28. S3 Bucket AIO Pwn https://github.com/blackhatethicalhacking/s3-buckets-aio-pwn
  29. BHEH Sub Pwner Recon https://github.com/blackhatethicalhacking/bheh-sub-pwner
  30. GitLeaks https://github.com/zricethezav/gitleaks
  31. Domain-2IP-Converter https://github.com/blackhatethicalhacking/Domain2IP-Converter
  32. Dalfox https://github.com/hahwul/dalfox
  33. Log4j Scanner https://github.com/Black-Hat-Ethical-Hacking/log4j-scan
  34. Osmedeus https://github.com/j3ssie/osmedeus
  35. getJS https://github.com/003random/getJS
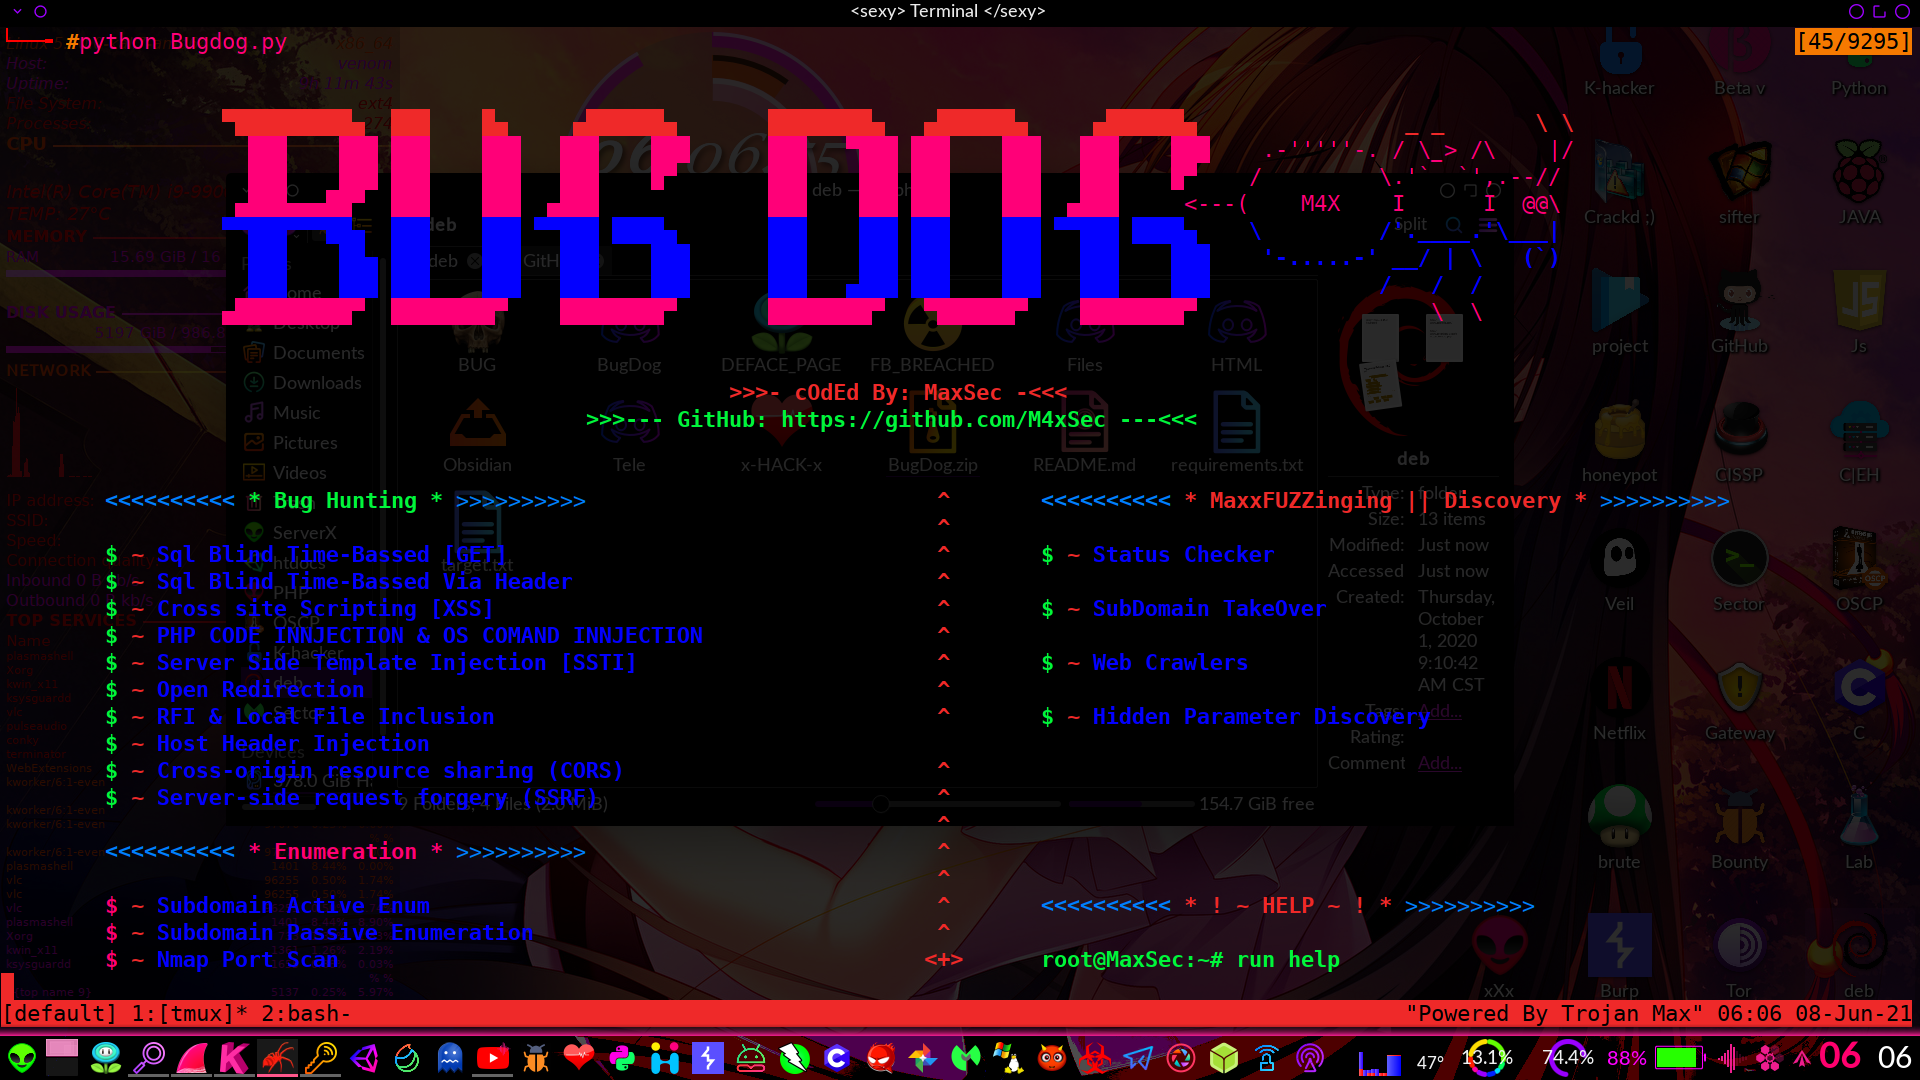
  • BugDog

    강력한 버그 헌팅 도구입니다. SQL, XSS, PHP 코드 실행, SSRF 등을 지원합니다. 제가 버그 헌팅 중 발견한 페이로드도 추가해 두었습니다. 나머지는 자신만의 커스텀 페이로드를 추가할 수 있습니다 ;)

    image

    • 참고: BugDog는 Python으로 만들어졌으며 정상적으로 실행하려면 python2가 필요합니다.

  • Bug-Bounty-Tools: 버그 바운티를 위한 랜덤 도구 모음

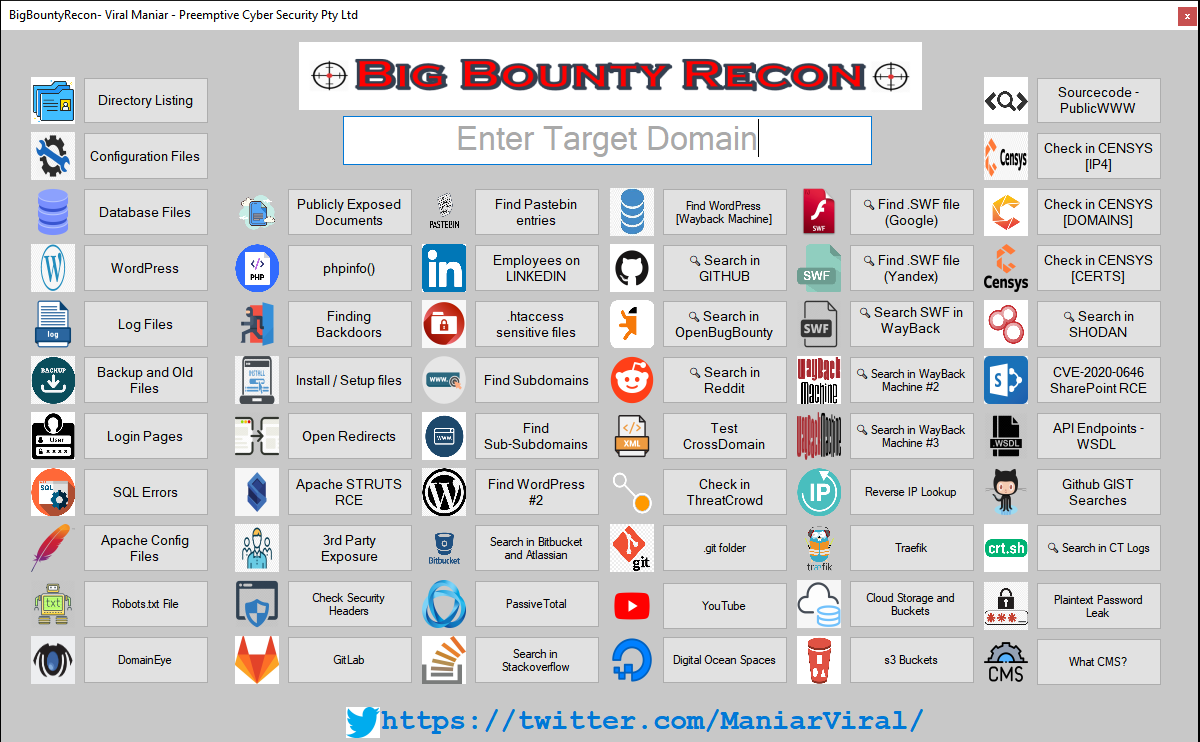
  • BigBountyRecon

    BigBountyRecon 도구는 다양한 Google dork와 오픈소스 도구를 활용한 58가지의 서로 다른 기술을 사용하여 대상 조직에 대한 초기 정찰 과정을 빠르게 진행합니다.
    • image
  • Hack-Pet:

    hack-pet은 해커/버그 바운티 헌터에게 유용한 명령 스니펫 모음입니다.

    recon_profile과 유사하지만 pet을 사용합니다. pet은 명령 세트를 더 발전적으로 관리할 수 있습니다.

    image
    image

  • CTF-tool

    Capture The Flag(CTF) 프레임워크, 라이브러리, 리소스, 소프트웨어의 선별된 목록입니다.

  • Bug bounty toolkit

    여기에서 버그 바운티 또는 침투 테스트에 사용할 수 있는 다양한 도구 목록을 찾을 수 있습니다.

    진행하면서 일부 카테고리와 도구가 추가될 예정입니다.

    질문이나 제안이 있으시면 트위터(https://twitter.com/_sehno_)로 연락주세요.

  • BugHuntingToolKit

    이것은 버그 헌터를 위한 도구로, 버그 헌터들이 사용하는 도구를 포함하고 있습니다.

  • Parrots Recon

    버그 바운티를 위한 정찰 자동화(Recon Automation)

도구 다운로드