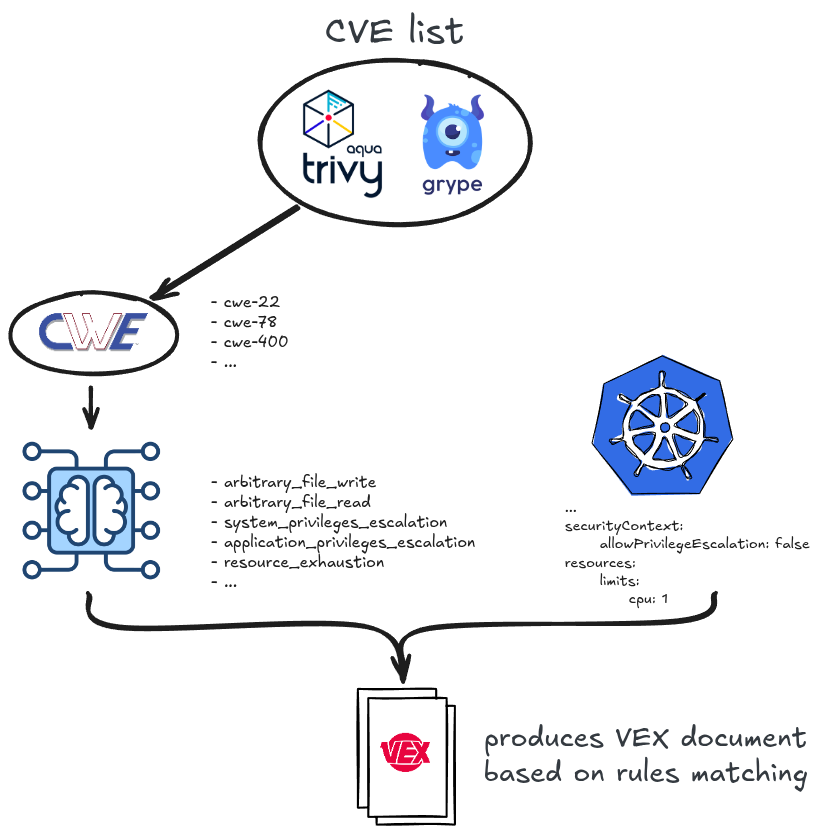

스캔에 Kubernetes 컨텍스트를 적용하여 취약점을 억제
 (이 로고는 AI로 생성되지 않았습니다)
Vex8s는 컨테이너 취약점을 Kubernetes 설정과 연관시켜 클러스터에서 실제로 악용 가능한 CVE를 판별함으로써 VEX 문서를 생성합니다.
이 프로젝트는 실험적인 프로젝트입니다. 변경 사항이 빠르게 적용될 수 있습니다.
이 프로젝트는 취약점 분류와 securityContext 분석을 결합하여 Kubernetes 워크로드 내에서 알려진 CVE의 악용 가능성을 평가하는 것을 목표로 합니다.
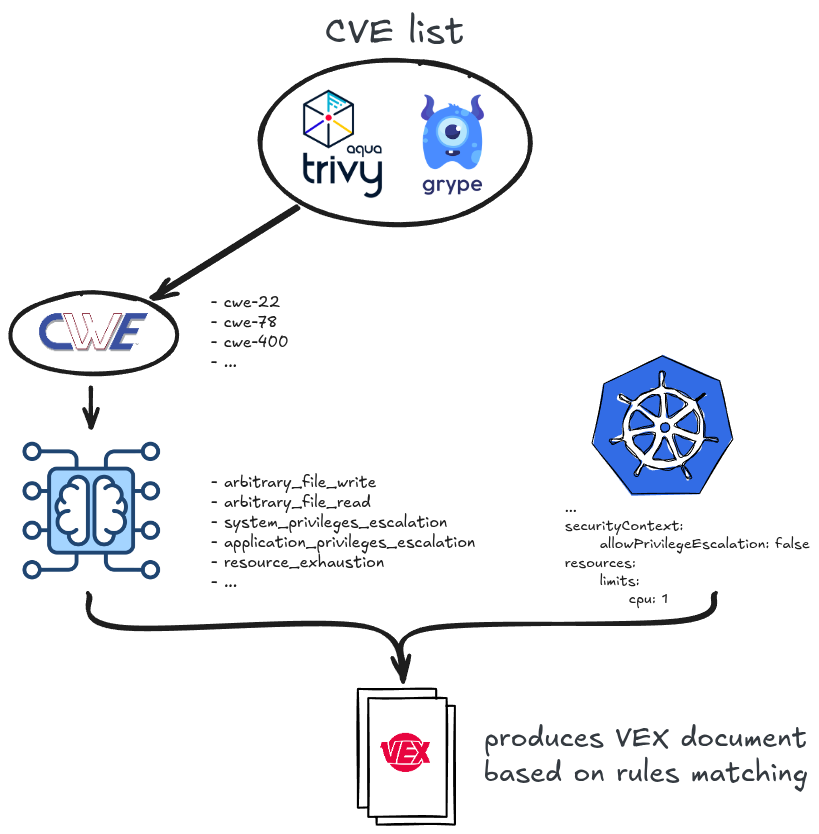
다음과 같은 개념을 기반으로 합니다:
보다 심층적인 내용은 다음 논문을 참고하시기 바랍니다: Environment-Aware Vulnerability Suppression Using Kubernetes Security Contexts and VEX
릴리스 페이지에서 최신 바이너리를 다운로드할 수 있습니다.
또는 직접 빌드할 수도 있습니다:
make build
vex8s는 현재 VEX 문서를 생성하는 두 가지 방법을 지원합니다:
passive-mode: trivy 또는 grype로 이미 생성된 취약점 보고서를 전달합니다.
active-mode: trivy 또는 grype 엔진을 사용하여 이미지를 직접 스캔한 후 결과를 기반으로 문서를 생성합니다.
trivy 사용:
# generate vulnerability report.
trivy image --format json --output nginx.trivy.json nginx:1.21.0

# generate VEX document by processing vulnerability report.
vex8s generate --manifest examples/nginx.yaml --report nginx.trivy.json --output nginx.vex.json

# scan again with VEX document to suppress vulnerabilities.
trivy image --vex nginx.vex.json --show-suppressed nginx:1.21.0
grype를 사용해도 동일하게 적용할 수 있습니다:
# generate sbom report.
grype --output cyclonedx-json --file nginx.grype.json nginx:1.21.0

# generate vulnerability report.
grype sbom:./nginx.grype.json --output json --file nginx.grype-vr.json

# generate VEX document by processing vulnerability report.
vex8s generate --manifest examples/nginx.yaml --report nginx.grype-vr.json --output nginx.vex.json

# scan sbom with VEX document to suppress vulnerabilities.
grype sbom:./nginx.grype.json --output table --vex nginx.vex.json --show-suppressed
trivy 사용:
# scan the image and automatically generate VEX document.
vex8s generate --manifest examples/nginx.yaml --scan.engine trivy --output nginx.vex.json

# scan again with VEX document to suppress vulnerabilities.
trivy image --vex nginx.vex.json --show-suppressed nginx:1.21.0
grype를 사용해도 동일하게 적용할 수 있습니다:
# generate sbom report.
grype --output cyclonedx-json --file nginx.grype.json nginx:1.21.0

# scan the image and automatically generate VEX document.
vex8s generate --manifest examples/nginx.yaml --scan.engine grype --output nginx.vex.json

# scan sbom with VEX document to suppress vulnerabilities.
grype sbom:./nginx.grype.json --output table --vex nginx.vex.json --show-suppressed
각 CVE는 하나 이상의 악용 클래스로 분류되며, 이는 완화 결정을
주도합니다. vex8s는 --classifier를 통해 세 가지 분류기 엔진을 지원합니다:
embedded (기본값): 바이너리에 번들로 포함된 오프라인 ONNX ML 모델입니다.
네트워크 접근이 필요하지 않습니다.gemini: Google의 Gemini LLM을 사용하여 CVE 설명을 분류합니다.
GEMINI_API_KEY 환경 변수가 필요합니다 (선택적으로 GEMINI_MODEL).ollama: 로컬에서 실행 중인 Ollama 서버를 사용하여
CVE 설명을 분류합니다. 먼저 qwen2.5:3b-instruct와 같은 모델을
가져오세요 (선택적으로 OLLAMA_HOST / OLLAMA_MODEL 설정).export GEMINI_API_KEY="your-api-key"
vex8s generate --manifest examples/nginx.yaml --report nginx.trivy.json \
--output nginx.vex.json --classifier ollama
전체 안내, Gemini 및 Ollama 분류기 설정, 그리고 전체 플래그 참조는 문서, 특히 사용자 가이드를 참고하세요.
이 프로젝트는 Akihiro Suda의 프로젝트 vexllm에서 영감을 받았습니다.

