
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
FISSURE — 모두를 위한 RF 및 리버스 엔지니어링 프레임워크입니다. 팔로우하고 ★를 눌러 지지를 보여주세요! | Kitploit

도구/GitHubGitHub/ainfosec/fissure
Reverse EngineeringFuzzingWireless SecurityCTFLearning & Education
GitHubainfosec/fissure

FISSURE

모두를 위한 RF 및 리버스 엔지니어링 프레임워크입니다. 팔로우하고 ★를 눌러 지지를 보여주세요!
저장소 보기
2.0k1381403일 전Kitploit 검토 완료
공유
웹사이트
요청한 언어로 콘텐츠를 사용할 수 없습니다. 영어 버전을 표시합니다.

FISSURE - The RF Framework

Frequency Independent SDR-based Signal Understanding and Reverse Engineering
Overview

FISSURE GRCon26 Conference Talk
GRCon26 Conference Talk
FISSURE Tactical Workflow Demo
Tactical Workflow Demo
GRCon26 Presentation Slides

Introduction

FISSURE is an open-source framework for RF analysis, automation, and distributed operations. It connects SDR hardware, signal processing, Sensor Nodes, geolocation, protocol analysis, targeting, and situational awareness within a single extensible environment.

FISSURE can run as a standalone workstation or scale across distributed Sensor Nodes connected over IP networks. GNU Radio and other tools provide the underlying RF processing, while FISSURE coordinates hardware, data, context, plugins, Actions, and operator workflows across local and remote systems.

The framework is designed for experimentation, research, education, capability development, and operational integration without locking users to a single protocol, sensor, platform, or use case.
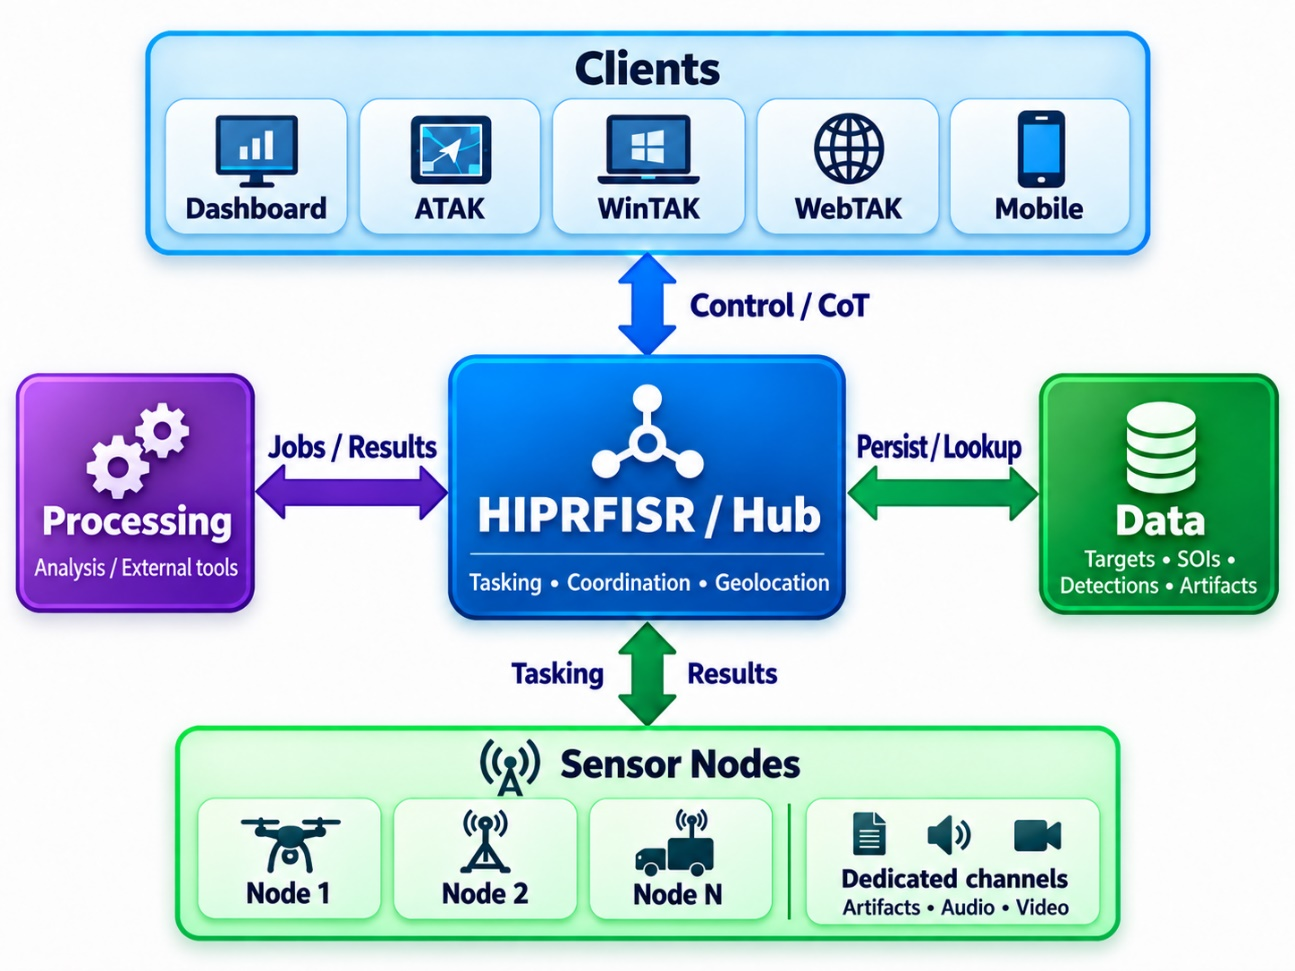
FISSURE distributed architecture

Workflow Overview

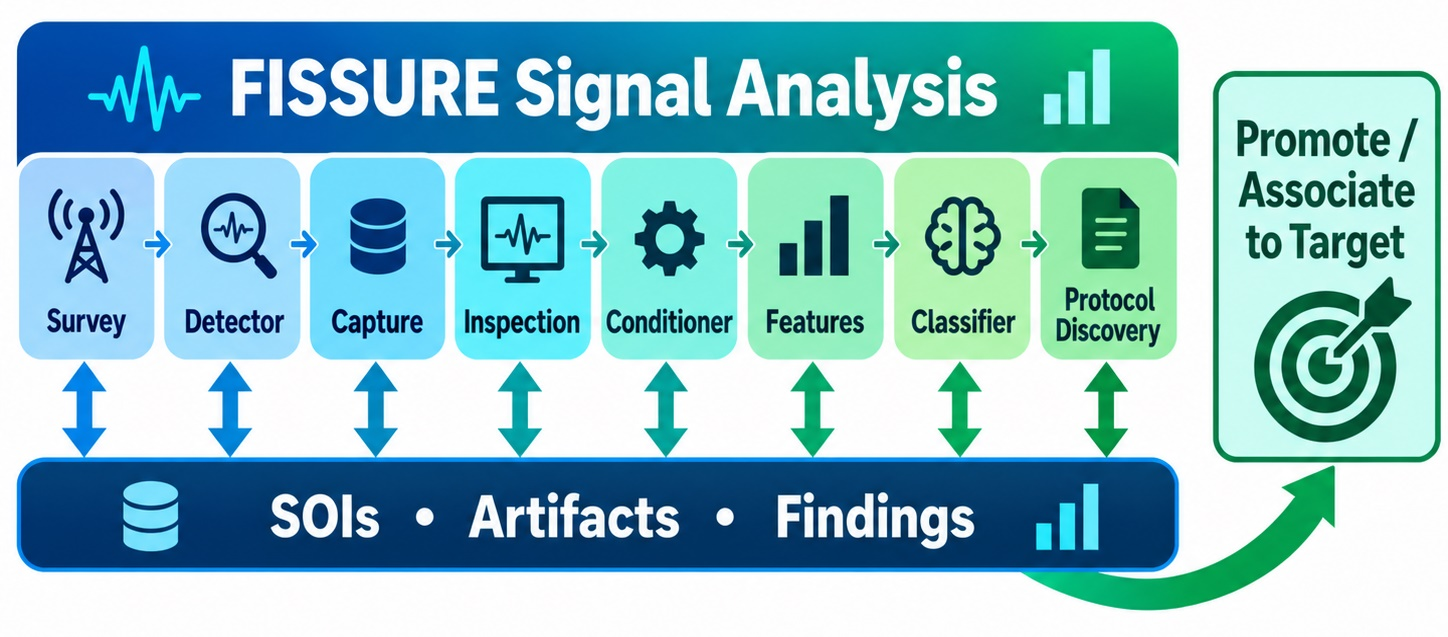
FISSURE organizes RF workflows around connected workspaces that share Sensor Nodes, SOIs, Targets, Detections, Artifacts, Findings, and plugin Actions.
  • Tactical: Monitor distributed Sensor Nodes, detections, SOIs, Targets, geolocation results, and other RF activity on a shared operational map.
  • Signal Analysis: Move from survey and detection through capture, inspection, conditioning, feature extraction, classification, and protocol discovery.
  • Targets & Actions: Manage Targets and execute reusable plugin Actions through focused, sequential, fuzzing, and packet-crafting workflows.
  • Sensor Nodes: Configure local and remote nodes, manage hardware, transfer files, automate startup behavior, and monitor node status.
  • Library: Maintain reusable protocol information, packet definitions, archived signals, replay content, datasets, and RF reference material.
  • Plugins & Actions: Add, deploy, and execute capabilities across supported nodes and interfaces without modifying the FISSURE core.

FISSURE signal analysis workflow

Core Information Model

FISSURE connects workflows through a shared information model rather than treating each tool or tab as an isolated function. SOIs anchor signal analysis, Targets anchor operational context, Detections capture sensor observations, Artifacts and Findings preserve data and results, and Alerts and Action Recommendations surface information that may require attention or follow-on action.
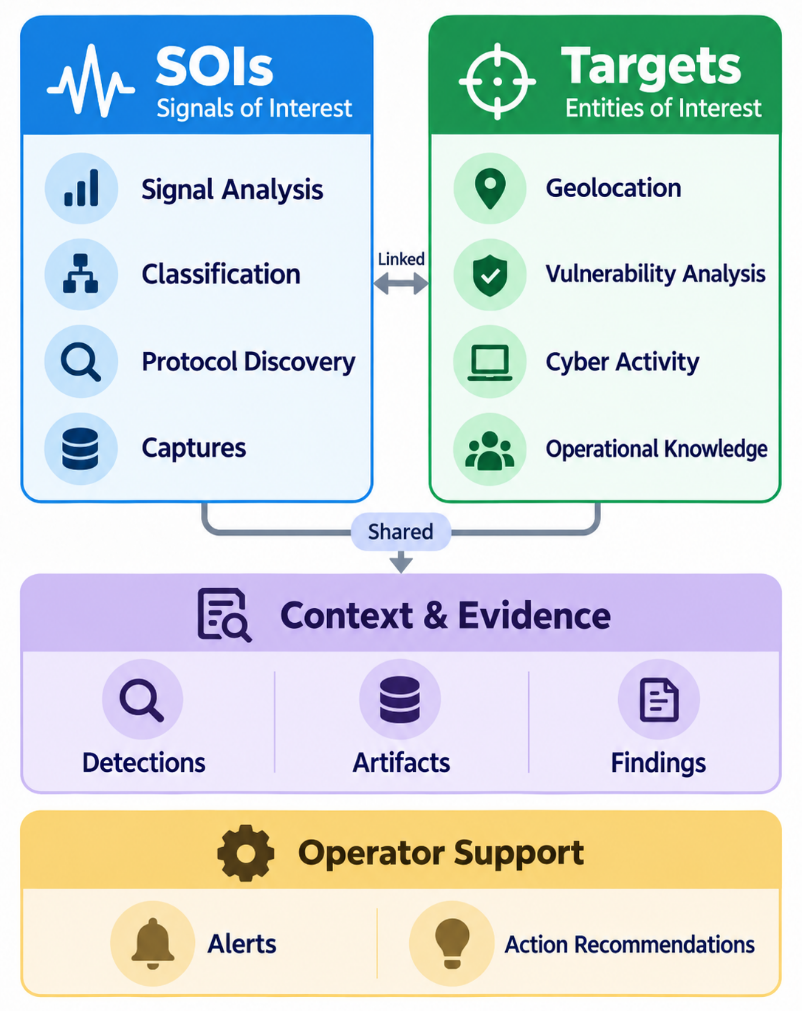
FISSURE core information model

Key Capabilities

  • Detect, classify, capture, and analyze RF signals
  • Record, inspect, replay, and manipulate IQ data
  • Discover protocols, build packets, and perform RF/cyber experimentation
  • Execute fuzzing, vulnerability analysis, and reusable test workflows
  • Coordinate local and distributed Sensor Nodes, SDRs, sensors, and tools
  • Geolocate emitters and maintain persistent Targets, detections, and observations
  • Share RF-derived awareness, alerts, artifacts, and target information through TAK
  • Extend capabilities through deployable plugins, Actions, and reusable Operations
  • Automate multi-step workflows across local and remote systems
  • Integrate custom analysis, external tools, and emerging AI/ML capabilities

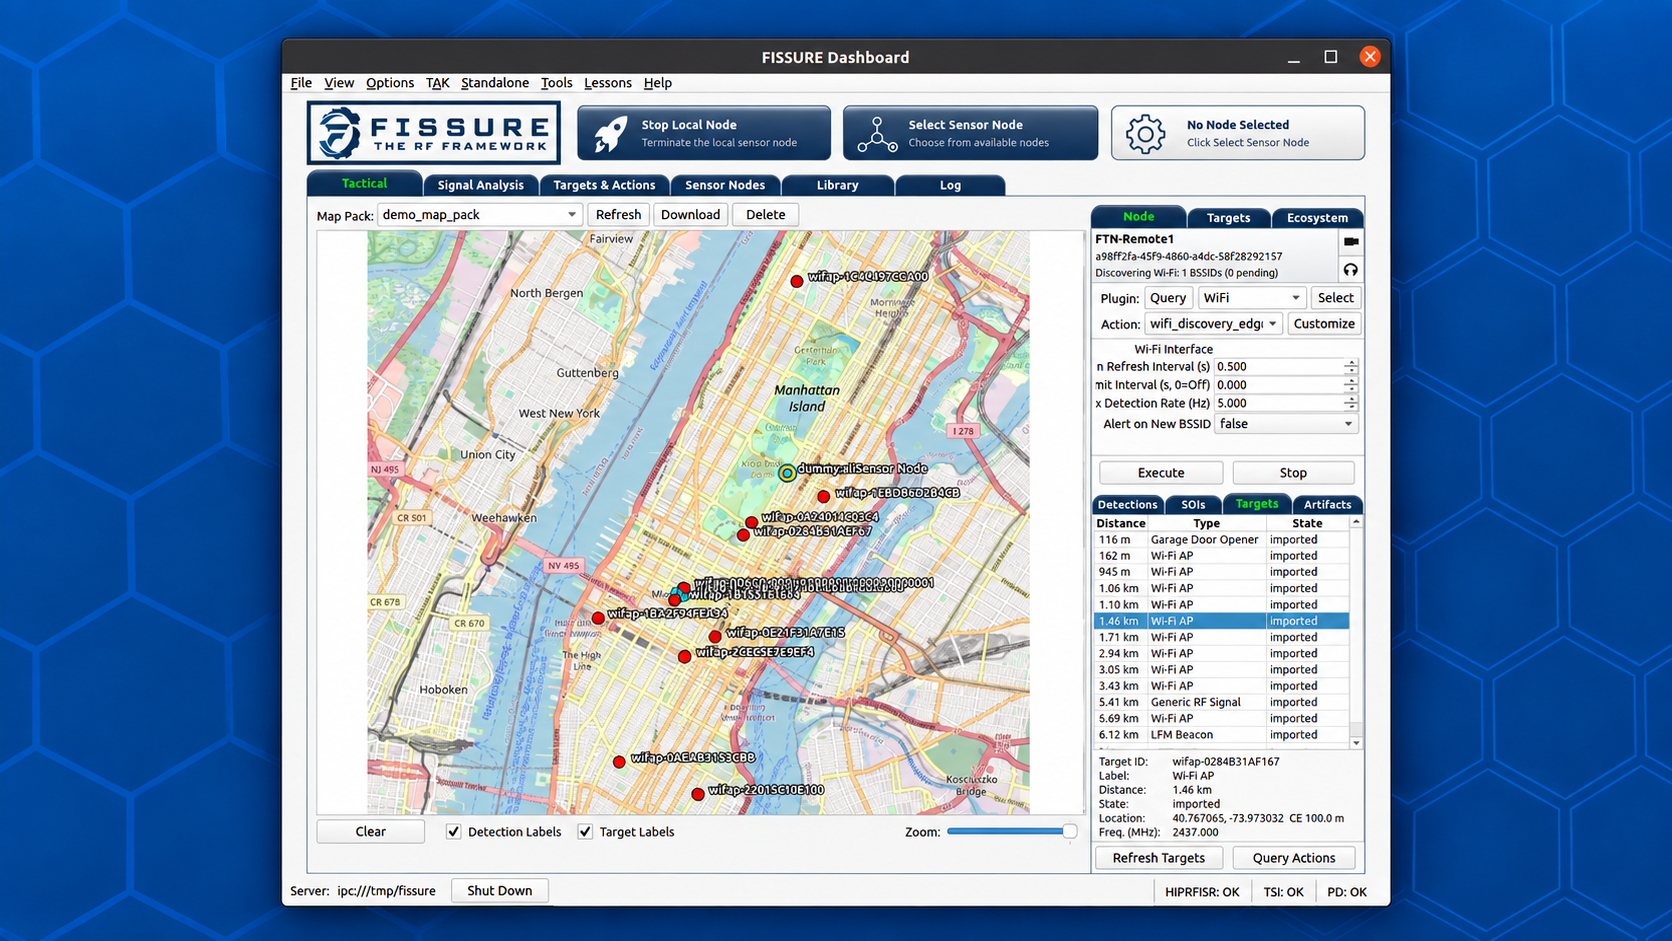
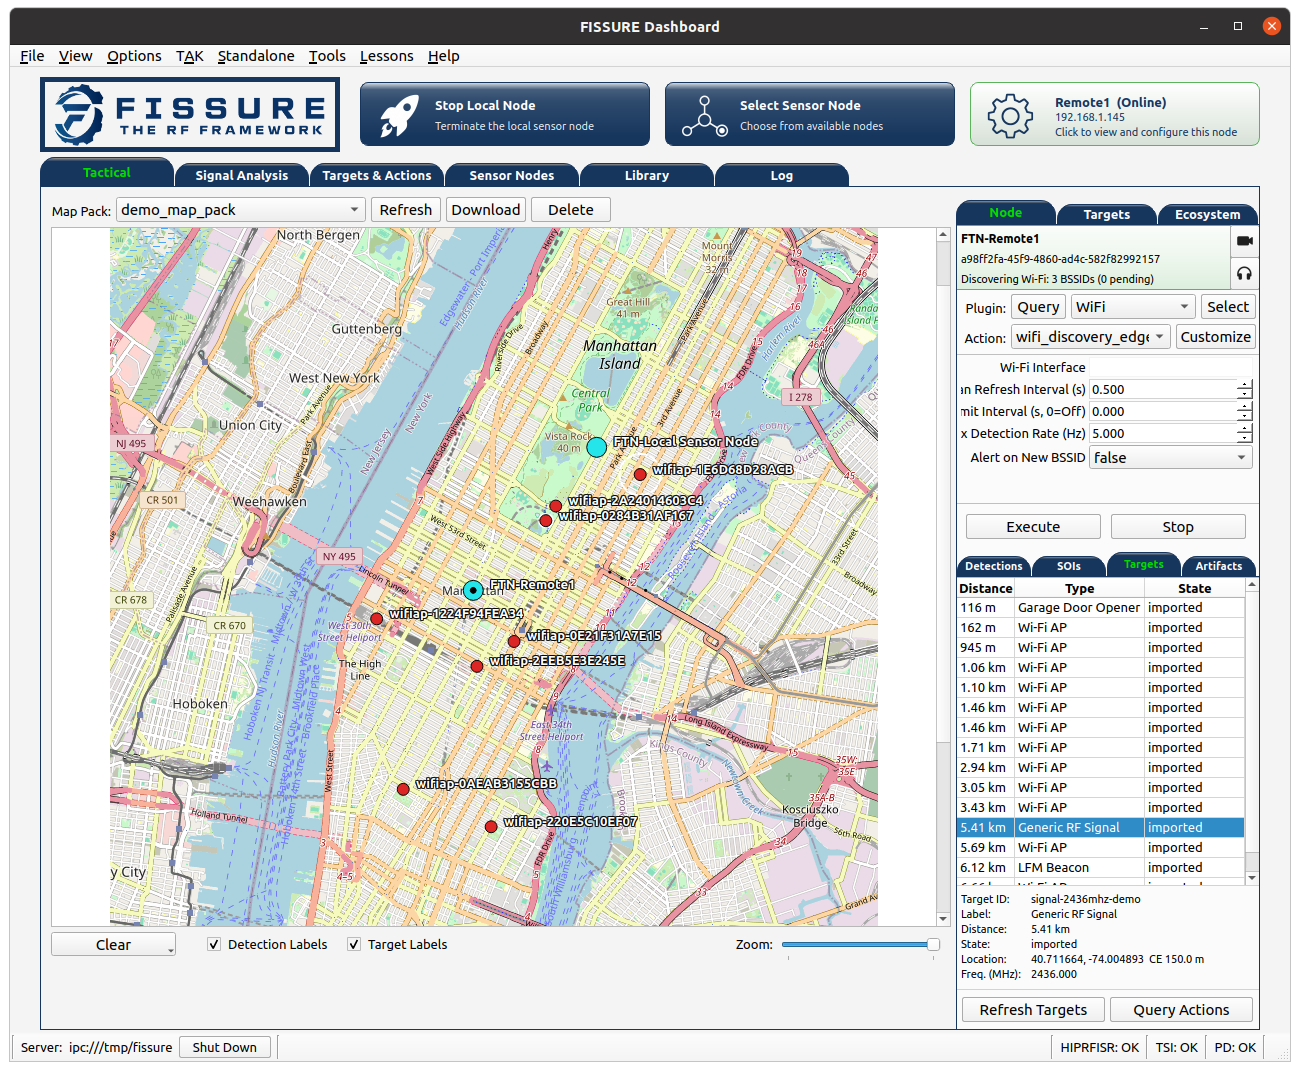
FISSURE Tactical Dashboard
FISSURE Tactical view connecting distributed Sensor Nodes, detections, SOIs, Targets, and operational context.

FISSURE and Fracture

Fracture is AIS's deployable tactical RF system built on the open-source FISSURE framework.

FISSURE provides the software foundation for RF sensing, signal analysis, distributed Sensor Nodes, geolocation, TAK integration, automation, and plugin-based capability development. Fracture packages that foundation into purpose-built hardware and software configurations designed for operational deployment.

Fracture combines SDRs, compute, networking, plugins, and mission-specific integrations around fixed-site, vehicle, manpack, sUAS, and other distributed deployments while preserving the flexibility and extensibility of FISSURE.
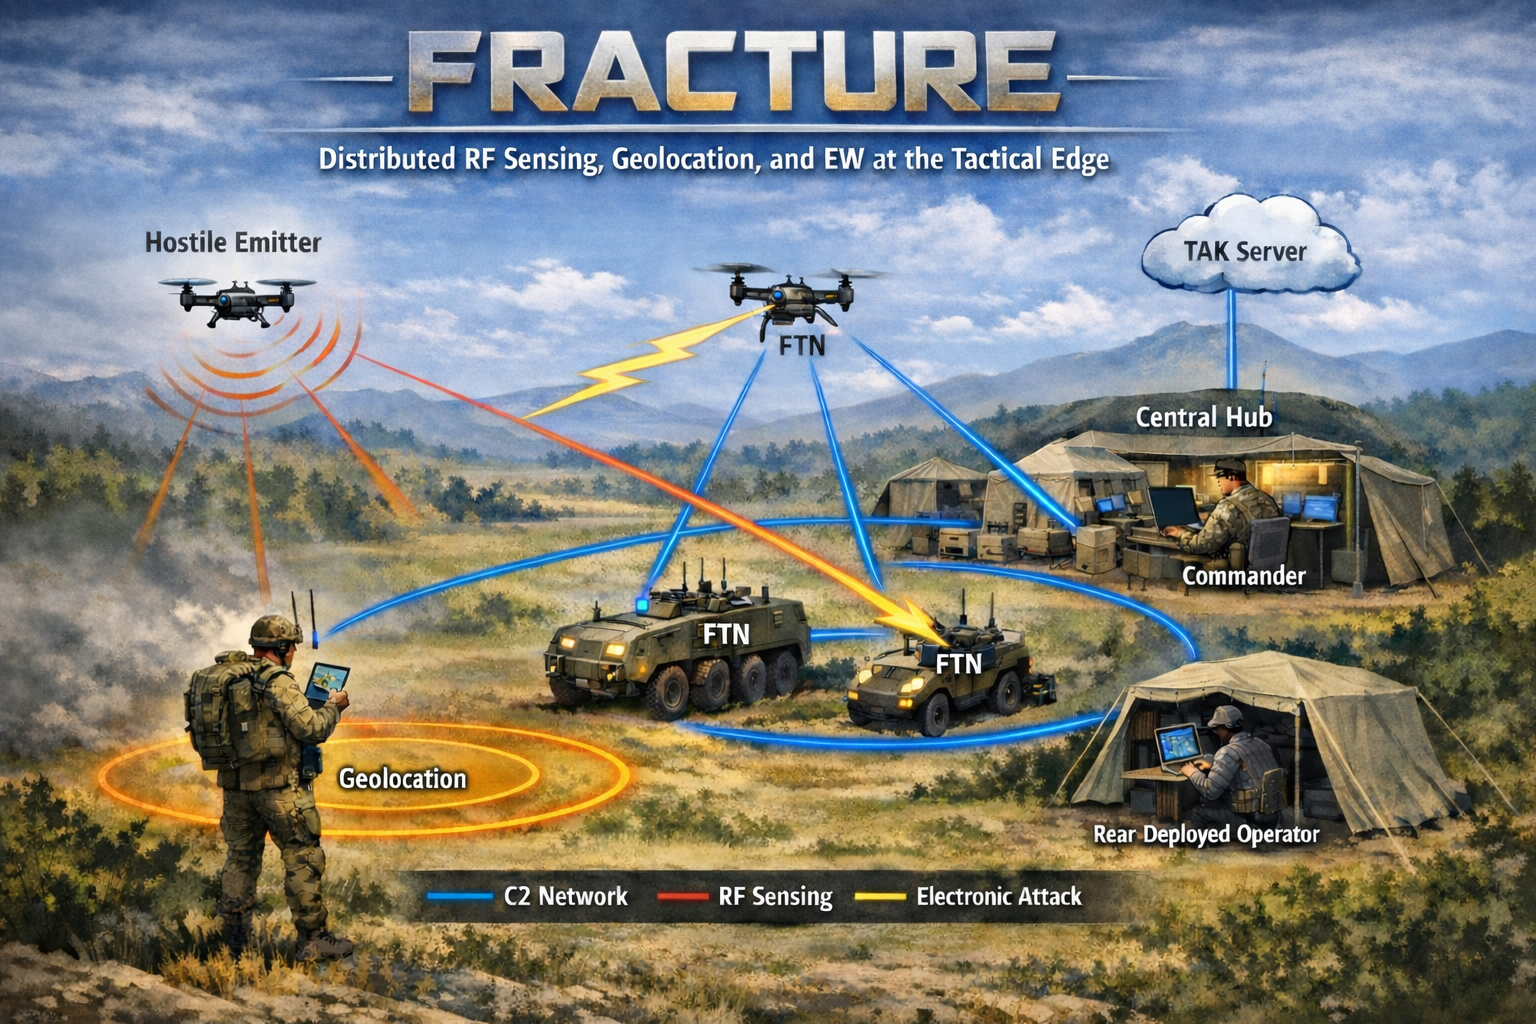
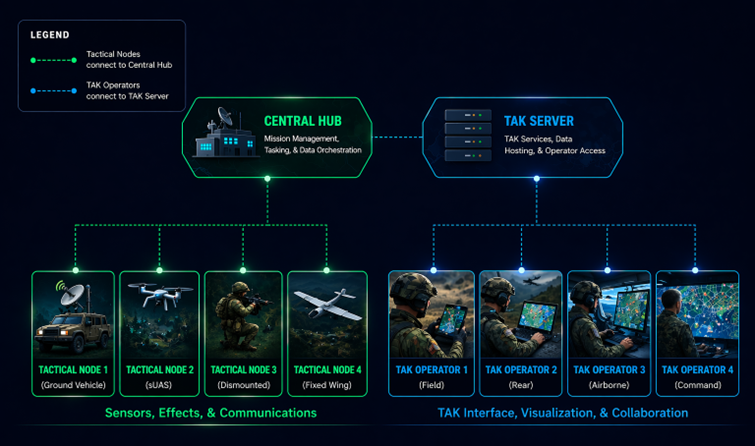
Fracture System Architecture

Deployment Options

FISSURE supports multiple deployment models depending on the intended workflow and operating environment:
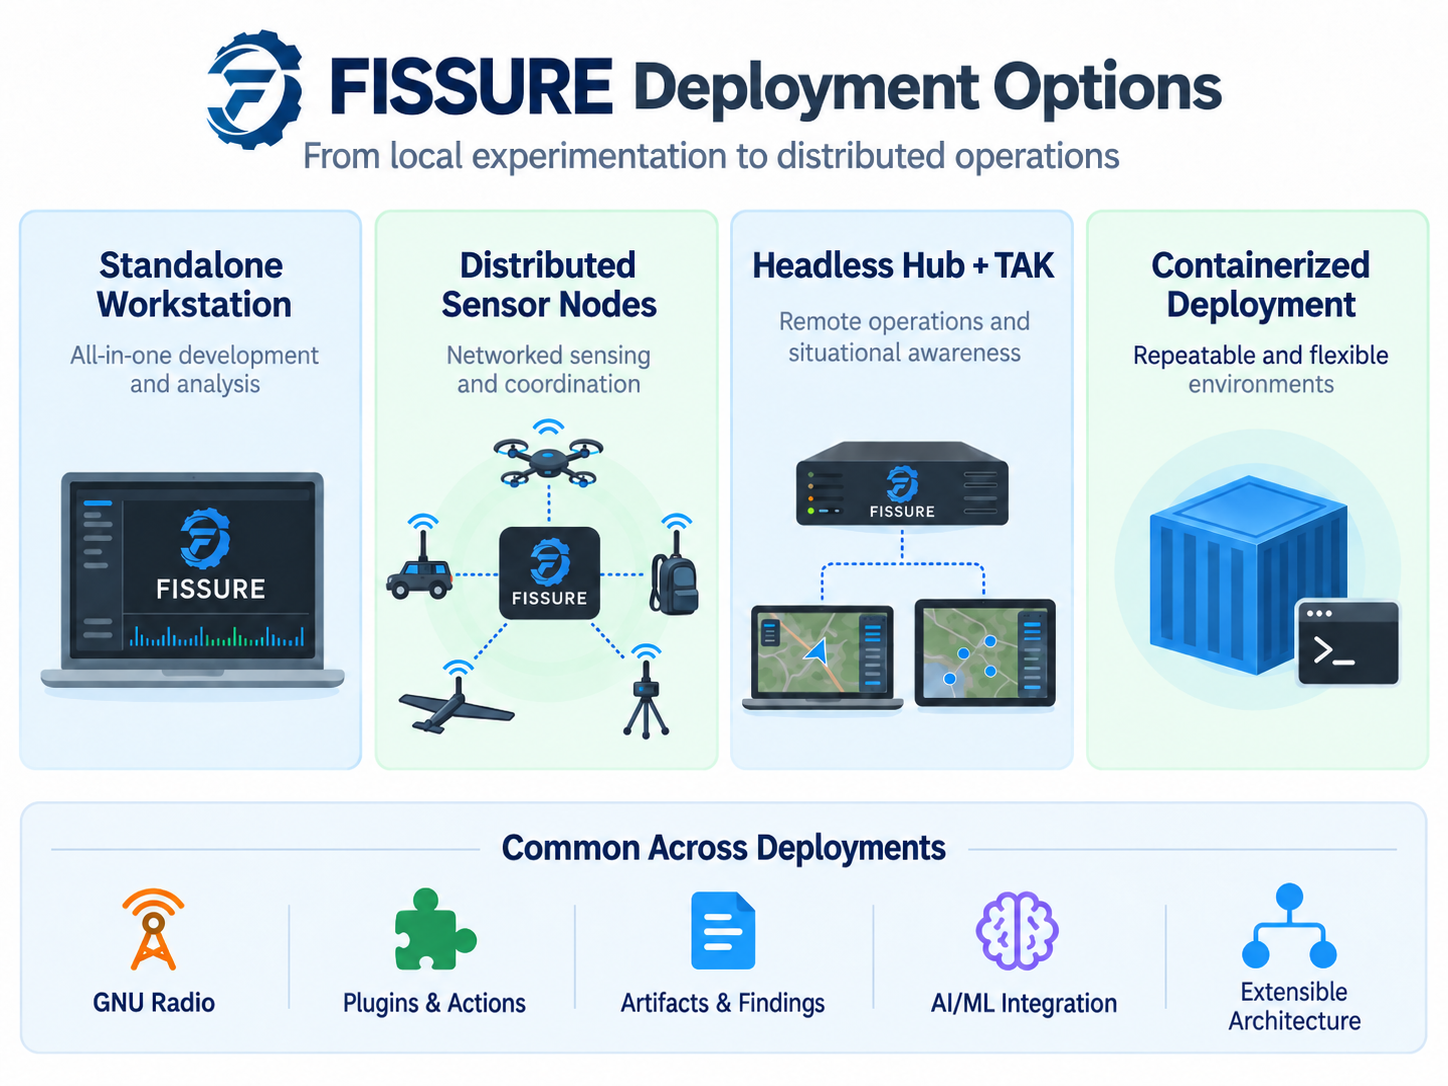
  • Standalone Workstation: Run the Dashboard, HIPRFISR, and a local Sensor Node on a single system for development, analysis, and experimentation.
  • Distributed Sensor Nodes: Run RF and plugin capabilities on remote systems while coordinating tasking, results, and data through a central hub.
  • Headless Hub: Run HIPRFISR and supporting services without the Dashboard for remote operations, TAK integration, and distributed deployments.
  • Containerized Deployment: Use Apptainer to build repeatable Dashboard, HIPRFISR, Sensor Node, Base, Full, or custom environments.
  • TAK-Integrated Operations: Share targets, detections, alerts, geolocation results, artifacts, and other operational information through ATAK, WinTAK, and TAK Server.

FISSURE deployment options

What's New

NEW

Connected Signal Analysis Workflows: FISSURE now connects survey, detection, capture, inspection, conditioning, feature extraction, classification, and protocol discovery through SOI-centered workflows with associated Artifacts and Findings.

NEW

도구 다운로드

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 궁극의 OSINT 툴킷: 조사 그래프, 신뢰도 점수 산정, 별칭 패밀리, 지도, 타임라인 및 보고서. 49개 모듈, 400개 이상 사이트, API 키 불필요.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # GhostLock 원탭 실행 앱 (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM 멀티 에이전트 자율 침투 테스트 플랫폼으로, 플래너/워커 에이전트, 자산 및 탐색 그래프, MITM 트래픽 기록, 취약점 재테스트 기능을 제공합니다.

    429
  • 4

    redforge

    cybersecurity91/redforge

    브라우저 측 레드 팀 툴킷으로, 정찰, 페이로드 생성, 자격 증명 공격, 암호화, 인코딩 및 참여 보고를 위한 102개의 오프라인 도구를 제공합니다.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI 네이티브 사이버보안을 위한 행동 체계—의도가 통제된 실행이 되고, 증거가 운영 메모리가 되며, 모든 운영이 다음 운영을 개선하는 곳.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    Shadowserver 보고서를 MongoDB로 수집하고 이를 대화형 지도, 분석, 발견 사항, 권고 및 경영진 대시보드로 재생하는 CSIRT 플랫폼입니다.

    256

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →