Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Social Engineering — 36페이지 | Kitploit
카테고리

Social Engineering

Tools for simulating human-based attacks (phishing, pretexting, baiting) and testing human factors in security.

Kitploit 추천
추천 도구

10 선택됨
social-engineer-toolkit preview#1

social-engineer-toolkit

GitHubtrustedsec/social-engineer-toolkit
15.2k4개월 전
gophish preview#2

gophish

GitHubgophish/gophish
14.1k2년 전
evilginx2 preview#3

evilginx2

GitHubkgretzky/evilginx2
15.5k4개월 전
Modlishka preview#4

Modlishka

GitHubdrk1wi/modlishka
5.4k2개월 전
muraena preview#5

muraena

GitHubmuraenateam/muraena
1.1k1년 전
wifiphisher preview#6

wifiphisher

GitHubwifiphisher/wifiphisher
14.8k5개월 전
zphisher preview#7

zphisher

GitHubhtr-tech/zphisher
16.6k2년 전
sherlock preview#9

sherlock

GitHubsherlock-project/sherlock
89.1k25일 전
maigret preview#10

maigret

GitHubsoxoj/maigret
36.5k11일 전
social-analyzer preview#11

social-analyzer

GitHubqeeqbox/social-analyzer
23.7k9개월 전
최신관련성인기최근 업데이트
729 결과
SOGo_web_mail-vulnerability-CVE-2025-50340 preview

SOGo_web_mail-vulnerability-CVE-2025-50340

GitHubmillad7/sogo_web_mail-vulnerability-cve-2025-50340

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail 사용자가 다른 사용자를 대신하여 이메일을 보낼 수 있도록 허용합니다.
vulnerability-analysisimpersonation-toolsweb-application-exploitation+3
1년 전
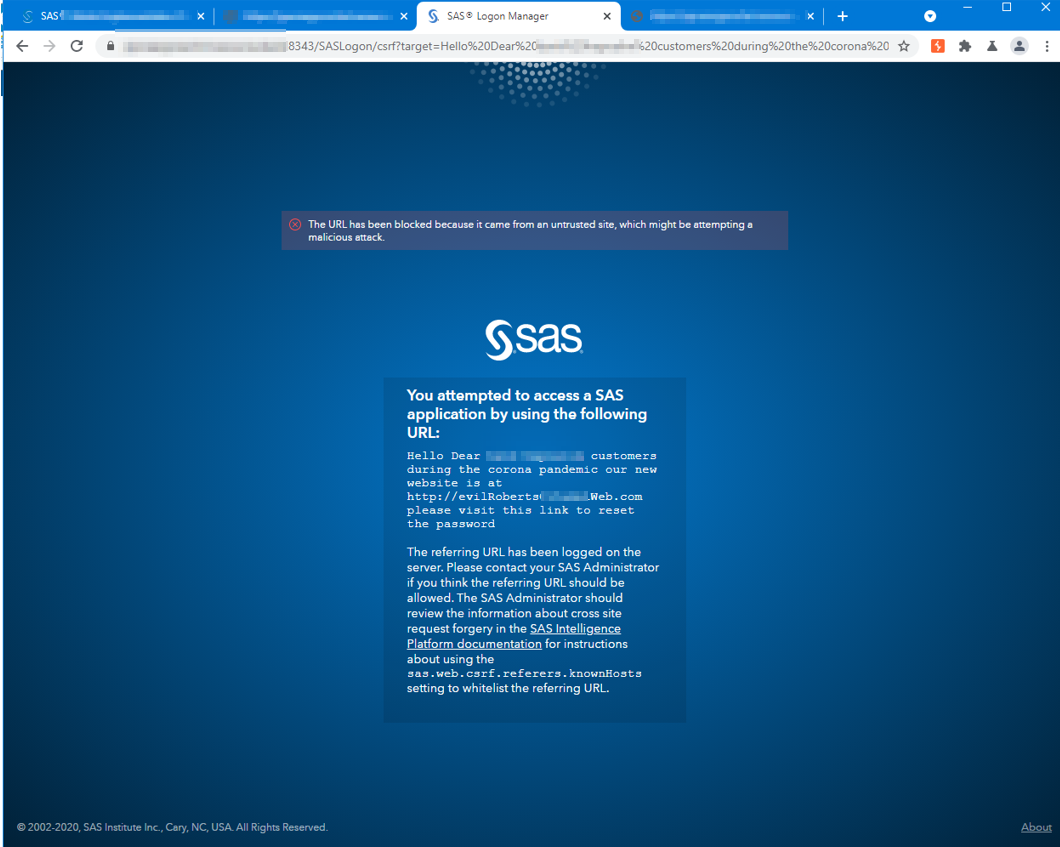
CVE-2022-25257 preview

CVE-2022-25257

GitHubpolling-repo-continua/cve-2022-25257

CVE-2022-25257에 대한 개념 증명 익스플로잇: SAS Logon 9.4에서 CSRF 파라미터 주입을 통해 피싱 공격을 위한 경고 메시지 스푸핑을 가능하게 함.
vulnerability-analysisexploitationweb-application-exploitation+2
4년 전
CVE-2022-2546 preview

CVE-2022-2546

GitHubopenxp-research/cve-2022-2546

All-in-One WP Migration < 7.63 - 인증되지 않은 반사형 XSS + CSRF
phishing-toolsvulnerability-analysisexploitation+3
2년 전
CVE-2025-51863 preview

CVE-2025-51863

GitHubsecsys-fdu/cve-2025-51863

ChatGPTUtil의 Self-XSS 취약점에 대한 개념 증명으로, 채팅 인터페이스에 붙여넣은 조작된 SVG 페이로드를 통해 쿠키 도용 및 계정 탈취를 시연합니다.
phishing-toolsvulnerability-analysisexploitation+2
1년 전
CVE-2023-0214 preview

CVE-2023-0214

GitHub0pts/cve-2023-0214

보안 웹 게이트웨이 10.2.11 - 교차 사이트 스크립팅 (XSS)

phishing-toolsvulnerability-analysisexploitation+3
8개월 전
FullscreenBrowserPhishing preview

FullscreenBrowserPhishing

GitHubgmh5225/fullscreenbrowserphishing

브라우저를 전체 화면 모드로 설정하여 수행하는 피싱의 PoC
phishing-toolsphishingweb-security+3
3년 전
JQueryingU preview

JQueryingU

GitHubsamsayen/jqueryingu

유효한 JQuery로, 시스템을 프로파일링하고 가짜 분석 GET 요청으로 서버에 정보를 반환합니다.
phishing-toolsreconnaissanceosint-social-engineering+2
7년 전
Invoke-LinkSpray preview

Invoke-LinkSpray

GitLabkevinjclark/invoke-linkspray

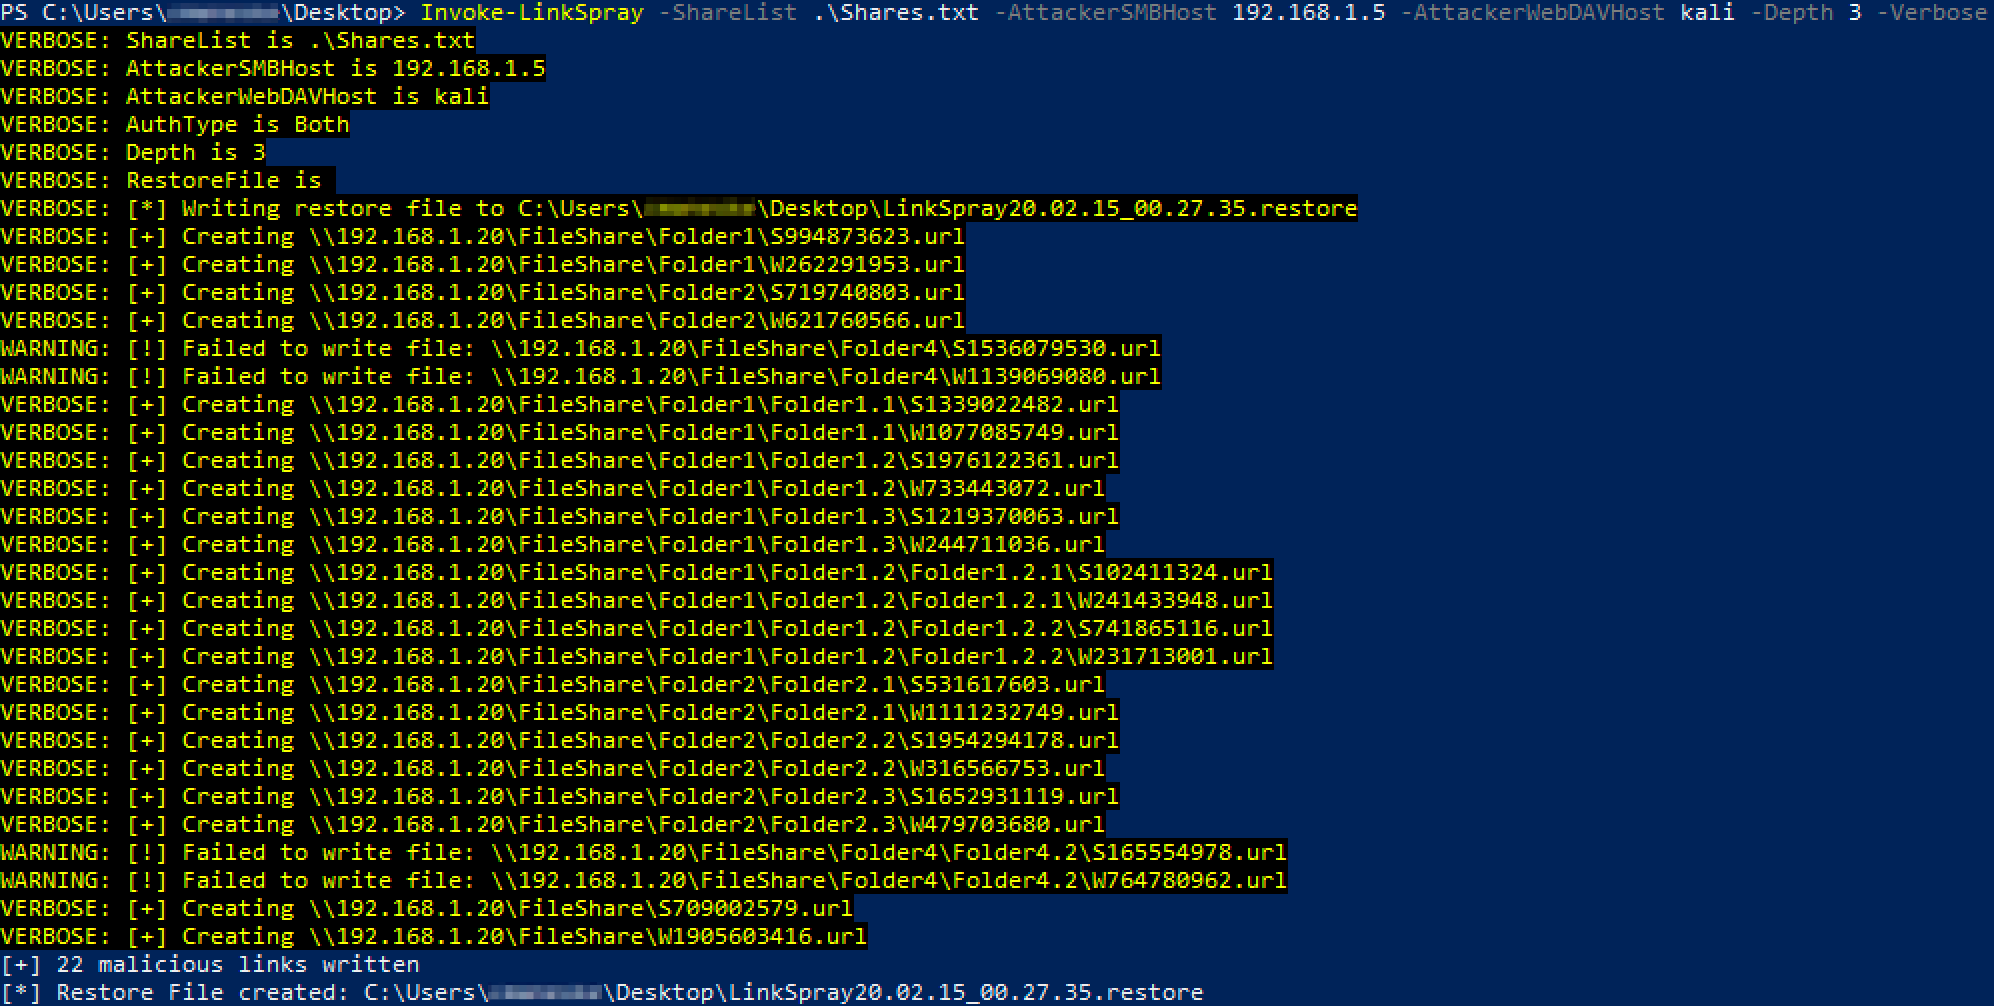
악성 SMB 또는 WebDAV 링크를 생성하여 NTLM 인증을 탈취하는 PowerShell 스크립트
phishingpenetration-testingsocial-engineering+2
6년 전
fluxion preview

fluxion

GitHubjas502n/fluxion

fluxion

wi-fi-auditingpassword-attacksphishing+4
8년 전
go-sherlock preview

go-sherlock

GitLabdrskelebones/go-sherlock

Go로 작성된 고성능 사용자 이름 검색 엔진. 수백 개의 소셜 네트워크 및 웹사이트를 스캔하여 주어진 사용자 이름과 연결된 계정을 발견하며, 원래 Sherlock보다 향상된 정확도와 속도를 제공합니다.
osintreconnaissanceinformation-gathering+2
4년 전
CVE-2020-10135-BIAS preview

CVE-2020-10135-BIAS

GitHubm4rm0k/cve-2020-10135-bias

CVE 2020-10135 일명 BIAS (블루투스 가장 공격)
bluetooth-securityexploitationimpersonation-tools+3
6년 전
LetterPress-1.2.1-Open-Redirection-Via-Html-Injection-Vulnerability preview

LetterPress-1.2.1-Open-Redirection-Via-Html-Injection-Vulnerability

GitHubsanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability

LetterPress 플러그인 <= 1.2.1은 HTML 인젝션 취약점에 취약하며, 이는 추가적으로 오픈 리다이렉션 취약점으로 이어질 수 있습니다.
phishing-toolsweb-application-exploitationpenetration-testing
5개월 전
CVE-2024-21413 preview

CVE-2024-21413

GitHubmseymend/cve-2024-21413

CVE-2024-21413 취약점을 이용한 로그인 정보 획득
exploitationinformation-gatheringphishing+2
2년 전
CVE-2024-37383-exploit preview

CVE-2024-37383-exploit

GitHubamirzargham/cve-2024-37383-exploit

Roundcube 메일 서버의 CVE-2024-37383 (저장형 XSS) 익스플로잇
phishing-toolspayload-generationexploitation+3
1년 전
CVE-2026-39047 preview

CVE-2026-39047

GitHubazhariramadhan/cve-2026-39047

프린터 보안 테스트를 위한 익스플로잇 프레임워크로, 원시 포트 9100을 통해 PCL 페이로드 전달, DoS 폭탄 공격, C2 QR 코드, 피싱 QR 코드, 그리고 은밀한 데이터 유출 마커 기능을 제공합니다.
reconnaissanceexploitationdata-exfiltration+4
6개월 전
Password-Analysis preview

Password-Analysis

GitHubam0nt31r0/password-analysis

비밀번호 목록을 엔트로피와 사전 기반 취약 비밀번호에 따라 분석하는 Go 스크립트입니다. 침투 테스트 및 피싱 캠페인에 유용합니다.
password-crackingphishing-toolspassword-attacks+1
4년 전
POC-CVE-2018-25031 preview

POC-CVE-2018-25031

GitHubgeozin/poc-cve-2018-25031

CVE-2018-25031(Swagger UI XSS)에 대한 개념 증명 익스플로잇으로, 조작된 configUrl/url 매개변수를 통해 인증 코드를 외부로 유출합니다.
phishing-toolsvulnerability-analysisexploitation+2
2년 전
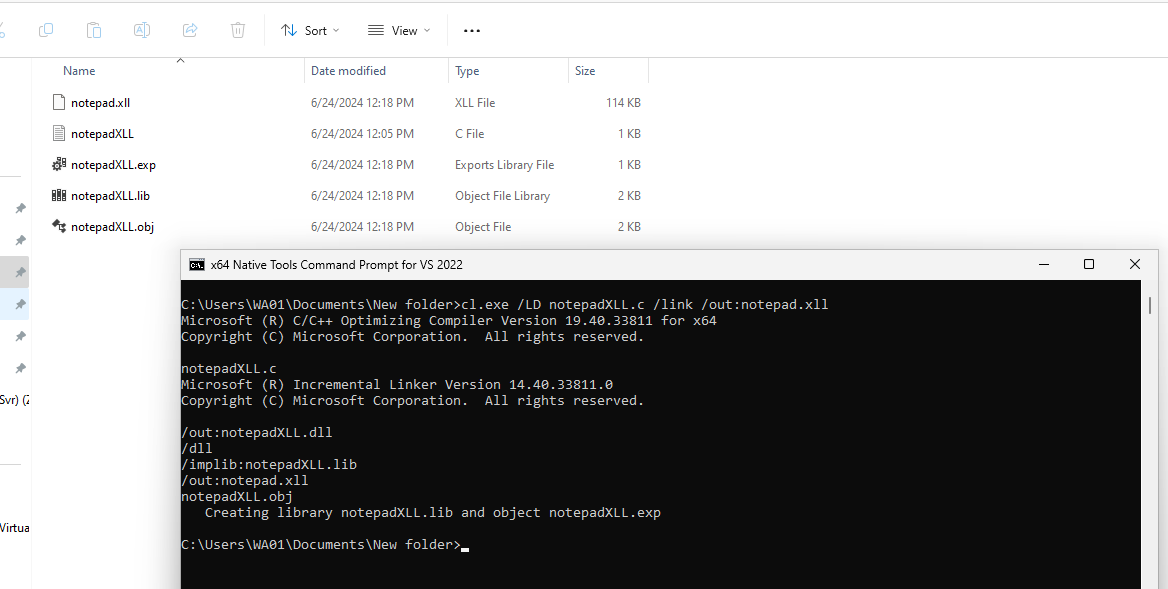
xll_windows_reverse_shell preview

xll_windows_reverse_shell

GitHubh3x0v3rl0rd/xll_windows_reverse_shell

xll windows 리버스 셸

phishing-toolsexploitationcommand-and-control+4
1년 전
이전1…353637…41다음