
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Post-Exploitation — 100페이지 | Kitploit
카테고리

Post-Exploitation

Tools for maintaining access, exploring, and expanding control within compromised systems and networks.

Kitploit 추천
추천 도구

10 선택됨
NetExec preview#1

NetExec

GitHubpennyw0rth/netexec
5.8k13시간 14분 전
impacket preview#2

impacket

GitHubfortra/impacket
16.0k15시간 31분 전
mimikatz preview#3

mimikatz

GitHubgentilkiwi/mimikatz
21.8k22시간 3분 전
PEASS-ng preview#4

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k1일 전
Rubeus preview#5

Rubeus

GitHubghostpack/rubeus
5.1k11개월 전
Seatbelt preview#6

Seatbelt

GitHubghostpack/seatbelt
4.7k1년 전
Empire preview#7

Empire

GitHubbc-security/empire
5.2k1개월 전
sliver preview#8

sliver

GitHubbishopfox/sliver
11.7k2일 전
LaZagne preview#10

LaZagne

GitHubalessandroz/lazagne
11.0k1년 전
PowerUpSQL preview#11

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1년 전
최신관련성인기최근 업데이트
6165 결과
loboguara preview

loboguara

GitHubolivsec/loboguara

악성 인프라를 식별하고 분석하기 위한 SSL 인증서 검색, 도메인/URL 스캐닝, 데이터 유출 모니터링, 추적 링크 생성 및 위협 피드 수집 기능을 제공하는 사이버 위협 인텔리전스 플랫폼입니다.
osintphishing-toolsvulnerability-scanners+6
731년 전
DiagTrackEoP preview

DiagTrackEoP

GitHubwh04m1001/diagtrackeop

DiagTrack RPC를 통해 SeImpersonate를 악용하는 Windows 권한 상승 익스플로잇으로, Secondary Logon을 사용하여 INTERACTIVE 토큰을 얻고 SYSTEM 권한을 획득합니다.
privilege-escalationexploitationpost-exploitation+3
884년 전
zygote-injection-toolkit preview

zygote-injection-toolkit

GitHubanonymous941/zygote-injection-toolkit

Android Zygote 주입을 악용하는 명령줄 유틸리티 (CVE-2024-31317)
android-securityprivilege-escalationexploitation+5
6010개월 전
Get-RBCD-Threaded preview

Get-RBCD-Threaded

GitHubfatrodzianko/get-rbcd-threaded

Active Directory 환경에서 리소스 기반 제한 위임 공격 경로를 발견하는 도구
privilege-escalationreconnaissancepenetration-testing+1
1335년 전
CVE-2018-8897 preview

CVE-2018-8897

GitHubnmulasmajic/cve-2018-8897

POP/MOV SS(CVE-2018-8897) 취약점을 구현하여 머신을 버그체크(로컬 DoS)합니다.
privilege-escalationvulnerability-analysisexploitation+3
818년 전
libreoffice-remote-arbitrary-file-disclosure preview

libreoffice-remote-arbitrary-file-disclosure

GitHubjollheef/libreoffice-remote-arbitrary-file-disclosure

LibreOffice 원격 임의 파일 공개 취약점의 개념 증명
vulnerability-analysisexploitationdata-exfiltration+1
968년 전
BloodfangC2 preview

BloodfangC2

GitHubzarkones/bloodfangc2

Windows용 최신 PIC 임플란트 (64 & 32비트)
shellcodepost-exploitationcommand-and-control+4
1051년 전
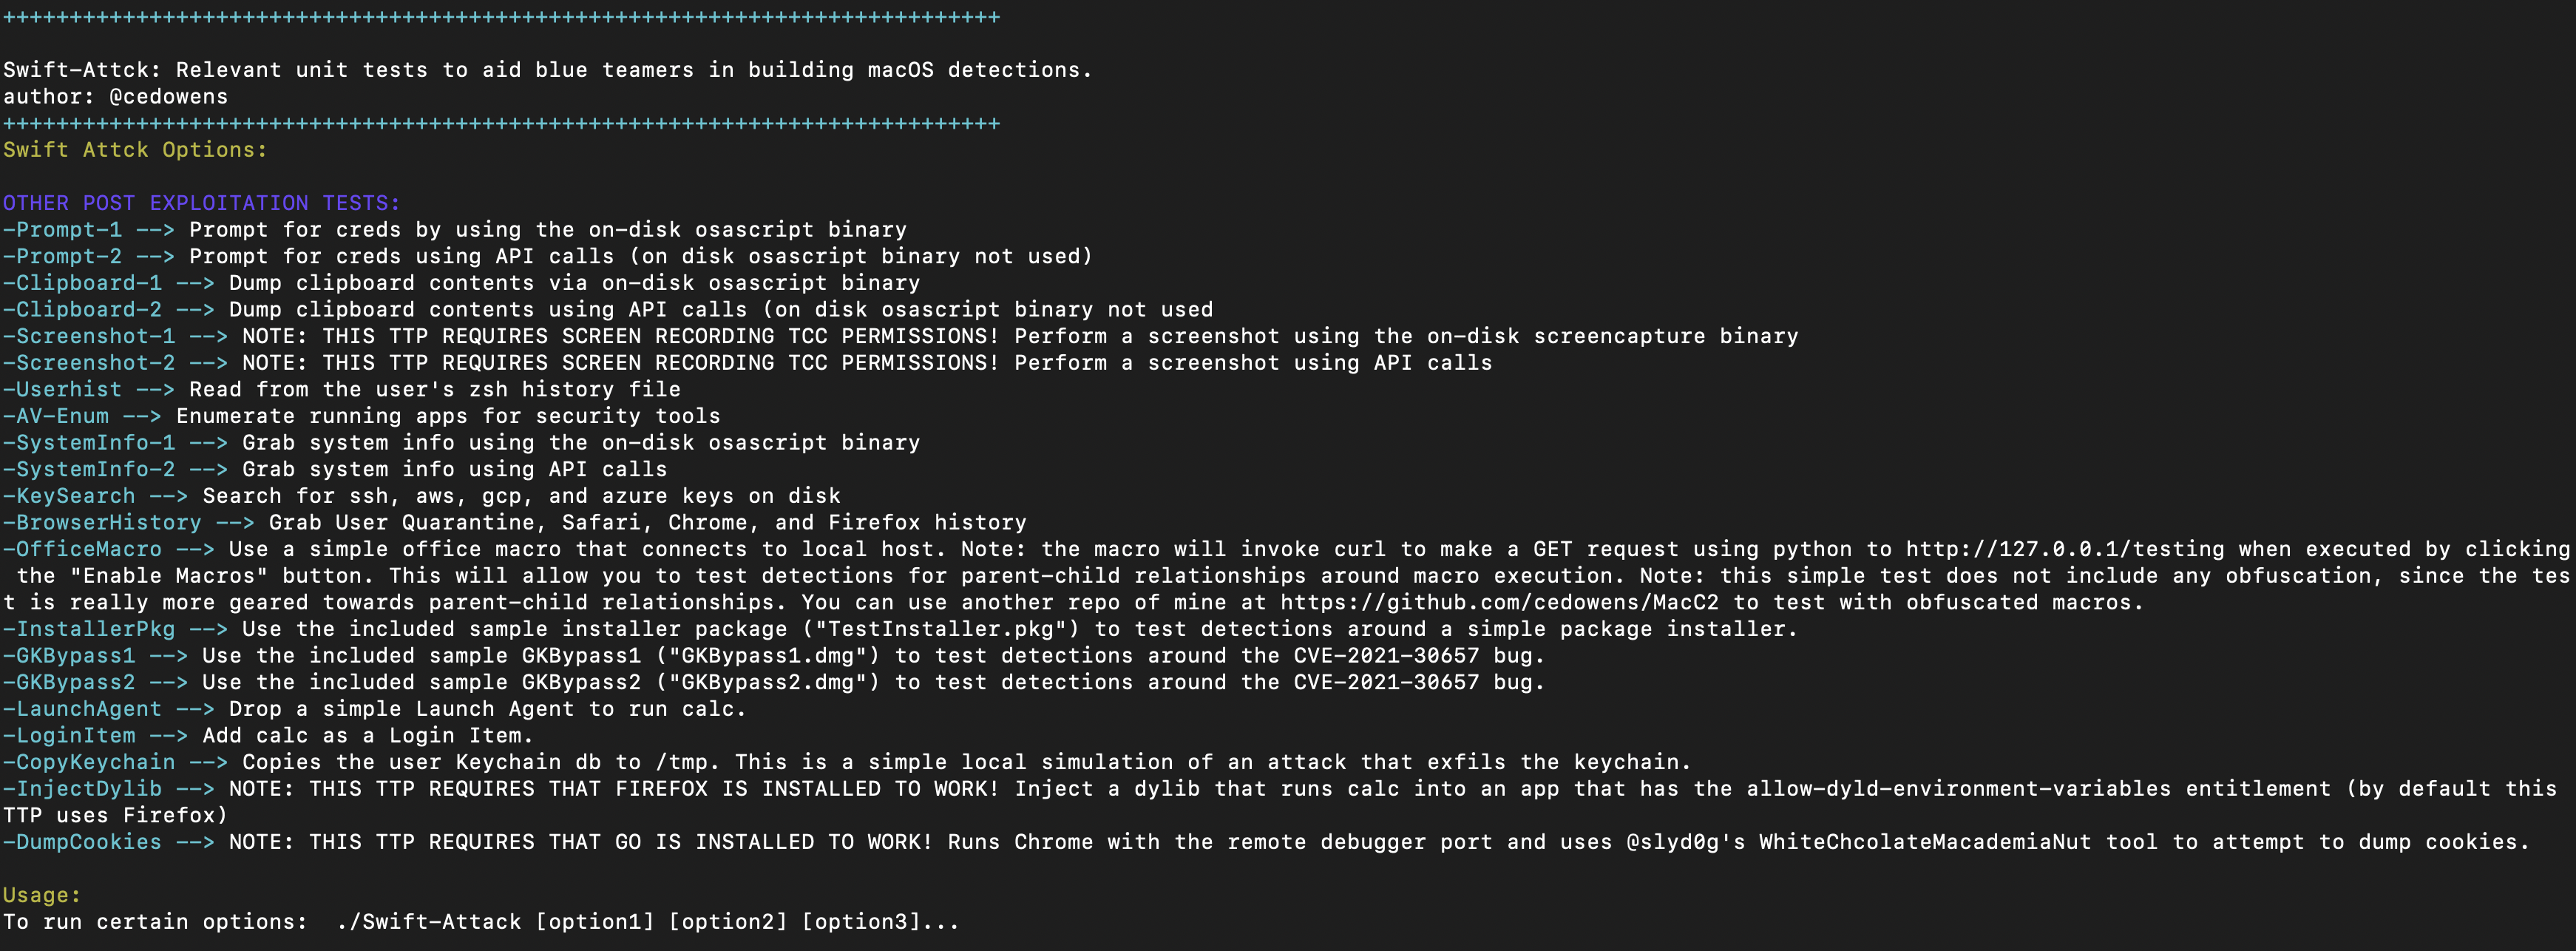
Swift-Attack preview

Swift-Attack

GitHubcedowens/swift-attack

블루 팀이 일반적인 macOS 사후 공격 방법에 대한 탐지를 구축하는 데 도움이 되는 단위 테스트.
post-exploitationeducationred-teaming+1
1073년 전
Reg1c1de preview

Reg1c1de

GitHubdeadjakk/reg1c1de

레지스트리 내 잠재적 권한 상승 경로를 찾기 위해 C#으로 작성된 레지스트리 권한 스캐너
privilege-escalationvulnerability-scannersconfiguration-auditing
865년 전
lenovo_exec preview

lenovo_exec

GitHubestimated1337/lenovo_exec

임의 커널 코드 실행 기능을 갖춘 CVE-2022-3699
privilege-escalationvulnerability-analysisexploitation+1
723년 전
NtDumpBOF preview

NtDumpBOF

GitHubdeh00ni/ntdumpbof

메모리에서 LSASS minidump를 생성하고 C2 콜백을 통해 이를 유출하여 Mimikatz 또는 pypykatz로 오프라인 자격 증명을 파싱할 수 있게 해주는 Cobalt Strike BOF입니다.
data-exfiltrationpost-exploitationred-teaming
1002년 전
MS16-032 preview

MS16-032

GitHubzcgonvh/ms16-032

MS16-032(CVE-2016-0099) 서비스 전용
privilege-escalationvulnerability-analysisexploitation+1
839년 전
CIFSwitch preview

CIFSwitch

GitHubmanizada/cifswitch

CVE-2026-46243에 대한 개념 증명 익스플로잇으로, 가짜 NSS 라이브러리와 네임스페이스 조작을 활용하여 cifs.upcall을 통해 권한을 상승시킵니다.
privilege-escalationvulnerability-analysisexploitation+3
694개월 전
EasyTokens preview

EasyTokens

GitHubsecdev02/easytokens

Kali365 - EvilTokens Replica
osint-social-engineeringinformation-gatheringpost-exploitation+7
723개월 전
android_autorooter preview

android_autorooter

GitHubscs-labrat/android_autorooter

CVE-2024-0044 취약점을 이용하여 Android 12 및 13의 앱에서 민감한 사용자 데이터를 원격으로 유출합니다
android-securityexploit-frameworkspayload-generation+5
762년 전
process-enumeration-stealth preview

process-enumeration-stealth

GitHublloydlabs/process-enumeration-stealth

NTFS를 통해 NtQueryInformationFile을 사용하여 PID를 나열하는 스텔스 Windows 프로세스 열거 PoC로, 표준 모니터링 API를 우회하고 레드 팀 작전 중 EDR 회피를 가능하게 합니다.
reconnaissanceids-ips-evasioninformation-gathering+2
842년 전
SliverMirage preview

SliverMirage

GitHubdaniomass/slivermirage

Sliver C2용 Crystal Palace PICO 로더 이중 계층 AMSI 우회, ETW 무력화, AES-256-CBC 암호화 페이로드, 6가지 전달 변형
exploitationpost-exploitationmalware-analysis+4
482개월 전
plague preview

plague

GitHubconnectedlucy/plague

EDR용 기본 탐지 규칙

defensive-toolsconfiguration-auditingdata-exfiltration+4
972년 전
이전1…99100다음









