GitHub Actionsのセキュリティスキャンを実行するGitHub Actionです。
このアクションはoctoscanに基づいています
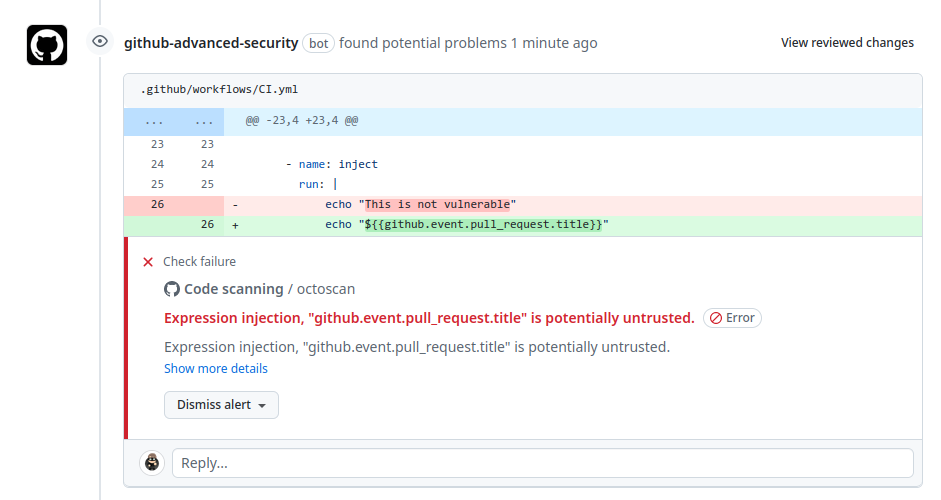

このアクションの基本的な使用例を以下に示します。これはpushイベントとpull_requestイベントの両方で機能します。
---
name: Octoscan

on:
  workflow_dispatch:
  pull_request:
    paths:
      - '.github/workflows/*'
  push:
    paths:
      - '.github/workflows/*'

permissions:
  security-events: write
  actions: read
  contents: read

jobs:
  octoscan:
    runs-on: ubuntu-latest
    steps:
      - name: Checkout code
        uses: actions/checkout@v4

      - id: octoscan
        name: Run octoscan
        uses: synacktiv/action-octoscan@v1

      - name: Upload SARIF file to GitHub
        uses: github/codeql-action/upload-sarif@v3
        with:
          sarif_file: "${{steps.octoscan.outputs.sarif_output}}"
          category: octoscan
このアクションは実行時に releases から octoscan をダウンロードするため、synacktiv/action-octoscan@v1 は常に octoscan の最新リリース を実行し、更新する必要はありません。
実行を再現するには、version 入力で octoscan を、コミット SHA でアクションを固定します:
- uses: synacktiv/action-octoscan@<commit sha>
  with:
    version: v0.1.7
バイナリはリリースの SHA256SUMS で検証されます(それらが存在する前に公開されたリリースは対象外です)。
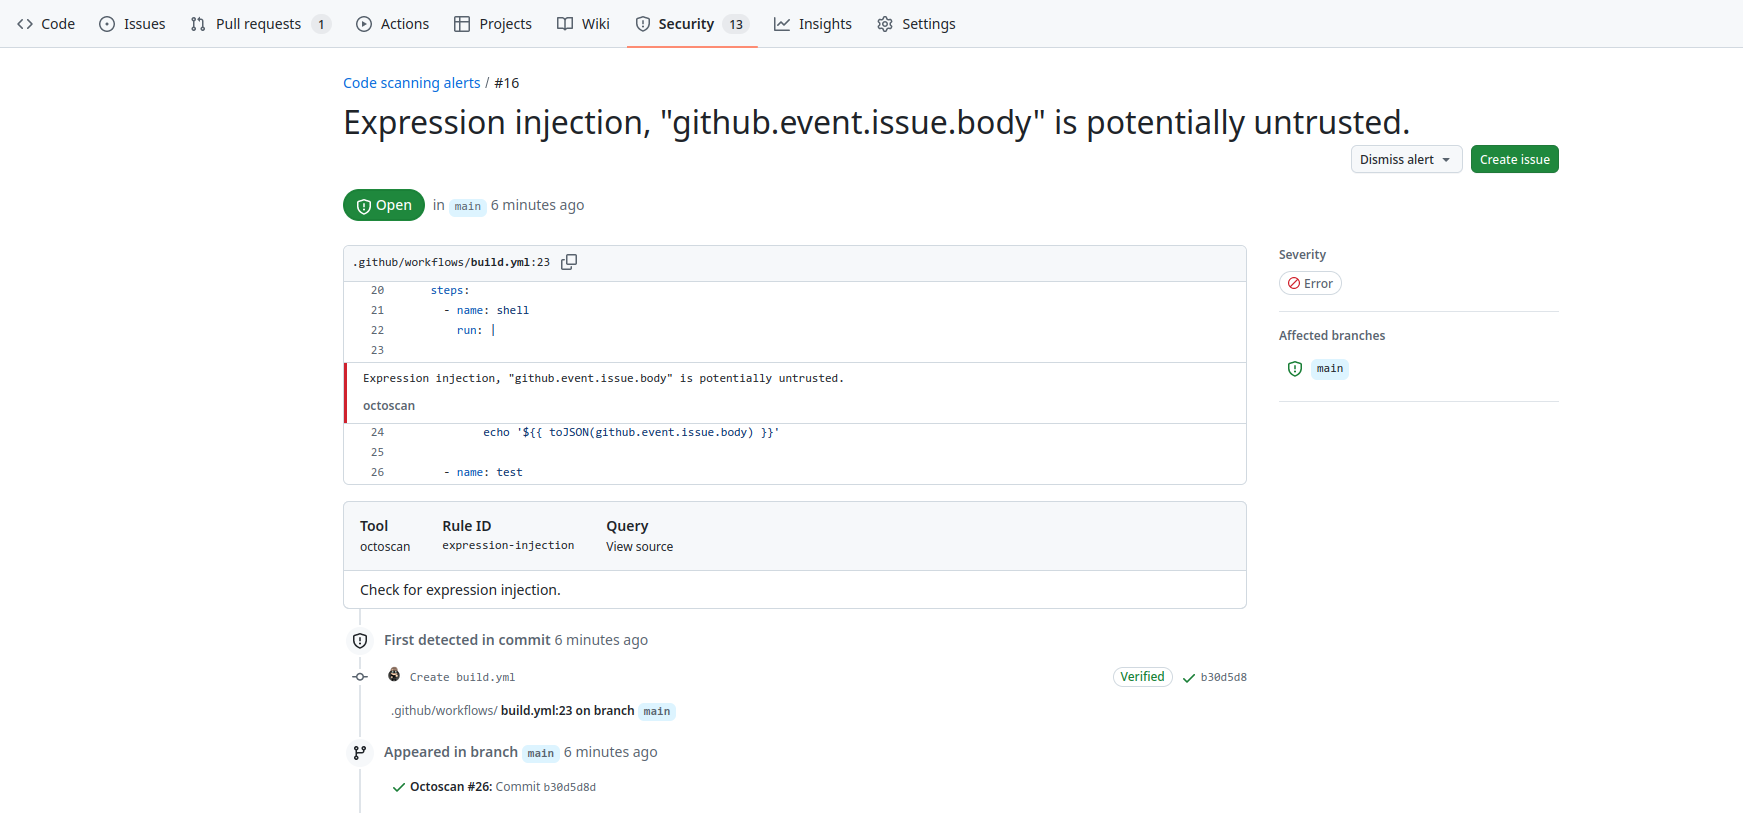
対象リポジトリへの書き込み権限がある場合、セキュリティ結果はコードセキュリティタブで確認できます:
またはプルリクエスト内で直接確認できます:
inputs は octoscan のオプションに基づいており、こちらで確認できます。
以下は step.with キーとして任意指定できます:



