

AWSリソースをローカルファイルシステムとしてマウントし、grep、diff、catなどの標準的なUnixツールを使用してインフラストラクチャの探索、セキュリティ監査、設定分析を行うことができます。
AWS をファイルシステムとして使う。
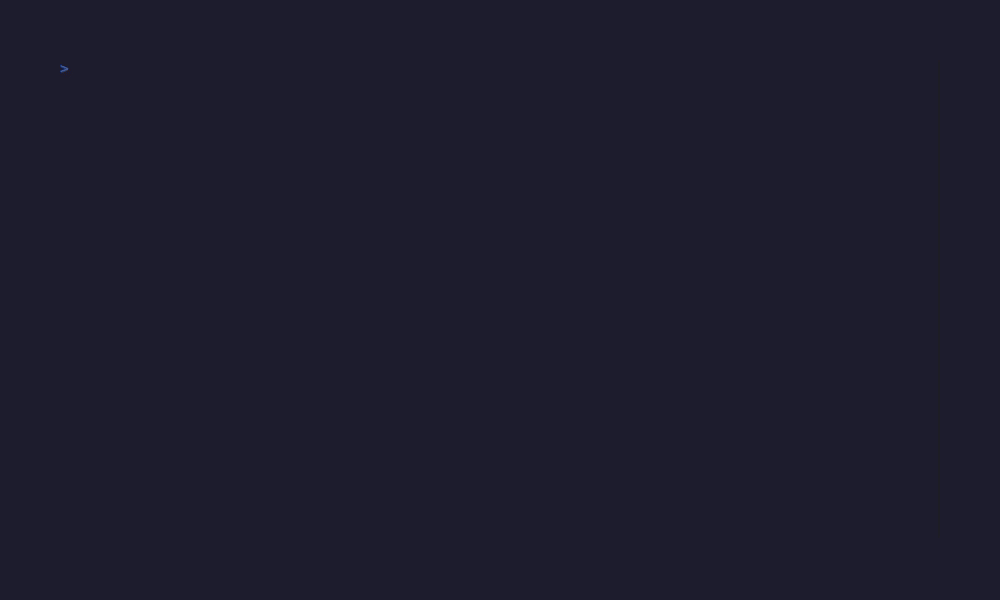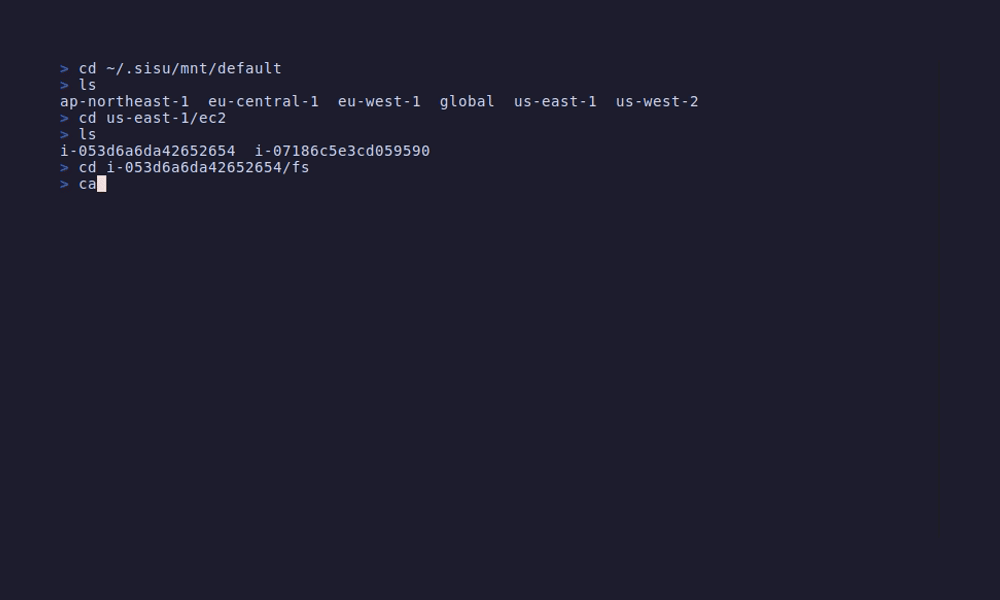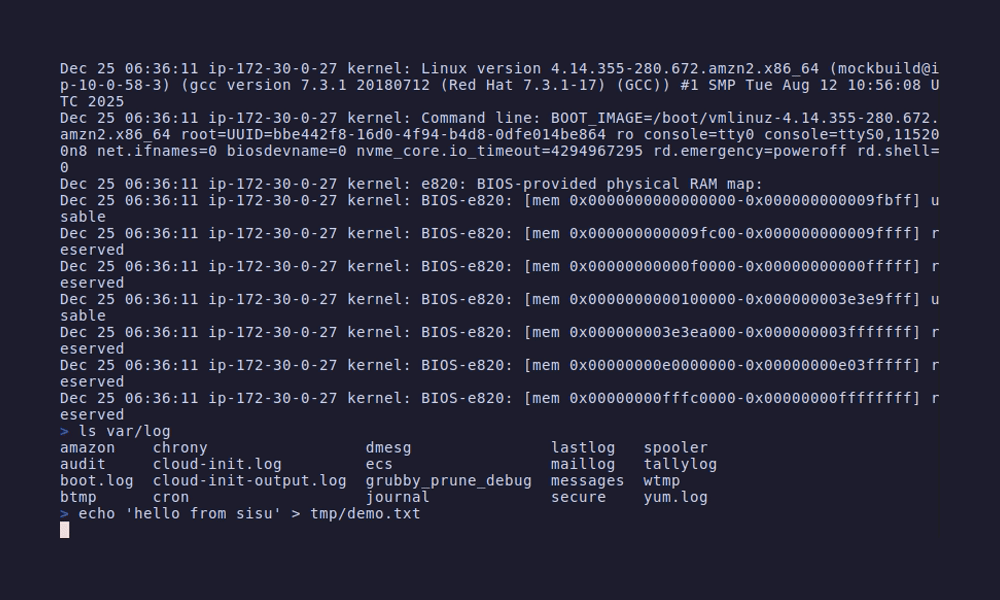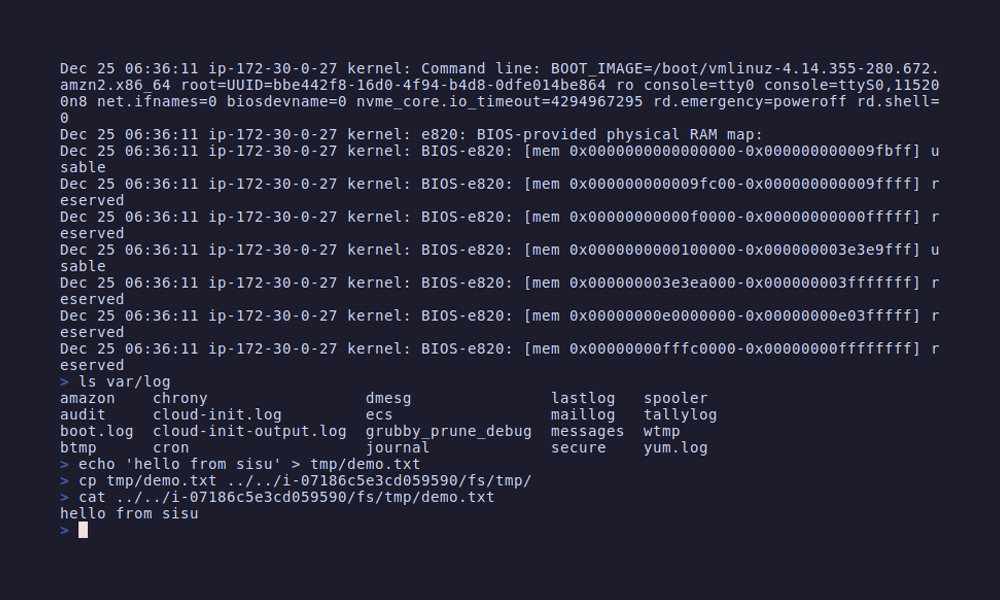
このように:
grep -l "AdministratorAccess" iam/users/*/policies.json
この代わりに:
aws iam list-users --query 'Users[].UserName' --output text | \
  xargs -I{} sh -c 'aws iam list-attached-user-policies --user-name {} --query "AttachedPolicies[].PolicyArn" --output text' | \
  grep AdministratorAccess
sisu は AWS リソースをローカルファイルシステムとしてマウントします。JSON や AWS CLI に煩わされる代わりに、使い慣れたツール - grep、cat、diff、vim - を使用できます。
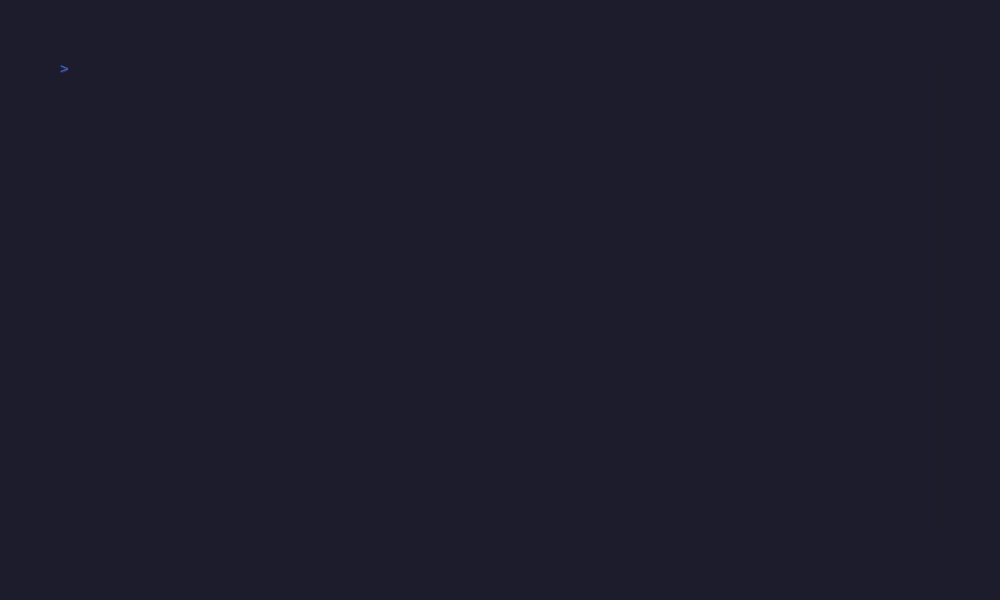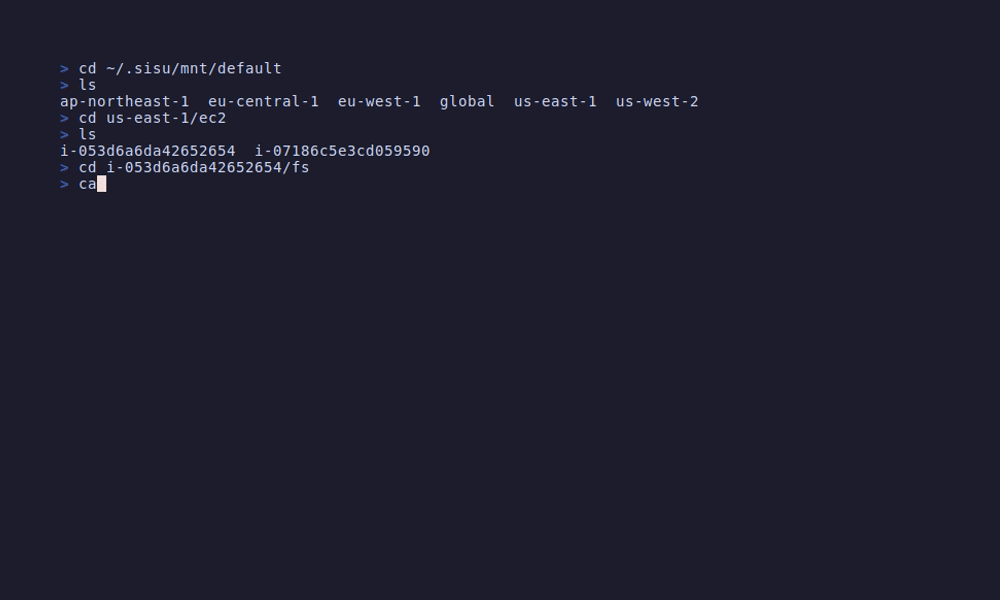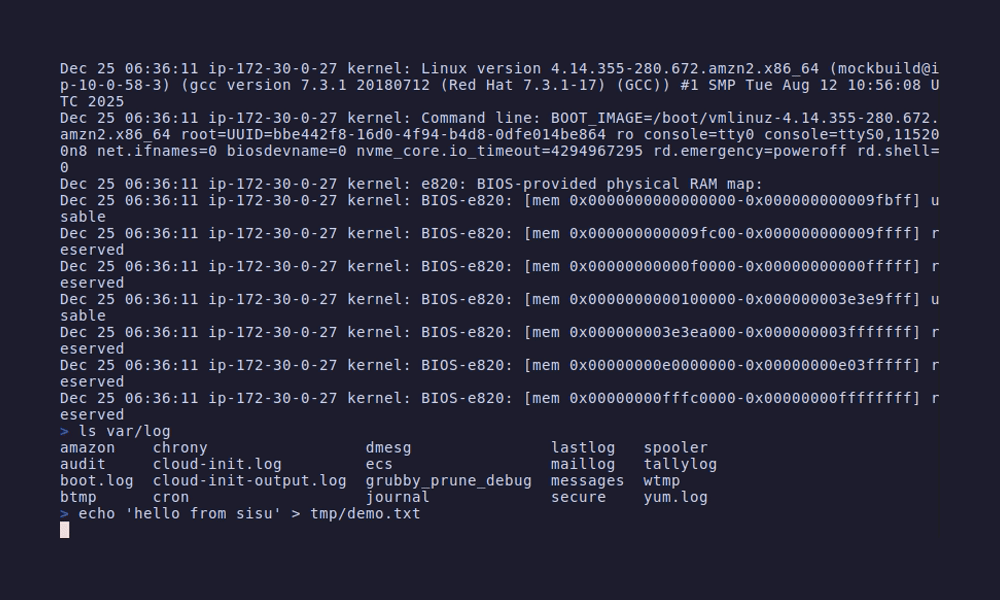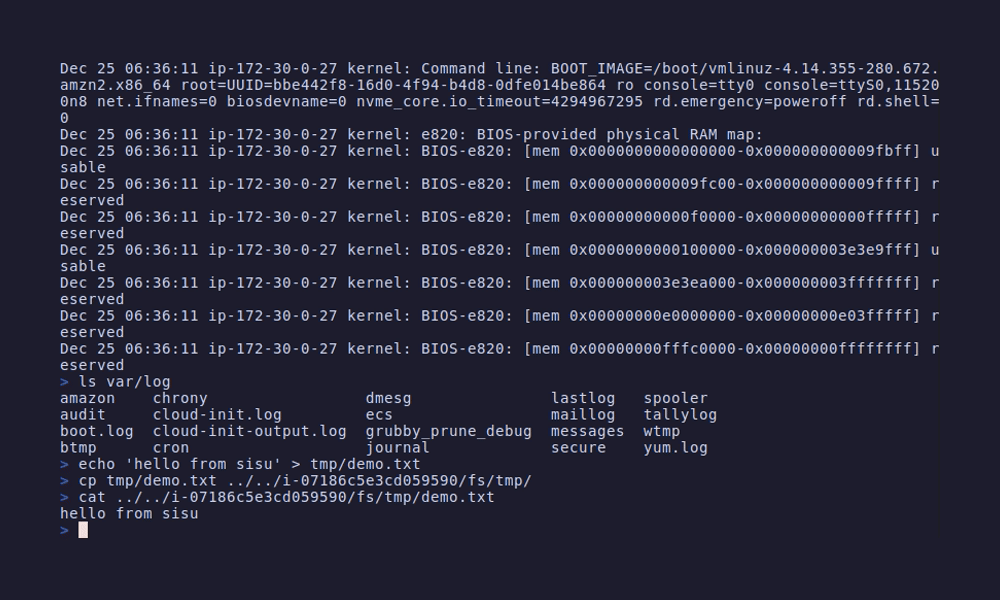
設計上 AI フレンドリー: AI ツールはサーバーに SSH したり、対話型の AWS CLI セッションを実行したりできません。しかし sisu を使えば、AWS インフラ全体がシンプルなファイルパスになり、あらゆる AI が読めるようになります。リモートの EC2 ファイルシステムには ec2/<instance>/fs/ でアクセスでき、/var/log、/etc、そしてインスタンス上のあらゆるファイルを SSH なしで AI が閲覧できます。
現在は S3、SSM、IAM、VPC、Lambda、EC2、ECS、CloudFront、Secrets Manager、Route 53、CloudWatch Logs に対応しています。
go install github.com/semonte/sisu@latest
FUSE が必要です:
sudo apt install fuse    # Ubuntu/Debian
sudo yum install fuse    # RHEL/CentOS
sisu
これで開始です。AWS が手のひらに乗ります:
~/.sisu/mnt/
├── default/              # AWS profile
│   ├── global/           # IAM, S3, Route 53 (region-independent)
│   │   ├── iam/
│   │   ├── route53/
│   │   └── s3/
│   ├── us-east-1/        # Regional services
│   │   ├── cloudfront/
│   │   ├── ec2/
│   │   ├── ecs/
│   │   ├── lambda/
│   │   ├── logs/
│   │   ├── secrets/
│   │   ├── ssm/
│   │   └── vpc/
│   └── eu-west-1/
│       └── ...
├── prod/                 # Other profiles from ~/.aws/credentials
└── staging/
終了したら exit と入力します。
# Who has admin access?
grep -l "AdministratorAccess" */global/iam/users/*/policies.json

# Security groups with SSH open
grep -r '"FromPort": 22' */us-east-1/vpc/*/security-groups/

# Roles that Lambda can assume
grep -l "lambda.amazonaws.com" */global/iam/roles/*/info.json

# Secrets in SSM?
grep -r "password" */us-east-1/ssm/

# Lambda functions with secrets in env vars
grep -r "PASSWORD\|SECRET\|API_KEY" */us-east-1/lambda/*/env.json

# Functions using deprecated runtimes
grep -r "python3.8\|nodejs16" */*/lambda/*/config.json

# EC2 instances with public IPs
grep -r "PublicIpAddress" */*/ec2/*/info.json

# Find stopped instances (wasting money?)
grep -r '"Name": "stopped"' */*/ec2/*/info.json

# Connect to an EC2 instance via SSM (no SSH keys needed!)
./default/us-east-1/ec2/i-abc123/connect

# View EC2 boot logs and kernel messages
cat default/us-east-1/ec2/i-abc123/console.log

# View all secrets
ls */us-east-1/secrets/

# Read a secret value
cat default/us-east-1/secrets/myapp/database/value

# List all DNS zones
ls */global/route53/

# View DNS records for a zone
cat default/global/route53/example.com/records.json

# Find all CNAME records
grep -r '"Type": "CNAME"' */global/route53/*/records.json

# Grep recent logs for errors
grep -i "error" default/us-east-1/logs/aws/lambda/my-function/latest.log

# View all log groups
ls */us-east-1/logs/

# List log streams (shows 20 most recent)
ls default/us-east-1/logs/aws/lambda/my-function/

# View events from a specific stream
cat default/us-east-1/logs/aws/lambda/my-function/2024_01_15_abc123/events.log

# ECS: Browse clusters, services, and tasks
ls default/us-east-1/ecs/my-cluster/my-service/
cat default/us-east-1/ecs/my-cluster/my-service/logs/latest.log

# CloudFront: View distributions and functions
ls default/us-east-1/cloudfront/distributions/
cat default/us-east-1/cloudfront/functions/my-auth/code.js

# S3: Check bucket policies and access settings
cat default/global/s3/my-bucket/.meta/policy.json
cat default/global/s3/my-bucket/.meta/public-access-block.json
# Compare IAM roles between accounts
diff prod/global/iam/roles/api/info.json staging/global/iam/roles/api/info.json

# Security group drift between regions
diff default/us-east-1/vpc/vpc-xxx/security-groups/sg-xxx.json default/eu-west-1/vpc/vpc-yyy/security-groups/sg-yyy.json

# Lambda config differences
diff prod/us-east-1/lambda/my-func/config.json staging/us-east-1/lambda/my-func/config.json
# Pretty print with jq
cat default/global/iam/roles/my-role/info.json | jq '.AssumeRolePolicyDocument'

# Count your roles
ls default/global/iam/roles/ | wc -l

# Find untagged resources
cat default/us-east-1/vpc/vpc-xxx/info.json | jq 'select(.Tags == null)'

# List all Lambda runtimes in use
grep -h "Runtime" */*/lambda/*/config.json | sort | uniq -c
cat default/us-east-1/ssm/myapp/database-url          # read
echo "postgres://prod:5432" > default/us-east-1/ssm/database-url  # write
vim default/us-east-1/ssm/myapp/config                # edit
cp local.txt default/global/s3/my-bucket/backup/
cat default/global/s3/my-bucket/logs/app.log | grep ERROR
rm default/global/s3/my-bucket/old-file.txt
sisu                                    # Start at root
sisu --profile prod                     # Start in prod/
sisu --profile prod --region us-east-1  # Start in prod/us-east-1/
sisu stop                               # Unmount
sisu --debug                            # Debug logging
| サービス | 読み取り | 書き込み | 削除 |
|---|---|---|---|
| S3 (オブジェクト、バケットポリシー、アクセス設定) | ✓ | ✓ | ✓ |
| SSM Parameter Store | ✓ | ✓ | ✓ |
| IAM (ユーザー、ロール、ポリシー、グループ) | ✓ | - | - |
| VPC (サブネット、セキュリティグループ、ルート) | ✓ | - | - |
| Lambda (設定、ポリシー、環境変数、ログ) | ✓ | - | - |
| EC2 (インスタンス、セキュリティグループ、タグ、ログ、リモート fs) | ✓ | - | - |
| ECS (クラスター、サービス、タスク、ログ) | ✓ | - | - |
| CloudFront (ディストリビューション、関数、ログ) | ✓ | - | - |
| Secrets Manager | ✓ | - | - |
| Route 53 (ゾーン、レコード) | ✓ | - | - |
| CloudWatch Logs | ✓ | - | - |
ログストリームの events.log ファイルは、全体をメモリに読み込むのではなく、AWS から遅延ストリーミングされます:
cat、grep、head、less で使用できます# Fetches only enough batches to find the match
grep "ERROR" .../my-stream/events.log
# Fetches just the first batch
head -50 .../my-stream/events.log
# Scroll through with on-demand loading
less .../my-stream/events.log
# Will fetch all events
cat .../my-stream/events.log | wc -l
注意: tail はファイルの末尾をシークするため、ストリーミングファイルでは正しく動作しません。実際のファイルサイズは完全に読み込まれるまで不明だからです。回避策として cat ... | tail を使用してください。
各サービスには、リソース直下にログがあります。ロググループを探し回る必要はありません:
# Lambda function logs
cat default/us-east-1/lambda/my-function/logs/latest.log

# EC2 instance logs (searches for log groups containing instance ID)
cat default/us-east-1/ec2/i-abc123/logs/latest.log

# ECS service logs
cat default/us-east-1/ecs/my-cluster/my-service/logs/latest.log

# CloudFront function logs
cat default/us-east-1/cloudfront/functions/my-auth/logs/latest.log
統合ログはすべてストリーミングを使用します。読み進めるとイベントをオンデマンドで取得します。
ECS クラスター、サービス、タスクを参照します:
