
 fr0gger/iatelligence
IATelligenceは、PEファイルのIATを抽出し、GPTにAPIと関連するATT&CKマトリックスについての詳細情報をリクエストするPythonスクリプトです。

IATelligence は、PEファイルからインポート アドレス テーブル(IAT)を抽出し、OpenAI の GPT-3 モデルを使用して、ファイルがインポートする各 Windows API に関する詳細を提供する Python スクリプトです。このスクリプトは、関連する MITRE ATT&CK テクニックを検索し、攻撃者がその API をどのように使用する可能性があるかを説明します。
また、ファイルのハッシュを表示し、GPT-3 リクエストのコストを見積もります。IATelligence は、マルウェア解析に GPT-3 を使用し、IAT に基づいてマルウェアの動作を迅速に評価するための概念実証です。
以下は、得られる結果の簡単な例です。IAT のサイズによっては、リクエストに時間がかかる場合があることに注意してください。
このツールを実行するには、OpenAi API へのアクセスが必要です。その後、スクリプトを変更して独自の API キーを追加する必要があります。
# Authenticate with the OpenAI API
openai.api_key = ""
また、依存関係をインストールする必要があります。
pip install -r requirements.txt
ツールを実行するには、スクリプトの引数として PE ファイルを指定するだけです。
python iatelligence.py sample.exe
スクリプトは、ハッシュとリクエストの推定コストも計算します。
[+] IAT Request from the file: .\sample.exe
[+] 33 functions will be requested to GPT!
[+] MD5: 2f82623f9523c0d167862cad0eff6806
[+] SHA1: 5d77804b87735e66d7d1e263c31c4ef010f16153
[+] SHA256: 9c2c8a8588fe6db09c09337e78437cb056cd557db1bcf5240112cbfb7b600efb
[+] Imphash: 8eeaa9499666119d13b3f44ecd77a729
[!] Estimated cost of requests: $0.0693
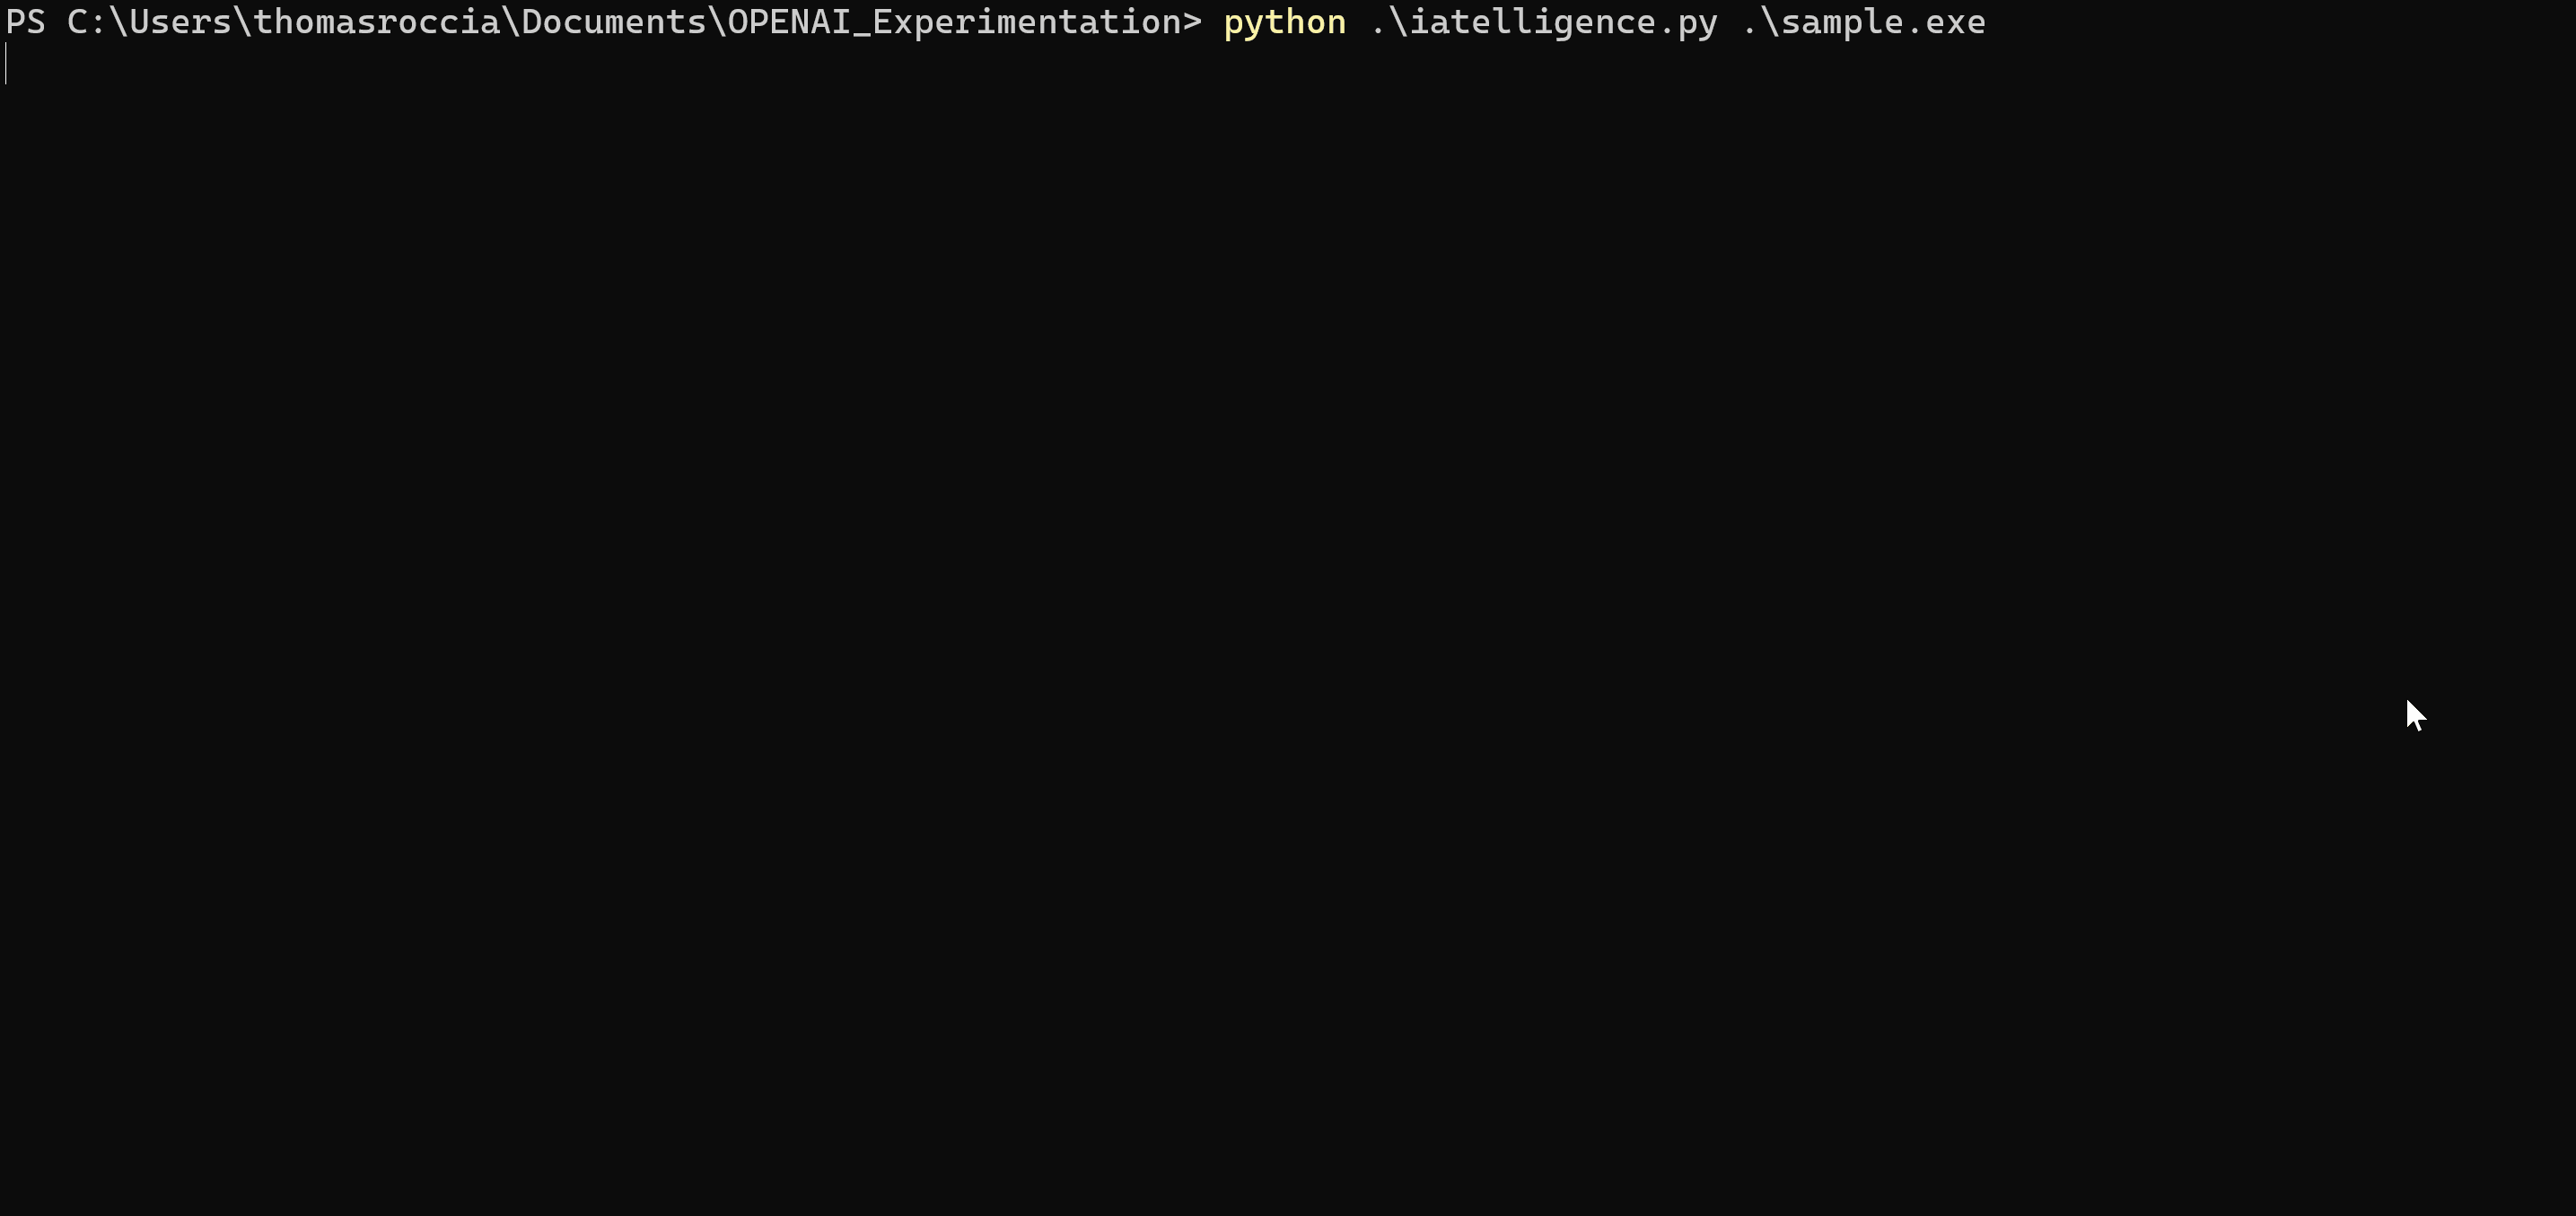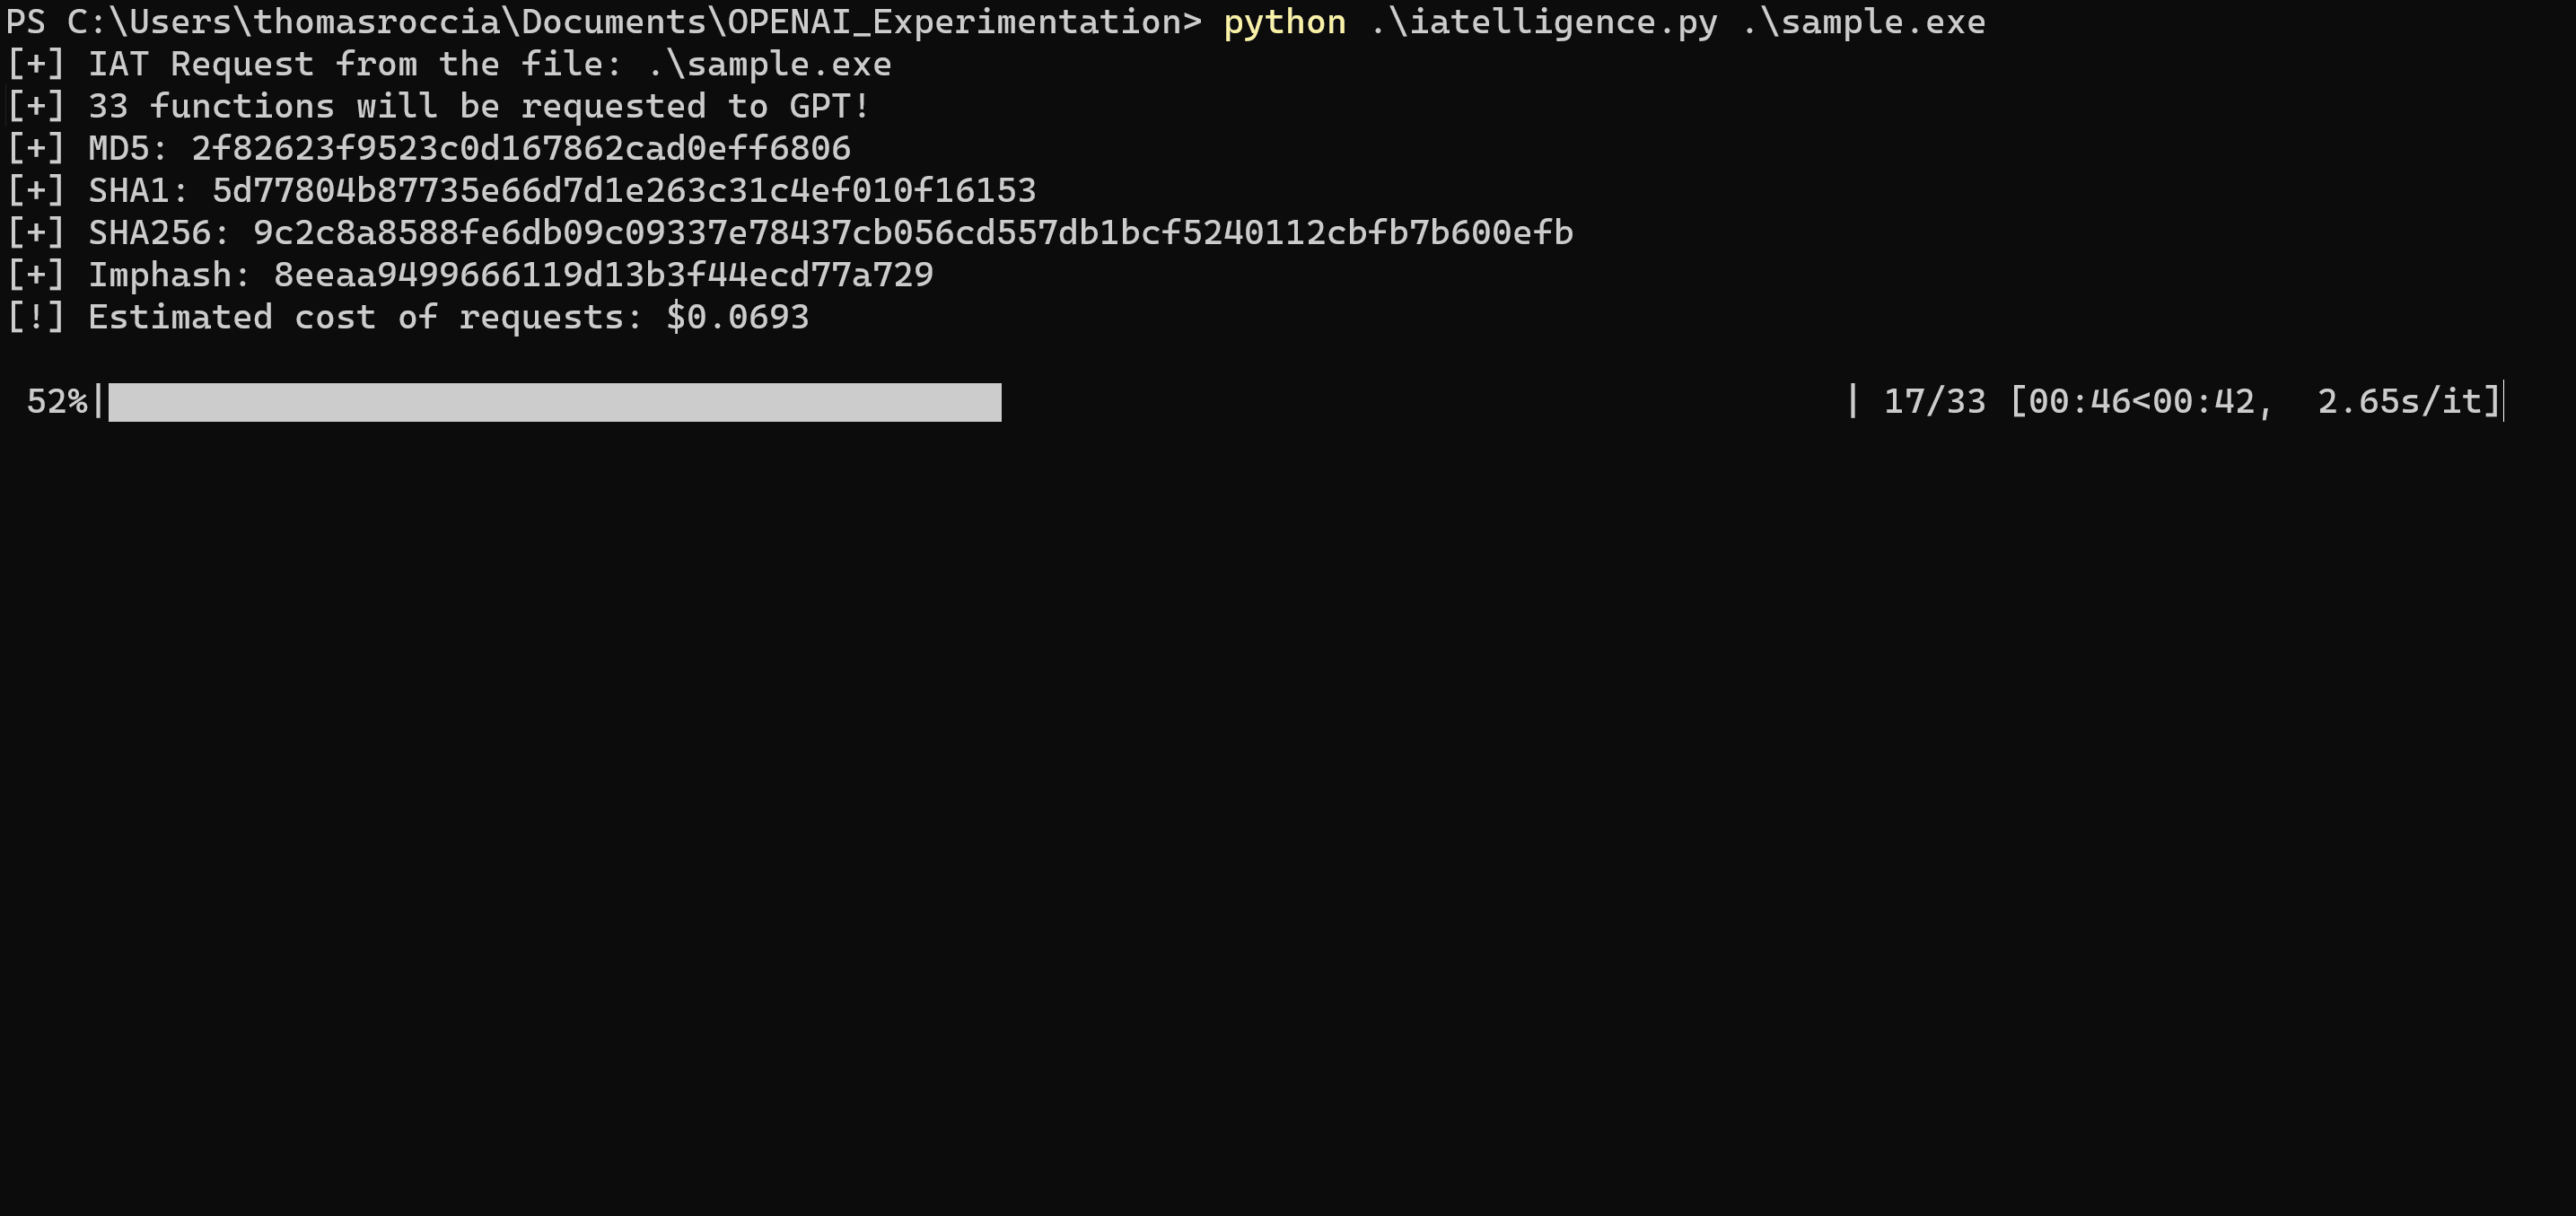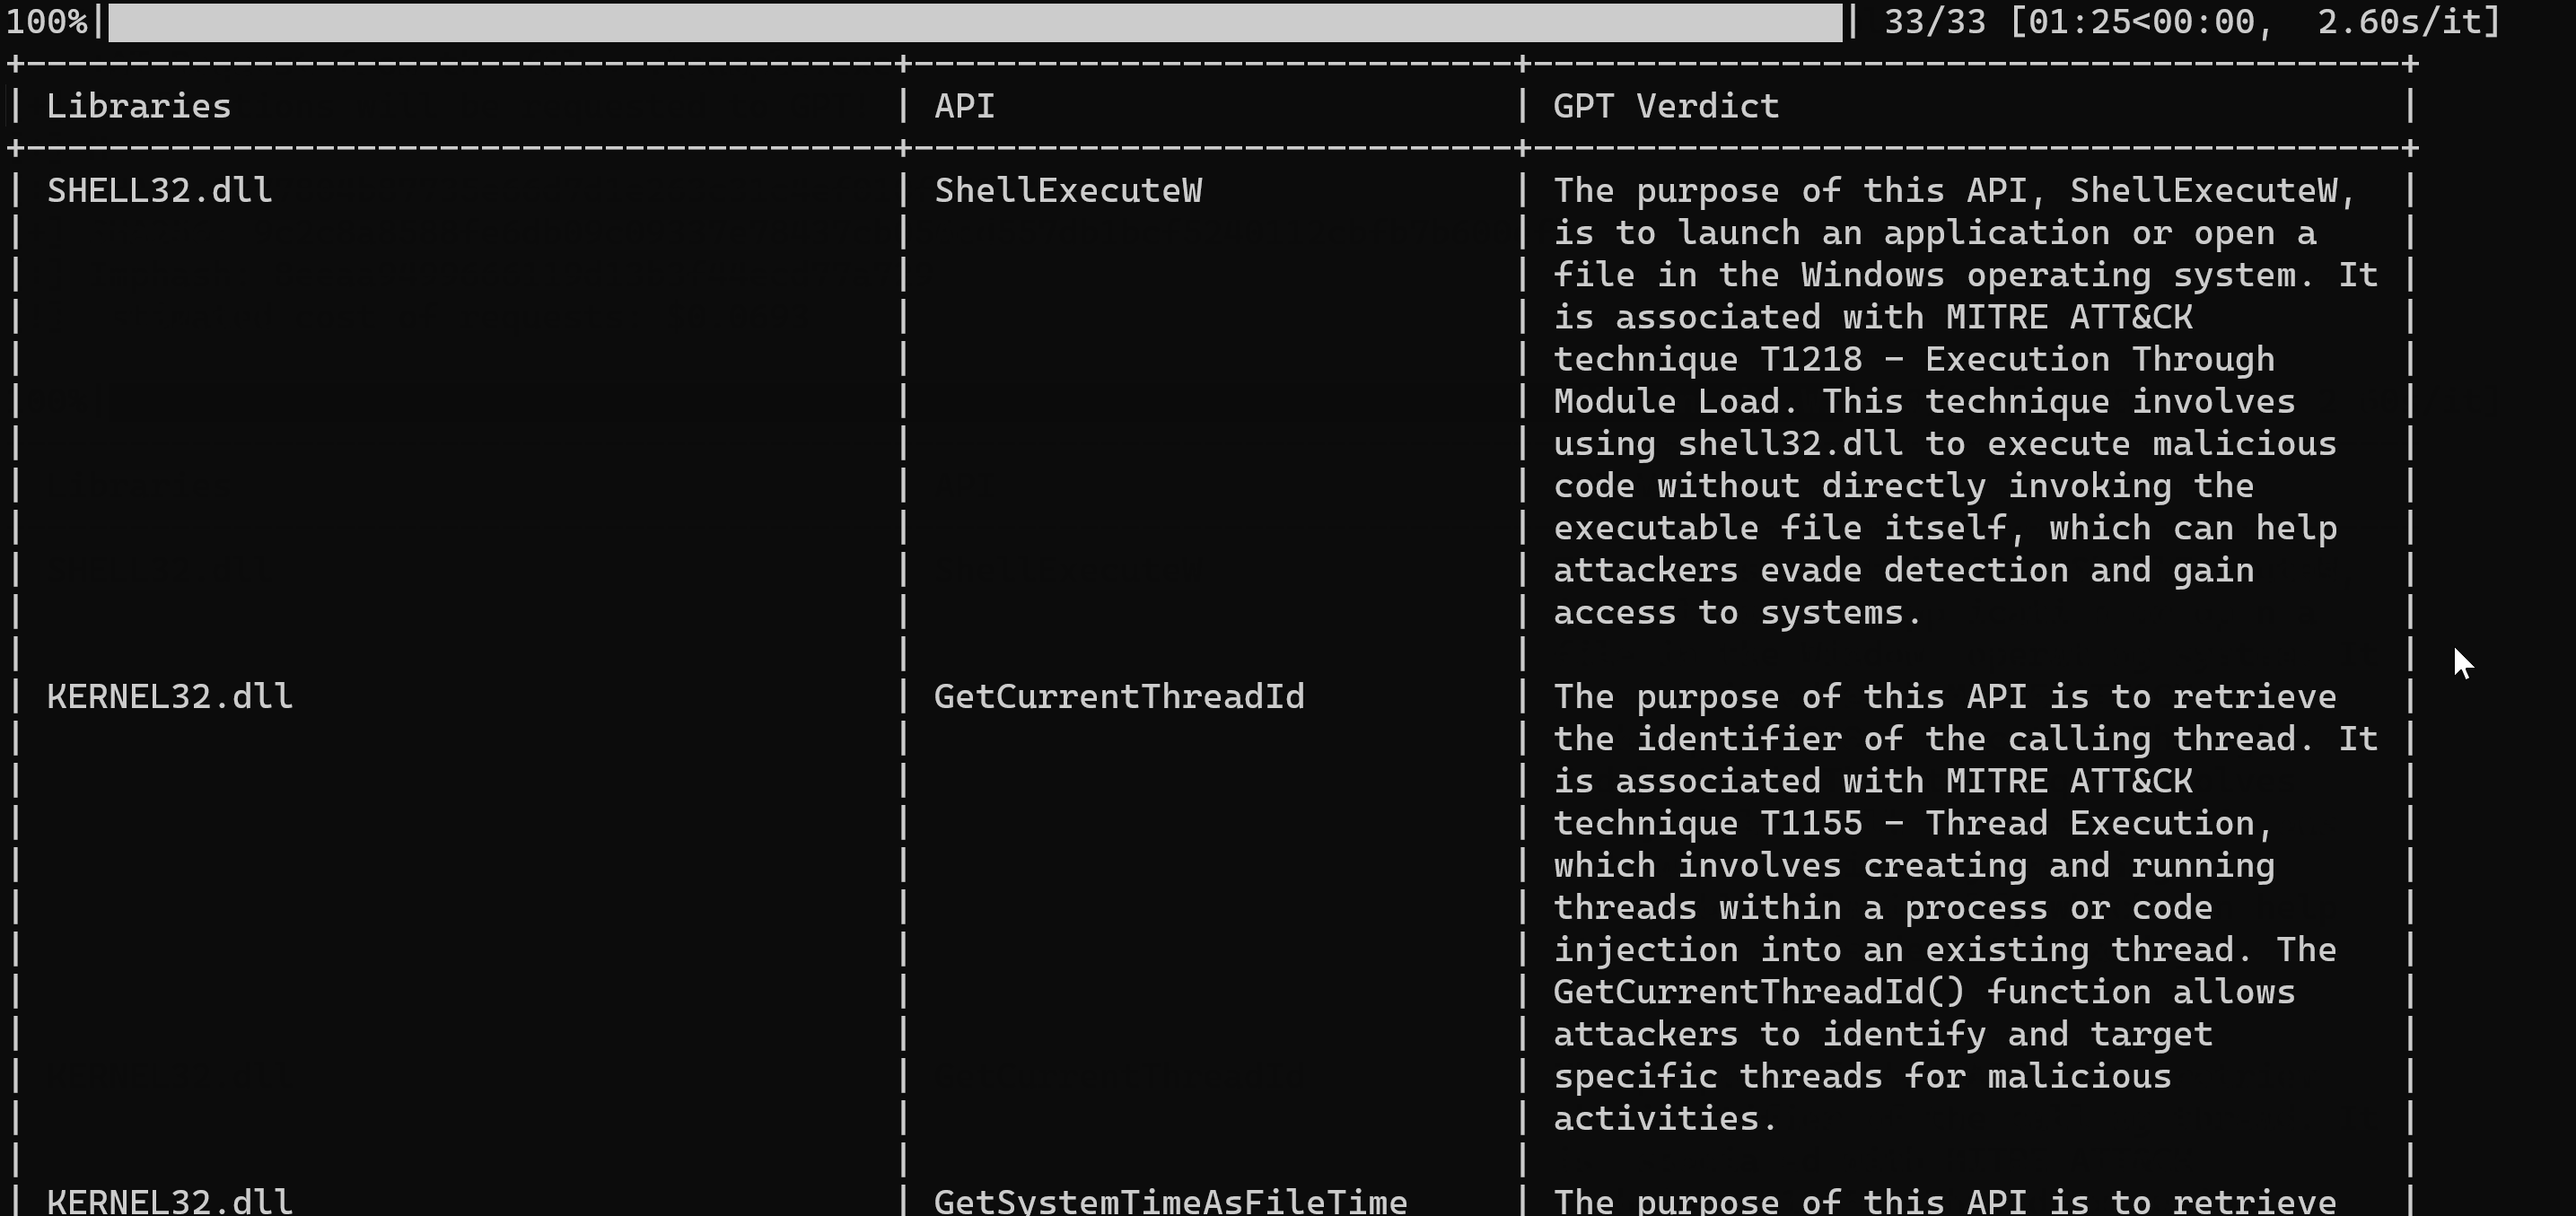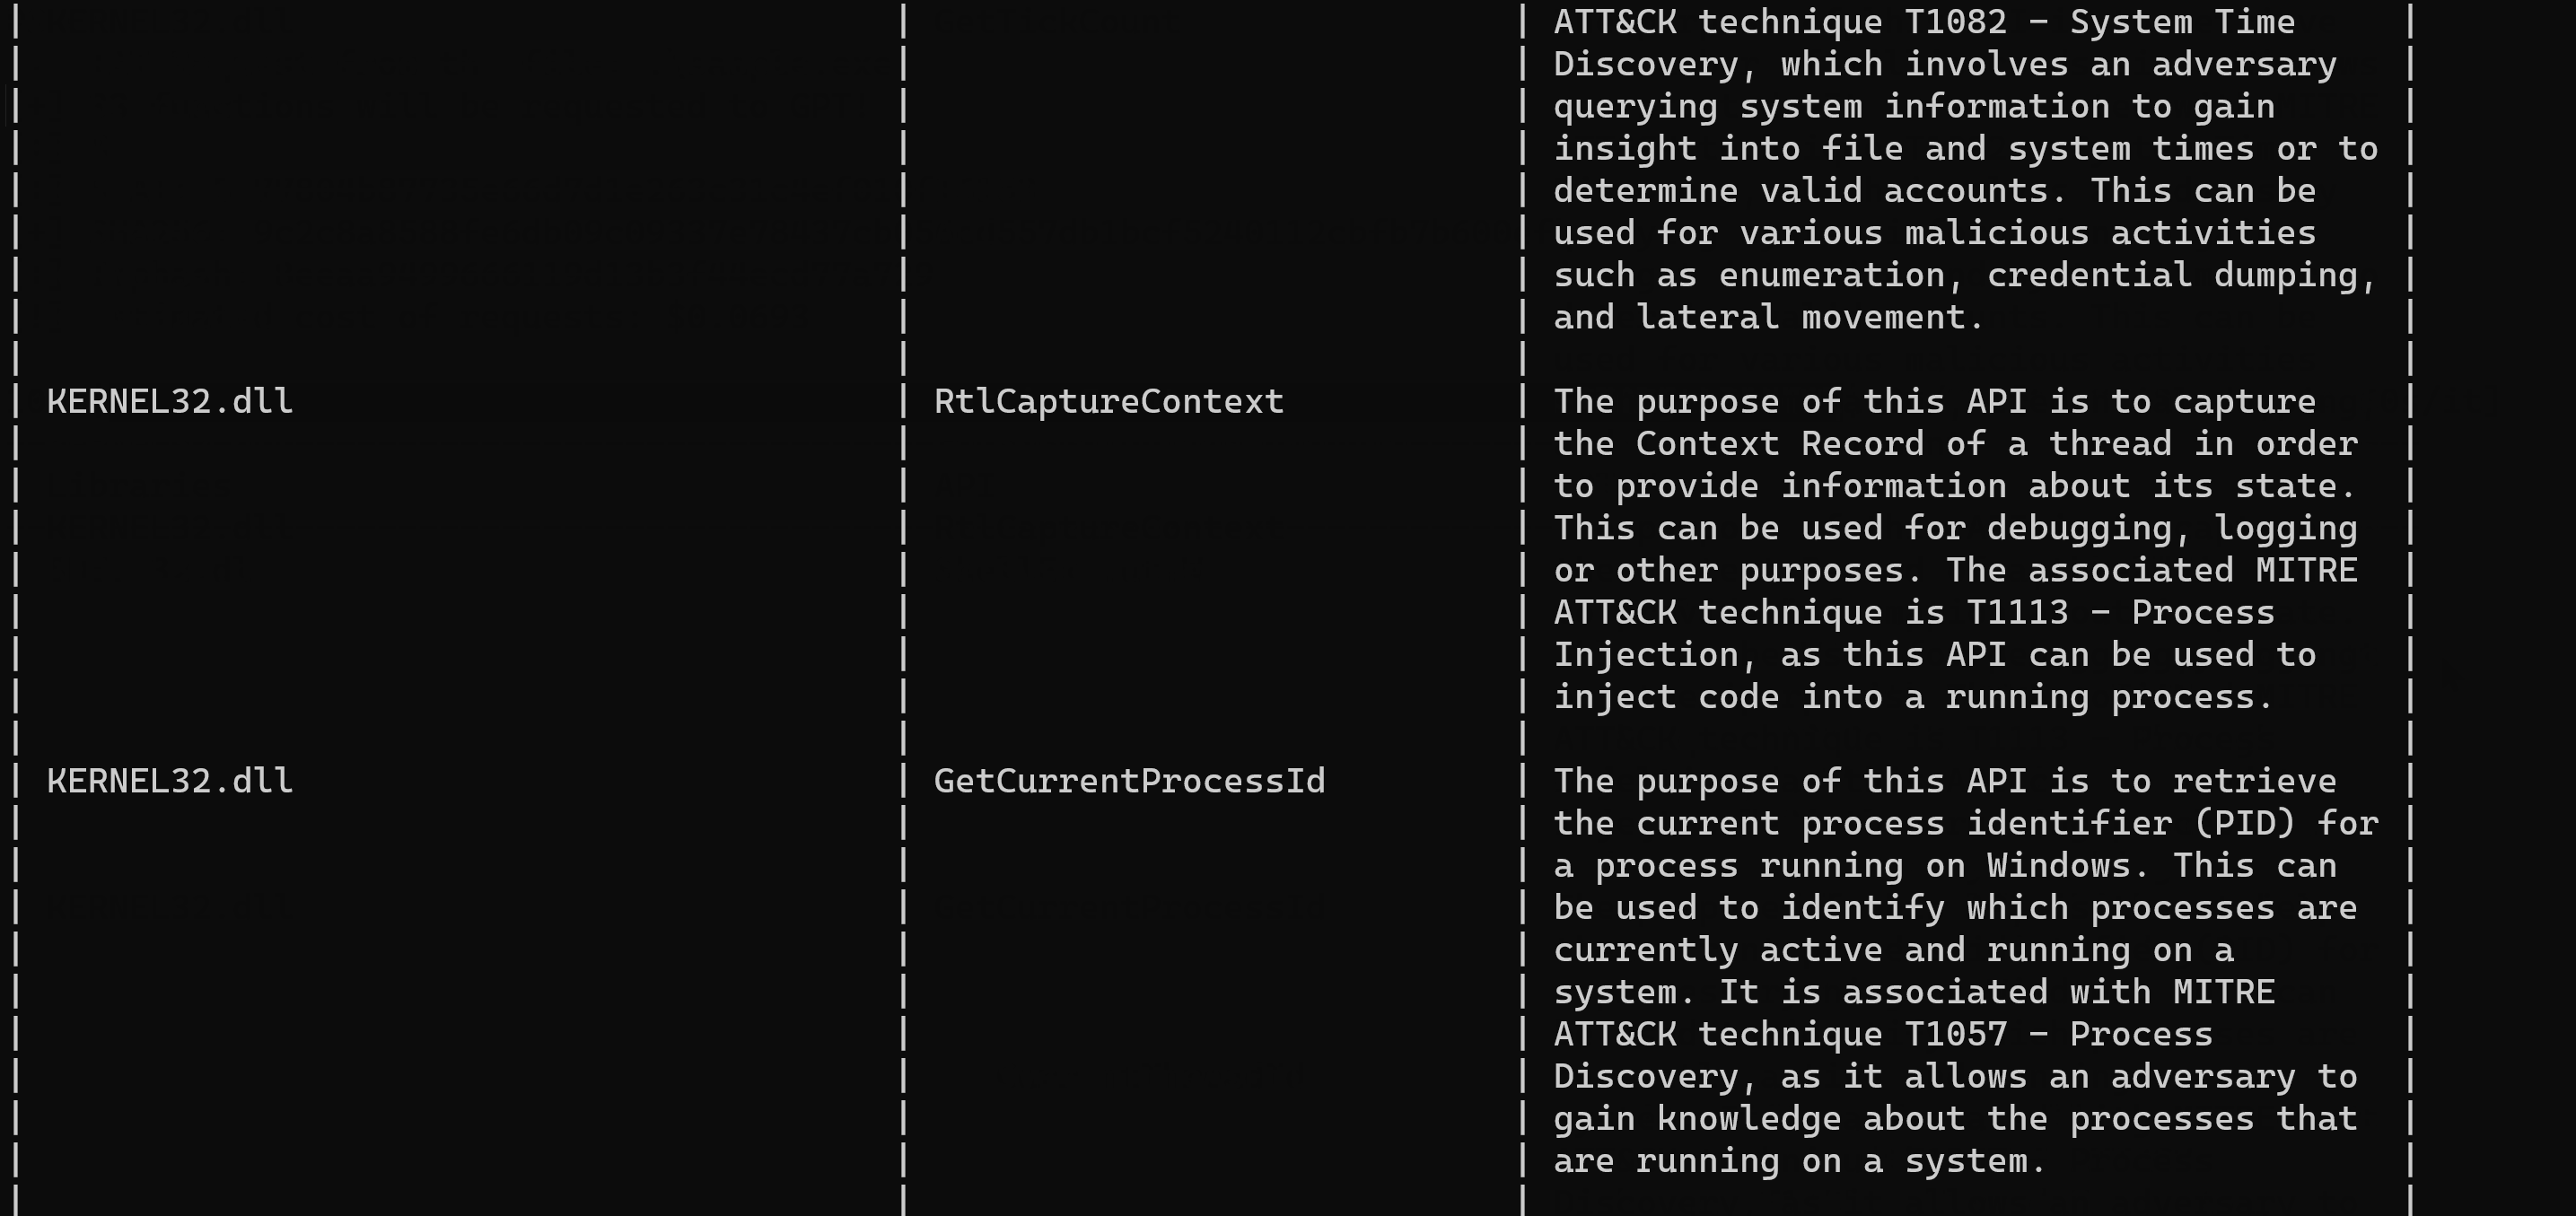
結果は表で確認できます。以下は切り詰めた抜粋です。
+------------------------------------------+-----------------------------+------------------------------------------+
| Libraries                                | API                         | GPT Verdict                              |
+------------------------------------------+-----------------------------+------------------------------------------+
| SHELL32.dll                              | ShellExecuteW               | The purpose of this API, ShellExecuteW,  |
|                                          |                             | is to launch an application or open a    |
|                                          |                             | file in the Windows operating system. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1218 - Execution Through      |
|                                          |                             | Module Load. This technique involves     |
|                                          |                             | using shell32.dll to execute malicious   |
|                                          |                             | code without directly invoking the       |
|                                          |                             | executable file itself, which can help   |
|                                          |                             | attackers evade detection and gain       |
|                                          |                             | access to systems.                       |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetCurrentThreadId          | The purpose of this API is to retrieve   |
|                                          |                             | the identifier of the calling thread. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1155 - Thread Execution,      |
|                                          |                             | which involves creating and running      |
|                                          |                             | threads within a process or code         |
|                                          |                             | injection into an existing thread. The   |
|                                          |                             | GetCurrentThreadId() function allows     |
|                                          |                             | attackers to identify and target         |
|                                          |                             | specific threads for malicious           |
|                                          |                             | activities.                              |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetSystemTimeAsFileTime     | The purpose of this API is to retrieve   |
|                                          |                             | the current system time as a file time   |
|                                          |                             | format. It is associated with the MITRE  |
|                                          |                             | ATT&CK technique T1124 - System Time     |
|                                          |                             | Discovery, which is used by adversaries  |
|                                          |                             | to gain insight into when certain        |
|                                          |                             | activities occurred or are scheduled to  |
|                                          |                             | occur. This allows them to perform       |
|                                          |                             | timing-based attacks and evade           |
|                                          |                             | detection.                               |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetTickCount                | The purpose of this API is to retrieve   |
|                                          |                             | the number of milliseconds since Windows |
|                                          |                             | was started. It is associated with MITRE |
|                                          |                             | ATT&CK technique T1082 - System Time     |
|                                          |                             | Discovery, which involves an adversary   |
|                                          |                             | querying system information to gain      |
|                                          |                             | insight into file and system times or to |
|                                          |                             | determine valid accounts. This can be    |
|                                          |                             | used for various malicious activities    |
|                                          |                             | such as enumeration, credential dumping, |
|                                          |                             | and lateral movement.                    |
|                                          |                             |                                          |
| KERNEL32.dll                             | RtlCaptureContext           | The purpose of this API is to capture    |
|                                          |                             | the Context Record of a thread in order  |
|                                          |                             | to provide information about its state.  |
|                                          |                             | This can be used for debugging, logging  |
|                                          |                             | or other purposes. The associated MITRE  |
|                                          |                             | ATT&CK technique is T1113 - Process      |






