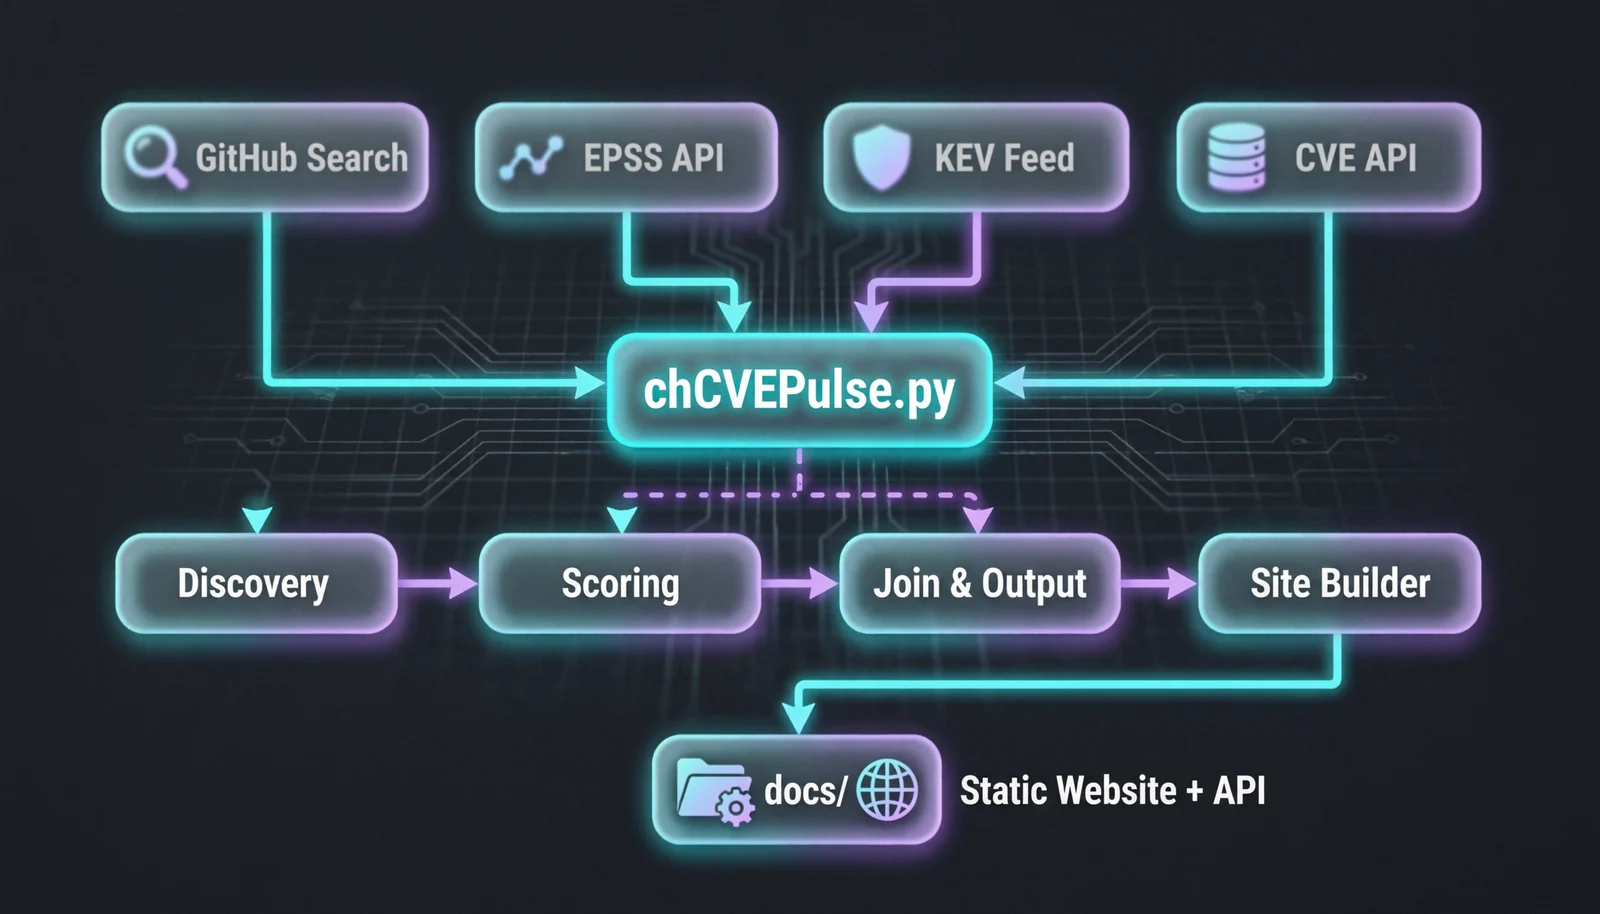


CVE PoC(概念実証)ライブアグリゲーター - スマート検索&脅威インテリジェンス搭載

CVE Pulse は、GitHubから CVE Proof‑of‑Concepts を自動的に発見、スコアリング、インデックス化します。
EPSSスコア と CISA KEV データでそれらを強化し、日次の スナップショット&差分 を構築し、高速で検索可能な 静的ウェブサイト を提供します
Ch4120N – セキュリティ愛好家&自動化好き。
📧 [email protected]
-windows) 対応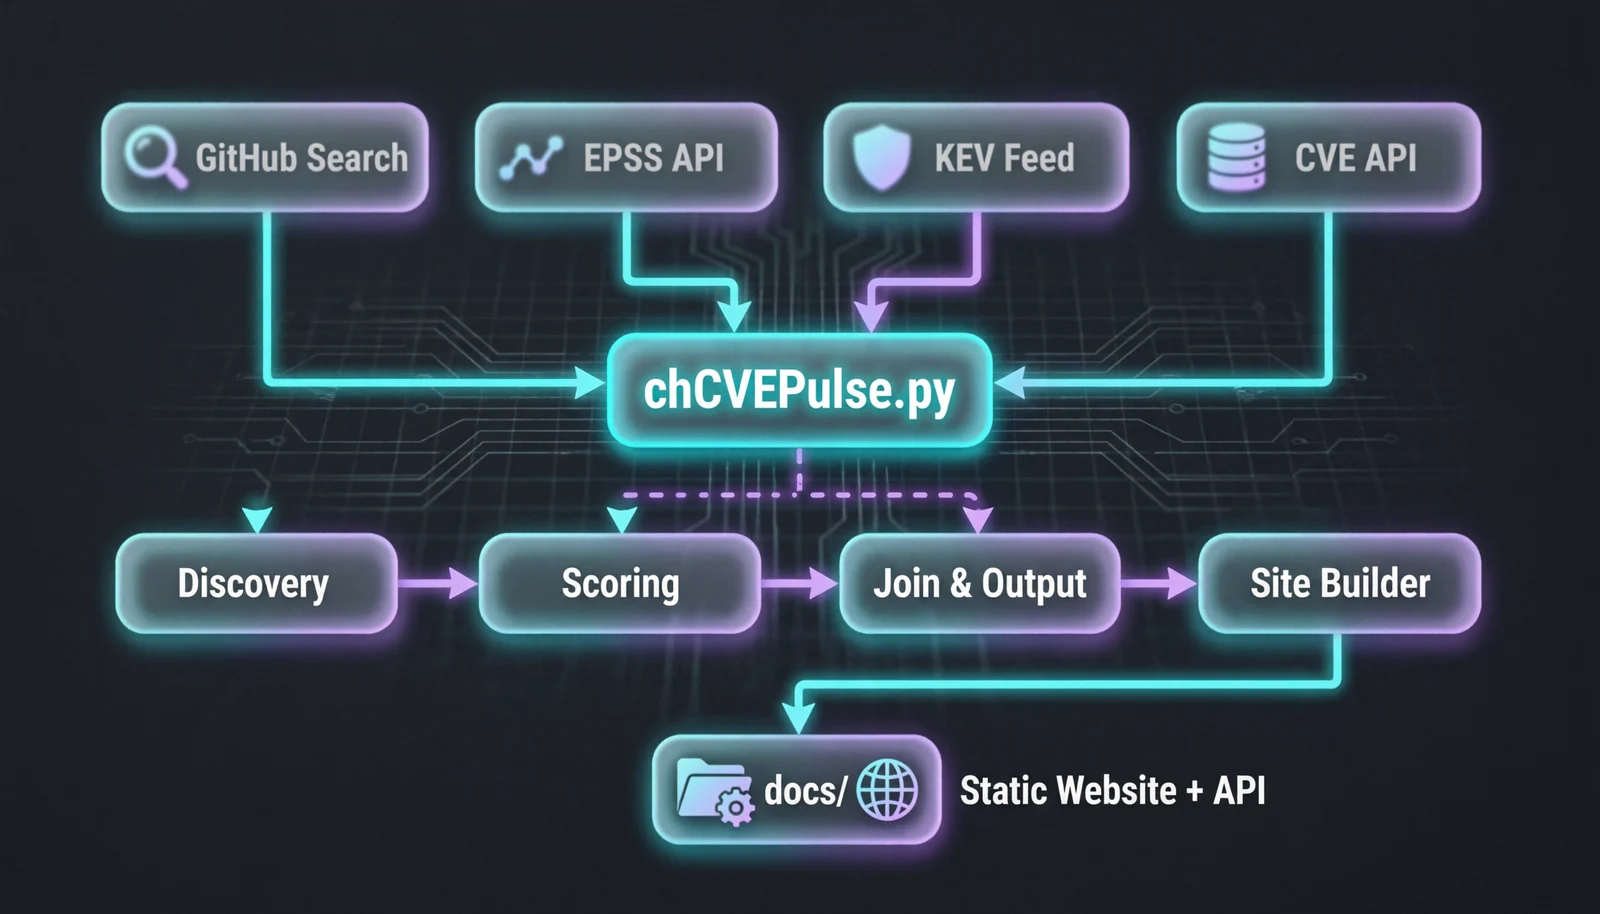
fetch-epss はEPSSスコア上位2000件のCVEをダウンロードします。fetch-kev はCISA KEVカタログをダウンロードします。sync-cves は data/github.txt を読み込み、MITRE APIからCVEメタデータを取得し、各CVEのmarkdownファイルを作成/更新します。pipeline(または個別の build-* コマンド):
github.txt または以前に低信頼度だったものから)。build-site は CVE_list.json、trending_poc.json、および静的HTMLページを生成します。docs/)はGitHub Pagesにデプロイされます。git clone https://github.com/Ch4120N/Ch4120N-CVE-Pulse.git cd Ch4120N-CVE-Pulse
pip install -r requirements.txt
python chCVEPulse.py fetch-epss python chCVEPulse.py fetch-kev
python chCVEPulse.py sync-cves
export GITHUB_TOKEN=your_token_here python chCVEPulse.py pipeline --days 7
python chCVEPulse.py build-site
## 📦 インストール

**要件:**
- Python 3.9+
- `pip`

パッケージをインストールします:```bash
pip install -r requirements.txt
(requirements.txt には requests、jinja2、その他の依存関係が含まれています。)
すべての操作は単一のスクリプト chCVEPulse.py を通じて行います。
例:```bash
python chCVEPulse.py fetch-epss --limit 2000 python chCVEPulse.py fetch-kev
python chCVEPulse.py sync-cves --cve CVE-2025-12345
python chCVEPulse.py pipeline --days 7 --mode daily --limit 50
python chCVEPulse.py build-site --html-mode summary
### フルパイプライン

`pipeline` サブコマンドは細かく調整できます:

- `--days` : GitHub を何日前まで遡って検索するか(デフォルト: 7)
- `--mode` : `daily`(最近の CVE、高速)または `weekly`(より広範なスキャン)
- `--limit` : スキャンする CVE の最大数(デフォルト: 50)
- `--cve` : スキャンする CVE ID を 1 つ以上指定
- `--skip-discovery` : 既存データから出力のみを再生成
- `--check-links` : リポジトリ URL がまだ有効か確認

---

## 📊 出力とウェブサイト

パイプラインの実行が成功すると、`docs/` には以下が含まれます:

- **`index.html`** – メイン検索ページ(`logic.js` と `style.css` で動作)
- **`CVE_list.json`** – 説明と PoC リンクを含むすべての CVE
- **`trending_poc.json`** – 最近更新された PoC(自動更新される README から)
- **`api/v1/`** – 完全な REST ライクな JSON エンドポイント:
  - `joined_top.json` – PoC、EPSS、KEV ステータスを含む優先度の高い CVE
  - `kev.json` – 拡充された KEV リスト
  - `epss_top.json` – PoC を含む EPSS 上位 CVE
  - `cve/{CVE-ID}.json` – CVE ごとの詳細な PoC 情報
  - `snapshots/` – 日次の状態スナップショット
  - `diffs/` – 前日比の変更

検索は**ファジーマッチング**、ベンダー/製品フィルター、除外語(例:`-windows`)をサポートしています。

---

## 🗂️ プロジェクト構成```
Ch4120N-CVE-Pulse/
├── chCVEPulse.py
├── scripts/
│   ├── config.py
│   ├── helpers.py
│   ├── github_api.py
│   ├── scoring.py
│   ├── discovery.py
│   ├── outputs.py
│   ├── diff.py
│   ├── joined.py
│   ├── site.py
│   ├── sync.py
│   ├── fetch_epss.py
│   ├── fetch_kev.py
│   └── pipeline.py
├── templates/
│   └── index.html# Jinja2 template for the website
├── data/
│   ├── github.txt# CVE -> PoC URL list (edit this)
│   ├── blacklist.txt
│   ├── cache/
│   └── evidence/
├── docs/
│   ├── api/v1/
│   └── index.html, style.css, logic.js
├── requirements.txt
└── README.md
ほぼすべての設定は scripts/config.py にあります:
GITHUB_SOURCES – data/github.txt へのパスEPSS_API_URL、KEV_URL、CVE_API_TEMPLATE – 外部 API エンドポイントHIGH_EPSS_THRESHOLD – 「高」アラートの最小 EPSSTOP_KEV_COUNT – 保持する KEV エントリ数SNAPSHOT_RETENTION_DAYS – 古いスナップショットを保持する期間API レート制限を緩和するために GitHub トークン の使用を推奨します(GITHUB_TOKEN 環境変数として設定)。
3 つの GitHub Actions ワークフローがすべてを最新の状態に保ちます:
sync_cve_pocs.yml – 毎日実行され、data/github.txt を読み込み、最新の CVE メタデータを取得して markdown ファイルを更新します。hot_cves.yml – 6 時間ごとに実行され、この README の Trending PoCs セクションを更新します。site.yml – 静的ウェブサイトをビルドし、GitHub Pages にデプロイします。すべてのワークフローは .github/workflows/ にあります。
以下の Trending PoCs テーブルは、CI パイプラインによって 6 時間ごとに自動更新 されます。
このプロジェクトは 脅威インテリジェンス、脆弱性管理、および防御的セキュリティ研究 を目的としています。
リンクされたリポジトリを違法または不正な活動に使用しないでください。
作者は PoC コードをホストまたは推奨しておらず、公開されている情報をインデックス化しているだけです。
GPLv3 ライセンス – 全文は LICENSE ファイルを参照してください。
"Stay ahead of threats – track every CVE PoC in real time."
⭐ このプロジェクトが役に立ったら、スターを付けていただけると幸いです!
Made with ❤️ by Ch4120N
| コマンド | 説明 |
|---|
fetch-epss | EPSS データをダウンロード |
fetch-kev | KEV カタログをダウンロード |
sync-cves | data/github.txt から CVE Markdown を更新 |
build-site | 静的ウェブサイト(CVE リスト + HTML)を生成 |
build-diffs | 直近2つのスナップショットから日次差分を構築 |
build-joined | KEV+EPSS+PoC を結合した JSON エンドポイントを作成 |
pipeline | フルパイプラインを実行(discover → output → diff → site) |
| ソース | 説明 |
|---|
| GitHub Search API | CVE ID に言及しているリポジトリを検出 |
| GitHub GraphQL | スター数、言語、トピック、フォーク/アーカイブ状態を取得 |
| FIRST EPSS | Exploit Prediction Scoring System |
| CISA KEV | Known Exploited Vulnerabilities カタログ |
| MITRE CVE API | 公式 CVE の説明、参照、製品 |
| Stars | Updated | Repository | Description |
|---|
| 4070⭐ | 4 hours ago | copy-fail-CVE-2026-31431 | Copy Fail (CVE-2026-31431): 9-year-old Linux kernel LPE found by Theori's Xint Code |
| 576⭐ | 8 days ago | cve_2026_31431 | Exploit POC for CVE_2026_31431 |
| 329⭐ | 20 hours ago | CVE-2026-54121 | Certighost POC |
| 245⭐ | 8 hours ago | CVE-2026-43499-popsicle | CVE-2026-43499 Implementation for 6.12.23-android16-5-g75e9b1c7ae7c-abogki463945075-4k |
| 231⭐ | 4 days ago | CVE-2026-41089 | Netlogon and CLDAP vulnerability research with a proof of concept. |
| 304⭐ | 1 day ago | CVE-2026-21858 | n8n Ni8mare - Unauthenticated Arbitrary File Read to RCE Chain (CVSS 10.0) |
| 208⭐ | 14 days ago | CVE-2026-24061 | Exploitation of CVE-2026-24061 |
| 159⭐ | 6 days ago | CVE-2026-43499 | CVE-2026-43499 PoC |
| 177⭐ | 2 days ago | CVE-2026-62911 | POC pre-auth RCE on Exchange |
| 825⭐ | 2 days ago | CVE-2026-24061 | CVE-2026-24061 exploit PoC |
| 141⭐ | 17 hours ago | CVE-2026-42980-POC | CVE-2026-42980 PUBLIC EXPLOIT + RESEARCH |
| 101⭐ | 17 hours ago | CVE-2026-75604-poc | CVE-2026-75604 Next.js Windows RCE poc |
| 124⭐ | 7 days ago | CVE-2026-41651 | |
| 102⭐ | 23 hours ago | CVE-2026-43499-Poc-Analysis | Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only. |
| 111⭐ | 25 days ago | CVE-2026-31431-Advanced-Exploit | CVE-2026-31431 纯文件利用 |
| 18⭐ | 6 days ago | CVE-2026-43499-Poc-Analysis | Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only. |
| 63⭐ | 29 days ago | CVE-2026-45504 | CVE-2026-45504 Microsoft Exchange File Read |
| 41⭐ | 8 days ago | CVE-2026-31431 | |
| 109⭐ | 6 days ago | Copy-Fail-Exploit-CVE-2026-31431 | Most Linux LPEs need a race window or a kernel-specific offset. Copy Fail is a straight-line logic flaw, it needs neither. The same 732-byte Python script (or .c elf) roots every Linux distribution shipped since 2017. |
| 83⭐ | 7 days ago | CVE-2026-0073-Android-adbd-authentication-bypass-POC |
| Stars | Updated | Repository | Description |
|---|
| 1430⭐ | 1 day ago | CVE-2025-55182 | Explanation and full RCE PoC for CVE-2025-55182 |
| 792⭐ | 8 days ago | CVE-2025-55182-research | CVE-2025-55182 POC |
| 717⭐ | 2 days ago | CVE-2025-33073 | PoC Exploit for the NTLM reflection SMB flaw. |
| 528⭐ | 14 hours ago | CVE-2025-32463_chwoot | Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463 |
| 477⭐ | 8 days ago | CVE-2025-32463 | Local Privilege Escalation to Root via Sudo chroot in Linux |
| 313⭐ | 19 hours ago | CVE-2025-53770-Exploit | SharePoint WebPart Injection Exploit Tool |
| 314⭐ | 17 days ago | CVE-2025-55182 | RSC/Next.js RCE Vulnerability Detector & PoC Chrome Extension – CVE-2025-55182 & CVE-2025-66478 |
| 1062⭐ | 7 days ago | React2Shell-CVE-2025-55182-original-poc | Original Proof-of-Concepts for React2Shell CVE-2025-55182 |
| 406⭐ | 2 days ago | CVE-2025-24071_PoC | CVE-2025-24071: NTLM Hash Leak via RAR/ZIP Extraction and .library-ms File |
| 213⭐ | 1 day ago | CVE-2025-32023 | PoC & Exploit for CVE-2025-32023 / PlaidCTF 2025 "Zerodeo" |
| 385⭐ | 10 days ago | ColorOS-CVE-2025-10184 | ColorOS短信漏洞,以及用户自救方案 |
| 281⭐ | 17 hours ago | CVE-2025-55182-advanced-scanner- | |
| 432⭐ | 2 days ago | Next.js-RSC-RCE-Scanner-CVE-2025-66478 | A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability. |
| 197⭐ | 1 day ago | POC-CVE-2025-24813 | his repository contains an automated Proof of Concept (PoC) script for exploiting CVE-2025-24813, a Remote Code Execution (RCE) vulnerability in Apache Tomcat. The vulnerability allows an attacker to upload a malicious serialized payload to the server, leading to arbitrary code execution via deserialization when specific conditions are met. |
| 190⭐ | 183 days ago | RSC-Detect-CVE-2025-55182 | RSC Detect CVE 2025 55182 |
| 194⭐ | 8 days ago | CVE-2025-30208-EXP | CVE-2025-30208-EXP |
| 142⭐ | 10 days ago | CVE-2025-32433 | CVE-2025-32433 https://github.com/erlang/otp/security/advisories/GHSA-37cp-fgq5-7wc2 |
| 119⭐ | 2 days ago | CVE-2025-43300 | This is POC for IOS 0click CVE-2025-43300 |
| 160⭐ | 8 days ago | CVE-2025-21756 | Exploit for CVE-2025-21756 for Linux kernel 6.6.75. My first linux kernel exploit! |
| 195⭐ | 27 days ago | CVE-2025-32756-POC | Proof of Concept for CVE-2025-32756 - A critical stack-based buffer overflow vulnerability affecting multiple Fortinet products. |
| Stars | Updated | Repository | Description |
|---|
| 2456⭐ | 2 days ago | CVE-2024-1086 | Universal local privilege escalation Proof-of-Concept exploit for CVE-2024-1086, working on most Linux kernels between v5.14 and v6.6, including Debian, Ubuntu, and KernelCTF. The success rate is 99.4% in KernelCTF images. |
| 689⭐ | 1 day ago | CVE-2024-38063 | poc for CVE-2024-38063 (RCE in tcpip.sys) |
| 497⭐ | 20 days ago | cve-2024-6387-poc | a signal handler race condition in OpenSSH's server (sshd) |
| 517⭐ | 1 day ago | CVE-2024-49113 | LdapNightmare is a PoC tool that tests a vulnerable Windows Server against CVE-2024-49113 |
| 526⭐ | 2 days ago | CVE-2024-6387_Check | CVE-2024-6387_Check is a lightweight, efficient tool designed to identify servers running vulnerable versions of OpenSSH |
| 224⭐ | 31 days ago | CVE-2024-38077 | RDL的堆溢出导致的RCE |
| 378⭐ | 23 days ago | cve-2024-6387-poc | 32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc |
| 333⭐ | 8 days ago | CVE-2024-21338 | Local Privilege Escalation from Admin to Kernel vulnerability on Windows 10 and Windows 11 operating systems with HVCI enabled. |
| 331⭐ | 5 days ago | CVE-2024-0044 | CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13 |
| 320⭐ | 2 days ago | CVE-2024-4577 | PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC |
| 285⭐ | 2 days ago | CVE-2024-21413 | CVE-2024-21413 PoC for THM Lab |
| 775⭐ | 1 day ago | CVE-2024-21413-Microsoft-Outlook-Remote-Code-Execution-Vulnerability | Microsoft-Outlook-Remote-Code-Execution-Vulnerability |
| 195⭐ | 2 days ago | CVE-2024-6387 | Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (CVE-2024-6387) |
| 9⭐ | 40 days ago | CVE-2024-38077-POC | |
| 235⭐ | 59 days ago | CVE_2024_30078_POC_WIFI | basic concept for the latest windows wifi driver CVE |
| 181⭐ | 6 days ago | CVE-2024-25600 | Unauthenticated Remote Code Execution – Bricks <= 1.9.6 |
| 208⭐ | 2 days ago | CVE-2024-23897 | CVE-2024-23897 |
| 87⭐ | 40 days ago | CVE-2024-40725-CVE-2024-40898 | CVE-2024-40725 and CVE-2024-40898, affecting Apache HTTP Server versions 2.4.0 through 2.4.61. These flaws pose significant risks to web servers worldwide, potentially leading to source code disclosure and server-side request forgery (SSRF) attacks. |
| 113⭐ | 14 days ago | CVE-2024-6387 | PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit) |
| 156⭐ | 16 days ago | CVE-2024-21413 | Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC |
| Stars | Updated | Repository | Description |
|---|
| 784⭐ | 14 days ago | CVE-2023-38831-winrar-exploit | CVE-2023-38831 winrar exploit generator |
| 504⭐ | 2 days ago | Windows_LPE_AFD_CVE-2023-21768 | LPE exploit for CVE-2023-21768 |
| 381⭐ | 3 days ago | CVE-2023-32233 | CVE-2023-32233: Linux内核中的安全漏洞 |
| 418⭐ | 10 days ago | CVE-2023-0386 | CVE-2023-0386在ubuntu22.04上的提权 |
| 116⭐ | 8 days ago | CVE-2023-21839 | Weblogic CVE-2023-21839 RCE (无需Java依赖一键RCE) |
| 394⭐ | 19 days ago | CVE-2023-4911 | PoC for CVE-2023-4911 |
| 284⭐ | 13 days ago | CVE-2023-21608 | Adobe Acrobat Reader - CVE-2023-21608 - Remote Code Execution Exploit |
| 317⭐ | 35 days ago | CVE-2023-4863 | |
| 246⭐ | 2 days ago | CVE-2023-44487 | Basic vulnerability scanning to see if web servers may be vulnerable to CVE-2023-44487 |
| 245⭐ | 45 days ago | CVE-2023-7028 | This repository presents a proof-of-concept of CVE-2023-7028 |
| 228⭐ | 57 days ago | CVE-2023-3519 | RCE exploit for CVE-2023-3519 |
| 168⭐ | 2 days ago | CVE-2023-36745 | |
| 226⭐ | 10 days ago | CVE-2023-20887 | VMWare vRealize Network Insight Pre-Authenticated RCE (CVE-2023-20887) |
| 345⭐ | 2 days ago | CVE-2023-23397-POC-Powershell | |
| 183⭐ | 2 days ago | CVE-2023-28252 | |
| 136⭐ | 40 days ago | CVE-2023-2640-CVE-2023-32629 | GameOver(lay) Ubuntu Privilege Escalation |
| 240⭐ | 8 days ago | Weblogic-CVE-2023-21839 | |
| 205⭐ | 2 days ago | CVE-2023-46747-RCE | exploit for f5-big-ip RCE cve-2023-46747 |
| 236⭐ | 2 days ago | CVE-2023-29357 | Microsoft SharePoint Server Elevation of Privilege Vulnerability |
| 166⭐ | 8 days ago | CVE-2023-25157 | CVE-2023-25157 - GeoServer SQL Injection - PoC |
| Stars | Updated | Repository | Description |
|---|
| 1132⭐ | 1 day ago | CVE-2022-0847-DirtyPipe-Exploit | A root exploit for CVE-2022-0847 (Dirty Pipe) |
| 570⭐ | 8 days ago | CVE-2022-23222 | CVE-2022-23222: Linux Kernel eBPF Local Privilege Escalation |
| 360⭐ | 37 days ago | CVE-2022-21907 | HTTP Protocol Stack Remote Code Execution Vulnerability CVE-2022-21907 |
| 357⭐ | 15 hours ago | CVE-2022-40684 | A proof of concept exploit for CVE-2022-40684 affecting Fortinet FortiOS, FortiProxy, and FortiSwitchManager |
| 377⭐ | 35 days ago | CVE-2022-29464 | WSO2 RCE (CVE-2022-29464) exploit and writeup. |
| 735⭐ | 2 hours ago | CVE-2022-0847-DirtyPipe-Exploits | A collection of exploits and documentation that can be used to exploit the Linux Dirty Pipe vulnerability. |
| 437⭐ | 3 days ago | CVE-2022-25636 | CVE-2022-25636 |
| 487⭐ | 6 days ago | CVE-2022-2588 | exploit for CVE-2022-2588 |
| 497⭐ | 24 days ago | CVE-2022-0995 | CVE-2022-0995 exploit |
| 385⭐ | 2 days ago | CVE-2022-39197 | CobaltStrike <= 4.7.1 RCE |
| 414⭐ | 2 days ago | CVE-2022-33679 | One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html |
| 281⭐ | 10 days ago | CVE-2022-0847 | CVE-2022-0847-DirtyPipe-Exploit CVE-2022-0847 是存在于 Linux内核 5.8 及之后版本中的本地提权漏洞。攻击者通过利用此漏洞,可覆盖重写任意可读文件中的数据,从而可将普通权限的用户提升到特权 root。 CVE-2022-0847 的漏洞原理类似于 CVE-2016-5195 脏牛漏洞(Dirty Cow),但它更容易被利用。漏洞作者将此漏洞命名为“Dirty Pipe” |
| 354⭐ | 18 hours ago | CVE-2022-21894 | baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability |
| 609⭐ | 2 days ago | CVE-2022-38694_unlock_bootloader | This is a one-time signature verification bypass. For persistent signature verification bypass, check https://github.com/TomKing062/CVE-2022-38691_38692 |
| 377⭐ | 2 days ago | CVE-2022-0185 | CVE-2022-0185 |
| 284⭐ | 31 days ago | cve-2022-27255 | |
| 265⭐ | 172 days ago | CVE-2022-39952 | POC for CVE-2022-39952 |
| 238⭐ | 31 days ago | CVE-2022-20699 | Cisco Anyconnect VPN unauth RCE (rwx stack) |
| 236⭐ | 9 days ago | CVE-2022-30075 | Tp-Link Archer AX50 Authenticated RCE (CVE-2022-30075) |
| 218⭐ | 10 days ago | CVE-2022-34918 | CVE-2022-34918 netfilter nf_tables 本地提权 POC |


