
 aquasecurity/trivy-action
TrivyをGitHub Actionとして実行し、Dockerコンテナイメージを脆弱性スキャンします。

[![GitHub Release][release-img]][release] [![GitHub Marketplace][marketplace-img]][marketplace] [![License][license-img]][license]
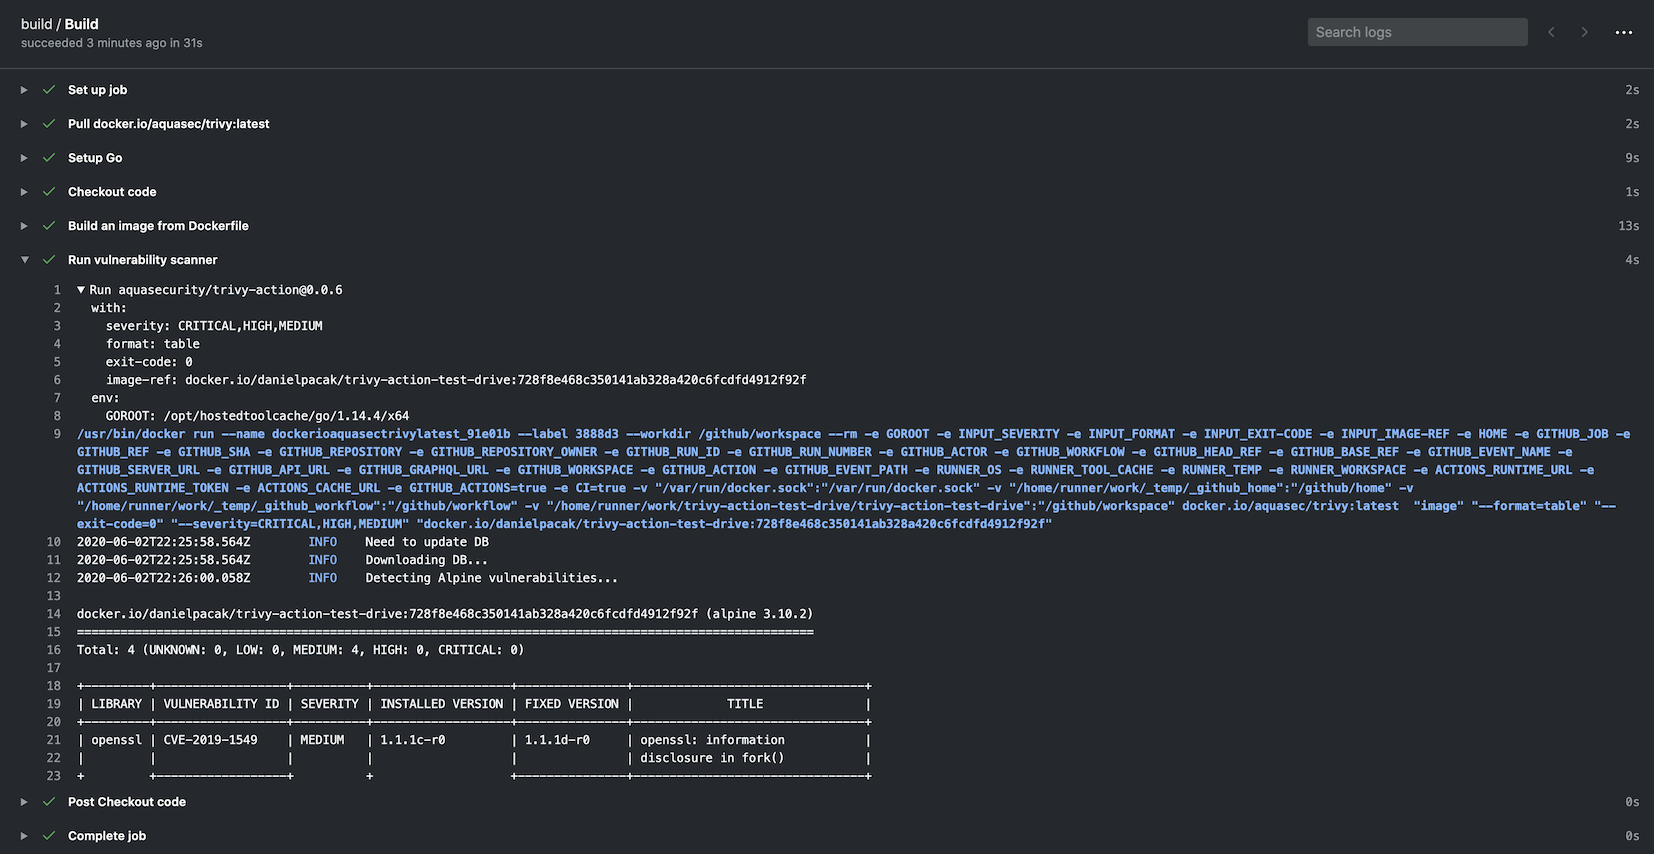
name: build
on:
  push:
    branches:
      - main
  pull_request:
jobs:
  build:
    name: Build
    runs-on: ubuntu-24.04
    steps:
      - name: Checkout code
        uses: actions/checkout@v4
      - name: Build an image from Dockerfile
        run: docker build -t docker.io/my-organization/my-app:${{ github.sha }} .
      - name: Run Trivy vulnerability scanner
        uses: aquasecurity/[email protected]
        with:
          image-ref: 'docker.io/my-organization/my-app:${{ github.sha }}'
          format: 'table'
          exit-code: '1'
          ignore-unfixed: true
          vuln-type: 'os,library'
          severity: 'CRITICAL,HIGH'
name: build
on:
  push:
    branches:
    - main
  pull_request:
jobs:
  build:
    name: Build
    runs-on: ubuntu-24.04
    steps:
    - name: Checkout code
      uses: actions/checkout@v4

    - name: Run Trivy vulnerability scanner in fs mode
      uses: aquasecurity/[email protected]
      with:
        scan-type: 'fs'
        scan-ref: '.'
        trivy-config: trivy.yaml
この場合、trivy.yaml はリポジトリの一部としてチェックインされる YAML 設定です。詳細情報は Trivy のウェブサイトで入手できますが、例は以下のとおりです:
format: json
exit-code: 1
severity: CRITICAL
secret:
  config: config/trivy/secret.yaml
すべてのオプションは trivy.yaml ファイルで定義できます。アクション経由で個別のオプションを指定する方法は、後方互換性のために残されています。以下は設定ファイルでは定義できないため、指定が必須です:
scan-ref: fs, repo スキャンを使用する場合。image-ref: image スキャンを使用する場合。scan-type: スキャンタイプを定義する場合(例:image、fs、repo など)。Trivy は Viper を使用しており、オプションには定義された優先順位があります。順序は以下のとおりです:
このアクションには、スキャン中にダウンロードされた場合に脆弱性 DB、Java DB、およびチェックバンドルをキャッシュおよび復元する組み込み機能があります。
キャッシュはデフォルトで $GITHUB_WORKSPACE/.cache/trivy ディレクトリに保存されます。
キャッシュはスキャン開始前に復元され、スキャン終了後に保存されます。
内部的には actions/cache を使用していますが、必要な設定項目はより少なくなっています。 キャッシュの入力は任意であり、キャッシュはデフォルトで有効になっています。
キャッシュを無効にしたい場合は、cache 入力を false に設定しますが、レート制限の問題を避けるために有効のままにしておくことを推奨します。
    - name: Run Trivy scanner without cache
      uses: aquasecurity/[email protected]
      with:
        scan-type: 'fs'
        scan-ref: '.'
        cache: 'false'
GitHub Actions では、ブランチ間のキャッシュアクセスに制限があることに注意してください。
デフォルトでは、ワークフローは現在のブランチまたはデフォルトブランチ(通常は main または master)で作成されたキャッシュにアクセスして復元できます。
ブランチ間でキャッシュを共有する必要がある場合は、デフォルトブランチでキャッシュを作成し、現在のブランチで復元する必要があります。
ワークフローを最適化するには、cron ジョブを設定してデフォルトブランチのキャッシュを定期的に更新できます。 これにより、後続のスキャンはキャッシュされた DB を再ダウンロードせずに使用できます。
# Note: This workflow only updates the cache. You should create a separate workflow for your actual Trivy scans.
# In your scan workflow, set TRIVY_SKIP_DB_UPDATE=true and TRIVY_SKIP_JAVA_DB_UPDATE=true.
name: Update Trivy Cache

on:
  schedule:
    - cron: '0 0 * * *'  # Run daily at midnight UTC
  workflow_dispatch:  # Allow manual triggering

jobs:
  update-trivy-db:
    runs-on: ubuntu-latest
    steps:
      - name: Setup oras
        uses: oras-project/setup-oras@v1

      - name: Get current date
        id: date
        run: echo "date=$(date +'%Y-%m-%d')" >> $GITHUB_OUTPUT

      - name: Download and extract the vulnerability DB
        run: |
          mkdir -p $GITHUB_WORKSPACE/.cache/trivy/db
          oras pull ghcr.io/aquasecurity/trivy-db:2
          tar -xzf db.tar.gz -C $GITHUB_WORKSPACE/.cache/trivy/db
          rm db.tar.gz

      - name: Download and extract the Java DB
        run: |
          mkdir -p $GITHUB_WORKSPACE/.cache/trivy/java-db
          oras pull ghcr.io/aquasecurity/trivy-java-db:1
          tar -xzf javadb.tar.gz -C $GITHUB_WORKSPACE/.cache/trivy/java-db
          rm javadb.tar.gz

      - name: Cache DBs
        uses: actions/cache/save@v4
        with:
          path: ${{ github.workspace }}/.cache/trivy
          key: cache-trivy-${{ steps.date.outputs.date }}
スキャンを実行する際は、環境変数 TRIVY_SKIP_DB_UPDATE と TRIVY_SKIP_JAVA_DB_UPDATE を設定してダウンロード処理をスキップしてください。
    - name: Run Trivy scanner without downloading DBs
      uses: aquasecurity/[email protected]
      with:
        scan-type: 'image'
        scan-ref: 'myimage'
      env:
        TRIVY_SKIP_DB_UPDATE: true
        TRIVY_SKIP_JAVA_DB_UPDATE: true
デフォルトでは、このアクションは最初のステップとして aquasecurity/setup-trivy を呼び出し、version 入力で指定されたバージョンの trivy をインストールします。他の手段で既に trivy をインストールしている場合(例: aquasecurity/setup-trivy を直接呼び出した場合、またはこのアクションを複数回実行する場合)は、skip-setup-trivy 入力を使用してこのステップを無効にできます。
name: build
on:
  push:
    branches:
    - main
  pull_request:
jobs:
  build:
    name: Build
    runs-on: ubuntu-24.04
    steps:
    - name: Checkout code
      uses: actions/checkout@v4

    - name: Manual Trivy Setup
      uses: aquasecurity/[email protected]
      with:
        cache: true
        version: v0.76.2

    - name: Run Trivy vulnerability scanner in repo mode
      uses: aquasecurity/[email protected]
      with:
        scan-type: 'fs'
        ignore-unfixed: true
        format: 'sarif'
        output: 'trivy-results.sarif'
        severity: 'CRITICAL'
        skip-setup-trivy: true
もう一つの一般的なユースケースは、ビルドがこのアクションを複数回呼び出す場合です。この場合、後続の呼び出しで skip-setup-trivy を true に設定できます。例:
name: build

on:
  push:
    branches:
      - main
  pull_request:

jobs:
  test:
    runs-on: ubuntu-latest
    permissions:
      contents: read
    steps:
      - name: Check out Git repository
        uses: actions/checkout@v4

      # The first call to the action will invoke setup-trivy and install trivy
      - name: Generate Trivy Vulnerability Report
        uses: aquasecurity/[email protected]
        with:
          scan-type: "fs"
          output: trivy-report.json
          format: json
          scan-ref: .
          exit-code: 0

      - name: Upload Vulnerability Scan Results
        uses: actions/upload-artifact@v4
        with:
          name: trivy-report
          path: trivy-report.json
          retention-days: 30






