Skip to content
KitploitKITPLOIT
ツールエクスプロイトブログ
Log in
提出
ツールエクスプロイトブログ
提出

ハッキング、侵入テスト、サイバーセキュリティツールをあなたのセキュリティアーセナルに!

Kitploitはハッキング、サイバーセキュリティ、ペネトレーションテストのツールディレクトリです。最新のプロジェクトアップデートを見つけて、脆弱性の発見、システム分析、テストの自動化、セキュリティの強化を行いましょう。

フィードお問い合わせプライバシー© 2026 Kitploit

ツールディレクトリ

カテゴリ

すべてのカテゴリを見る
Loading categories
Brovan — User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing, network dumping, and interactive debugging in a sandboxed environment. | Kitploit
ツール/GitHubGitHub/advdebug/brovan
Dynamic Analysis (Sandboxing)Dynamic Code Analysis (DAST)Reverse EngineeringDebuggersMalware AnalysisBinary Analysis
GitHubadvdebug/brovan

Brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing, network dumping, and interactive debugging in a sandboxed environment.

リポジトリを見る
155115011時間16分前Kitploit レビュー済み
共有
要求された言語のコンテンツは利用できません。英語版を表示しています。
Brovan banner


.NET Language License

A user-mode x86_64 binary emulator for inspecting programs, tracing syscalls, and safely running untrusted software.

What is Brovan?

Brovan is an interactive x86_64 emulator that gives you full control over how programs execute. It can be used to reverse engineer binaries, trace API and system calls, capture network traffic, or run software in an isolated environment without executing it directly on your host CPU.

It is designed to support as much software as possible while remaining a safe, efficient, and high-performance option for running Windows and Linux software across Windows, Linux and Android. Brovan is still in early development, so it is not yet fully mature or reliable.

Supported backends:

  • Unicorn Engine for cross-platform emulation
  • WHP (Windows Hypervisor Platform) for hardware acceleration on Windows
  • KVM (Kernel-based Virtual Machine) for hardware acceleration on Linux

Core Features

MULTI-FORMAT LOADING

Load and execute binaries directly inside the emulator without host installation.

PE   ELF   Memory Dumps   Raw Shellcode

BROVVULK GRAPHICS LAYER

Custom Vulkan translation subsystem handling DXVK calls and game rendering.

DXVK   DirectX   Vulkan Surface

SYSCALL & API TRACING

Inspect execution live to see what functions, DLLs, and kernel calls the program accesses.

Kernel Syscalls   Symbol Resolving   Loaded DLLs

NETWORK DUMPING

Intercept guest socket traffic and export network activity for payload analysis.

Socket Intercept   PCAP Capture   Traffic Analysis

Previews & Demos

Gaming & Graphics (Brovvulk)

Brovan can render guest graphical applications through its Brovvulk (Brovan<->Vulkan) translation subsystem. Here is a sample game i had (Deltarune), but it can work on many other games:
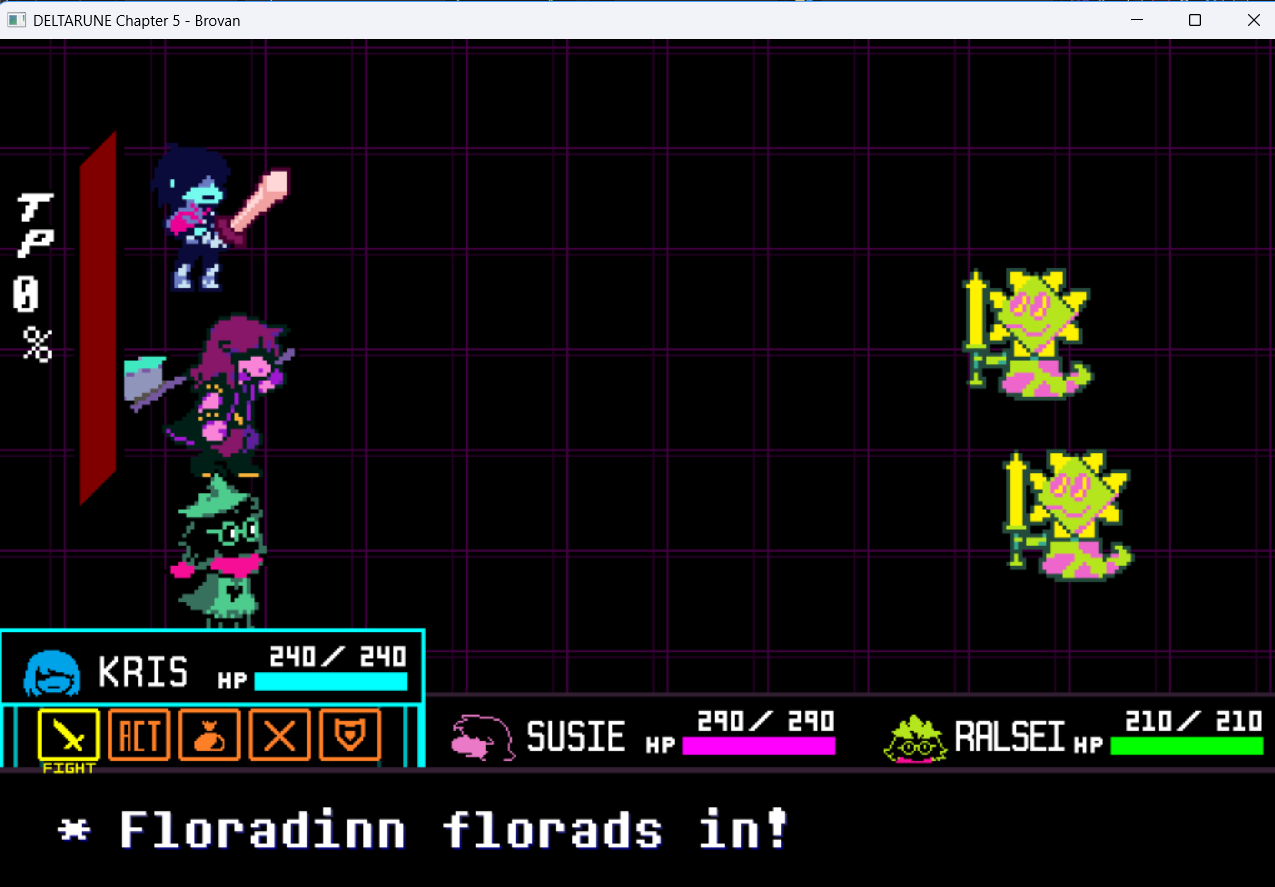
Deltarune running in Brovan

Deltarune Bring-up

  • Vulkan surface rendering via Brovvulk
  • DPI-aware host window integration
  • WHP acceleration for a smoother gaming experience

Binary Execution & Tracing

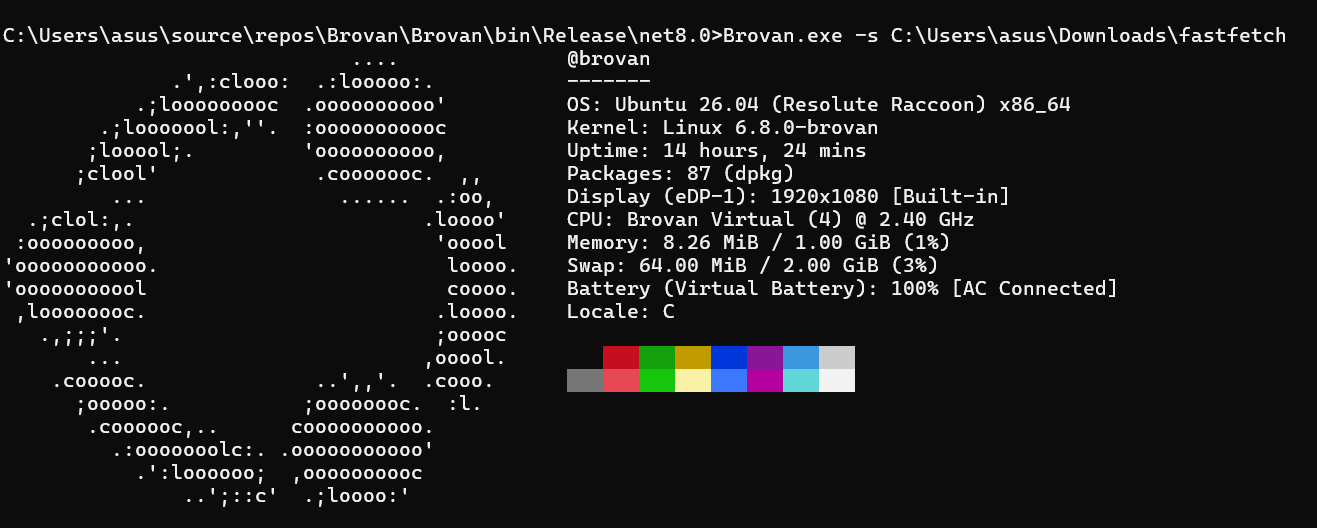
Cross-platform Linux execution
Linux ELF on Windows
Running fastfetch cross-platform
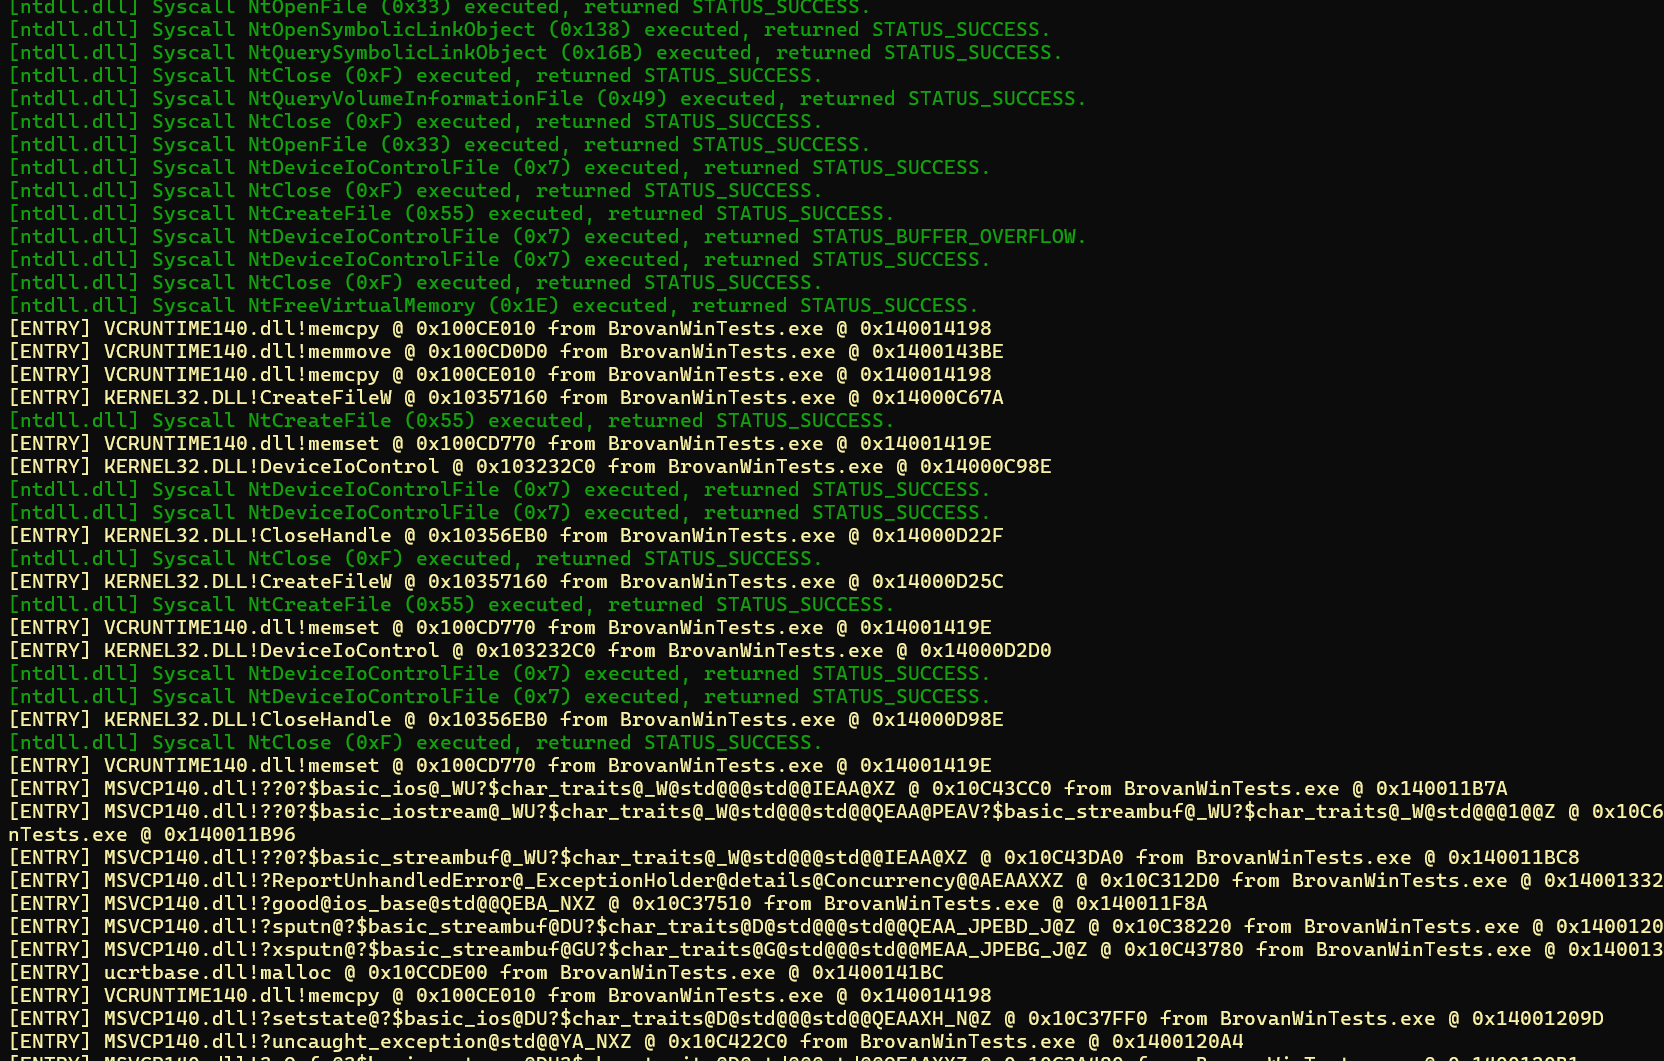
Syscall tracing log
Syscall Tracing
Live logs of API calls and dynamic symbols
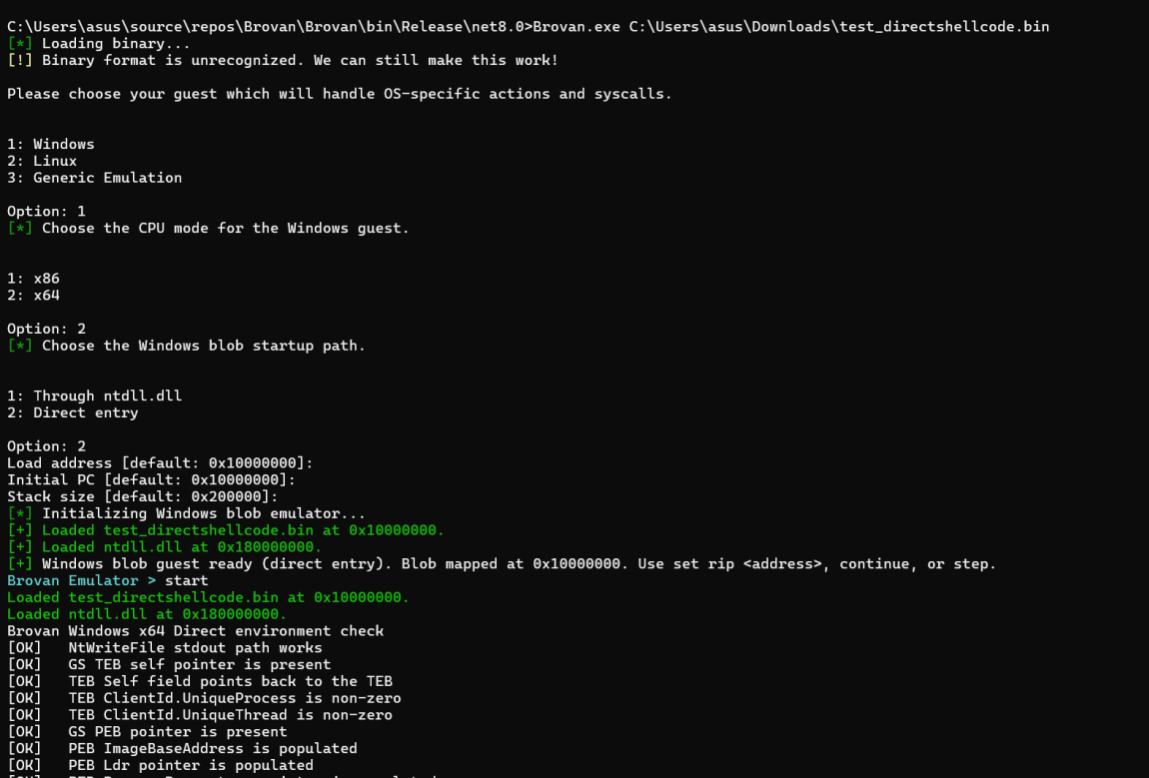
Raw binary execution
Raw Binaries
Executing shellcode and memory dumps

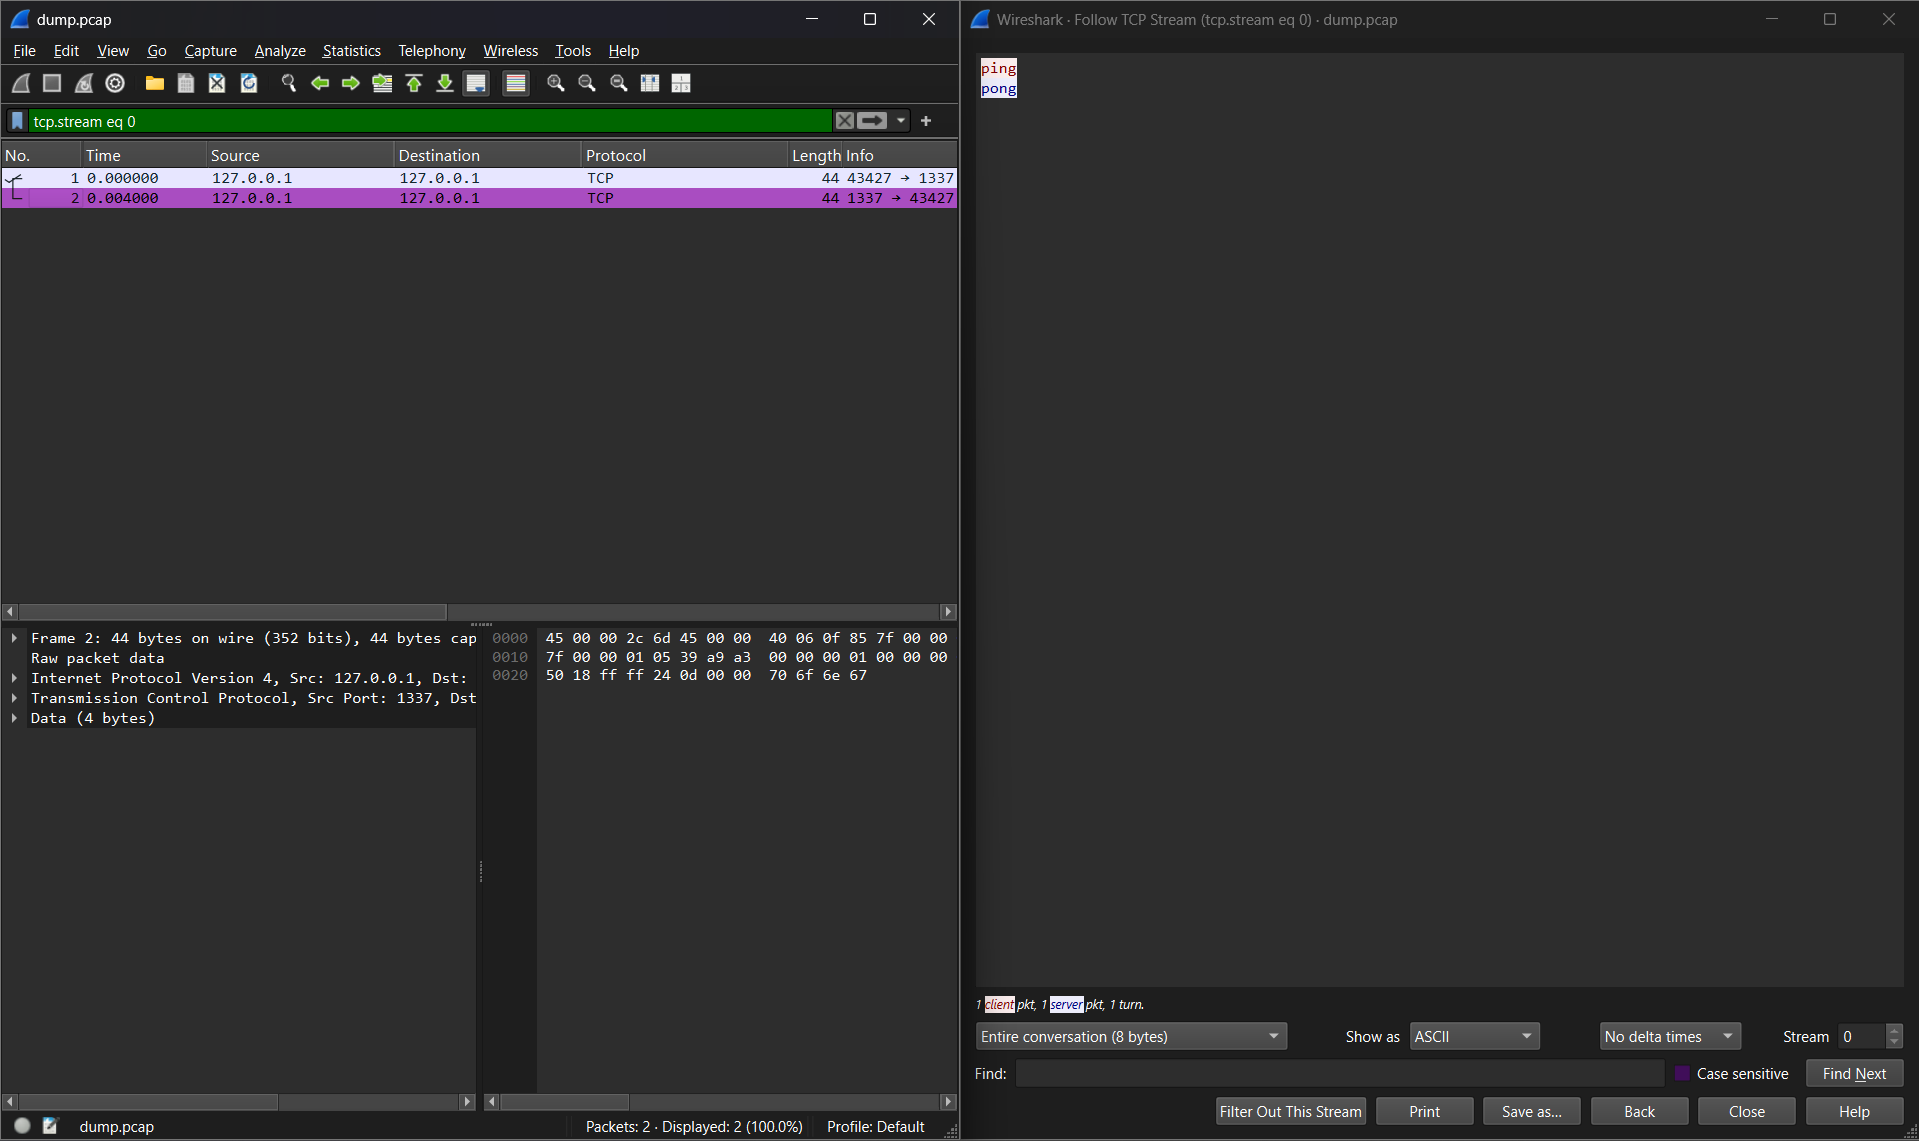
Network Inspection

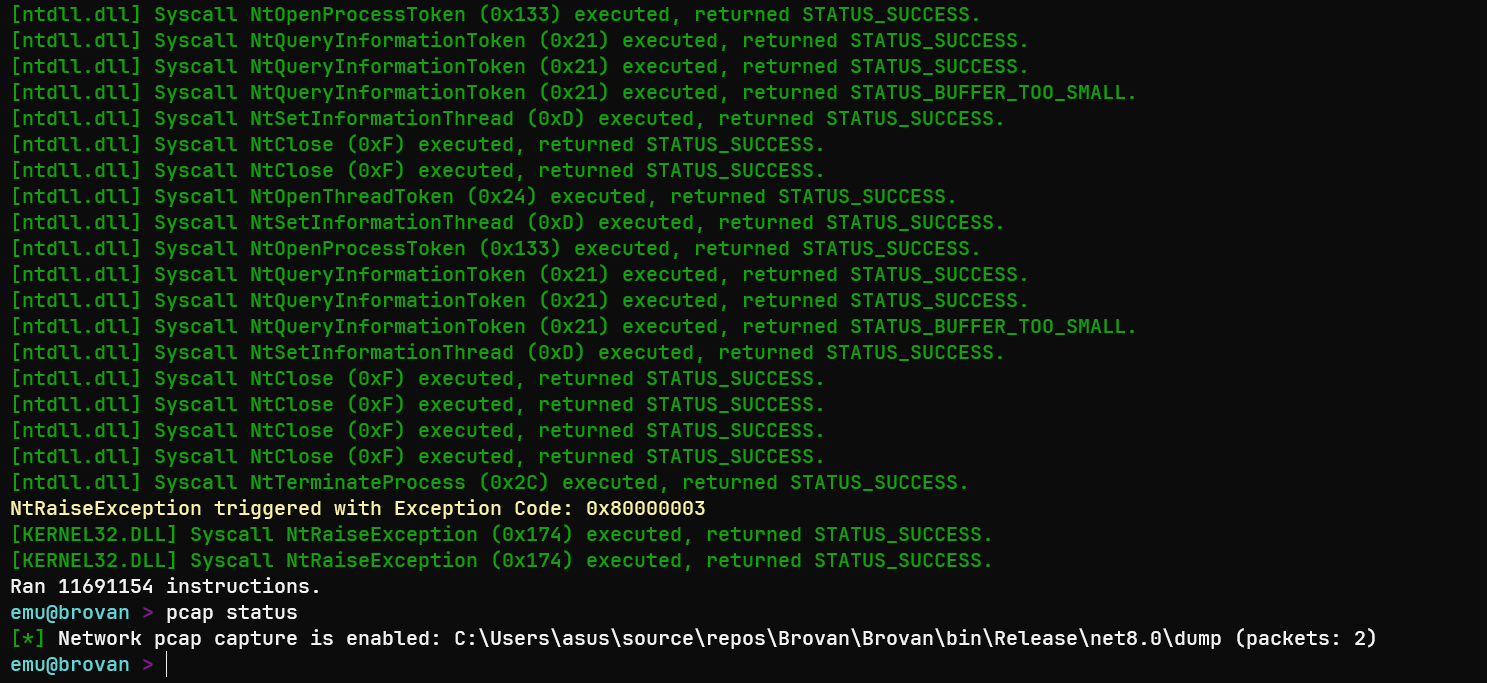
Network dumping
Network Capture
Intercepting guest socket reads and writes
Traffic viewer
Traffic Analyzer
Viewing dumped PCAPs and payloads

Documentation & Wiki

Check out the GitHub Wiki for:

  • Building from source
  • Architecture details
  • Command reference and usage guides
  • FAQ

[!WARNING] The Releases page may not always have the latest changes.
For the most up-to-date version, build from source instead or use the latest build from GitHub Actions

Credits

Thanks to Iced library for x86_64 disassembly and assembly.

Thanks to Unicorn Engine for the core emulator.

Thanks to Mesa for zink, which gives Windows programs OpenGL on top of Brovvulk.

ツールをダウンロード

人気

すべて見る →

コミュニティで最も使われているツールを見つけましょう。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 究極のOSINTツールキット:調査グラフ、信頼度スコアリング、エイリアスファミリー、マップ、タイムライン、レポート。49個のモジュール、400以上のサイト、APIキー不要。

    509
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock ワンタップ実行アプリ(CVE-2026-43499)

    469
  • 3

    ARTEX

    baarai/artex

    プランナー/ワーカーエージェント、資産グラフと探索グラフ、MITMトラフィック記録、脆弱性の再テストを備えたLLMマルチエージェント自律ペネトレーションテストプラットフォーム。

    343
  • 4

    redforge

    cybersecurity91/redforge

    ブラウザ側のレッドチームツールキット。偵察、ペイロード生成、認証情報攻撃、暗号、エンコーディング、エンゲージメントレポート向けの102のオフラインツールを備えています。

    310
  • 5

    opencti

    opencti-platform/opencti

    オープンサイバー脅威インテリジェンスプラットフォーム

    306
  • 6

    estorides

    grisuno/estorides

    99以上の無料OSINTソースを並列で集約し、エンティティをナレッジグラフに解決し、LLM支援の分析とともにSTIX 2.1、MISP、またはGraphMLでエクスポートします。

    301

すべてのツールを探索

ツールコレクションを閲覧

すべてのツールを見る →