

Skip to content
KitploitKITPLOIT
ツールエクスプロイトブログ
Log in
提出
ツールエクスプロイトブログ
提出

ハッキング、侵入テスト、サイバーセキュリティツールをあなたのセキュリティアーセナルに!

Kitploitはハッキング、サイバーセキュリティ、ペネトレーションテストのツールディレクトリです。最新のプロジェクトアップデートを見つけて、脆弱性の発見、システム分析、テストの自動化、セキュリティの強化を行いましょう。

フィードお問い合わせプライバシー© 2026 Kitploit

ツールディレクトリ

カテゴリ

すべてのカテゴリを見る
Loading categories
ログ分析 — 36 ページ | Kitploit
カテゴリ

ログ分析

ログ解析、SIEM、集中ログ記録、フォレンジックタイムライン、セキュリティイベント相関ツール。

Kitploit おすすめ

おすすめツール

10 選択中
wazuh preview#1

wazuh

GitHubwazuh/wazuh
16.5k1日前
graylog2-server preview#2

graylog2-server

GitHubgraylog2/graylog2-server
8.2k4時間23分前
loki preview#3

loki

GitHubgrafana/loki
29.0k8時間56分前
osquery preview#7

osquery

GitHubosquery/osquery
23.4k5日前
securityonion preview#8

securityonion

GitHubsecurity-onion-solutions/securityonion
4.9k1ヶ月前
zeek preview#9

zeek

GitHubzeek/zeek
7.8k14時間47分前
suricata preview#10

suricata

GitHuboisf/suricata
6.5k4日前
sigma preview#11

sigma

GitHubsigmahq/sigma
10.9k11時間27分前
detection-rules preview#12

detection-rules

GitHubelastic/detection-rules
2.7k8時間48分前
logparser preview#13

logparser

GitHublogpai/logparser
2.0k1年前
最新関連度人気最近更新
682 件
S1EM preview

S1EM

GitHubv1d1an/s1em

このプロジェクトは、SIEM、SIRP、Threat Intelをすべて統合したものです。

vulnerability-scannersforensicsnetwork-security+6
4621年前
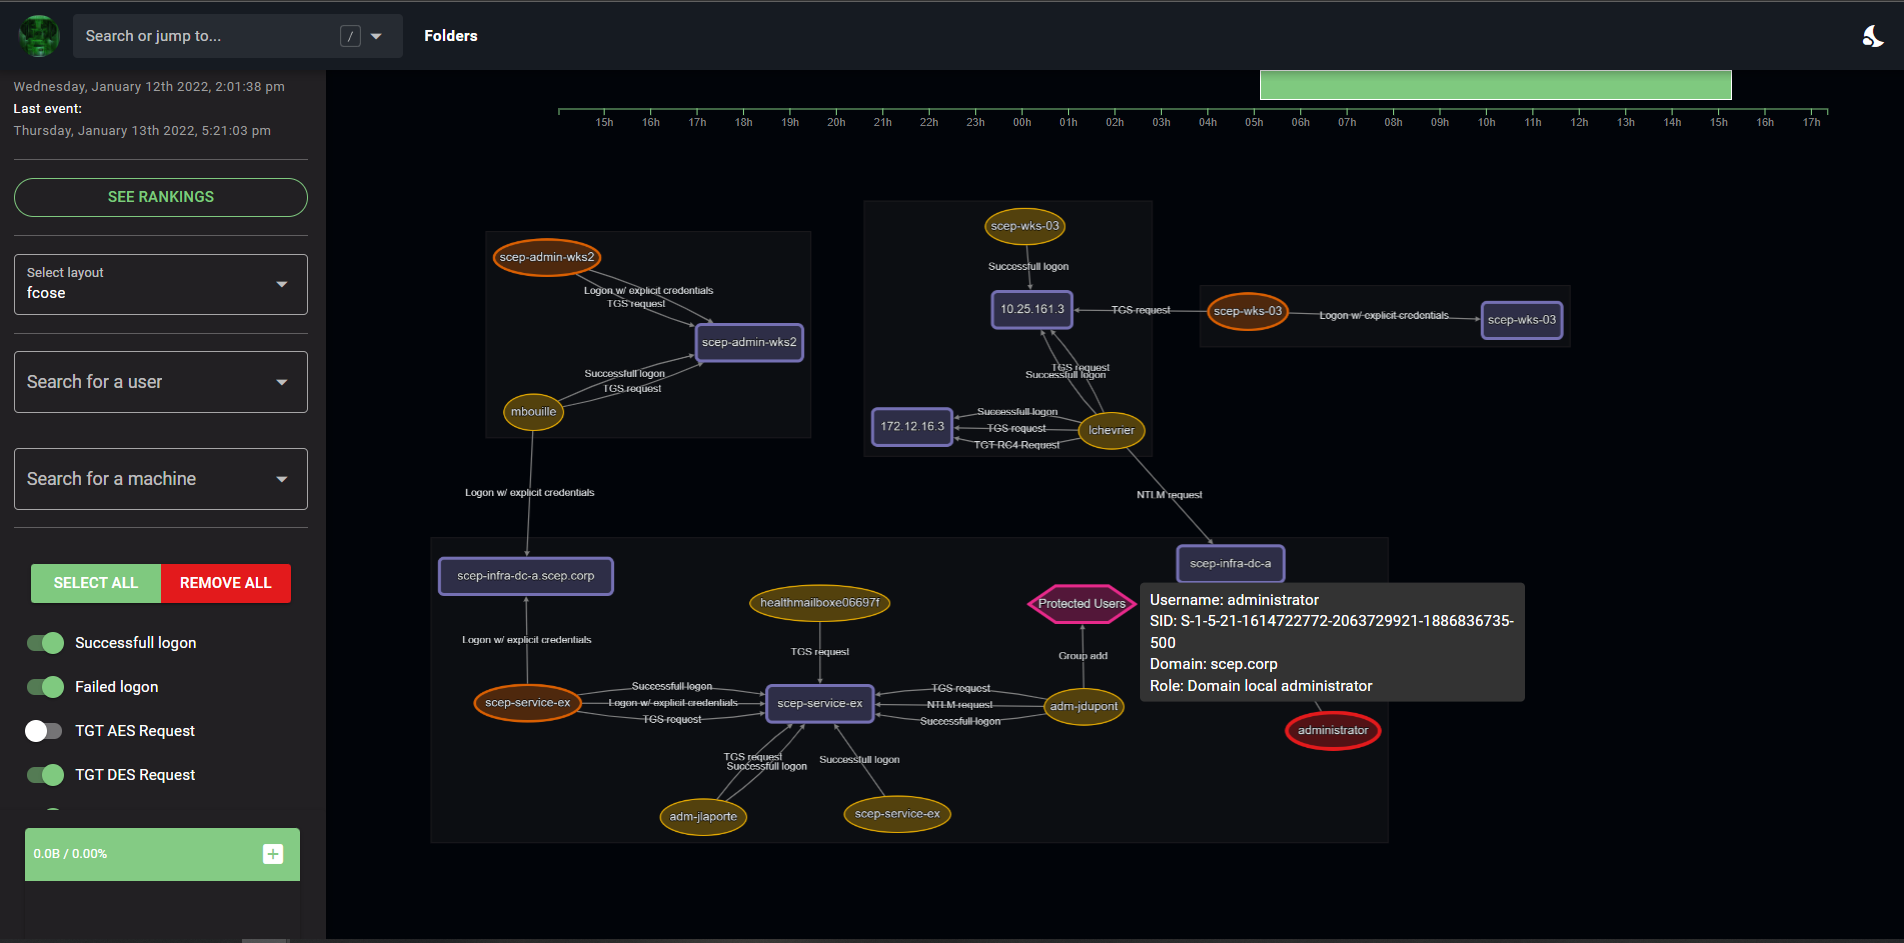
epagneul preview

epagneul

GitHubjurelou/epagneul

Windows イベントログのグラフ可視化

forensicslog-analysis
2511年前
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

マルチスレッド対応のWindowsイベントログフォレンジックタイムライン生成および脅威ハンティングツール。Sigmaルールを完全サポートし、Elastic Stack、Timesketch、Timeline Explorerで分析するためのCSV/JSONタイムラインを出力します。
forensicsdigital-forensicsthreat-intelligence+2
3.3k7日前
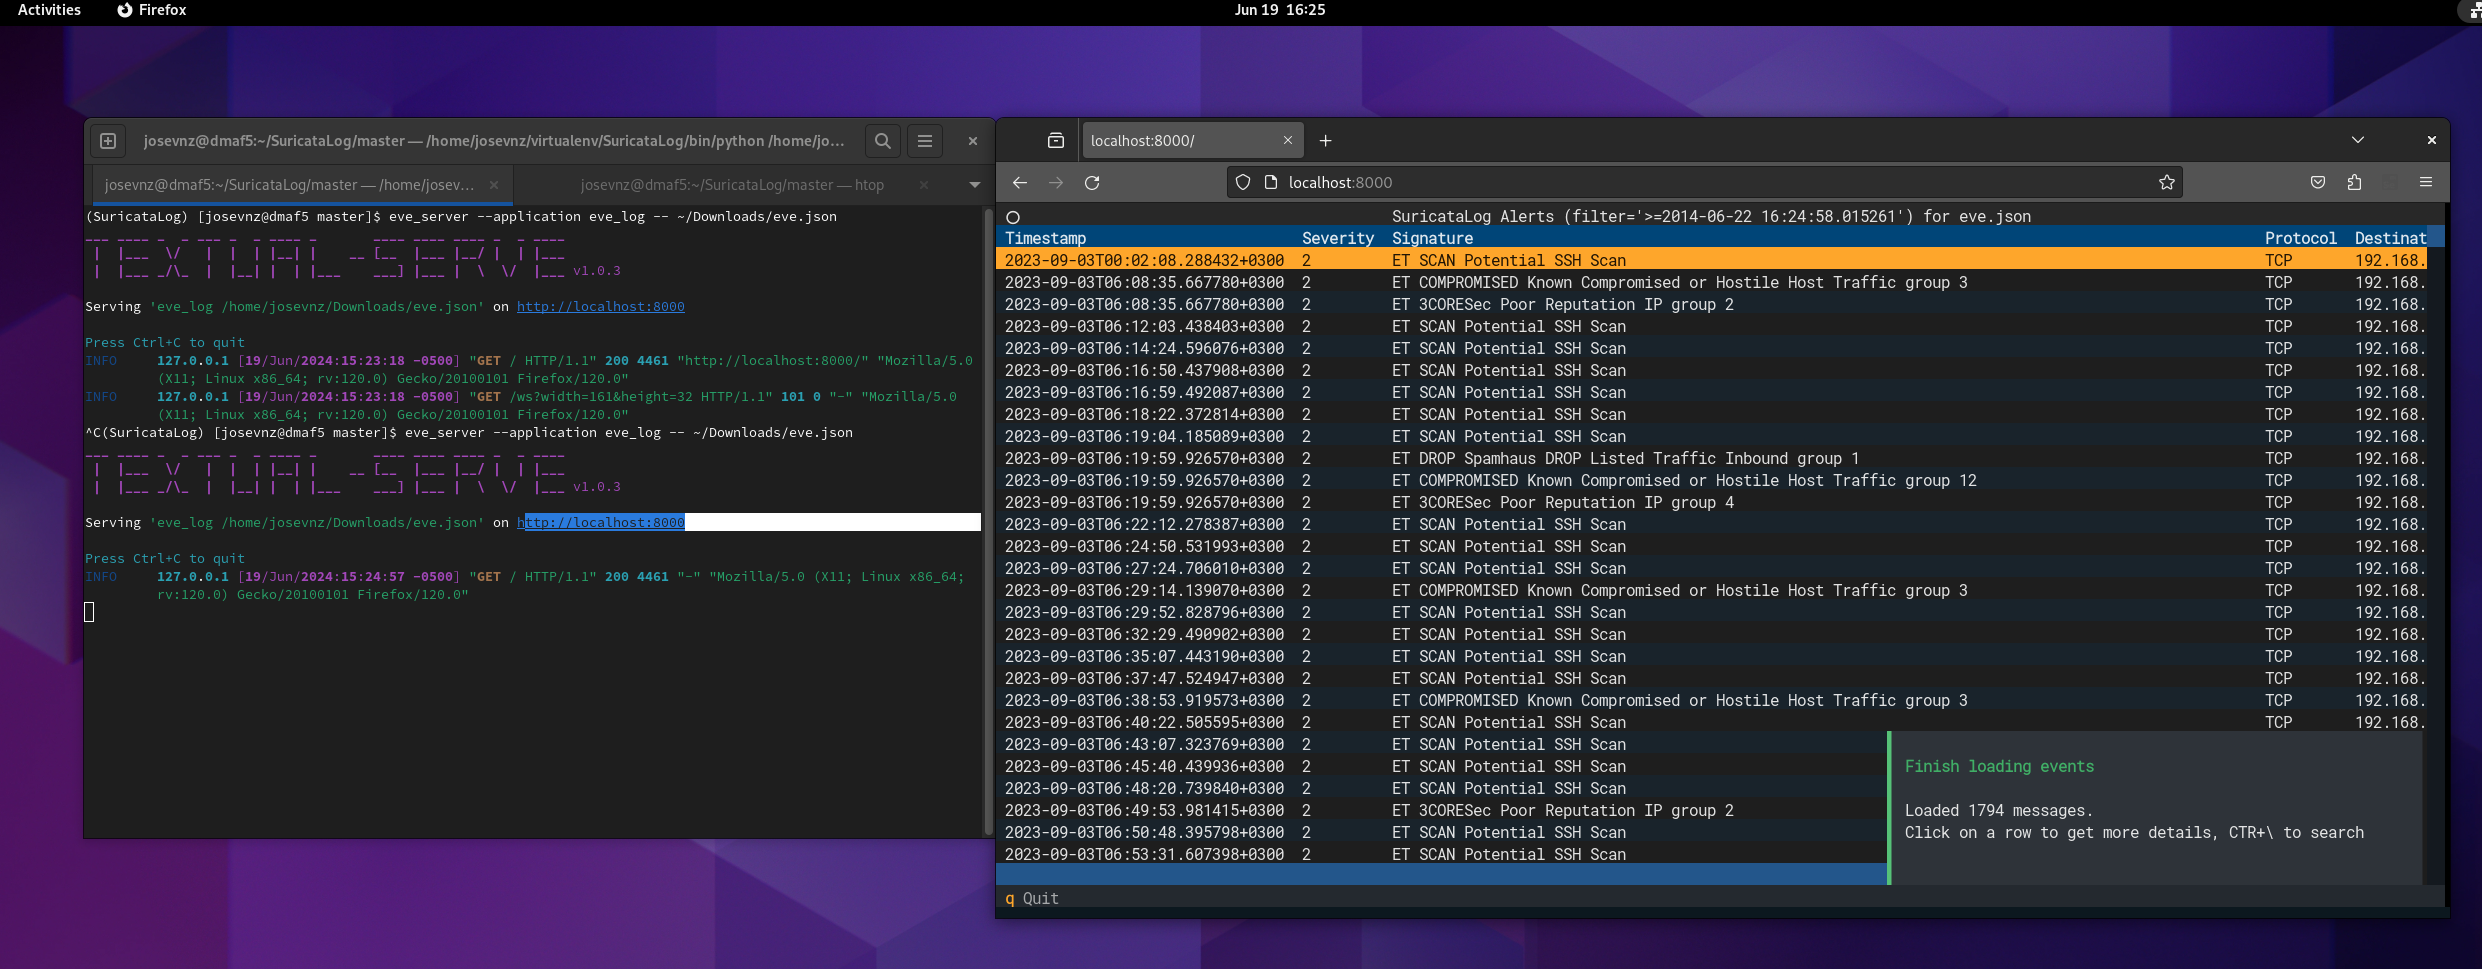
SuricataLog preview

SuricataLog

GitHubjosevnz/suricatalog

Suricataのeve.jsonログを解析、フィルタリング、可視化するCLIツール。アラート、フロー、DNS、ペイロードに対応。Suricataの学習とルールテストのためのチュートリアルも含まれています。
network-securityintrusion-detectioneducation+1
2713日前
L3MON preview

L3MON

GitHubd3vl/l3mon

ウェブベースのネットワーク監視システムで、リアルタイムの帯域幅トラッキング、サーバーパフォーマンスメトリクス、およびプロアクティブなネットワーク管理のためのカスタマイズ可能なアラートを提供します。

network-mappingnetwork-securitylog-analysis
2863年前
DetectionLabELK preview

DetectionLabELK

GitHubcyberdefenders/detectionlabelk

DetectionLabELKは、Splunkの代わりにELKスタックを使用するDetectionLabのフォークです。
defensive-toolsosintconfiguration-auditing+7
5755年前
SnitchDNS preview

SnitchDNS

GitHubctxis/snitchdns

Web UIを備えたデータベース駆動型DNSサーバー
phishing-toolsdata-exfiltrationinformation-gathering+7
2442年前
DFIR-O365RC preview

DFIR-O365RC

GitHubanssi-fr/dfir-o365rc

Office 365およびAzureログ収集のためのPowerShellモジュール

forensicsdigital-forensicscloud-security+2
2821年前
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
disk-forensicsioc-managementvulnerability-analysis+8
856ヶ月前
hawk preview

hawk

GitHubt0pcyber/hawk

Powershellベースのツール、O365の侵入や潜在的な侵害に関する情報収集のための。
cloud-infrastructure-securityinformation-gatheringdigital-forensics+3
9491年前
Cowrie and Grafana Honeypot using Terraform on DigitalOcean preview

Cowrie and Grafana Honeypot using Terraform on DigitalOcean

GitLaboseguera12/cowrie-honeypot-digitalocean

Cowrie、Loki、Promtail、Grafanaを使用して構築された中程度の対話型SSH/Telnetハニーポット - GitLab CI検証パイプラインを使用してTerraform経由でDigitalOcean上にプロビジョニング。
cloud-infrastructure-securitynetwork-securitydevsecops+2
124日前
deadair preview

deadair

GitHubbig-comfy/deadair

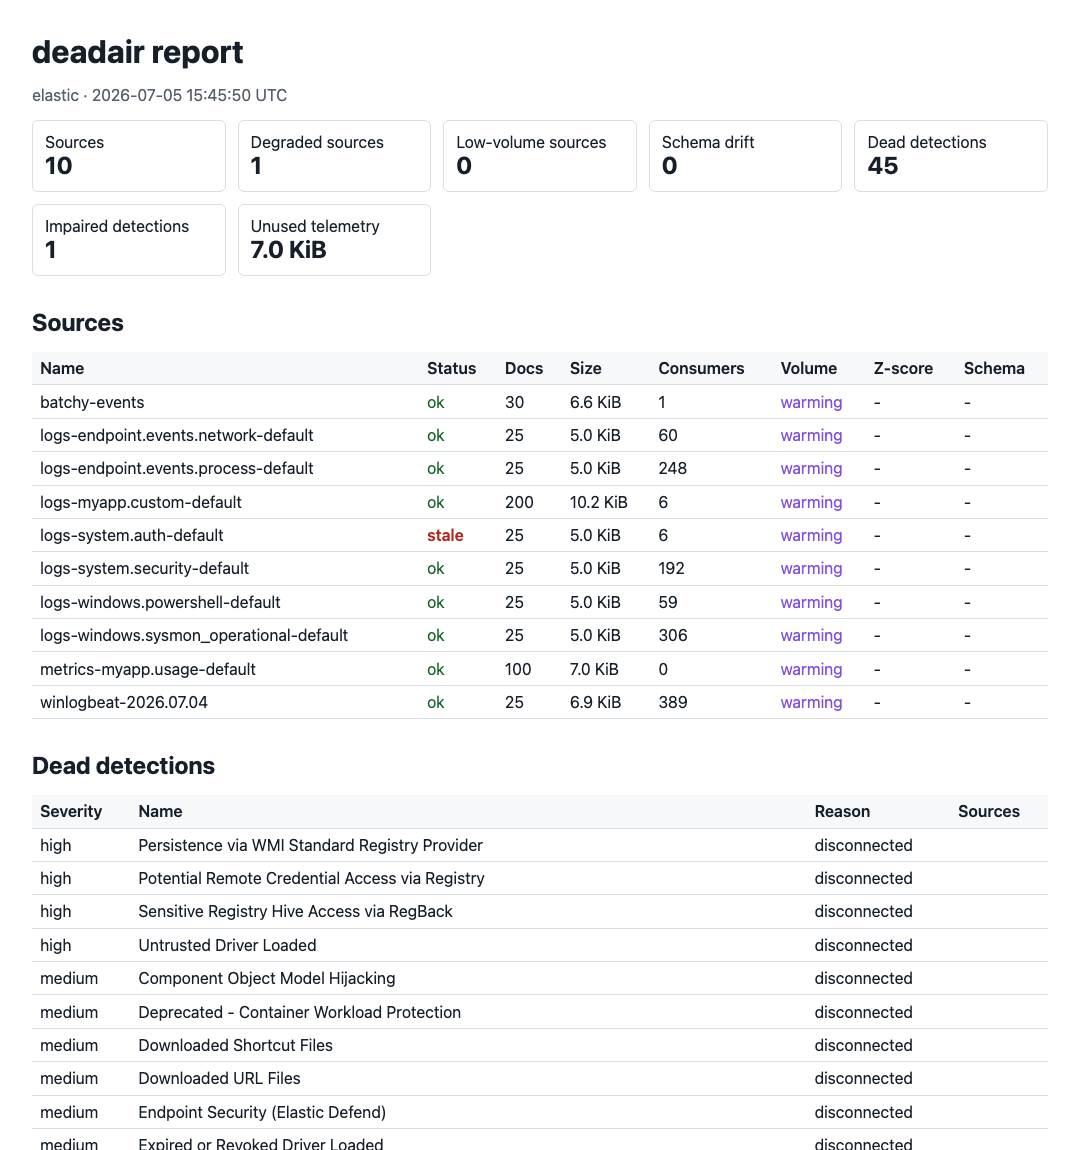
SIEM内でブラインド状態になっている検出ルールを見つけ出します

vulnerability-analysisconfiguration-auditinglog-analysis
61ヶ月前
tirreno preview

tirreno

GitHubtirrenotechnologies/tirreno

リアルタイムなイベント追跡、脅威検出、リスクスコアリングのためのオープンソースセキュリティフレームワーク。ルールエンジンと監査証跡を介してユーザー行動を監視し、不正、ボット攻撃、アカウント乗っ取りを検出します。

threat-intelligenceincident-responseapi-security+3
1.5k14日前
How-To-Secure-A-Linux-Server preview

How-To-Secure-A-Linux-Server

GitHubimthenachoman/how-to-secure-a-linux-server

Linuxサーバーの堅牢化のためのステップバイステップガイド。SSHセキュリティ、ファイアウォール、侵入検知、監査、システム設定を網羅し、攻撃対象領域を減らし防御を強化します。

vulnerability-scannersconfiguration-auditingnetwork-security+7
30.3k1ヶ月前
kippo-g0tmi1k preview
Archived

kippo-g0tmi1k

GitHubg0tmi1k/kippo-g0tmi1k

ブルートフォース攻撃と攻撃者のシェル操作全体を記録する中規模インタラクション型SSHハニーポット。フィンガープリンティングを低減するためのカスタマイズオプション付き。

defensive-toolspassword-attacksinformation-gathering+4
1312年前
dfir-toolkit preview
Archived

dfir-toolkit

GitHubdfir-dd/dfir-toolkit

Windowsアーティファクトのフォレンジック調査用CLIツール
disk-forensicsforensicsdigital-forensics+2
3551年前
EventLogging preview
Archived

EventLogging

GitHubblackhillsinfosec/eventlogging

Active Directory 環境で Windows イベント転送、Sysmon、およびカスタム監査ポリシーを展開するための自動化スクリプト。

defensive-toolsscripting-automationconfiguration-auditing+3
4911年前
BearFTP preview
Archived

BearFTP

GitHubkolya5544/bearftp

.NET Core (C#) で書かれた、Linux と Windows の両方に対応したハニーポット FTP サーバー。

defensive-toolsinformation-gatheringnetwork-security+4
143年前
前へ1…35363738次へ