#1
 jenderal92/poc-autosync
🧠 poc-in-github.motikan2010.net から公開されている Proof-of-Concept (PoC) エクスプロイトを自動的に収集・更新します。
 azure/azure-sentinel
企業全体のインテリジェントなセキュリティ分析のためのクラウドネイティブSIEM。
 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 patrickmgarrity/anthropic-credited-cves
Anthropic 研究チームに帰属していると思われる脆弱性の追跡
 hacktricks-wiki/hacktricks
CTFや実際のアプリケーション、研究やニュースから学んだ各トリック/テクニック/あらゆるものを紹介するページへようこそ。
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
 horkimhab/poc-cve-collection
🧪 CVE PoCを収集し、GitHubで利用できない場合にはInternet Archiveにバックアップします。
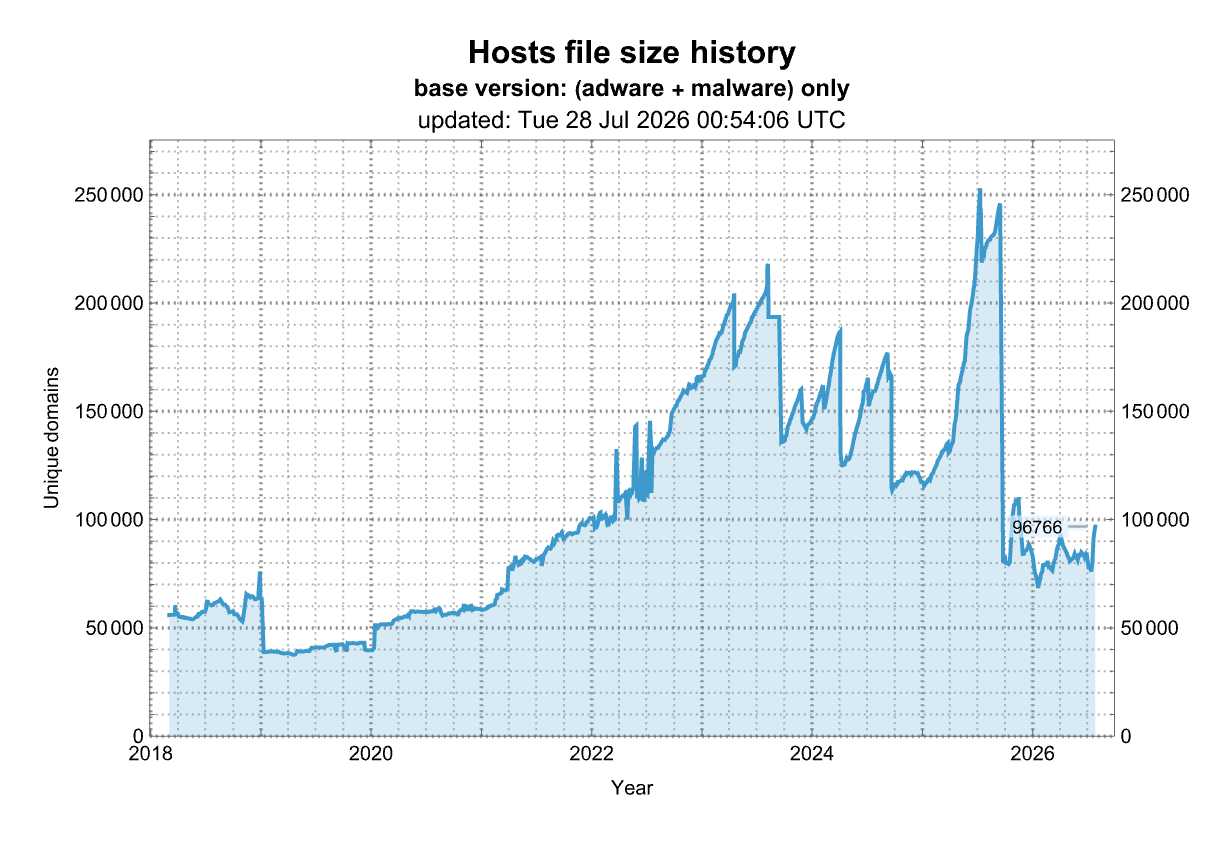 stevenblack/hosts
🔒 Consolidating and extending hosts files from several well-curated sources. Optionally pick extensions for porn, social media, and other categories.
 asgeirtj/system_prompts_leaks
Curated collection of extracted system prompts from major AI chatbots including Claude, ChatGPT, Gemini, Grok, and Copilot. Updated regularly with…
 trailofbits/skills
Trail of Bits Claude Code スキル: セキュリティ研究、脆弱性検出、および監査ワークフロー向け
 cisagov/kev-data
CISAのKnown Exploited Vulnerabilities(KEV)カタログをCSVおよびJSON(JSONスキーマ付き)としてミラーリングし、KEV更新へのプログラムによるアクセスとコミット履歴の追跡を可能にします。
 oritwoen/boha
Crypto bounties, puzzles and challenges data library
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 aquasecurity/vuln-list-debian
Debian セキュリティトラッカー
 aquasecurity/vuln-list-nvd
NVD
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)