 target/strelka
Scansione di file in tempo reale basata su container su scala aziendale

<h1 align="center">
<img src="https://assets.kitploit.com/production/public/readmes/2436/2065ad071dd20cf7e35ddddfba0598d78452e4670e89342eed6f7a190a0a1fcb.png" alt="Banner di Strelka" />
</h1>
<div align="center">
[Rilasci][release] | [Documentazione][wiki] | [Pull Requests][pr] | [Issues][issues]
[![Rilascio GitHub][img-version-badge]][repo] [![Stato Build][img-actions-badge]][actions-ci] [![Pull Requests][img-pr-badge]][pr] [![Slack][img-slack-badge]][slack] [![Licenza][img-license-badge]][license]
</div>
Strelka è un sistema di scansione file in tempo reale basato su container, utilizzato per la caccia alle minacce, il rilevamento delle minacce e la risposta agli incidenti. Originariamente basato sul design stabilito da Lockheed Martin [Laika BOSS](https://github.com/lmco/laikaboss) e progetti simili (vedi: [progetti correlati](#related-projects)), lo scopo di Strelka è eseguire l'estrazione di file e la raccolta di metadati su scala aziendale.
Strelka si differenzia dai progetti fratelli in alcuni aspetti significativi:
* Il codice base principale è in Go e Python3.10+
* I componenti server vengono eseguiti in container per facilità e flessibilità di distribuzione
* Applicazioni client native per Windows, Mac e Linux
* Costruito utilizzando [librerie e formati](#architecture) che supportano l'uso multipiattaforma e multilinguaggio
## Caratteristiche
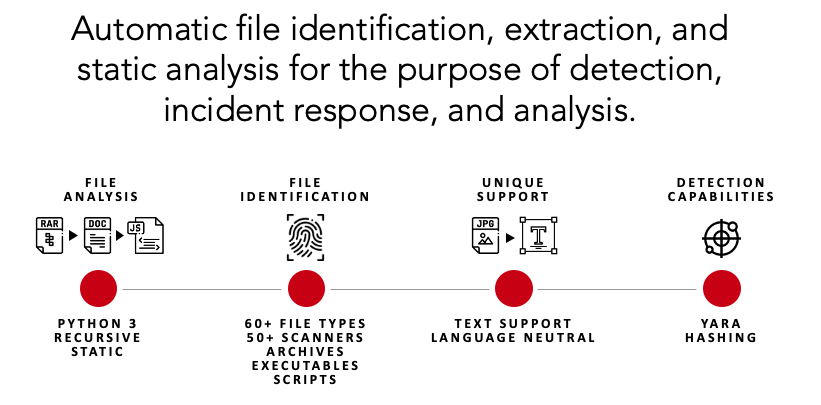
Strelka è una piattaforma modulare di scansione dati che consente a utenti o sistemi di inviare file allo scopo di analizzare, estrarre e riportare contenuti e metadati dei file. Abbinato a un [SIEM](https://en.wikipedia.org/wiki/Security_information_and_event_management), Strelka è in grado di aggregare, allertare e fornire agli analisti la capacità di comprendere meglio il proprio ambiente senza dover eseguire raccolta diretta di dati o analisi file dispendiose in tempo.
## Avvio rapido
Eseguire un file attraverso Strelka è semplice. In questa sezione, le capacità di estrazione e analisi di Strelka vengono dimostrate per un'analisi una tantum.
*Si prega di consultare la [documentazione](https://target.github.io/strelka/) per i dettagli su come costruire e distribuire correttamente Strelka in un ambiente aziendale.*
#### Passo 1: Installare i prerequisiti
```bash
# Ubuntu 23.04
sudo apt install -y wget git docker docker-compose golang jq && \
sudo usermod -aG docker $USER && \
newgrp docker
````
#### Passo 2: Scaricare Strelka
```bash
git clone https://github.com/target/strelka.git && \
cd strelka
```
#### Passo 3: Scaricare e installare le regole yara preferite (opzionale)
```bash
rm configs/python/backend/yara/rules.yara && \
git clone https://github.com/Yara-Rules/rules.git configs/python/backend/yara/rules/ && \
echo 'include "./rules/index.yar"' > configs/python/backend/yara/rules.yara
```
#### Passo 4a: Scaricare immagini precompilate e avviare Strelka
**Nota**: Puoi saltare il processo `go build` e utilizzare la `Strelka UI` all'indirizzo `http://0.0.0.0:9980` per analizzare i file.
```bash
docker compose -f build/docker-compose-no-build.yaml up -d && \
go build github.com/target/strelka/src/go/cmd/strelka-oneshot
```
#### Passo 4b: Costruire e avviare Strelka
**Nota**: Puoi saltare il processo `go build` e utilizzare la `Strelka UI` all'indirizzo `http://0.0.0.0:9980` per analizzare i file.
```bash
docker compose -f build/docker-compose.yaml build && \
docker compose -f build/docker-compose.yaml up -d && \
go build github.com/target/strelka/src/go/cmd/strelka-oneshot
```
#### Passo 5: Preparare un file da analizzare
Usa qualsiasi campione di malware, o altro file che desideri far analizzare a Strelka.
```bash
wget https://github.com/ytisf/theZoo/raw/master/malware/Binaries/Win32.Emotet/Win32.Emotet.zip -P samples/
```
#### Passo 6: Analizzare il file con Strelka utilizzando lo oneshot containerizzato
```bash
./strelka-oneshot -f samples/Win32.Emotet.zip -l - | jq
```
#### Cosa sta succedendo?
1. Strelka ha determinato che il file inviato era uno ZIP crittografato (Vedi: [taste.yara](https://github.com/target/strelka/blob/master/configs/python/backend/taste/taste.yara) [backend.yaml](https://github.com/target/strelka/blob/master/configs/python/backend/backend.yaml))
2. [ScanEncryptedZip](https://github.com/target/strelka/blob/master/src/python/strelka/scanners/scan_encrypted_zip.py) ha utilizzato un dizionario per forzare la password del file ZIP ed estrarre il file compresso
3. Il file estratto è stato reinviato nella pipeline di Strelka dallo scanner, e Strelka ha determinato che il file estratto era un EXE
4. [ScanPe](https://github.com/target/strelka/blob/master/src/python/strelka/scanners/scan_pe.py) ha sezionato il file EXE e aggiunto metadati utili all'output
5. [ScanYara](https://github.com/target/strelka/blob/master/src/python/strelka/scanners/scan_yara.py) ha analizzato il file EXE utilizzando le regole fornite e ha aggiunto numerose corrispondenze all'output, alcune delle quali indicano che il file potrebbe essere malevolo
*Il seguente output è stato modificato per brevità.*
```json
{
"file": {
"depth": 0,
"flavors": {
"mime": ["application/zip"],
"yara": ["encrypted_zip", "zip_file"]
},
"scanners": [
"ScanEncryptedZip",
"ScanEntropy",
"ScanFooter",
"ScanHash",
"ScanHeader",
"ScanYara",
"ScanZip"
]
},
"scan": {
"encrypted_zip": {
"cracked_password": "infected",
"elapsed": 0.114269,
"total": {"extracted": 1, "files": 1}
}
}
}
```
```json
{
"file": {
"depth": 1,
"flavors": {
"mime": ["application/x-dosexec"],
"yara": ["mz_file"]
},
"name": "29D6161522C7F7F21B35401907C702BDDB05ED47.bin",
"scanners": [
"ScanEntropy",
"ScanFooter",
"ScanHash",
"ScanHeader",
"ScanPe",
"ScanYara"
]
},
"scan": {
"pe": {
"address_of_entry_point": 5168,
"base_of_code": 4096,
"base_of_data": 32768,
"checksum": 47465,
"compile_time": "2015-03-31T08:53:51",
"elapsed": 0.013076,
"file_alignment": 4096,
"file_info": {
"company_name": "In CSS3",
"file_description": "Note: In CSS3, the text-decoration property is a shorthand property for text-decoration-line, text-decoration-color, and text-decoration-style, but this is currently.",
"file_version": "1.00.0065",
"fixed": {"operating_systems": ["WINDOWS32"]},
"internal_name": "Callstb",
"original_filename": "NOFAstb.exe",
"product_name": "Goodreads",
"product_version": "1.00.0065",
"var": {"character_set": "Unicode", "language": "U.S. English"}
}
},
"yara": {
"elapsed": 0.068918,
"matches": [
"SEH__vba",
"SEH_Init",
"Big_Numbers1",
"IsPE32",
"IsWindowsGUI",
"HasOverlay",
"HasRichSignature",
"Microsoft_Visual_Basic_v50v60",
"Microsoft_Visual_Basic_v50",
"Microsoft_Visual_Basic_v50_v60",
"Microsoft_Visual_Basic_v50_additional",
"Microsoft_Visual_Basic_v50v60_additional"
],
"tags": [
"AntiDebug",
"SEH",
"Tactic_DefensiveEvasion",
"Technique_AntiDebugging",
"SubTechnique_SEH",
"PECheck",
"PEiD"
]
}
}
}
```
#### Cosa fare dopo?
Se Strelka fosse distribuito e stesse acquisendo file nel tuo ambiente, potresti raccogliere questi eventi nel tuo SIEM. Con questa analisi, potresti scrivere una regola che cerchi eventi corrispondenti ai tag yara sospetti, avvisandoti di un file potenzialmente malevolo.
```
scan.yara.tags:("Technique_AntiDebugging" && "SubTechnique_SEH")
```
## Interfaccia Fileshot
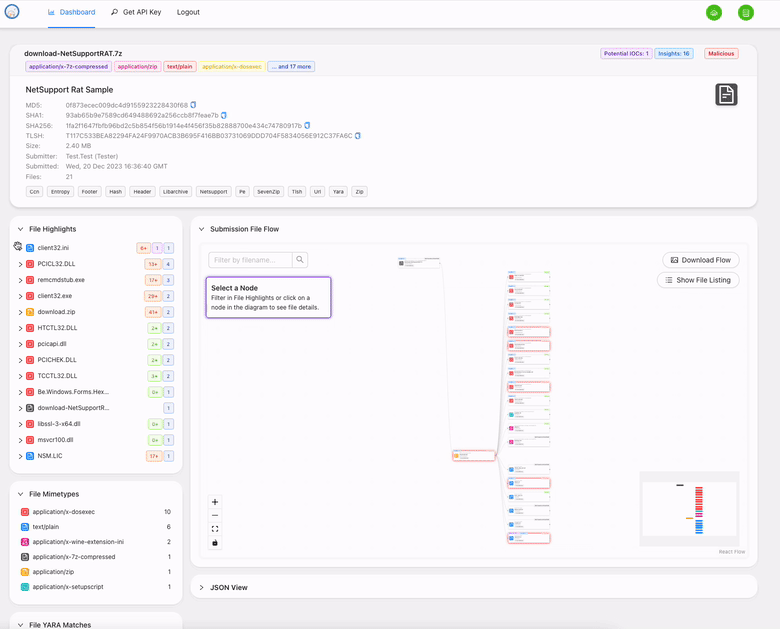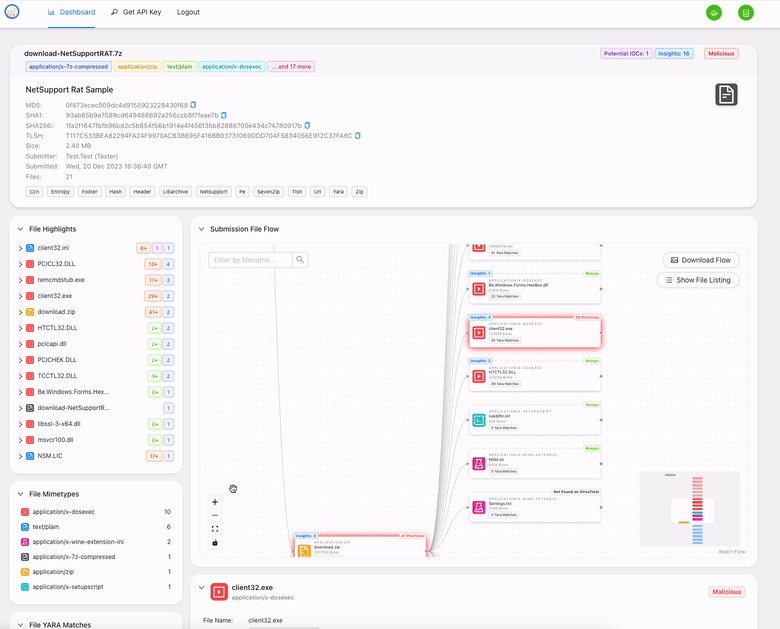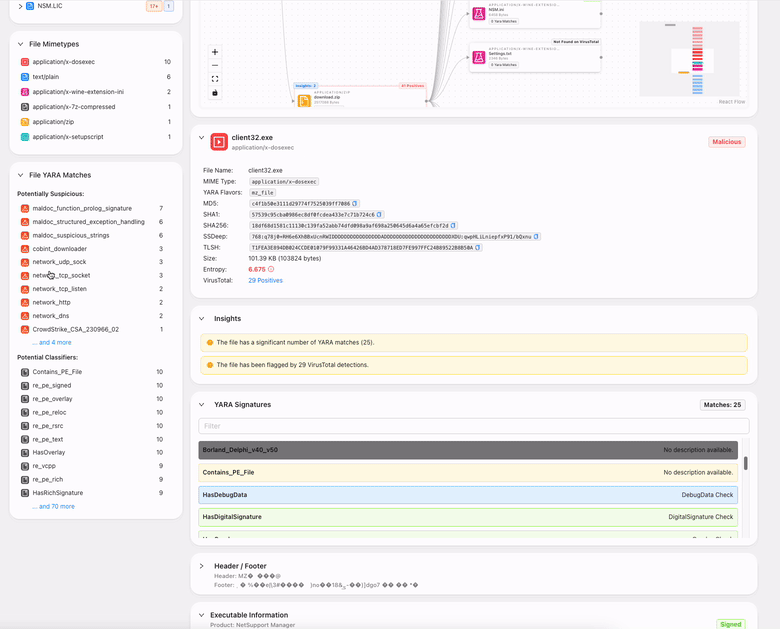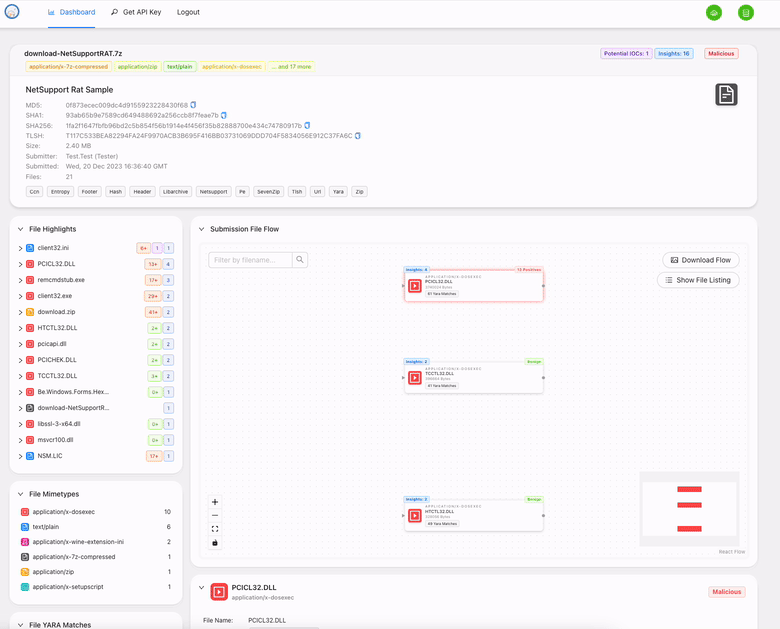
L'[interfaccia di Strelka](https://github.com/target/strelka-ui) è disponibile quando costruisci i container forniti. Questa interfaccia web ti consente di caricare file su Strelka e catturare gli eventi, che vengono memorizzati localmente.
Naviga su http://localhost:9980/ e usa le credenziali strelka/strelka.
## Usi potenziali
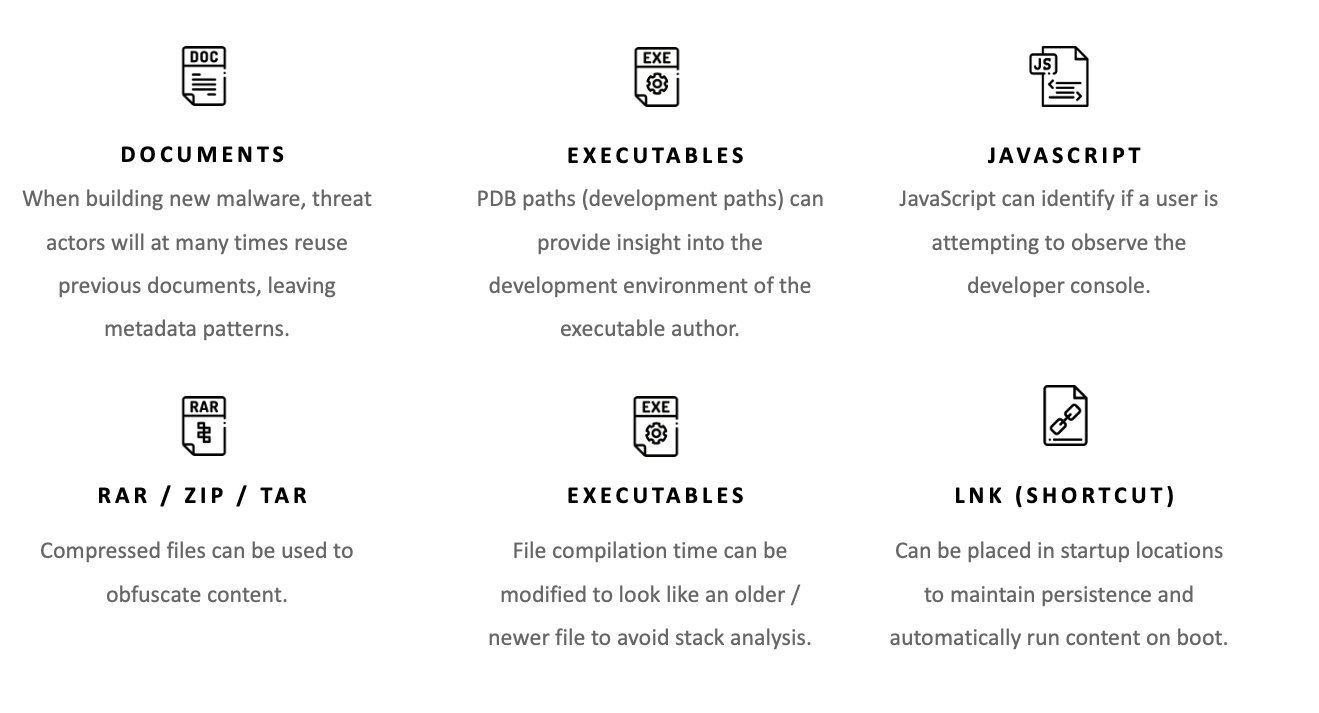
Con oltre 50 scanner di file per i tipi di file più comuni (es. exe, docx, js, zip), Strelka fornisce agli utenti la capacità di ottenere nuove informazioni sui file presenti sul proprio host, rete o azienda. Sebbene Strelka *non sia* un motore di rilevamento in sé (anche se utilizza [YARA](https://virustotal.github.io/yara/)), può fornire metadati sufficienti per identificare file sospetti o malevoli. Alcuni usi potenziali di Strelka includono:
## Documentazione aggiuntiva
Ulteriore documentazione su Strelka può essere trovata nel [README](https://target.github.io/strelka/), inclusi:
- [Installazione](https://target.github.io/strelka/#/?id=installation)
- [Distribuzione](https://target.github.io/strelka/#/?id=deployment)
- [Progettazione](https://target.github.io/strelka/#/?id=design)
- [Architettura](https://target.github.io/strelka/#/?id=architecture)
- [FAQ](https://target.github.io/strelka/#/?id=frequently-asked-questions)
## Contribuisci
Linee guida per contribuire si trovano [qui](https://github.com/target/strelka/blob/master/CONTRIBUTING.md).
## Problemi noti
### Problemi con il caricamento delle regole YARA
Si consiglia agli utenti di precompilare le proprie regole YARA per prestazioni ottimali e per evitare potenziali problemi durante l'esecuzione.
L'uso di file YARA precompilati aiuta a ridurre i tempi di caricamento e l'utilizzo delle risorse, specialmente in ambienti con un ampio
set di regole. Assicurati di utilizzare l'[opzione compilata nella configurazione di Strelka](https://github.com/target/strelka/blob/master/configs/python/backend/backend.yaml)
per puntare al file di regole precompilato.
### Altri problemi
Vedi i [problemi etichettati come `bug`](https://github.com/target/strelka/issues?q=is%3Aissue+is%3Aopen+label%3Abug) nel tracker per eventuali altri problemi.
## Progetti correlati
* [Laika BOSS](https://github.com/lmco/laikaboss)
* [File Scanning Framework](https://github.com/EmersonElectricCo/fsf)
* [Assemblyline](https://cybercentrecanada.github.io/assemblyline4_docs/)
## Licenza
Strelka e il suo codice associato sono rilasciati secondo i termini della [Licenza Apache 2.0](https://github.com/target/strelka/blob/master/LICENSE).
<div align="center">
<img src="https://assets.kitploit.com/production/public/readmes/2436/1bbf5d22a15b9058f400fdd15b49dc4bbca672a6e4ad5bd4773998390025305b.png" alt="Banner Target" />
</div>
<!--
Collegamenti
-->
[release]:https://github.com/target/strelka/releases/latest "Ultima versione Strelka ➶"
[issues]:https://github.com/target/strelka/issues "Problemi Strelka ➶"
[pull-requests]:https://github.com/target/strelka/pulls "Pull Request Strelka ➶"
[wiki]:https://target.github.io/strelka/#/ "Documentazione Strelka ➶"
[repo]:https://github.com/target/strelka "Repository Strelka ➶"
[slack]:https://join.slack.com/t/cfc-open-source/shared_invite/zt-e54crchh-a6x4iDy18D5lVwFKQoEeEQ "Slack (link esterno) ➶"
[actions-ci]:https://github.com/target/strelka/actions/workflows/build_strelka_nightly.yml "Github Actions ➶"
[pr]:https://github.com/target/strelka/pulls "Pull Request Strelka ➶"
[license]:https://raw.githubusercontent.com/target/strelka/master/LICENSE "File licenza Strelka ➶"
[docker]:https://www.docker.com/ "Docker (link esterno) ➶"
<!--
Badge
-->
[img-version-badge]:https://img.shields.io/github/release/target/strelka.svg?style=for-the-badge
[img-slack-badge]:https://img.shields.io/badge/slack-join-red.svg?style=for-the-badge&logo=slack
[img-actions-badge]:https://img.shields.io/github/actions/workflow/status/target/strelka/build_strelka_nightly.yml?branch=master&style=for-the-badge
[img-pr-badge]:https://img.shields.io/badge/PRs-welcome-orange.svg?style=for-the-badge&logo=data:image/svg+xml;base64,PD94bWwgdmVyc2lvbj0iMS4wIiBlbmNvZGluZz0iVVRGLTgiPz48c3ZnIGlkPSJzdmcyIiB3aWR0aD0iNjQ1IiBoZWlnaHQ9IjU4NSIgdmVyc2lvbj0iMS4wIiB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciPiA8ZyBpZD0ibGF5ZXIxIj4gIDxwYXRoIGlkPSJwYXRoMjQxNyIgZD0ibTI5Ny4zIDU1MC44N2MtMTMuNzc1LTE1LjQzNi00OC4xNzEtNDUuNTMtNzYuNDM1LTY2Ljg3NC04My43NDQtNjMuMjQyLTk1LjE0Mi03Mi4zOTQtMTI5LjE0LTEwMy43LTYyLjY4NS01Ny43Mi04OS4zMDYtMTE1LjcxLTg5LjIxNC0xOTQuMzQgMC4wNDQ1MTItMzguMzg0IDIuNjYwOC01My4xNzIgMTMuNDEtNzUuNzk3IDE4LjIzNy0zOC4zODYgNDUuMS02Ni45MDkgNzkuNDQ1LTg0LjM1NSAyNC4zMjUtMTIuMzU2IDM2LjMyMy0xNy44NDUgNzYuOTQ0LTE4LjA3IDQyLjQ5My0wLjIzNDgzIDUxLjQzOSA0LjcxOTcgNzYuNDM1IDE4LjQ1MiAzMC40MjUgMTYuNzE0IDYxLjc0IDUyLjQzNiA2OC4yMTMgNzcuODExbDMuOTk4MSAxNS42NzIgOS44NTk2LTIxLjU4NWM1NS43MTYtMTIxLjk3IDIzMy42LTEyMC4xNSAyOTUuNSAzLjAzMTYgMTkuNjM4IDM5LjA3NiAyMS43OTQgMTIyLjUxIDQuMzgwMSAxNjkuNTEtMjIuNzE1IDYxLjMwOS02NS4zOCAxMDguMDUtMTY0LjAxIDE3OS42OC02NC42ODEgNDYuOTc0LTEzNy44OCAxMTguMDUtMTQyLjk4IDEyOC4wMy01LjkxNTUgMTEuNTg4LTAuMjgyMTYgMS44MTU5LTI2LjQwOC0yNy40NjF6IiBmaWxsPSIjZGQ1MDRmIi8+IDwvZz48L3N2Zz4=
[img-license-badge]:https://img.shields.io/badge/license-apache-ff69b4.svg?style=for-the-badge&logo=apache
[img-docker-badge]:https://img.shields.io/badge/Supports-Docker-yellow.svg?style=for-the-badge&logo=docker