
 stanfrbd/cyberbro
Un'applicazione semplice che estrae i tuoi IoC da input spazzatura e ne verifica la reputazione utilizzando molteplici servizi CTI.
<h1 align="center">Cyberbro</h1>
<p align="center">
<img src="https://assets.kitploit.com/production/public/readmes/10725/4970c639439a60187e1ba39523b24c3343a5b6946445d8225e23c4060e002ff0.png" width="90" /><br />
<b><i>Una semplice applicazione che estrae i tuoi IoC da input disordinati e ne verifica la reputazione utilizzando molteplici servizi.</i></b>
<br />
<b>🌐 <a href="https://demo.cyberbro.net/">demo.cyberbro.net</a></b><br />
</p>
---
<p align="center">
<a href="https://github.com/stanfrbd/cyberbro/stargazers">
<img src="https://img.shields.io/github/stars/stanfrbd/cyberbro?style=social" alt="GitHub stars">
</a>
<a href="https://x.com/cyberbro_cti">
<img src="https://img.shields.io/twitter/follow/cyberbro_cti?style=social" alt="Follow on X/Twitter">
</a>
<a href="https://infosec.exchange/@cyberbro">
<img src="https://img.shields.io/badge/Follow_@cyberbro-23-blue?logo=mastodon" alt="Mastodon">
</a>
<a href="https://github.com/stanfrbd/cyberbro/issues">
<img src="https://img.shields.io/github/issues/stanfrbd/cyberbro" alt="GitHub issues">
</a>
<a href="https://github.com/stanfrbd/cyberbro/blob/main/LICENSE">
<img src="https://img.shields.io/github/license/stanfrbd/cyberbro" alt="License">
</a>
<a href="https://github.com/stanfrbd/cyberbro/actions/workflows/jobs.yml">
<img src="https://github.com/stanfrbd/cyberbro/actions/workflows/jobs.yml/badge.svg" alt="build and test badge">
</a>
<a href="https://github.com/stanfrbd/cyberbro/actions/workflows/pre-commit-validation.yml">
<img src="https://github.com/stanfrbd/cyberbro/actions/workflows/pre-commit-validation.yml/badge.svg" alt="pre-commit validation badge">
</a>
<a href="https://www.python.org/">
<img src="https://img.shields.io/badge/Python-3.13-blue?logo=python" alt="Python">
</a>
</p>
---
# Informazioni
Ispirato a [Cybergordon](https://cybergordon.com/) e [IntelOwl](https://github.com/intelowlproject/IntelOwl).
Questo progetto mira a fornire un modo semplice ed efficiente per verificare la reputazione dei tuoi osservabili utilizzando molteplici servizi,
senza dover distribuire una soluzione **complessa**. Leggi la documentazione su https://docs.cyberbro.net/
> [!TIP]
> Per creare report personalizzati, usa Cyberbro con il tuo **LLM** preferito (Claude, OpenAI gpt-5...) tramite **MCP** (Model Context Protocol) \
> Consulta [Cyberbro MCP](https://github.com/stanfrbd/mcp-cyberbro) per maggiori informazioni.
# Demo
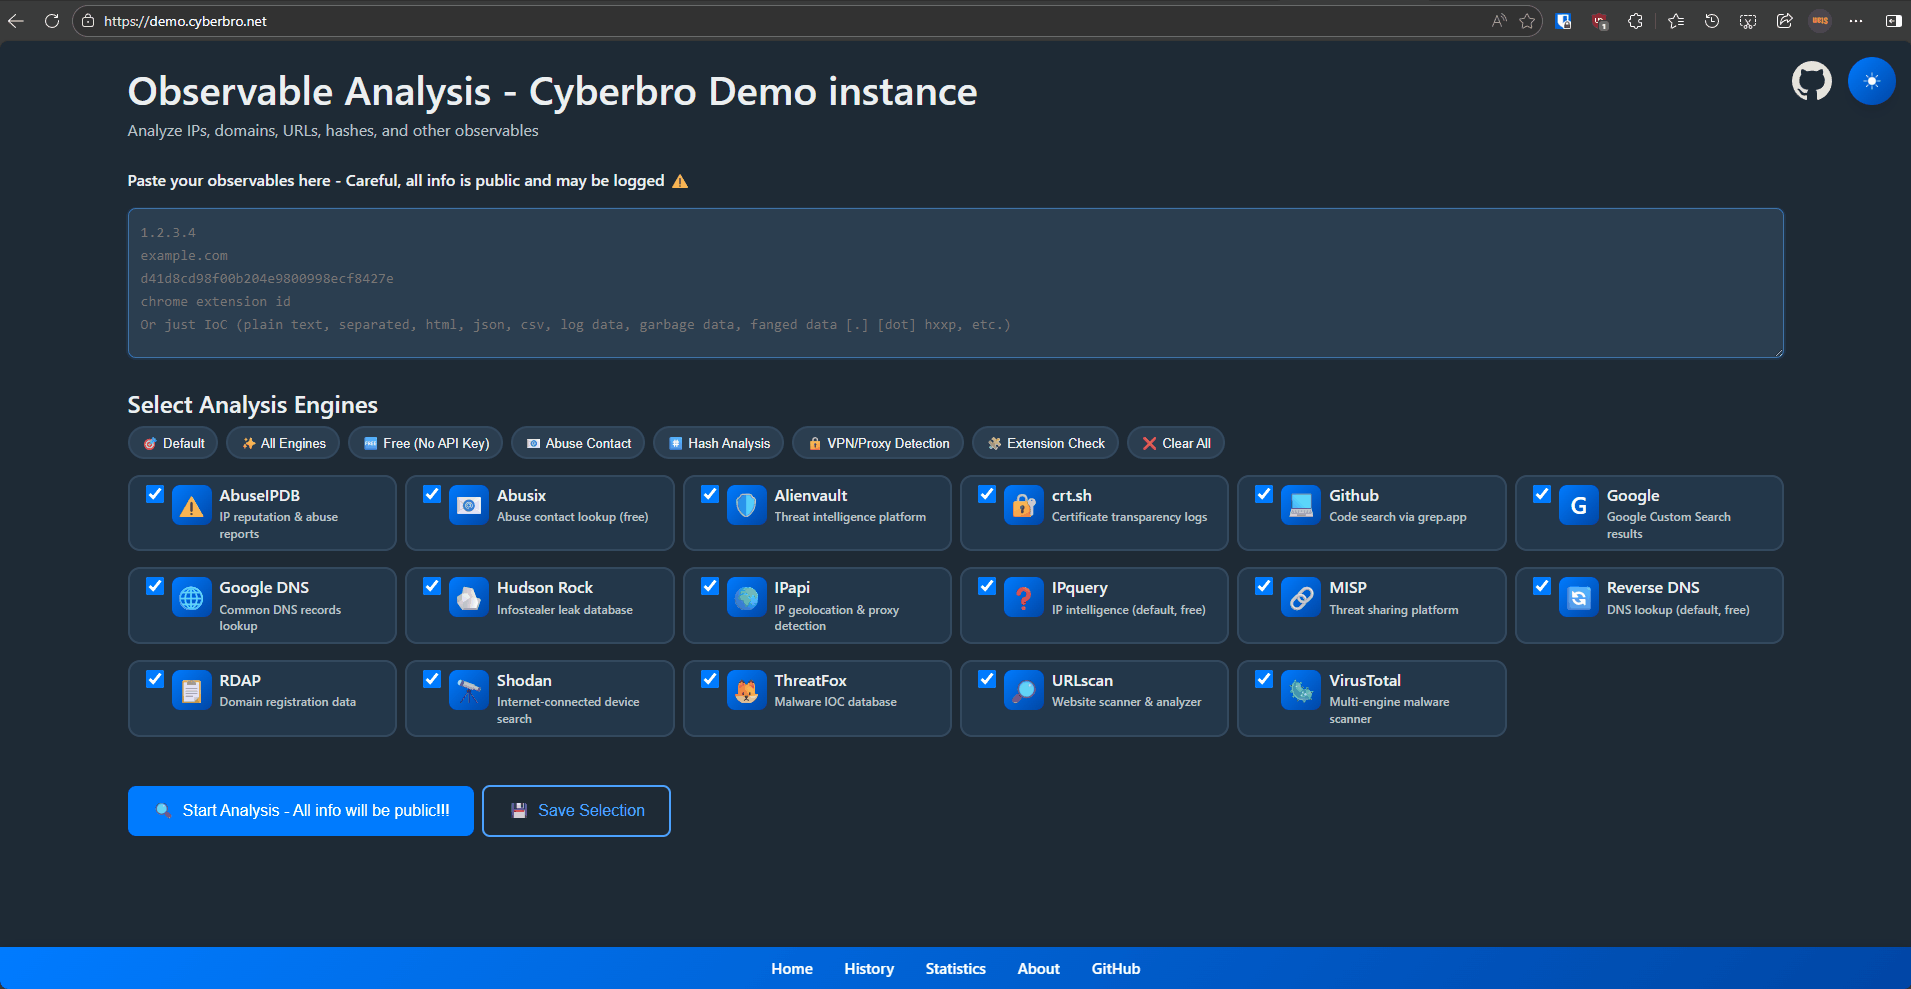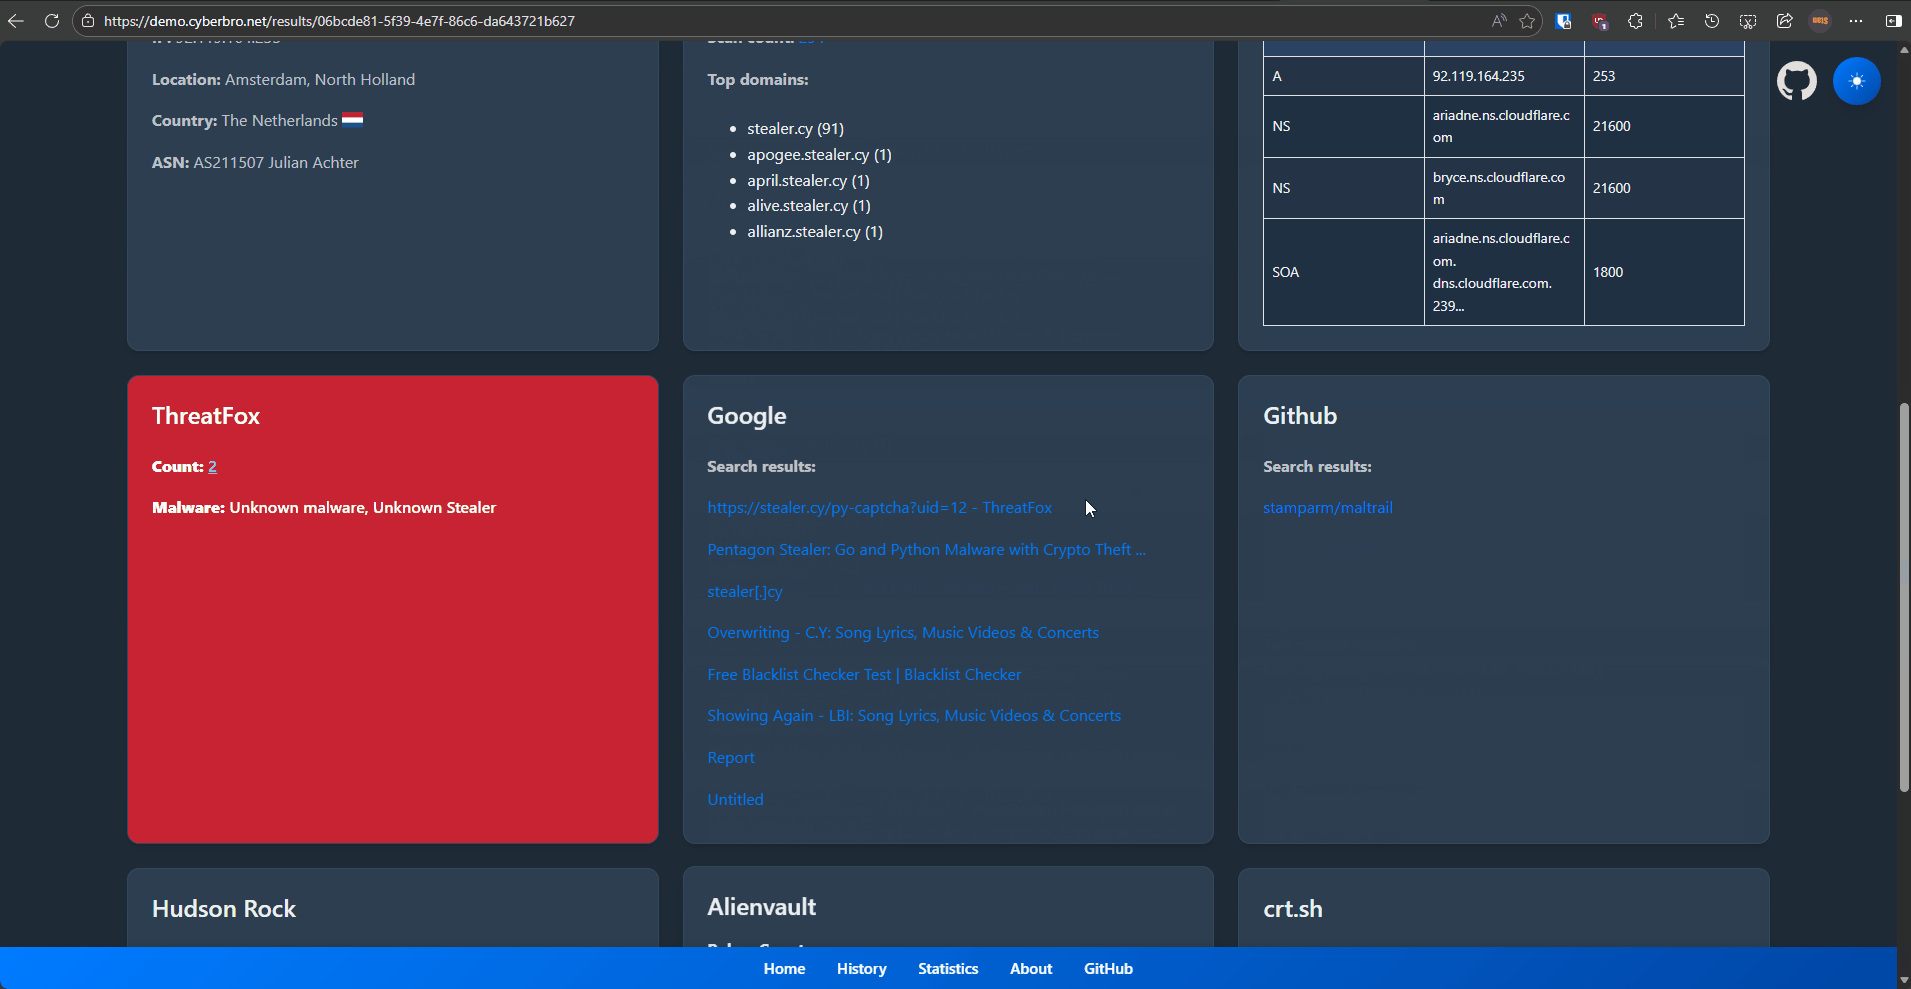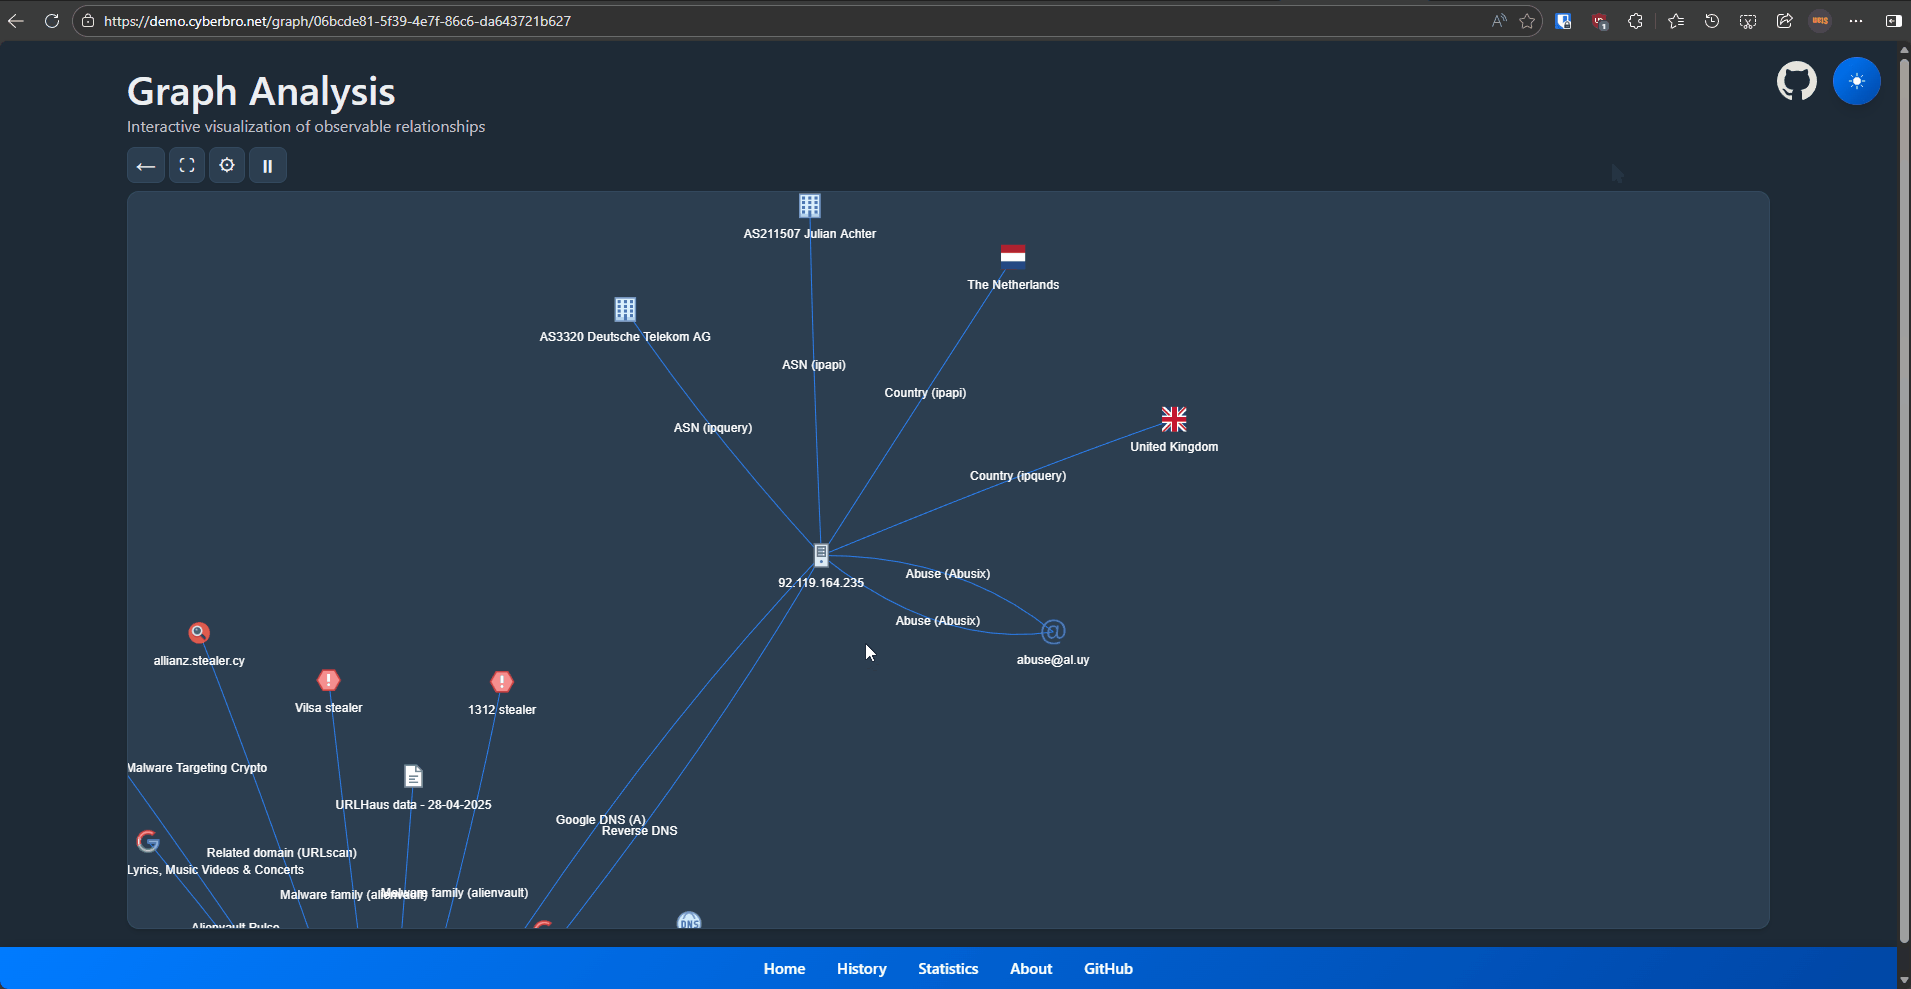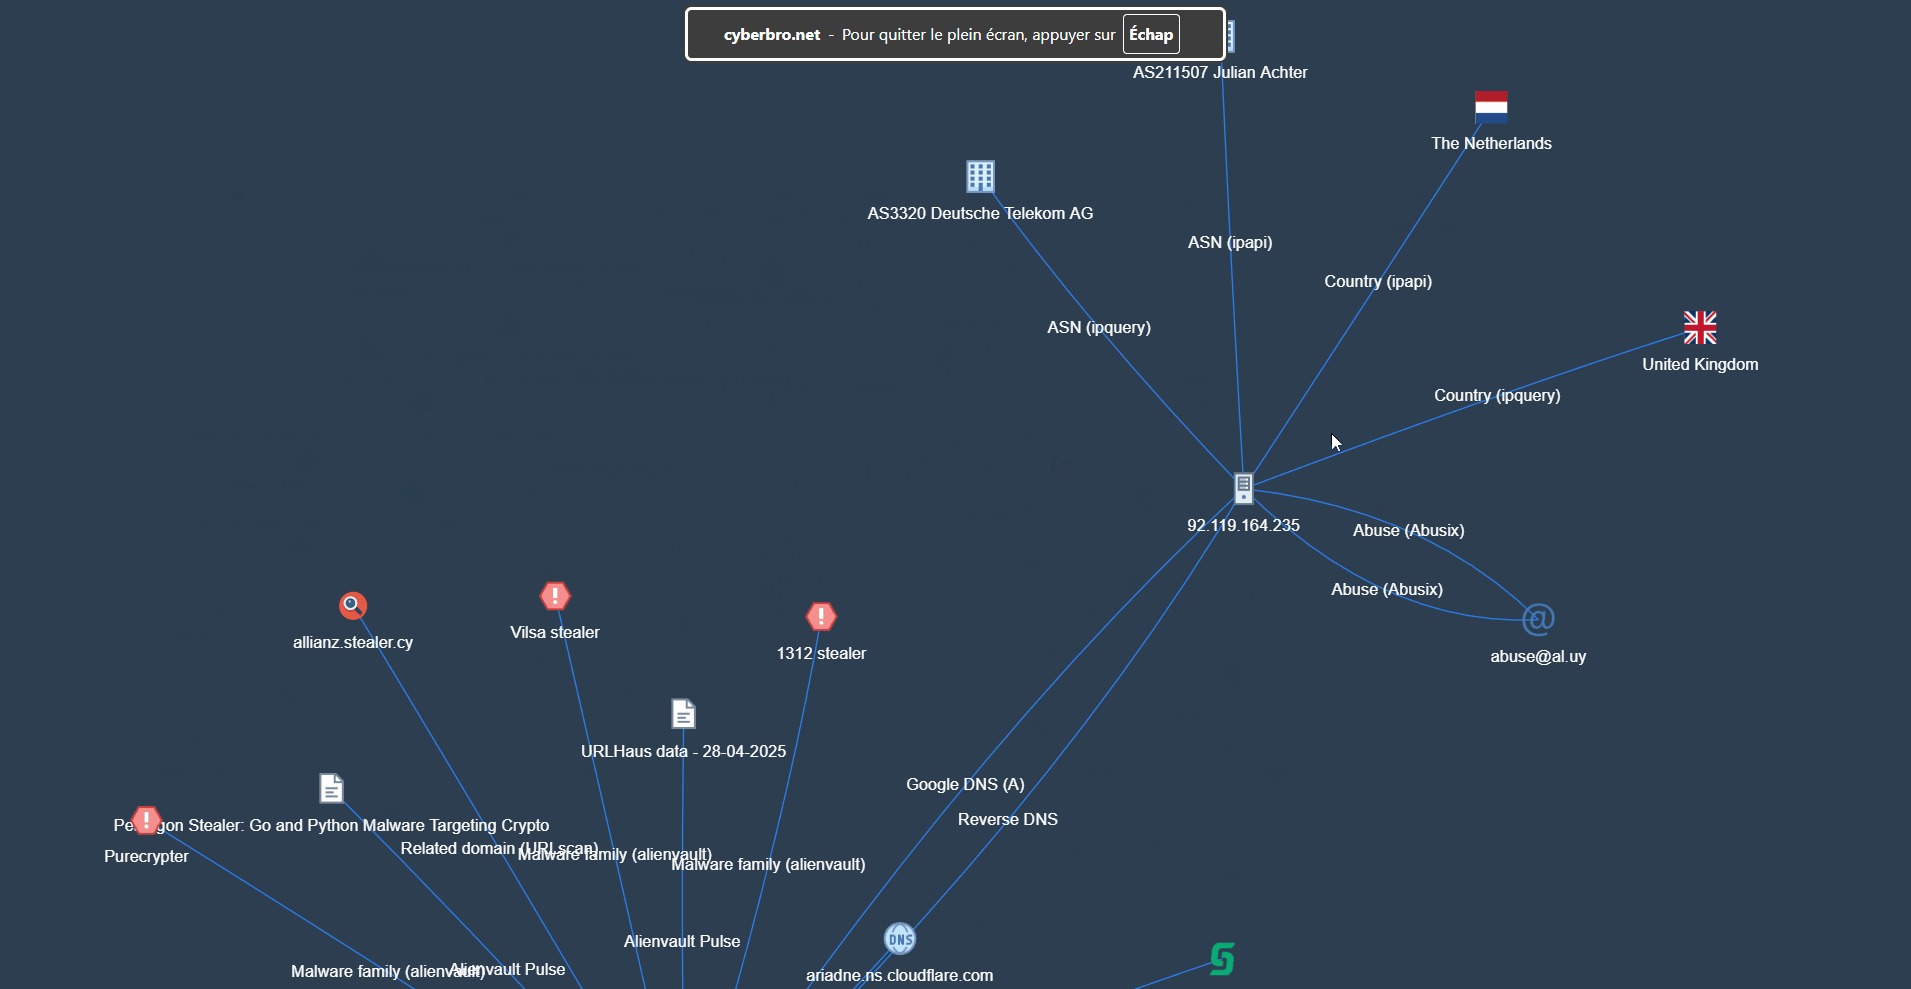
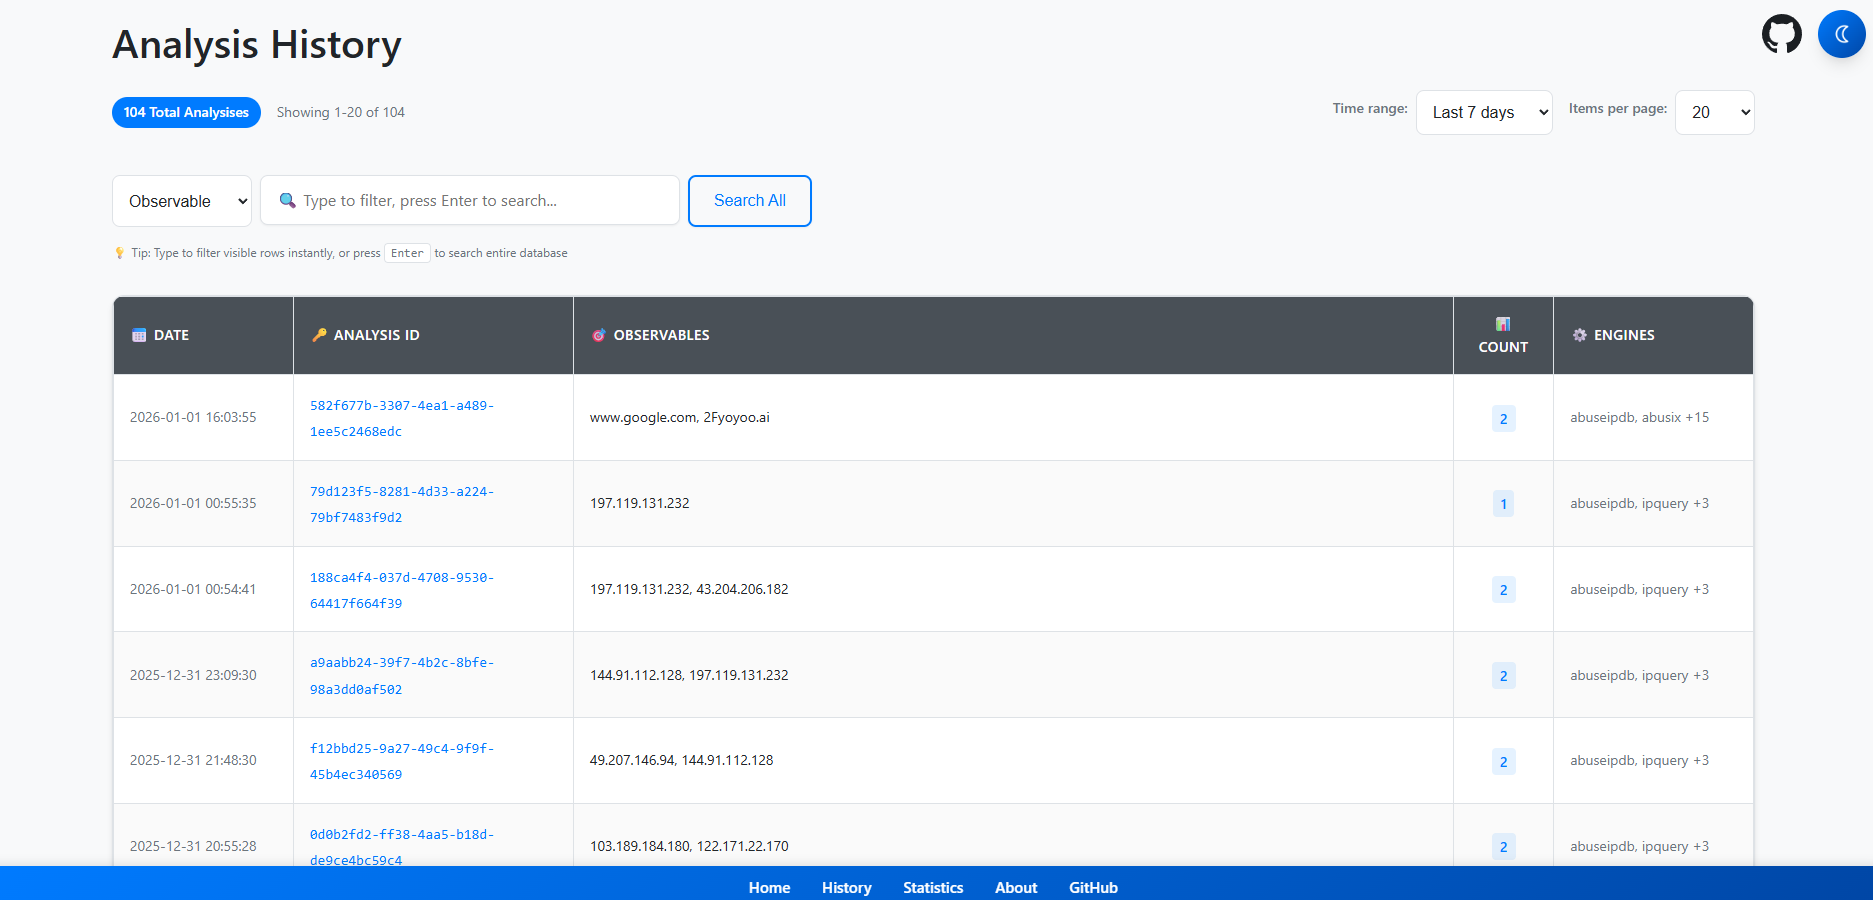
# Funzionalità
* **Input Semplice**: Incolla log grezzi o IoC - parsing ed estrazione automatici.
* **Verifiche Multi-Servizio**: Ricerca della reputazione per IP, hash, domini, URL e ID di estensioni Chrome su numerosi servizi di threat intelligence.
* **Report Completi**: Ricerca avanzata, filtraggio ed esportazione in CSV/Excel.
* **Elaborazione Veloce**: Multithread per la velocità.
* **Pivoting Automatizzato**: Scopri domini, URL e IP correlati tramite reverse DNS e RDAP / Whois.
* **Informazioni Accurate su Domini e Abuse**: Ricerche RDAP / Whois e contatti di abuse.
* **Integrazioni**: Microsoft Defender for Endpoint, CrowdStrike, OpenCTI, Grep.App, Hudson Rock e altro ancora.
* **Proxy e Archiviazione**: Supporto proxy e risultati memorizzati in SQLite.
* **Cronologia e Grafici**: Cronologia delle analisi e vista grafica sperimentale.
* **Cache**: Caching per ricerche ripetute più veloci (abilitato a livello multi-engine, non per ogni singolo engine).
# Cosa Rende Cyberbro Unico
* **Adatto ai Principianti**: Accessibile a tutti i livelli di competenza.
* **Ricerca ID Estensioni Chrome**: Ottieni nomi delle estensioni e dati CTI dagli ID.
* **Distribuzione Leggera**: Configurazione e utilizzo semplici.
* **Estrazione Avanzata dei TLD**: Rilevamento accurato del dominio root per ricerche migliori.
* **Raccolta Dati Pragmatica**: Utilizza GitHub e Google per trovare IoC trascurati.
* **Integrazione Report CTI**: Recupera report correlati agli IoC da IoC.One.
* **Integrazione EDR**: Verifica gli osservabili rispetto ai tuoi strumenti di sicurezza (MDE, CrowdStrike).
# Per Iniziare - TL;DR
> [!TIP]
> Se sei pigro, ti serve Docker. \
> Fai un `git clone` ; copia `.env.sample` in `.env` ; `docker compose up` poi vai su `localhost:5000`. Sì, tutto qui!
# Per Iniziare
* Per iniziare, clona il repository
```bash
git clone https://github.com/stanfrbd/cyberbro
cd cyberbro
```
## Modifica il file di configurazione (obbligatorio)
```
cp .env.sample .env
```
> [!NOTE]
> Non hai le API key? Nessun problema, copia semplicemente `.env.sample` in `.env` e lascia vuoti i valori opzionali. Fai attenzione se viene utilizzato un proxy. \
> Potrai utilizzare **tutti gli engine gratuiti!**
* Compila i valori (incluso il proxy se necessario) nel file `.env`.
> [!WARNING]
> `.env` contiene segreti sensibili e non deve mai essere committato.
> Per distribuzioni in produzione/team, usa SOPS, Vault o un workflow equivalente di gestione dei segreti.
```bash
ABUSEIPDB=token_here
ALIENVAULT=token_here
CRIMINALIP_API_KEY=token_here
CROWDSTRIKE_CLIENT_ID=client_id_here
CROWDSTRIKE_CLIENT_SECRET=client_secret_here
DFIR_IRIS_API_KEY=token_here
DFIR_IRIS_URL=https://dfir-iris.local
DFIR_IRIS_SEARCH_NOTES=false
GOOGLE_CSE_CX=cx_here
GOOGLE_CSE_KEY=key_here
GOOGLE_CSE_URL=https://www.googleapis.com/customsearch/v1
GOOGLE_SAFE_BROWSING=token_here
HISTER_TOKEN=token_here
HISTER_BASE_URL=https://hister.example.com
IPAPI=token_here
IPINFO=token_here
MDE_CLIENT_ID=client_id_here
MDE_CLIENT_SECRET=client_secret_here
MDE_TENANT_ID=tenant_here
MISP_API_KEY=token_here
MISP_URL=https://misp.local
MISP_FEEDBACK_SERVER_URL=https://misp-feedback.local
MISP_FEEDBACK_TOKEN=token_here
OPENCTI_API_KEY=token_here
OPENCTI_URL=https://demo.opencti.io
PROXY_URL=
RANSOMWARE_LIVE_API_KEY=token_here
RL_ANALYZE_API_KEY=token_here
RL_ANALYZE_URL=https://spectra_analyse_url_here
ROSTI_API_KEY=token_here
SHODAN=token_here
SPUR_US=token_here
THREATFOX=token_here
VIRUSTOTAL=token_here
WEBSCOUT=token_here
```
> [!IMPORTANT]
> A partire dalla versione `v0.13.0`, Cyberbro non supporta più `secrets.json` e la pagina `/config`. Cfr. [discussion 165](https://github.com/stanfrbd/cyberbro/discussions/165).\
> Se hai già un `secrets.json` legacy, convertilo in `.env` con:
> `python3 scripts/secrets_json_to_env.py`
Consulta [Opzioni avanzate per la distribuzione](https://docs.cyberbro.net/quick-start/Advanced-options-for-deployment) nella documentazione.
# Avvia l'app
## Pigro e facile - usa docker
> [!WARNING]
> Assicurati di installare il plugin `compose` come `docker compose` e non `docker-compose`.
> In Docker, l'app si associa a `0.0.0.0` all'interno del container anche se il tuo `.env` locale imposta `FLASK_HOST=127.0.0.1`.
```bash
docker compose up # use -d to run in background and use --build to rebuild the image
```
* Vai su http://127.0.0.1:5000 e divertiti.
> Non dimenticare di modificare `.env` prima di costruire l'immagine.
Consulta [Opzioni avanzate per la distribuzione](https://docs.cyberbro.net/quick-start/Advanced-options-for-deployment) nella documentazione per ottenere tutte le opzioni di distribuzione Docker.
## Il vecchio modo
* Clona il repository e installa i requisiti.
Potresti voler creare un [`venv`](https://docs.python.org/3/library/venv.html) prima di installare le dipendenze.
```bash
pip install -r requirements.txt
```
* Avvia l'app con `gunicorn` (modalità clean).
```bash
gunicorn -c prod/gunicorn.conf.py app:app
```
* Avvia l'app in modalità sviluppo.
```bash
python3 app.py
```
# Screenshot
<details>
<summary>Vedi tutti gli screenshot</summary>
<img width="1897" height="909" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/b3a07f1e163ae260b2a5f908a70d571a145f702ad50b524725ce4b3562f7c367.png" />
<img width="1883" height="907" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/3d3404a7e55b688b497db428ecb7fa01b6a23ec8879e2c2c751c68a92545a334.png" />
<img width="1887" height="906" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/cd57a214ae604ed83ca50d119b49391afc0a66c03b3ed93feecfbb59578f5984.png" />
</details>
<img width="1788" height="1536" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/2e6051fe1ad7fadde5ff9074dbb4d96528dd2c8ab8262ea10e1fe49fee031153.png" />
<img width="1873" height="900" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/5201b888fdaa97465f141379e9f5caedb0bdd847b1e31a08b3e236df8b663ed6.png" />
> [!CAUTION]
> Se intendi utilizzarlo in un **ambiente di produzione**, usa un **Reverse Proxy** + **WAF** ben configurati per prevenire **problemi di sicurezza**.
# Estensione browser Cyberbro
<p>
<a href="https://addons.mozilla.org/addon/cyberbro-analyzer/"><img src="https://assets.kitploit.com/production/public/readmes/10725/7e7e7002c8f357304f16d1d06ff840c40e92c66f6ed072b18da36329502c7a13.png" alt="Get Cyberbro Analyzer for Firefox"></a>
<a href="https://chromewebstore.google.com/detail/cyberbro-analyzer/nfcfigpaollodajabegcdobhmgaclbbm"><img src="https://assets.kitploit.com/production/public/readmes/10725/28dd6378e71c68b4f21b54ad99bb1225f978b8f2bacfa3c46444f988c09ace1c.png" alt="Get Cyberbro Analyzer for Chromium"></a>
<a href="https://microsoftedge.microsoft.com/addons/detail/cyberbro-analyzer/lbponbmcggcepflackehgpbceehagiam"><img src="https://assets.kitploit.com/production/public/readmes/10725/0a301e6c3048478ead36dfbccdba2e5263de7fbeb3de9d22a9f159f64f378273.png" alt="Get Cyberbro Analyzer for Microsoft Edge"></a>
</p>
# API di Cyberbro
* L'API è disponibile su `/api/` ed è accessibile tramite la GUI o la riga di comando.
**Attualmente ci sono 3 endpoint:**
* `/api/analyze` - Analizza un testo e restituisce l'ID dell'analisi (JSON).
* `/api/is_analysis_complete/<analysis_id>` - Verifica se l'analisi è completa (JSON).
* `/api/results/<analysis_id>` - Recupera i risultati di un'analisi precedente (JSON).
```bash
curl -X POST "http://localhost:5000/api/analyze" -H "Content-Type: application/json" -d '{"text": "cyberbro.net", "engines": ["reverse_dns", "rdap_whois"]}'
```
```json
{
"analysis_id": "e88de647-b153-4904-91e5-8f5c79174854",
"link": "/results/e88de647-b153-4904-91e5-8f5c79174854"
}
```
```bash
curl "http://localhost:5000/api/is_analysis_complete/e88de647-b153-4904-91e5-8f5c79174854"
```
```json
{
"complete": true
}
```
```bash
curl "http://localhost:5000/api/results/e88de647-b153-4904-91e5-8f5c79174854"
```
```json
[
{
"observable": "cyberbro.net",
"rdap_whois": {
"abuse_contact": "[email protected]",
"creation_date": "2024-12-20",
"data_source": "rdap",
"emails": [
"[email protected]"
],
"expiration_date": "2026-12-20",
"link": "https://rdap.verisign.com/net/v1/domain/CYBERBRO.NET",
"name_servers": [
"anderson.ns.cloudflare.com",
"lisa.ns.cloudflare.com"
],
"organization": null,
"registrant": null,
"registrant_country": null,
"registrant_email": null,
"registrar": "Cloudflare, Inc.",
"update_date": "2025-11-20"
},
"reverse_dns": {
"reverse_dns": [
"172.67.197.226",
"104.21.42.7"
]
},
"reversed_success": true,
"type": "FQDN"
}
]
```
> [!NOTE]
> La [pagina dedicata della documentazione](https://docs.cyberbro.net/quick-start/API-usage-and-engine-names) fornisce tutti i nomi degli engine utilizzabili.
# API e servizi di terze parti
* [AbuseIPDB](https://docs.abuseipdb.com/)
* [Abusix](https://abusix.com/)
* [Alienvault](https://otx.alienvault.com/)
* [CriminalIP](https://www.criminalip.io/)
* [CrowdStrike](https://www.crowdstrike.com/)
* [crt.sh](https://crt.sh/)
* [DFIR Iris](https://www.dfir-iris.org/)
* [Github](https://github.com/)
* [Google Safe Browsing](https://developers.google.com/safe-browsing)
* [Google](https://google.com/)
* [Google DNS](https://dns.google/)
* [Grep.App](https://grep.app/)
* [Hister](https://hister.org/)
* [Hudson Rock](https://hudsonrock.com/)
* [ICANN](https://lookup.icann.org/)
* [IPapi](https://ipapi.is/)
* [IPinfo](https://ipinfo.io/developers)
* [IPquery](https://ipquery.gitbook.io/ipquery-docs)
* [Ioc.One](https://ioc.one/)
* [Microsoft Defender for Endpoint](https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/microsoft-defender-for-endpoint-api)
* [Microsoft Entra ID (OpenID Configuration)](https://login.microsoftonline.com/)
* [MISP](https://www.misp-project.org/)
* [MISP Feedback](https://github.com/MISP/misp-feedback/)
* [OpenCTI](https://www.opencti.io/)
* [OpenRDAP](https://www.openrdap.org/)
* [Phishtank](https://www.phishtank.com/)
* [Ransomware.Live](https://ransomware.live/)
* [ReversingLabs Spectra Analyze](https://www.reversinglabs.com/products/spectra-analyze)
* [Rösti](https://rosti.bin.re/) - Repackaged Open Source Threat Intelligence
* [ScanMalware](https://scanmalware.com/)
* [Shodan](https://developer.shodan.io/)
* [Spur.us](https://spur.us/)
* [ThreatFox](https://threatfox.abuse.ch/api/)
* [URLscan](https://urlscan.io/)
* [VirusTotal](https://developers.virustotal.com/v3.0/reference)
* [WebScout](https://webscout.io/)
> [!NOTE]
> Hai domande? Consulta https://docs.cyberbro.net o apri una [issue](https://github.com/stanfrbd/cyberbro/issues/new) \
> Per la configurazione avanzata (tuning di `supervisord.conf` prima della distribuzione, selezione degli engine visibili, modifica del prefisso `/api/`...), consulta la [pagina dedicata della documentazione](https://docs.cyberbro.net/quick-start/Advanced-options-for-deployment).
# Ringraziamenti speciali
Un enorme ringraziamento a tutti gli straordinari contributori che hanno inviato pull request e contribuito a migliorare questo progetto:
* [Florian PILLOT](https://github.com/Harukunnn) che ha rielaborato gli engine (refactoring e ottimizzazioni).
* [Axel](https://github.com/botlabsDev) che sviluppa [Ioc.One](https://ioc.one/) e ha aggiunto uno User-Agent specifico che consente lo scraping di Ioc[.]One.
* [Jon Mark Allen](https://github.com/ubahmapk/) che ha aggiunto una migliore gestione dei segreti e test. Ha rifattorizzato molto e apportato numerosi miglioramenti al codebase, incluso CriminalIP.
* [cirosec GmbH - Felix Friedberger](https://github.com/cirosec) per aver aggiunto l'engine crt.sh.
* [Stig Dahl](https://github.com/sdaaish) per aver migliorato l'engine crt.sh, aggiunto la ricerca DFIR IRIS e risolto i problemi di Bandit, corretto l'engine MISP, aggiunto l'engine MISP Feedback.
* [0xffr](https://github.com/0xffr) per aver risolto la issue #98 - engine Grep.app non funzionante e aver commentato correttamente nell'engine CriminalIP.
* [Maxime Berthault - Maxou56800](https://github.com/Maxou56800) per aver sviluppato Cyberbro CLI.
* [Jonas Lejon](https://github.com/jonaslejon) per aver aggiunto l'engine ScanMalware.
* [egeoguz04](https://github.com/egeoguz04) per aver consentito la configurazione dell'endpoint Google CSE. Questo sarà utile per i prossimi cambiamenti di Google.
I vostri contributi sono molto apprezzati!
# Licenza
```
MIT License
Copyright (c) 2024-2026 stanfrbd
Permission is hereby granted, free of charge, to any person obtaining a copy
of this software and associated documentation files (the "Software"), to deal
in the Software without restriction, including without limitation the rights
to use, copy, modify, merge, publish, distribute, sublicense, and/or sell
copies of the Software, and to permit persons to whom the Software is
furnished to do so, subject to the following conditions:
The above copyright notice and this permission notice shall be included
in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS
OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY,
FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL
THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER
LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING
FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER
DEALINGS IN THE SOFTWARE.
```
# Logo
Il logo utilizzato in questo progetto è gratuito per uso personale e commerciale e può essere trovato [qui](https://www.veryicon.com/icons/object/material_design_icons/web-39.html).