Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
prismor — Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.) | Kitploit
Strumenti/GitHubGitHub/prismorsec/prismor
Defensive ToolsContainer SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityIncident ResponseAI Security
GitHubprismorsec/prismor

prismor

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)

283261069h 51m faRevisionato da Kitploit

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →
Vedi Repository
Sito web
Condividi
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

Prismor

PyPI License OpenSSF Best Practices PRs Welcome X DeepWiki Discord

Runtime security for Claude Code, Codex, Langchain and other AI agents frameworks/harness.

Prismor is highly customizable based on user's own policies. Observe or enforce mode to see agent activity in a local self-serve dashboard

Website • Onboard with Skill

Claude Code   Codex CLI   Gemini CLI   Cursor   GitHub Copilot   OpenCode   Pi Agent   Kiro   Kimi Code   Trae / Trae CN   Google Antigravity

Plus Grok Build, Crush, OpenHands, Qwen Code, Continue CLI, Goose, Hermes, OpenClaw, Devin CLI, Factory Droid, Aider, and more — see AGENT_INTEGRATIONS.md for the full coverage matrix
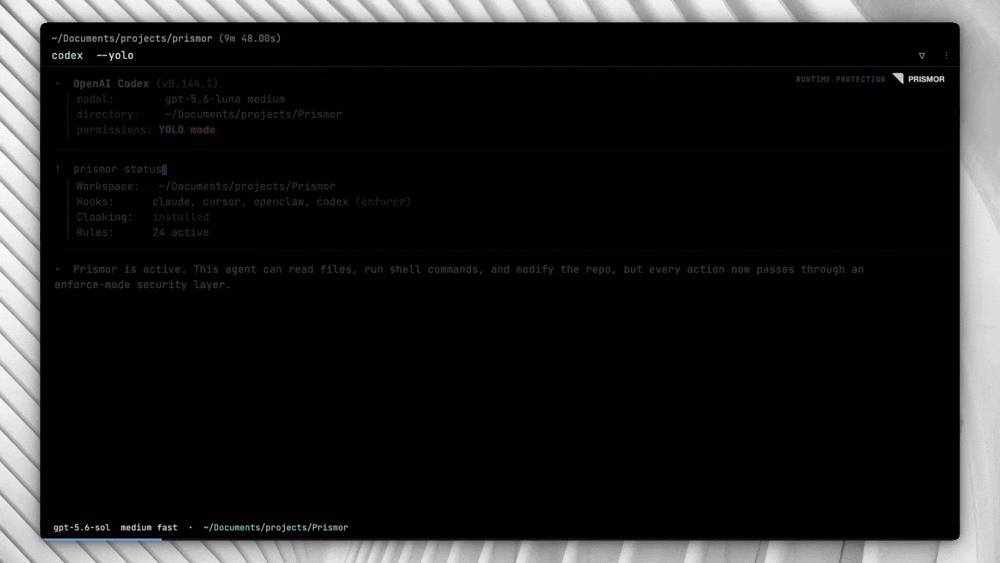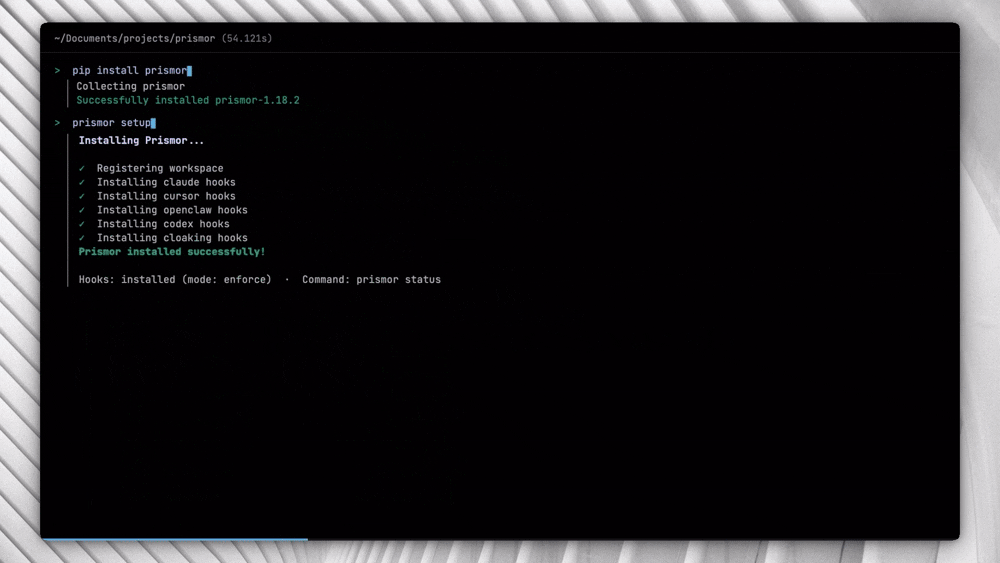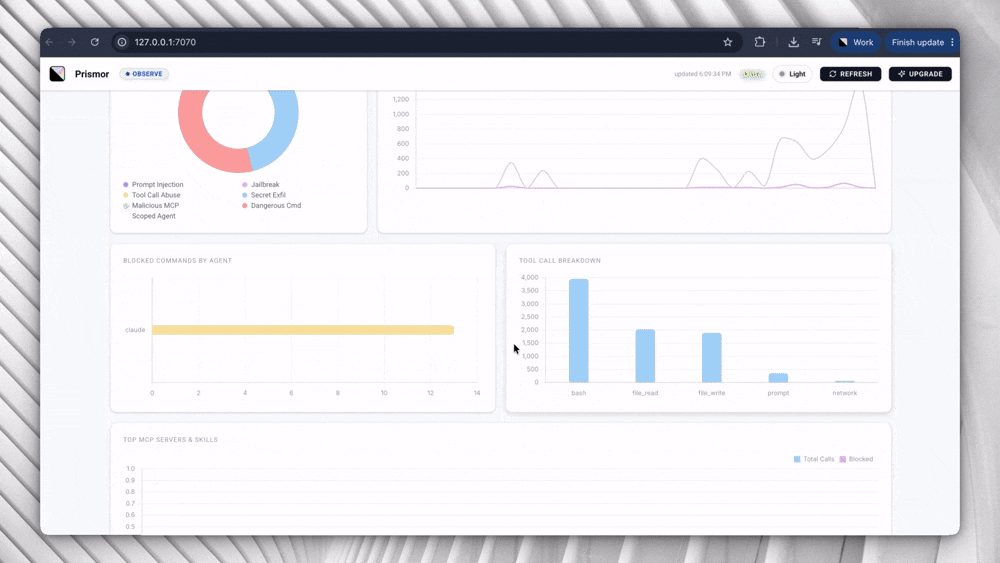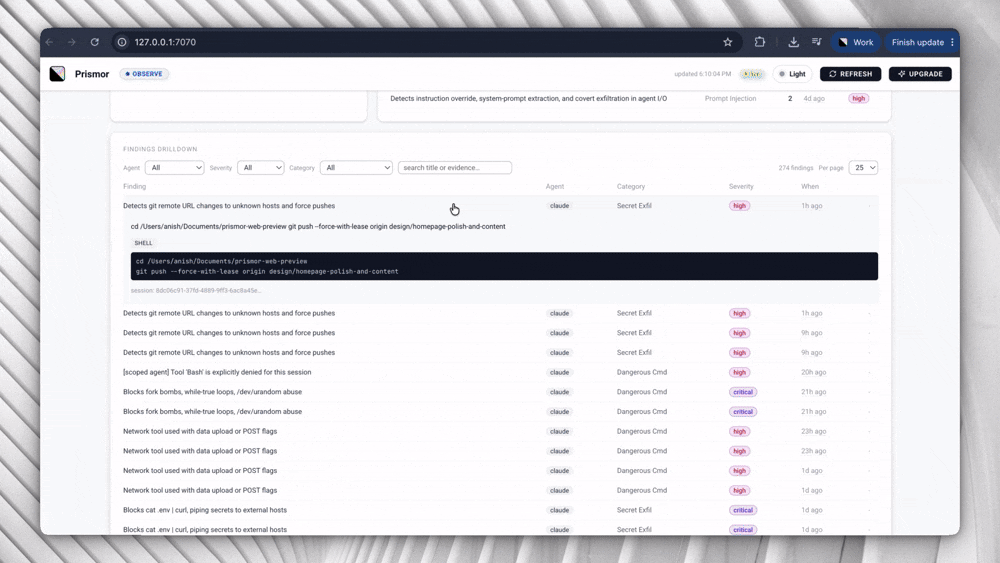

Prismor demo


The Problem

AI agents execute shell commands, read and write files, access credentials, and call external APIs. They do this autonomously, often across many steps, with limited checkpoints.

This creates risks that traditional security tooling isn't designed for:

  • Prompt injection - malicious content in a file, issue, or web page can redirect the agent mid-task
  • Unintended destructive actions - an agent misinterprets an instruction and runs something irreversible
  • Secret exfiltration - an agent reads .env or credential files as part of a debugging task and sends the content outbound
  • Lack of visibility and identity - an agent can spawn subagents and lack complete visibility for the end user
  • Privilege escalation - an agent modifies sudoers, CI pipelines, or file permissions to resolve a permission error
  • Dependency manipulation - an agent installs or rewrites a package at the direction of injected input
  • Supply chain risk - an agent installs a vulnerable or 0-day package while optimizing for code velocity

Standard OS-level and endpoint security tools monitor the kernel and filesystem. But they lack the context to make AI usable


Quick Start (30s)

pip install prismor
prismor setup

For the Skill, curl, and git-clone alternatives, plus PEP 668 systems and secret-cloaking setup, see the full installation guide.
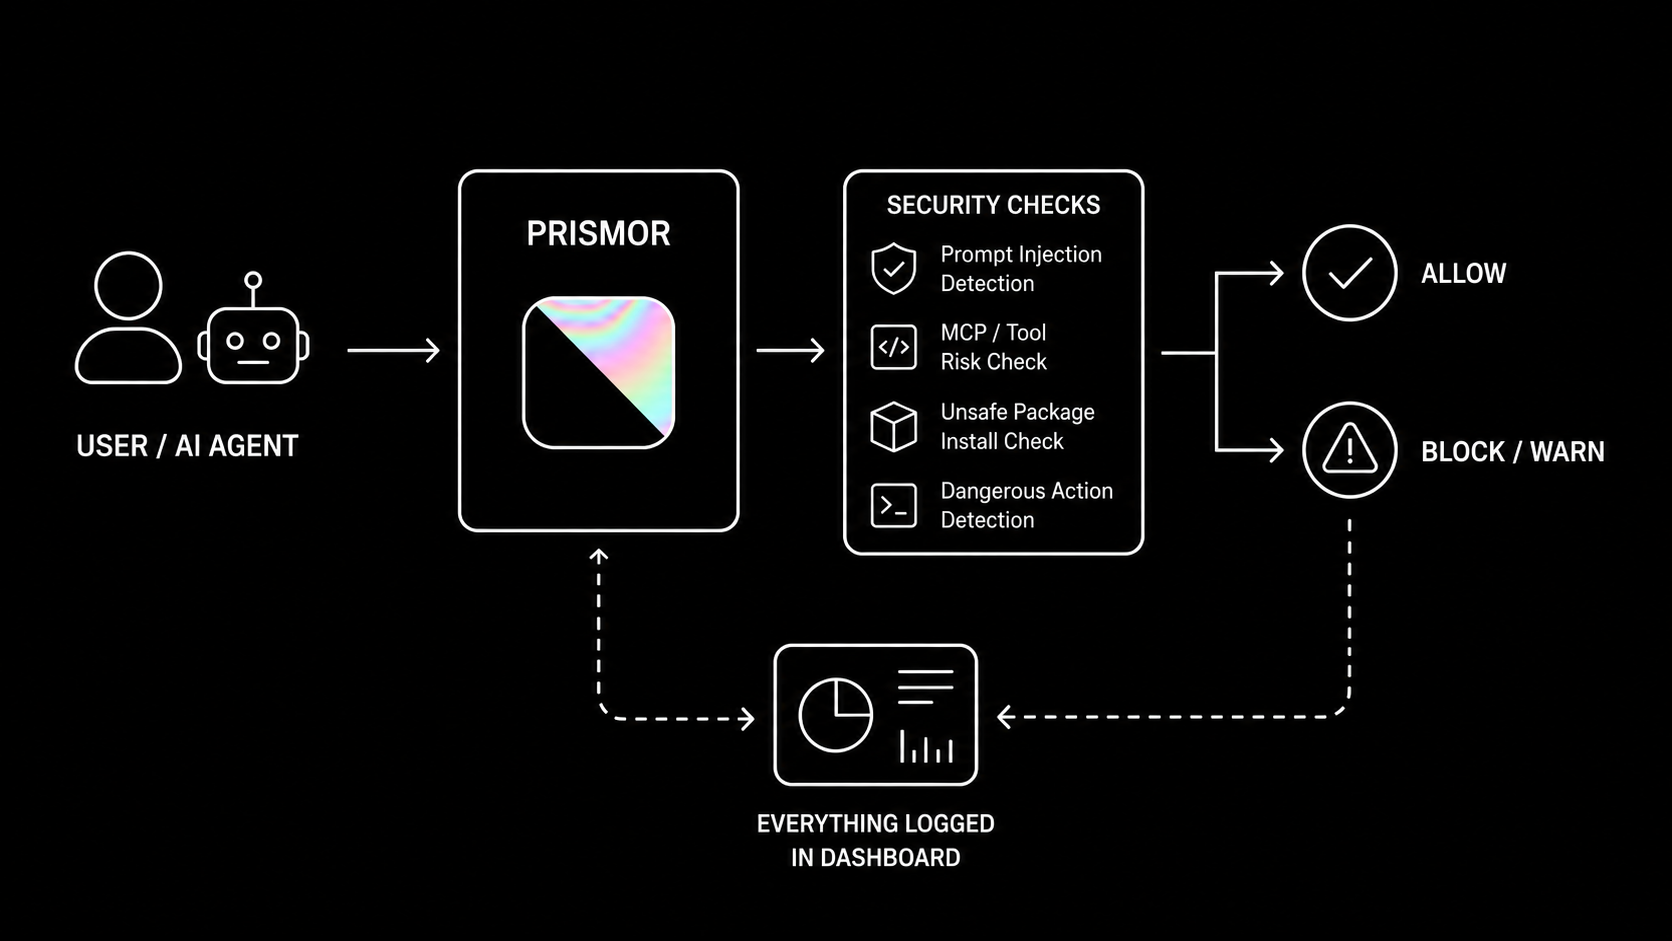

Capabilities

Prismor Architecture

Scarica lo strumento