Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
infisical — Infisical is the open-source platform for secrets, certificates, and privileged access management. | Kitploit
Strumenti/GitHubGitHub/infisical/infisical
Authentication & AuthorizationConfiguration AuditingCryptographyCloud SecurityDevSecOpsSecret DetectionIdentity & Access Management (IAM)
GitHubinfisical/infisical

infisical

Infisical is the open-source platform for secrets, certificates, and privileged access management.

Vedi Repository
28.5k2.2k451h 40m faRevisionato da Kitploit

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →
Condividi
Sito web
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

infisical

The open-source secret management platform: Sync secrets/configs across your team/infrastructure and prevent secret leaks.

Community | Infisical Cloud | Self-Hosting | Docs | Website | X | Hiring (Remote/SF)

Infisical is released under the MIT license. Latest Infisical release Cloudsmith downloads Infisical community forum

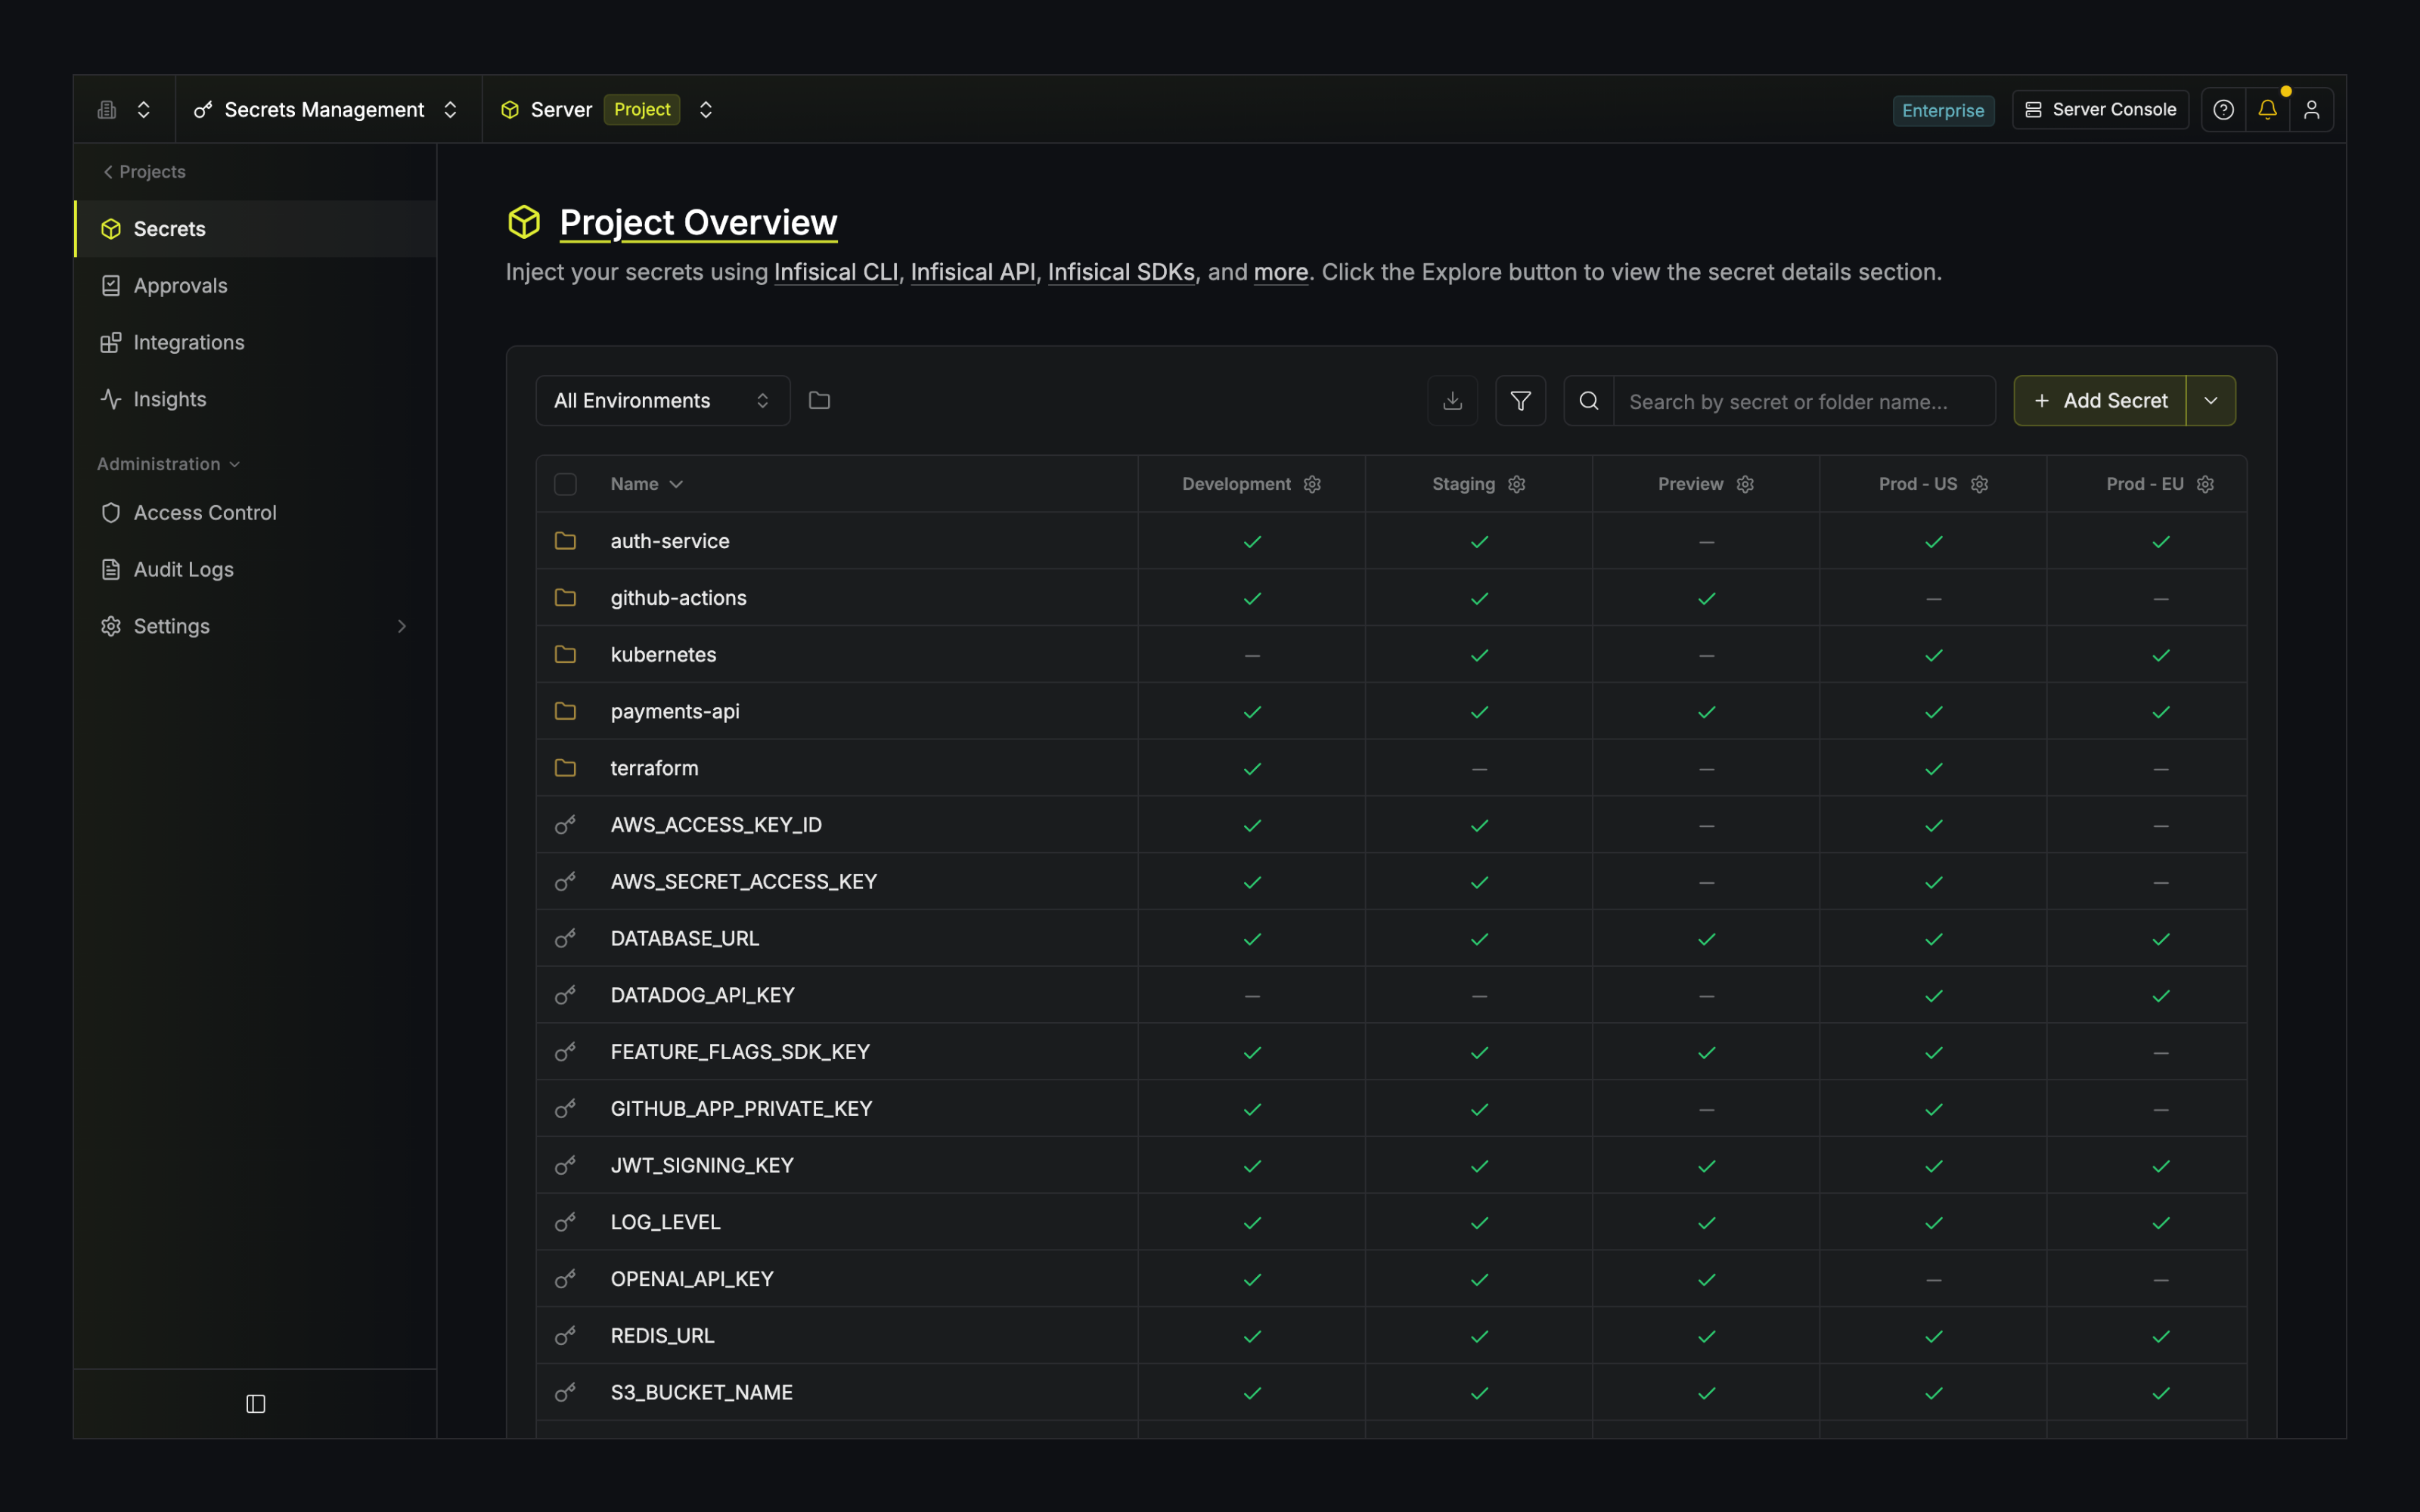
Infisical secrets management dashboard

Introduction

Infisical is the open source security infrastructure platform that teams use for secrets, certificates, and privileged access management.

We're on a mission to make security tooling more accessible to everyone, not just security teams, and that means redesigning the entire developer experience from ground up.

Features

Secrets Management:

Centralize your application secrets and configuration across every environment, with versioning, rotation, and leak prevention built in.

  • Dashboard: Manage secrets across projects and environments (e.g. development, production, etc.) through a user-friendly interface.
  • Secret Syncs: Sync secrets to platforms like GitHub, Vercel, AWS, and use tools like Terraform, Ansible, and more.
  • Secret versioning and Point-in-Time Recovery: Keep track of every secret and project state; roll back when needed.
  • Secret Rotation: Rotate secrets at regular intervals for services like PostgreSQL, MySQL, AWS IAM, and more.
  • Dynamic Secrets: Generate ephemeral secrets on-demand for services like PostgreSQL, MySQL, RabbitMQ, and more.
  • Secret Scanning and Leak Prevention: Prevent secrets from leaking to git.
  • Infisical Kubernetes Operator: Deliver secrets to your Kubernetes workloads and automatically reload deployments.
  • Infisical Agent: Inject secrets into applications without modifying any code logic.
  • Honey Tokens: Plant decoy credentials alongside your real secrets that act as tripwires, instantly alerting your team the moment an attacker tries to use them.
  • Agent Vault: Broker AI agent access to external APIs so agents never hold real credentials. Outbound requests route through a proxy that injects secrets before forwarding, eliminating credential exfiltration risk from prompt injection.

Certificate Management

Run a complete private PKI: issue, manage, and monitor X.509 certificates from a centralized platform.

  • Internal CA: Create and manage a private CA hierarchy directly within Infisical.
  • External CA: Integrate with third-party certificate authorities such as Let’s Encrypt, DigiCert, Microsoft AD CS, and more to leverage existing PKI infrastructure or issue publicly trusted certificates.
  • Certificate Lifecycle Management: Create certificate profiles and policies to control how certificates are issued, including enrollment methods such as API, ACME, or EST. Manage the full lifecycle from issuance to renewal and revocation with CRL and inventory tracking.
  • Certificate Syncs: Sync certificates to external platforms like AWS Certificate Manager and Azure Key Vault.
  • Alerting: Configure alerting for expiring CA and end-entity certificates.
  • Code Signing: Sign software artifacts like containers, installers, and packages with managed code-signing certificates, central approval, and a full audit trail.

Infisical Key Management System (KMS):

Centrally manage cryptographic keys and use them to encrypt and decrypt data across your projects.

  • Cryptographic Keys: Centrally manage keys across projects through a user-friendly interface or via the API.
  • Encrypt and Decrypt Data: Use symmetric keys to encrypt and decrypt data.

Privileged Access Management (PAM)

Scarica lo strumento