
 #1
Framework C2, redirector, listener e strumenti di infrastruttura di comando.
Raccomandato da Kitploit

 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 capesandbox/cape-parsers
CAPE: parser core e della community
 pennyw0rth/netexec
Framework post-sfruttamento per test automatizzati di autenticazione di rete, raccolta di credenziali e movimento laterale in ambienti Windows/AD con…
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 rapid7/metasploit-payloads
Repository unificato per diversi payload del Metasploit Framework
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
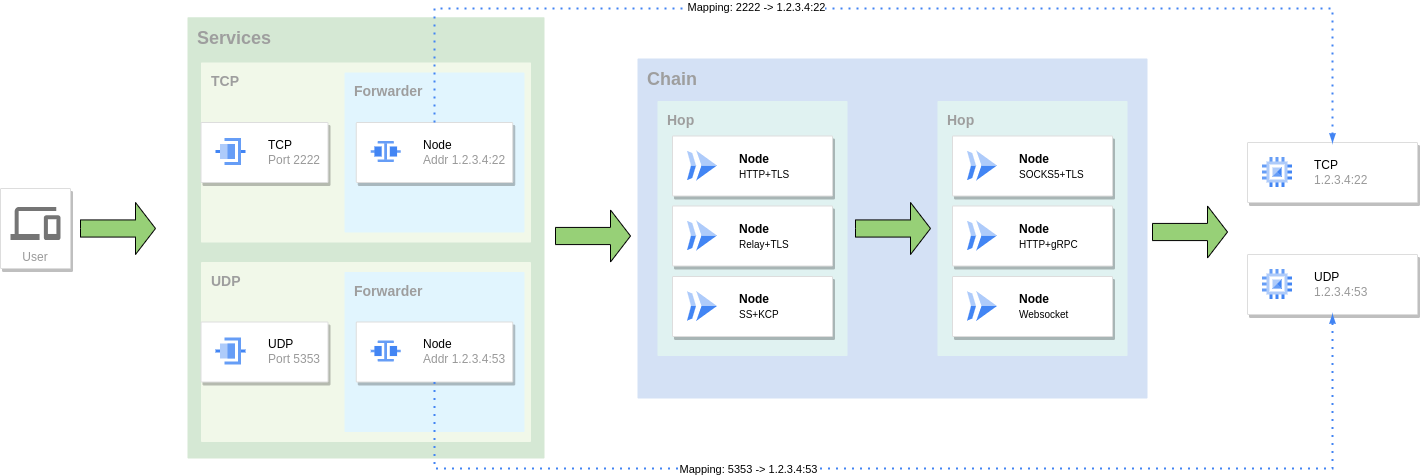 go-gost/gost
GO Simple Tunnel - un semplice tunnel scritto in golang
 sia-iotechnology/kittysploit-framework
Framework di sfruttamento in Python, Debugger del Motore V8, Intercettore Proxy, marketplace, post-sfruttamento, generatore di backdoor,....
 yaklang/yakit
Piattaforma di penetration testing all-in-one con proxy MITM, web fuzzer, gestore di connessioni inverse e sistema di plugin per test di sicurezza ed…
 rapid7/metasploit-framework
Framework di exploitation open-source con sistema modulare di payload, encoder e ausiliari per penetration testing, validazione delle vulnerabilità e…
 aipentest/cyberstrikeai
Il sistema d'azione per la cybersecurity nativa dell'IA—dove l'intento diventa esecuzione governata, l'evidenza diventa memoria operativa e ogni…





