

Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
APTs-Adversary-Simulation — This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks . | Kitploit
उपकरण/GitHubGitHub/s3n4t0r-0x0/apts-adversary-simulation
Privilege EscalationReconnaissancePersistence MechanismsExploitationLateral MovementPost-ExploitationPenetration TestingCommand and ControlLearning & EducationRed TeamingPayload DevelopmentAdversarial Attack
1.1k190497 दिन पहलेKitploit द्वारा समीक्षित

विवरण

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks .

साझा करें
GitHubs3n4t0r-0x0/apts-adversary-simulation

APTs-Adversary-Simulation

रिपॉजिटरी देखें
अनुरोधित भाषा में सामग्री उपलब्ध नहीं है। अंग्रेज़ी संस्करण दिखाया जा रहा है।

APTs Adversary Simulation


Comprehensive collection of simulated APT attacks based on real world TTPs used by state sponsored APT Groups from Russia, China, Iran, and North Korea
hollywood-Comp-02

[!CAUTION] Important Notice: This project is strictly for educational, research, and defensive security purposes only. Unauthorized use of these techniques may violate laws and result in serious legal consequences.

🧠 Overview

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, command and control (C2) servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks. The simulations are based on extensive research from leading cybersecurity firms, including PaloAlto Unit42, Kaspersky, Microsoft, Cisco, Trellix, CrowdStrike, and WithSecure.

Learn More About the Importance and Outcomes of the Experience:

  • Why Adversary Simulation? - Understanding the strategic value of simulating advanced threats
  • Adversary Simulation VS Adversary Emulation - Key differences and when to use each approach
  • How do I simulate an APT - Adversary Simulation Is Not a Methodology It's the Outcome of Experience

🎯 Simulated APT Groups

Note: APT group names in this repository follow the naming conventions used by different security vendors. The same APT group may have different names depending on the vendor (e.g., Mandiant, CrowdStrike, Microsoft, Kaspersky, etc.).
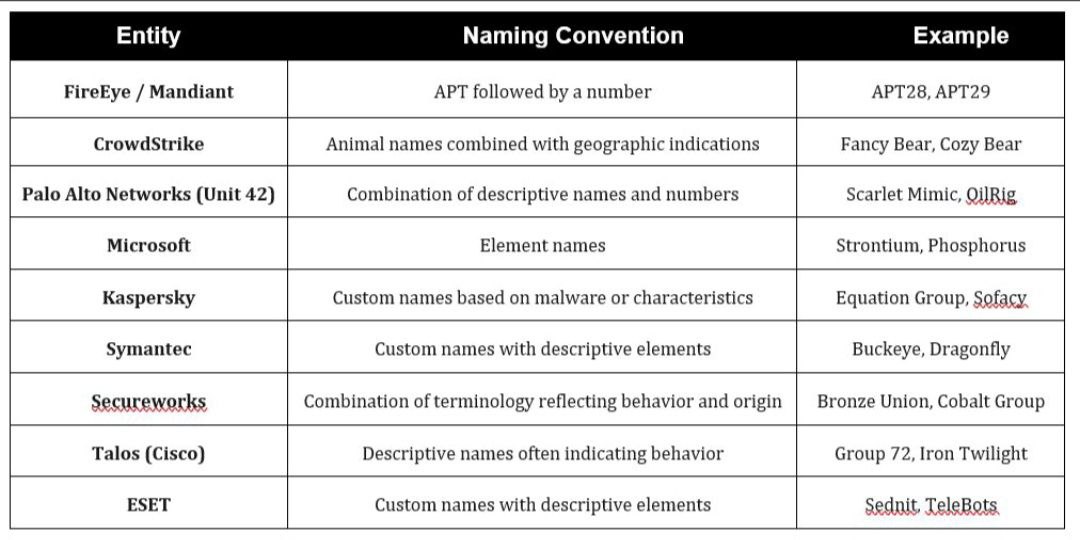
photo_2025-11-09_04-26-38

Below is the complete list of simulated APT Groups:

Country
of Origin
Russia 🇷🇺 China 🇨🇳 North Korea 🇰🇵 Iran 🇮🇷
APT Groups

Cozy Bear
Voodoo Bear
Fancy Bear
Energetic Bear
Berserk Bear
Gossamer Bear
Primitive Bear
Ember Bear
Venomous Bear

Mustang Panda
Wicked Panda
Goblin Panda
Deep Panda
Glacial Panda
Anchor Panda
Samurai Panda
Phantom Panda
Sunrise Panda
Ethereal Panda

Lazarus
Labyrinth Chollima
Velvet Chollima
Famous Chollima
Ricochet Chollima
Silent Chollima

Helix Kitten
Charming Kitten
Static Kitten
Muddy Water
Tracer Kitten
Pioneer Kitten
Nemesis Kitten
Clever Kitten
Pulsar Kitten
Remix Kitten
Haywire Kitten

🛠️ Adversary Framework

All adversary simulations are powered by BEAR-C2 a custom command and control framework designed for realistic threat simulation.
image psd(1)

📫 Contact

Telegram Twitter/X LinkedIn Reddit
टूल डाउनलोड करें

सबसे लोकप्रिय

सभी देखें →

हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 अंतिम OSINT टूलकिट: जाँच ग्राफ़, विश्वास स्कोरिंग, उपनाम परिवार, मानचित्र, टाइमलाइन और रिपोर्ट। 49 मॉड्यूल, 400+ साइटें, किसी API कुंजी की आवश्यकता नहीं।

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # घोस्टलॉक वन-टैप निष्पादन ऐप (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    प्लानर/वर्कर एजेंट, एसेट और एक्सप्लोरेशन ग्राफ़, MITM ट्रैफ़िक रिकॉर्डिंग, और भेद्यता पुनःपरीक्षण के साथ LLM मल्टी-एजेंट स्वायत्त पेनेट्रेशन टेस्टिंग प्लेटफ़ॉर्म।

    424
  • 4

    redforge

    cybersecurity91/redforge

    ब्राउज़र-साइड रेड टीम टूलकिट, जिसमें रेकॉन, पेलोड जनरेशन, क्रेडेंशियल हमलों, क्रिप्टो, एन्कोडिंग और एंगेजमेंट रिपोर्टिंग के लिए 102 ऑफ़लाइन टूल्स हैं।

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT प्लेटफ़ॉर्म जो Shadowserver रिपोर्ट्स को MongoDB में इनजेस्ट करता है और उन्हें इंटरैक्टिव मैप्स, विश्लेषण, निष्कर्षों, सलाहों और कार्यकारी डैशबोर्ड के रूप में पुनः प्रस्तुत करता है।

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI-मूल साइबरसुरक्षा के लिए कार्रवाई की प्रणाली—जहाँ इरादा नियंत्रित निष्पादन बन जाता है, साक्ष्य परिचालन स्मृति बन जाता है, और हर ऑपरेशन अगले को बेहतर बनाता है।

    276

सभी उपकरण खोजें

हमारे उपकरणों का संग्रह ब्राउज़ करें

सभी उपकरण देखें →






