Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
उपकरण/GitHubGitHub/msaad00/agent-bom
Vulnerability ScannersContainer SecurityCloud SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityMisconfigurationAI Security
GitHubmsaad00/agent-bom

agent-bom

AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account.

297883 दिन पहलेKitploit द्वारा समीक्षित
रिपॉजिटरी देखेंवेबसाइट
साझा करें
अनुरोधित भाषा में सामग्री उपलब्ध नहीं है। अंग्रेज़ी संस्करण दिखाया जा रहा है।

agent-bom — AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

Build PyPI Python 3.11 through 3.14

Apache-2.0 license OpenSSF Scorecard

AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

For AppSec teams and developers who run Claude Code, Cursor, Codex or any MCP client: see which agents, MCP servers, tools and packages are installed, which are vulnerable, and what each one can reach. Local scans need no account.

Quick start · Try in browser · Laptop → team → org · Product tour · Docs

Quick start

From the repository you want to inspect, with uv installed:

uvx agent-bom scan . -f html -o agent-bom-report.html

Open agent-bom-report.html for inventory, findings and fix guidance. Run it again later to see what changed. No MCP configuration in the project? Package findings still apply.

No project handy? uvx agent-bom scan --demo --offline scans a bundled sample. Exit 1 is expected there: the sample trips the security gate. Elsewhere, a non-zero exit can mean a security gate or incomplete assessment; inspect the report and coverage (exit codes, first-run guide).
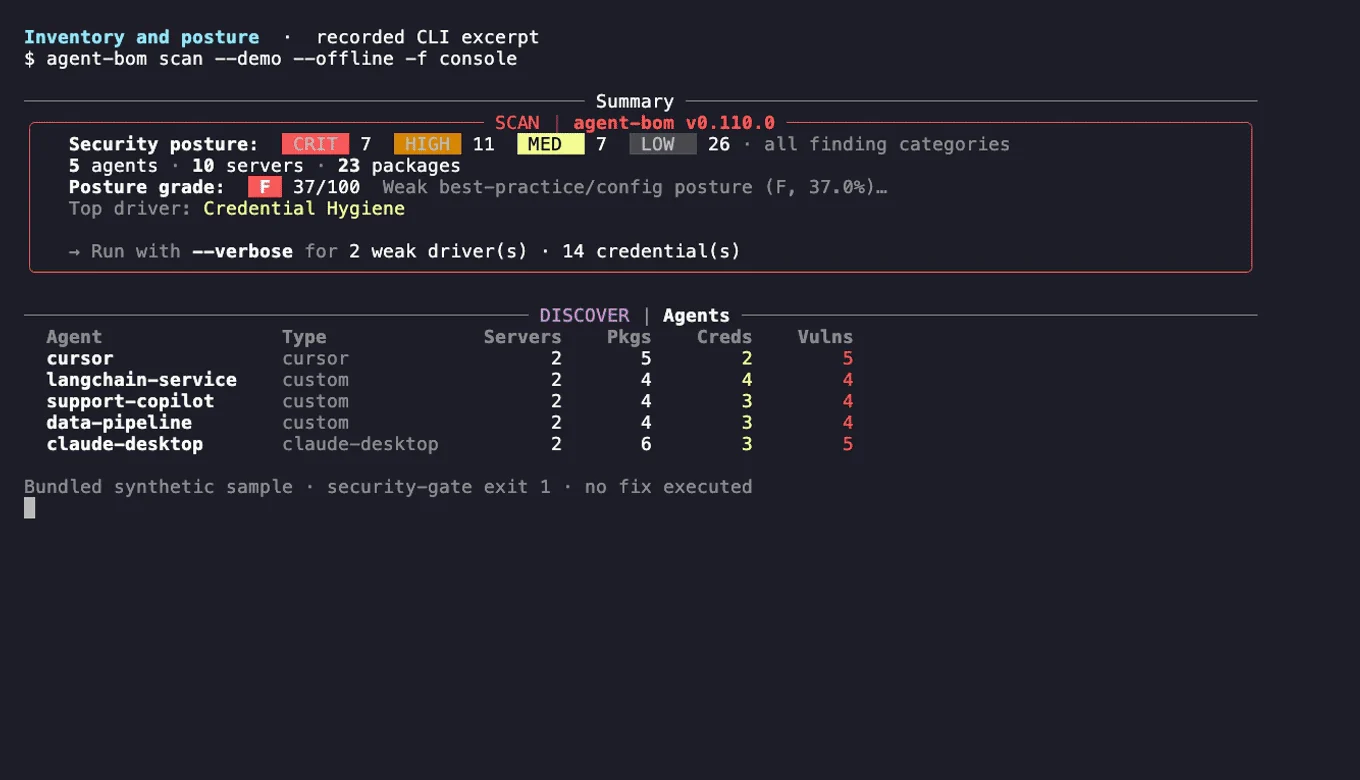
Recorded agent-bom CLI showing sample findings and remediation guidance; no fix executed

What the scan reads and what it does not establish

The scan stays inside this repository: packages, MCP configuration, secrets and personal data, skills and IaC. It does not read agent configuration elsewhere on the machine. Missing evidence is reported as partial, not clean. See what a scan does and does not establish.

From laptop to team to org

  • On your laptop: uvx agent-bom scan . for findings with fixes and a delta on every rescan; claude mcp add agent-bom -- uvx agent-bom mcp server to use agent-bom as a tool inside your coding agent (MCP server, plugins).
  • In your team: uses: koda-ai-studio/agent-bom@v0 on pull requests and a weekly schedule: for a PR gate with a findings comment, SARIF in code scanning and a weekly rescan that catches new CVEs in unchanged code (GitHub Action).
  • Across your org: agent-bom up locally, then Docker Compose or the Helm chart from oci://ghcr.io/koda-ai-studio/charts/agent-bom for retained scans, one graph of agents, MCP servers, packages and credentials, SSO and audit in your own infrastructure (self-host).

All three are free under Apache-2.0 and are adoption paths, not editions. There is no managed cloud offering today; community support runs on GitHub (deployment chooser, support model).

Why an AI supply-chain BOM

A CVE in an AI package, a poisoned tool description or an over-scoped credential matters by what the agent that loads it can reach. A package SBOM stops at packages; agent-bom records the chain, agent → MCP server → tool → package → credential → data, and keeps the evidence for every edge.

Sample production AI environment: Document Intake Agent uses a document-tools MCP server that depends on pillow 9.0.0, linked to KEV-listed CVE-2023-4863; Support Triage Agent uses a ticketing MCP server that references TICKETING_API_KEY, which can access a customer ticket archive

Sample data. What the sample shows

What it covers

Agents and MCP servers, models and AI platforms, dependencies, code, containers and IaC, cloud and data platforms, and a runtime MCP proxy and gateway. Exports are SARIF, CycloneDX, SPDX, JSON and HTML.


Coverage by area
टूल डाउनलोड करें

सबसे लोकप्रिय

सभी देखें →

हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 अंतिम OSINT टूलकिट: जाँच ग्राफ़, विश्वास स्कोरिंग, उपनाम परिवार, मानचित्र, टाइमलाइन और रिपोर्ट। 49 मॉड्यूल, 400+ साइटें, किसी API कुंजी की आवश्यकता नहीं।

    614
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # घोस्टलॉक वन-टैप निष्पादन ऐप (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    प्लानर/वर्कर एजेंट, एसेट और एक्सप्लोरेशन ग्राफ़, MITM ट्रैफ़िक रिकॉर्डिंग, और भेद्यता पुनःपरीक्षण के साथ LLM मल्टी-एजेंट स्वायत्त पेनेट्रेशन टेस्टिंग प्लेटफ़ॉर्म।

    389
  • 4

    redforge

    cybersecurity91/redforge

    ब्राउज़र-साइड रेड टीम टूलकिट, जिसमें रेकॉन, पेलोड जनरेशन, क्रेडेंशियल हमलों, क्रिप्टो, एन्कोडिंग और एंगेजमेंट रिपोर्टिंग के लिए 102 ऑफ़लाइन टूल्स हैं।

    334
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI-मूल साइबरसुरक्षा के लिए कार्रवाई की प्रणाली—जहाँ इरादा नियंत्रित निष्पादन बन जाता है, साक्ष्य परिचालन स्मृति बन जाता है, और हर ऑपरेशन अगले को बेहतर बनाता है।

    257
  • 6

    antifox

    antifox-ai/antifox

    AI मल्टी-एजेंट स्वायत्त पेनेट्रेशन टेस्टिंग प्लेटफ़ॉर्म जो रेकॉन, अटैक-सरफ़ेस डिस्कवरी, एक्सप्लॉइटेशन वैलिडेशन और साक्ष्य-आधारित रिपोर्ट डिलीवरी संचालित करता है।

    247

सभी उपकरण खोजें

हमारे उपकरणों का संग्रह ब्राउज़ करें

सभी उपकरण देखें →