
Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
HackSysExtremeVulnerableDriver — HackSys Extreme Vulnerable Driver (HEVD) - Windows और Linux | Kitploit
उपकरण/GitHubGitHub/hacksysteam/hacksysextremevulnerabledriver
भेद्यता विश्लेषणलर्निंग और शिक्षाबाइनरी शोषणलैब और अभ्यास
GitHubhacksysteam/hacksysextremevulnerabledriver

HackSysExtremeVulnerableDriver

HackSys Extreme Vulnerable Driver (HEVD) - Windows और Linux

रिपॉजिटरी देखें
वेबसाइट
3.1k584801 साल पहलेKitploit द्वारा समीक्षित

सबसे लोकप्रिय

सभी देखें →

हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।

सभी उपकरण खोजें

हमारे उपकरणों का संग्रह ब्राउज़ करें

सभी उपकरण देखें →
साझा करें

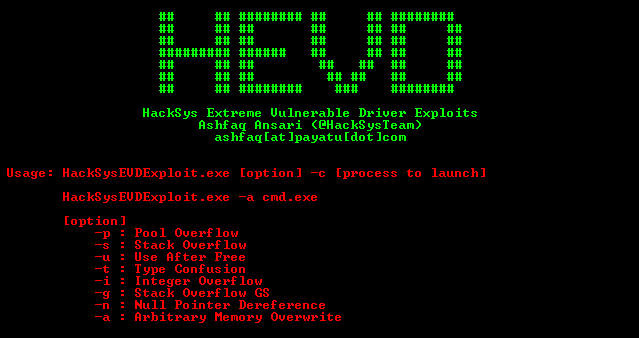
HackSys Extreme Vulnerable Driver

           ooooo   ooooo oooooooooooo oooooo     oooo oooooooooo.   
           `888'   `888' `888'     `8  `888.     .8'  `888'   `Y8b  
            888     888   888           `888.   .8'    888      888 
            888ooooo888   888oooo8       `888. .8'     888      888 
            888     888   888    "        `888.8'      888      888 
            888     888   888       o      `888'       888     d88' 
           o888o   o888o o888ooooood8       `8'       o888bood8P'   

Black Hat Arsenal Appveyor Build Status GitHub all Releases Twitter Follow Mastodon Follow Discord Server

HackSys Extreme Vulnerable Driver (HEVD) एक Windows Kernel ड्राइवर है जो जानबूझकर कमज़ोर बनाया गया है। इसे सुरक्षा शोधकर्ताओं और उत्साही लोगों के लिए विकसित किया गया है ताकि वे कर्नल-स्तर के शोषण में अपने कौशल में सुधार कर सकें।

HEVD विभिन्न प्रकार की कमज़ोरियाँ प्रदान करता है, सरल स्टैक बफ़र ओवरफ़्लो से लेकर अधिक जटिल समस्याओं जैसे use-after-free, पूल बफ़र ओवरफ़्लो, और रेस कंडीशन तक। इससे शोधकर्ता प्रत्येक कार्यान्वित कमज़ोरी के लिए शोषण तकनीकों का पता लगा सकते हैं।

Black Hat Arsenal 2016

  • प्रस्तुति
  • श्वेत पत्र

ब्लॉग पोस्ट

  • http://www.payatu.com/hacksys-extreme-vulnerable-driver/

बाहरी शोषण

  • https://github.com/wetw0rk/Exploit-Development/tree/master/HEVD-Exploits
  • https://github.com/sam-b/HackSysDriverExploits
  • https://github.com/sizzop/HEVD-Exploits
  • https://github.com/badd1e/bug-free-adventure
  • https://github.com/FuzzySecurity/HackSysTeam-PSKernelPwn
  • https://github.com/theevilbit/exploits/tree/master/HEVD
  • https://github.com/GradiusX/HEVD-Python-Solutions
  • http://pastebin.com/ALKdpDsF
  • https://github.com/Cn33liz/HSEVD-StackOverflow
  • https://github.com/Cn33liz/HSEVD-StackOverflowX64
  • https://github.com/Cn33liz/HSEVD-StackCookieBypass
  • https://github.com/Cn33liz/HSEVD-ArbitraryOverwrite
  • https://github.com/Cn33liz/HSEVD-ArbitraryOverwriteGDI
  • https://github.com/Cn33liz/HSEVD-StackOverflowGDI
  • https://github.com/Cn33liz/HSEVD-ArbitraryOverwriteLowIL
  • https://github.com/mgeeky/HEVD_Kernel_Exploit
  • https://github.com/tekwizz123/HEVD-Exploit-Solutions
  • https://github.com/FULLSHADE/Windows-Kernel-Exploitation-HEVD
  • https://github.com/w4fz5uck5/3XPL01t5/tree/master/OSEE_Training

बाहरी ब्लॉग पोस्ट

  • https://wetw0rk.github.io/posts/0x00-introduction-to-windows-kernel-exploitation/
  • https://wetw0rk.github.io/posts/0x00-introducci%C3%B3n-a-windows-kernel-explotaci%C3%B3n/
  • https://wetw0rk.github.io/posts/0x01-killing-windows-kernel-mitigations/
  • https://wetw0rk.github.io/posts/0x01-mat%C3%A1ndo-windows-kernel-mitigaciones/
  • https://wetw0rk.github.io/posts/0x02-introduction-to-windows-kernel-uafs/
  • https://wetw0rk.github.io/posts/0x02-introducci%C3%B3n-a-windows-kernel-uafs/
  • https://wetw0rk.github.io/posts/0x03-approaching-the-modern-windows-kernel-heap/
  • https://wetw0rk.github.io/posts/0x03-acerc%C3%A1ndose-al-heap-moderno-del-windows-kernel/
  • https://wetw0rk.github.io/posts/0x04-writing-what-where-in-the-kernel/
  • https://wetw0rk.github.io/posts/0x04-escribiendo-que-donde-en-el-kernel/
  • https://wetw0rk.github.io/posts/0x05-introduction-to-windows-kernel-type-confusion-vulnerabilities/
  • https://wetw0rk.github.io/posts/0x05-introducci%C3%B3n-a-windows-kernel-type-confusion-vulnerabilidades/
  • https://wetw0rk.github.io/posts/0x06-approaching-modern-windows-kernel-type-confusions/
  • https://wetw0rk.github.io/posts/0x06-acerc%C3%A1ndose-a-windows-kernel-type-confusions-modernos/
  • https://wetw0rk.github.io/posts/0x07-introduction-to-windows-kernel-race-conditions/
  • https://wetw0rk.github.io/posts/0x07-introducci%C3%B3n-a-windows-kernel-race-conditions/
  • https://wetw0rk.github.io/posts/0x08-modern-windows-kernel-race-conditions/
  • https://wetw0rk.github.io/posts/0x08-race-conditions-moderno-del-windows-kernel/
  • https://wetw0rk.github.io/posts/0x09-return-of-the-stack-overflow/
  • https://wetw0rk.github.io/posts/0x09-el-regreso-del-stack-overflow/
  • http://niiconsulting.com/checkmate/2016/01/windows-kernel-exploitation/
  • http://samdb.xyz/2016/01/16/intro_to_kernel_exploitation_part_0.html
  • http://samdb.xyz/2016/01/17/intro_to_kernel_exploitation_part_1.html
  • http://samdb.xyz/2016/01/18/intro_to_kernel_exploitation_part_2.html
  • http://samdb.xyz/2017/06/22/intro_to_kernel_exploitation_part_3.html
  • https://sizzop.github.io/2016/07/05/kernel-hacking-with-hevd-part-1.html
  • https://sizzop.github.io/2016/07/06/kernel-hacking-with-hevd-part-2.html
  • https://sizzop.github.io/2016/07/07/kernel-hacking-with-hevd-part-3.html
  • https://sizzop.github.io/2016/07/08/kernel-hacking-with-hevd-part-4.html
  • https://www.fuzzysecurity.com/tutorials/expDev/14.html
  • https://www.fuzzysecurity.com/tutorials/expDev/15.html
  • https://www.fuzzysecurity.com/tutorials/expDev/16.html
  • https://www.fuzzysecurity.com/tutorials/expDev/17.html
  • https://www.fuzzysecurity.com/tutorials/expDev/18.html
  • https://www.fuzzysecurity.com/tutorials/expDev/19.html
  • https://www.fuzzysecurity.com/tutorials/expDev/20.html
  • http://dokydoky.tistory.com/445
  • https://hshrzd.wordpress.com/2017/05/28/starting-with-windows-kernel-exploitation-part-1-setting-up-the-lab/
  • https://hshrzd.wordpress.com/2017/06/05/starting-with-windows-kernel-exploitation-part-2/
  • https://hshrzd.wordpress.com/2017/06/22/starting-with-windows-kernel-exploitation-part-3-stealing-the-access-token/
  • https://osandamalith.com/2017/04/05/windows-kernel-exploitation-stack-overflow/
  • https://osandamalith.com/2017/06/14/windows-kernel-exploitation-arbitrary-overwrite/
  • https://osandamalith.com/2017/06/22/windows-kernel-exploitation-null-pointer-dereference/
  • http://dali-mrabet1.rhcloud.com/windows-kernel-exploitation-arbitrary-memory-overwrite-hevd-challenges/
  • https://blahcat.github.io/2017/08/31/arbitrary-write-primitive-in-windows-kernel-hevd/
  • https://klue.github.io/blog/2017/09/hevd_stack_gs/
  • https://glennmcgui.re/introduction-to-windows-kernel-exploitation-pt-1/
  • https://glennmcgui.re/introduction-to-windows-kernel-driver-exploitation-pt-2/
  • https://kristal-g.github.io/2021/02/07/HEVD_StackOverflowGS_Windows_10_RS5_x64.html
  • https://kristal-g.github.io/2021/02/20/HEVD_Type_Confusion_Windows_10_RS5_x64.html
  • https://wafzsucks.medium.com/hacksys-extreme-vulnerable-driver-arbitrary-write-null-new-solution-7d45bfe6d116
  • https://wafzsucks.medium.com/how-a-simple-k-typeconfusion-took-me-3-months-long-to-create-a-exploit-f643c94d445f
  • https://mdanilor.github.io/posts/hevd-0/
  • https://mdanilor.github.io/posts/hevd-1/
  • https://mdanilor.github.io/posts/hevd-2/
  • https://mdanilor.github.io/posts/hevd-3/
  • https://mdanilor.github.io/posts/hevd-4/

लेखक

Ashfaq Ansari

टूल डाउनलोड करें