
 ev-flow/quark-engine
नियम-आधारित एंड्रॉइड मैलवेयर स्कोरिंग इंजन जो स्थैतिक और गतिशील विश्लेषण का उपयोग करके APK का विश्लेषण करता है, कमजोरियों का पता लगाता है, मैलवेयर परिवारों की पहचान करता है, और विस्तृत खतरा रिपोर्ट तैयार करता है।
<p align="center">
    <a href="https://www.blackhat.com/asia-24/arsenal/schedule/index.html#quark-script---dig-vulnerabilities-in-the-blackbox-37549">
        <img alt="Black Hat Arsenal" src="https://img.shields.io/badge/Black%20Hat%20Arsenal-Asia%202024-blue">
    </a>
    <a href="https://www.blackhat.com/asia-21/arsenal/schedule/index.html#quark-engine-storyteller-of-android-malware-22458">
        <img alt="Black Hat Arsenal" src="https://img.shields.io/badge/Black%20Hat%20Arsenal-Asia%202021-blue">
    </a>
    <a href="https://conference.hitb.org/hitb-lockdown002/sessions/quark-engine-an-obfuscation-neglect-android-malware-scoring-system/">
        <img alt="HITB" src="https://img.shields.io/badge/HITB-Lockdown%20002-red">
    </a>
    <a href="https://www.youtube.com/watch?v=XK-yqHPnsvc&ab_channel=DEFCONConference">
        <img alt="defcon" src="https://img.shields.io/badge/DEFCON%2028-BTV-blue">
    </a><br>
    <a href="https://github.com/quark-engine/quark-engine/actions/workflows/pytest.yml">
        <img alt="build status" src="https://github.com/quark-engine/quark-engine/actions/workflows/pytest.yml/badge.svg">
    </a>
    <a href="https://codecov.io/gh/quark-engine/quark-engine">
        <img alt="codecov" src="https://codecov.io/gh/ev-flow/quark-engine/graph/badge.svg">
    </a>
    <a href="https://github.com/18z/quark-rules/blob/master/LICENSE">
        <img alt="license" src="https://img.shields.io/badge/License-GPLv3-blue.svg">
    </a>
    <a href="https://www.python.org/downloads/release/python-31015/">
        <img alt="python version" src="https://img.shields.io/badge/python-3.10-blue.svg">
    </a>
    <a href="https://pypi.org/project/quark-engine/">
        <img alt="PyPi Download" src="https://pepy.tech/badge/quark-engine">
    </a><br>
    <a href="https://twitter.com/quarkengine">
        <img alt="Twitter" src="https://img.shields.io/twitter/follow/quarkengine?style=social">
    </a><br>
    <img src="https://assets.kitploit.com/production/public/readmes/6741/03a197011a23cc6c340ef8243156a4a8da0cb226daf3ea012a0d007029c48fa9.png"/>
</p>

## मैलवेयर परिवार विश्लेषण रिपोर्ट प्रदर्शनी

<table>

  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/e14e7970a278faef3a85a6ceee30dd7681c8d7be6f16bc8fad16ff3230600bc1.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/72948195e3960572f7c23ff84362625375890339c5f75d651fe42d02e9ed1e95.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/1705305abf7957429991bf0cf5ba0bc619edc460604806451ecd0ddc8c464a23.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/d94cb3d285cfcc850934be26d17b38c226bc671cddb707ce6597e399f2dca1de.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/2423f24f7933d1923794763e041bdb9d99027688f5f3254e73f7b36e79e3c00a.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/0035c5f69112d8097ee4ece87a8b0f05f28bc2dec6a8f8cec645138c4d0b5080.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/f73f15ad9490c35e70dbea6a90acbd69b480103f9fcdc87440868c3f745c1450.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/c0628a03cbd744f7cb5077d27e9cf3b31e4e6faa11a480c729e6f66f1c9f9391.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/ff076c7dc8c384297783518dcec6861ef3de193f292724589759ab38c6717032.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/d8a967c14e5b508626a281d50f008ab3a6422008231e9e7b3b6b8bbc0822afe5.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/eea1fde985ce1cbc5097045e39ed59a92b3c1b9defa920084d64764bd582b8f6.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/4e1ef70891c707c427030190d413c66e65183608abfc96d550c203ae7b121ead.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/64d7d5044f1b2e2219507f765302a95313f04c19e81a10f5b7c0dd04ceb13a12.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/5a4348c3ee554e08cf1509923c29152a337b9c1e7f674b5d0f187feb8884b7f0.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/cf2ac808de2437476ff2b20e8178cd906614fe5daea9c3d56c57683c45f73558.png" width="310"></td>
  </tr>
  <tr>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/00a382b46e7116952deba2411f72d1eb3addd9d94a0f43cc28419c6e7728c4c0.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/fb3f3c0f39b14940edfc6ba133a0670a333e509b19d1e4c5d259621d8875eefb.png" width="310"></td>
    <td><img src="https://assets.kitploit.com/production/public/readmes/6741/6bc7b397dedd9d531ff7a4add4e97001ff5bfe6f78d0506de06b0f4352f65538.png" width="310"></td>
  </tr>
  <tr>
      <td><img src="https://assets.kitploit.com/production/public/readmes/6741/946a13c57e64267f069f0bd0ca98dba98216d014092dc0f09c5eadb060854986.png" width="310"></td>
  </tr>
</table>


| परिवार      | सारांश                                            | हस्ताक्षर व्यवहार                    | रिपोर्ट |
|-------------|----------------------------------------------------|--------------------------|--------|
| DroidKungFu | C2 नियंत्रण के साथ विशेषाधिकार वृद्धि।              | 1. डिवाइस तक असीमित पहुंच प्राप्त करें।<br>2. अतिरिक्त ऐप्स इंस्टॉल/अनइंस्टॉल करें।<br>3. गोपनीय डेटा अग्रेषित करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-droidkungfu) |
| GoldDream   | रिमोट C2 कमांड के साथ SMS/कॉल लॉग एक्सफ़िल्ट्रेशन। | 1. SMS संदेशों और फ़ोन कॉल्स की निगरानी करें।<br>2. SMS संदेशों और फ़ोन कॉल्स को रिमोट सर्वर पर अपलोड करें।              | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-golddream) |
| SpyNote     | RAT के माध्यम से क्रेडेंशियल चोरी और डिवाइस निगरानी।  | 1. स्क्रीनशॉट लें।<br>2. उपयोगकर्ता इशारों का अनुकरण करें।<br>3. उपयोगकर्ता इनपुट लॉग करें।<br>4. C2 सर्वर के साथ संचार करें।      | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-spynote) |
| DawDropper  | वित्तीय चोरी के लिए बैंकिंग ट्रोजन इंस्टॉल करने वाला ड्रॉपर। | 1. रिमोट सर्वर से APK डाउनलोड करें।<br>2. अतिरिक्त APK इंस्टॉल करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-dawdropper) |
| SLocker     | एंड्रॉइड रैनसमवेयर जो डिवाइस को लॉक/एन्क्रिप्ट करता है।     | 1. ओवरले स्क्रीन से डिवाइस को लॉक करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-slocker) |
| PhantomCard | NFC रिले-आधारित वित्तीय धोखाधड़ी।                   | 1. C2 सर्वर से संचार करें।<br>2. NFC कार्ड का भुगतान डेटा पढ़ें।<br>3. धोखाधड़ी वाली स्क्रीन के माध्यम से NFC कार्ड के PIN कैप्चर करें।  | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-phantomcard) |
| ToxicPanda  | डिवाइस पर धोखाधड़ी सक्षम करने वाला बैंकिंग ट्रोजन।     | 1. एक्सेसिबिलिटी का दुरुपयोग करें।<br>2. रिमोट डिवाइस नियंत्रण।<br>3. OTP इंटरसेप्ट करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-toxicpanda) |
| Hydra       | ओवरले हमलों का उपयोग करने वाला बैंकिंग ट्रोजन।        | 1. ओवरले क्रेडेंशियल चोरी।<br>2. एक्सेसिबिलिटी का दुरुपयोग।<br>3. OTP/कुकीज़ चुराएं। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-hydra) |
| SharkBot    | वित्तीय क्रेडेंशियल और लेन-देन को लक्षित करने वाला बैंकिंग ट्रोजन। | 1. एक्सेसिबिलिटी सेवाओं का दुरुपयोग करें।<br>2. क्रेडेंशियल चुराने के लिए ओवरले हमले करें।<br>3. SMS संदेशों (OTP) को इंटरसेप्ट करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-sharkbot) |
| Antidot     | वित्तीय डेटा चोरी के लिए वैध अपडेट के रूप में प्रच्छन्न बैंकिंग ट्रोजन। | 1. SMS संदेशों (OTP) को इंटरसेप्ट करें।<br>2. उपयोगकर्ता इनपुट लॉग करें (कीलॉगिंग)।<br>3. C2 के माध्यम से रिमोट कंट्रोल सक्षम करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-antidot) |
| Arsink      | क्रेडेंशियल और वित्तीय डेटा एक्सफ़िल्ट्रेशन पर ध्यान केंद्रित करने वाला बैंकिंग ट्रोजन। | 1. डिवाइस से संवेदनशील डेटा चुराएं।<br>2. SMS संदेशों (OTP) को इंटरसेप्ट करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-arsink) |
| TrickMo     | ओवरले हमलों और एक्सेसिबिलिटी दुरुपयोग के माध्यम से क्रेडेंशियल चोरी के लिए बैंकिंग ट्रोजन। | 1. बैंकिंग क्रेडेंशियल चुराने के लिए ओवरले हमले।<br>2. 2FA बायपास के लिए SMS इंटरसेप्ट करें।<br>3. स्क्रीन रिकॉर्डिंग और एक्सेसिबिलिटी दुरुपयोग।<br>4. रिफ्लेक्शन के माध्यम से डायनामिक पेलोड लोडिंग। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-trickmo) |
| Anubis      | RAT क्षमताओं वाला बैंकिंग ट्रोजन।              | 1. ओवरले क्रेडेंशियल चोरी।<br>2. कीलॉगिंग।<br>3. SMS (OTP) इंटरसेप्ट करें।<br>4. C2 के माध्यम से रिमोट कंट्रोल। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-anubis) |
| GodFather  | ओवरले और एक्सेसिबिलिटी दुरुपयोग के माध्यम से वित्तीय क्रेडेंशियल को लक्षित करने वाला बैंकिंग ट्रोजन। | 1. क्रेडेंशियल चुराने के लिए ओवरले हमले करें।<br>2. एक्सेसिबिलिटी सेवाओं का दुरुपयोग करें।<br>3. SMS संदेशों (OTP) को इंटरसेप्ट करें।<br>4. बैंकिंग क्रेडेंशियल और संवेदनशील डेटा चुराएं। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-godfather) |
| TangleBot   | व्यक्तिगत और वित्तीय डेटा चुराने वाला SMS-आधारित एंड्रॉइड मैलवेयर। | 1. SMS फ़िशिंग लिंक के माध्यम से फैलें।<br>2. डिवाइस इंटरैक्शन और ओवरले स्क्रीन को नियंत्रित करें।<br>3. SMS, संपर्क, कॉल लॉग, कैमरा और माइक्रोफ़ोन तक पहुंचें।<br>4. खाता और वित्तीय जानकारी चुराएं। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#new-quark-rules-for-tanglebot) |
| BRATA       | रिमोट कंट्रोल और एंटी-विश्लेषण क्षमताओं वाला बैंकिंग ट्रोजन। | 1. बैंकिंग क्रेडेंशियल चुराने के लिए ओवरले हमले करें।<br>2. डिवाइस नियंत्रण के लिए एक्सेसिबिलिटी सेवाओं का दुरुपयोग करें।<br>3. SMS संदेशों (OTP) को इंटरसेप्ट करें।<br>4. फ़ैक्टरी रीसेट या डिवाइस वाइप कमांड निष्पादित करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#brata-malware-family-analysis-report) |
| Cerberus    | ओवरले और डिवाइस नियंत्रण के माध्यम से वित्तीय क्रेडेंशियल को लक्षित करने वाला बैंकिंग ट्रोजन। | 1. क्रेडेंशियल चुराने के लिए ओवरले हमले करें।<br>2. एक्सेसिबिलिटी सेवाओं का दुरुपयोग करें।<br>3. उपयोगकर्ता इनपुट लॉग करें (कीलॉगिंग)।<br>4. C2 के माध्यम से रिमोट कंट्रोल सक्षम करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#cerberus-malware-family-analysis-report) |
| SuperCardX  | संपर्क रहित भुगतान धोखाधड़ी सक्षम करने वाला NFC रिले मैलवेयर। | 1. NFC भुगतान कार्ड डेटा पढ़ें।<br>2. NFC लेन-देन को हमलावर-नियंत्रित डिवाइसों पर रिले करें।<br>3. C2 सर्वर से संचार करें।<br>4. अनधिकृत संपर्क रहित भुगतान की सुविधा प्रदान करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#supercardx-malware-family-analysis-report) |
| NGate       | रिले हमलों और भुगतान धोखाधड़ी सक्षम करने वाला NFC-आधारित मैलवेयर। | 1. NFC भुगतान कार्ड डेटा पढ़ें।<br>2. NFC संचार को हमलावर-नियंत्रित डिवाइसों पर रिले करें।<br>3. C2 सर्वर से संचार करें।<br>4. अनधिकृत संपर्क रहित भुगतान की सुविधा प्रदान करें। | [देखें](https://quark-engine.readthedocs.io/en/latest/malware_report.html#ngate-malware-family-analysis-report) |

## त्वरित आरंभ

### चरण 1. PyPi के माध्यम से इंस्टॉल करें
Quark Engine का नवीनतम संस्करण इंस्टॉल करें:
```bash
$ pip3 install -U quark-engine
```

### चरण 2. नवीनतम नियम डाउनलोड करें
नवीनतम नियम डेटाबेस प्राप्त करें:
```bash
$ freshquark
```

### चरण 3. सारांश रिपोर्ट चलाएँ
डाउनलोड किए गए नियमों के साथ APK का विश्लेषण करें और एक सारांश रिपोर्ट तैयार करें:
```bash
$ quark -a <apk_file> -s
```
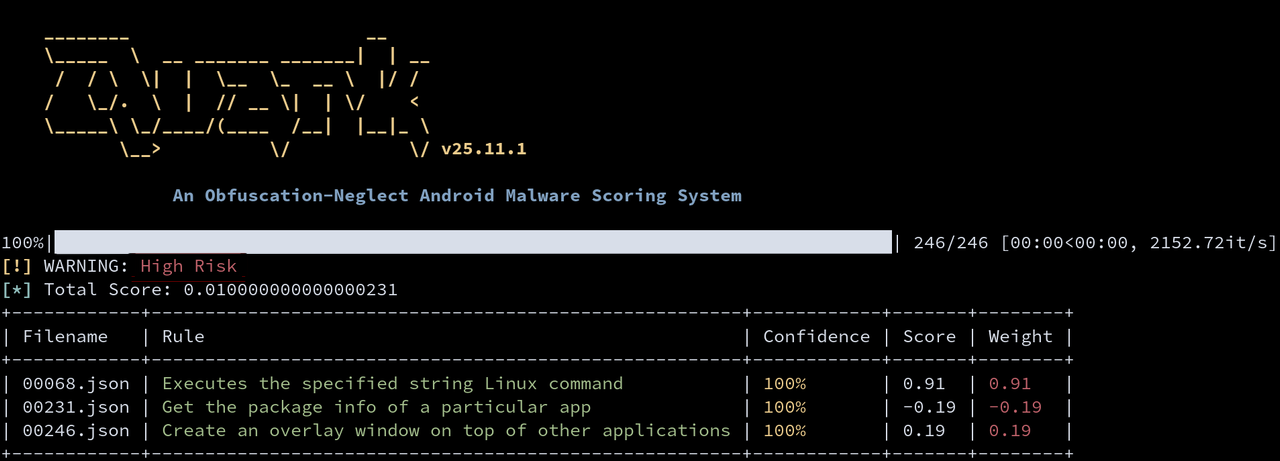
### चरण 4. परिणाम देखें
उदाहरण आउटपुट:
<img width="1280" height="461" alt="Screenshot-2025-11-25-22-36-54" src="https://assets.kitploit.com/production/public/readmes/6741/896c831335911a2de27ffe4eaa7f501d0f1670432afde44c94df5f1a46b06bd1.png" />


## आभार

### दी हनीनेट प्रोजेक्ट (The Honeynet Project)

<a href="https://www.honeynet.org"> <img style="border: 0.2px solid black" width=115 height=150 src="https://assets.kitploit.com/production/public/readmes/6741/3434e2b0361550a5a1836ff81c009062d9e83ef7bb84cd53186cd9cd939252ed.png" alt="Honeynet.org logo"> </a>

### गूगल समर ऑफ़ कोड (Google Summer Of Code)

Quark-Engine ने Honeynet Project के तहत GSoC में भाग लिया है!

*   2021:
    *   [YuShiang Dang](https://twitter.com/YushianhD): [नई नियम निर्माण तकनीक और सुरक्षा ओपन सोर्स प्रोजेक्ट्स के बीच Quark को सर्वव्यापी बनाना](https://github.com/ev-flow/ref/blob/main/GSoC-2021-YuShiangDang.md)
    *   [Sheng-Feng Lu](https://twitter.com/haeter525): [Quark-Engine की कोर लाइब्रेरी बदलना](https://github.com/ev-flow/ref/blob/main/GSoC-2021-ShengFengLu.md)

आगामी GSoC के लिए जुड़े रहें! अधिक जानकारी के लिए [Honeynet Slack chat](https://gsoc-slack.honeynet.org/) में शामिल हों।

## Quark Engine टीम के मुख्य मूल्य

*   हम **युद्धक्षेत्र** से प्यार करते हैं। हम **अनिश्चितताओं** को अपनाते हैं। हम **असंभव** को चुनौती देते हैं। हम हर चीज़ पर **पुनर्विचार** करते हैं। हम लोगों के सोचने का तरीका बदलते हैं। और सबसे महत्वपूर्ण, हम पहले दूसरों को लाभ पहुँचाकर स्वयं को लाभ पहुँचाते हैं।