
 dozermx/argus
बहु-चरणीय टोही और आक्रमण-सतह स्कैनर जो डोमेन, IP, ASN, क्लाउड संपत्तियों और CVE को CVSS स्कोरिंग और अनुपालन मैपिंग के साथ एक ज्ञान ग्राफ में मैप करता है।





सुरक्षा खुफिया फ्रेमवर्क
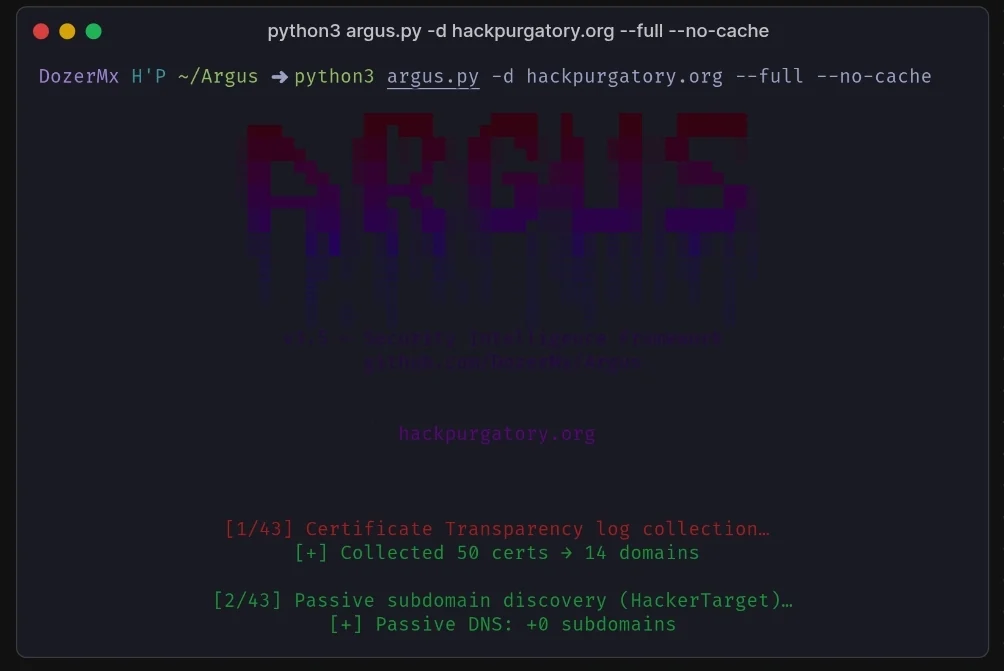
Argus एक मल्टी-फेज़ सुरक्षा टोही और विश्लेषण फ्रेमवर्क है जो पेशेवर पेनेट्रेशन टेस्टिंग और अटैक सरफेस आकलन के लिए बनाया गया है। यह पूरी तरह से स्वायत्त रूप से चलता है — कोई API कुंजी आवश्यक नहीं, कोई बाहरी सेवा नहीं, कोई खाता नहीं। एक एकल कमांड किसी संगठन के बाहरी एक्सपोज़र की पूरी तस्वीर तैयार करता है।
argus/
├── sources/          Certificate Transparency, passive DNS, brute force
├── correlators/      DNS resolution, CDN bypass, port scanning
├── intelligence/     43 analysis modules
│   ├── Core          TLS, HTTP, email, content discovery, JS secrets
│   ├── Graph         Attack paths, compliance, CVE, anomaly detection
│   ├── Advanced      SSRF chains, OAuth/GraphQL/WebSocket, BGP, stealth
│   └── Intelligence  Deep CVE, API enumeration, cloud storage, threat intel
├── ontology/         Knowledge graph (NetworkX), entity model, pivot engine
├── output/           HTML report, executive report, CSV, JSON, terminal
└── web/              FastAPI real-time dashboard with WebSocket
इंजन सभी खोजी गई संस्थाओं — डोमेन, IP, प्रमाणपत्र, संगठन, तकनीक, खुले पोर्ट — और उनके बीच के संबंधों का एक नॉलेज ग्राफ बनाता है। प्रत्येक निष्कर्ष एक विसंगति है जो CVSS 3.1 स्कोर, अटैक पाथ लिंकेज और कंप्लायंस मैपिंग के साथ एक ग्राफ नोड से जुड़ी होती है।
| रेंज | श्रेणी | कवरेज |
|---|---|---|
| 1–9 | टोही | CT लॉग संग्रह, passive DNS, AXFR, सबडोमेन ब्रूट फोर्स (2,500+ शब्द + permutations), DNS रिज़ॉल्यूशन, IPv6, ASN खुफिया, CDN origin bypass |
| 10–17 | सरफेस विश्लेषण | TLS फिंगरप्रिंटिंग, HTTP हेडर विश्लेषण, कंटेंट डिस्कवरी (100+ पाथ), JavaScript सीक्रेट स्कैनिंग, सप्लाई चेन CVE, कैश पॉइज़निंग, CORS, HTTP स्मगलिंग प्रोब |
| 18–30 | खुफिया | ईमेल सुरक्षा (SPF/DMARC/DKIM), Wayback Machine, रिवर्स IP, JARM C2 फिंगरप्रिंटिंग, विसंगति पहचान, CVSS 3.1 स्कोरिंग, अटैक पाथ संश्लेषण, कंप्लायंस मैपिंग (OWASP/GDPR/ISO 27001/NIST/PCI-DSS), CVE सहसंबंध, ग्राफ एनालिटिक्स, स्कैन diff |
| 31–35 | सक्रिय परीक्षण | HTTP रिक्वेस्ट स्मगलिंग (CL.TE/TE.CL/TE.TE), क्रॉस-ऑर्ग सहसंबंध, GNN सबडोमेन भविष्यवाणी, प्रमाणीकरण विश्लेषण (forms/JWT/Basic Auth), पैरामीटर फ़ज़िंग (SQLi/XSS/SSRF/IDOR/traversal) |
| 36–39 | उन्नत | BGP/AS पाथ + क्लाउड प्रदाता सहसंबंध, SSRF चेन पिवटिंग (क्लाउड मेटाडेटा, आंतरिक सेवाएँ, Gopher), OAuth/GraphQL/WebSocket प्रोटोकॉल फ़ज़िंग, हनीपॉट पहचान |
| 40–43 | खुफिया+ | डीप CVE फिंगरप्रिंटिंग (22 तकनीकें), API/OpenAPI/Swagger गणना, क्लाउड स्टोरेज गणना (S3/Azure/GCS/DO), थ्रेट इंटेलिजेंस (DNS ब्लैकलिस्ट, Tor exit, ASN प्रतिष्ठा) |
आवश्यकताएँ: Python 3.9+, Linux/macOS/Termux
git clone https://github.com/DozerMx/Argus
cd Argus
pip install -r requirements.txt
वेब UI (वैकल्पिक):
pip install fastapi uvicorn websockets
python argus.py -d TARGET [OPTIONS]
# CT log collection + DNS resolution + anomaly detection
python argus.py -d target.com

# Full 43-phase scan
python argus.py -d target.com --full

# Full scan with executive report
python argus.py -d target.com --full --output executive

# Full scan with authentication and fuzzing
python argus.py -d target.com --full --fuzz --auth

# Scan with known credentials
python argus.py -d target.com --full --auth --user admin --password admin123
# Subdomain brute force + AXFR
python argus.py -d target.com --brute --axfr

# Deep infrastructure: ASN + CDN bypass + ports
python argus.py -d target.com --deep --cdn-bypass --ports

# Stealth scan (paranoid jitter profile)
python argus.py -d target.com --full --stealth-profile paranoid

# Through Tor
python argus.py -d target.com --full --proxy socks5://127.0.0.1:9050
# Bulk scan from file
python argus.py -f targets.txt --full --output json

# Continuous monitoring with Slack alerts
python argus.py -d target.com --daemon --webhook https://hooks.slack.com/...

# Web UI dashboard
python argus.py --serve --ui-port 8080
Target:
  -d DOMAIN             Single target domain
  -f FILE               File with one domain per line

Scan Modules:
  --full                Enable all modules
  --deep                ASN, cloud detection, Wayback, reverse IP
  --brute               Subdomain brute force + permutations
  --axfr                DNS zone transfer
  --cdn-bypass          CDN/WAF origin IP discovery
  --ports               TCP port scan + banner grab (178 ports)
  --jarm                JARM TLS fingerprinting
  --fuzz                Parameter fuzzing (SQLi, XSS, SSRF, IDOR, traversal)
  --auth                Authentication analysis
  --user USER           Username for authenticated scanning
  --password PASS       Password for authenticated scanning

Output:
  --output FORMAT       terminal | html | executive | json | csv
  --outfile PATH        Output file path
  -v                    Verbose logging
  -q                    Quiet mode

Performance:
  --threads N           Concurrent threads (default: 30)
  --timeout N           Request timeout in seconds (default: 10)
  --proxy URL           Proxy (socks5://host:port or http://host:port)
  --no-cache            Disable disk cache
  --stealth-profile     paranoid | careful | normal | aggressive

Web UI:
  --serve               Launch real-time web dashboard
  --ui-port N           Web UI port (default: 8080)

Daemon:
  --daemon              Continuous monitoring mode
  --webhook URL         Webhook URL for alerts (Slack/Telegram)
  --interval N          Scan interval in hours (default: 6)
संपूर्ण इन्फ्रास्ट्रक्चर का इंटरैक्टिव ग्राफ विज़ुअलाइज़ेशन जिसमें निष्कर्ष, जोखिम स्कोरिंग और संबंध मैपिंग शामिल है। स्व-निहित एकल फ़ाइल।
व्यावसायिक भाषा में सारांश जिसमें अटैक पाथ विवरण, फ्रेमवर्क-वार कंप्लायंस उल्लंघन, प्राथमिकता-आधारित रेमेडिएशन रोडमैप और जोखिम मैट्रिक्स शामिल है।
पूर्ण मशीन-पठनीय आउटपुट जिसमें संपूर्ण नॉलेज ग्राफ, CVSS स्कोर सहित सभी विसंगतियाँ, अटैक पाथ और स्कैन मेटाडेटा शामिल हैं। SIEM, टिकटिंग या कस्टम टूलिंग के साथ एकीकरण के लिए उपयुक्त।

