
FortinetHunter (@YogSoth0) बाइनरी क्रैकिंग एप्लिकेशन। FortinetHunter के लिए CTF का हिस्सा। ELF door: एक stripped Nuitka onefile, एक XOR-scrambled Argon2id verifier, AES-GCM integrity।
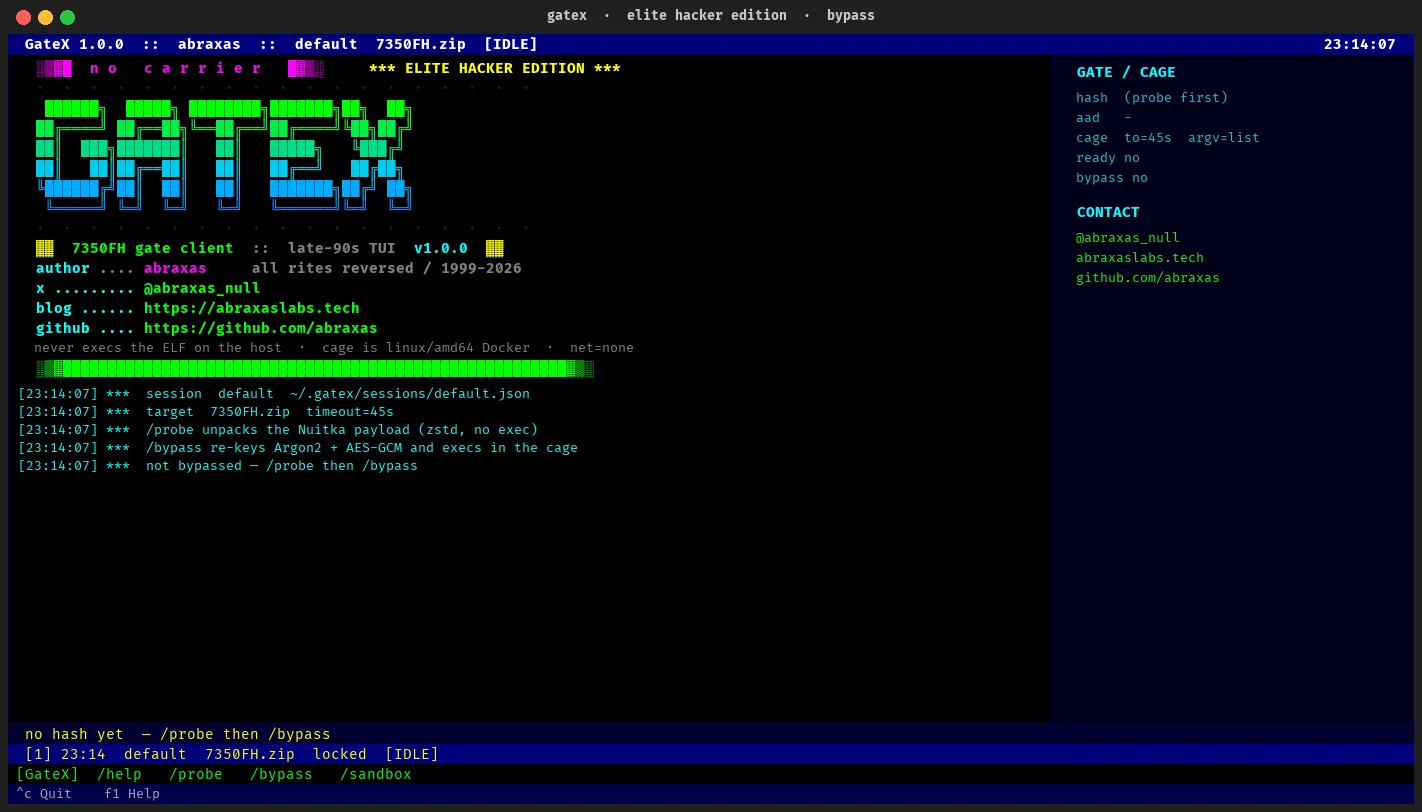
TUI जो "Fortinet Hunter 2026" Nuitka पासवर्ड गेट को re-key करता है। @YoSoth0 द्वारा एक capture-the-flag चुनौती का हिस्सा Write-up: Hunting the Fortinet Hunter 0-day
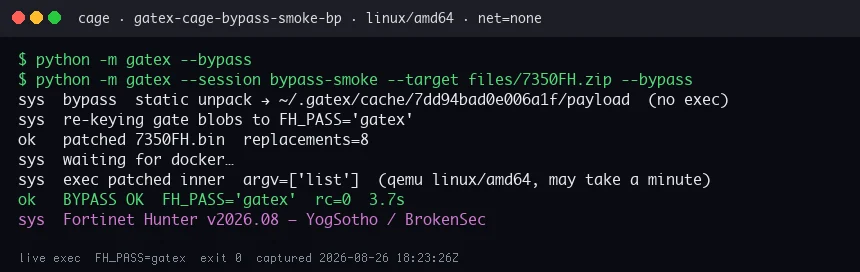
ELF होस्ट पर कभी नहीं चलता। GateX स्थिर रूप से onefile payload को unpack करता है, scrambled Argon2id hash और AES-GCM banner को XOR-unmask करता है, उन blobs को फिर से लिखता है ताकि FH_PASS=gatex दोनों checks को संतुष्ट करे, फिर inner binary को एक locked-down Docker cage के अंदर exec करता है।
यह लेखक के मूल passphrase को recover नहीं करता। Argon2id (m=65536,t=3,p=4) अपना काम कर रहा है। Plugins पहले से ही inner ELF में compile किए गए थे; पासवर्ड केवल एक banner को unwrap करता है।
abraxas
7350FH.zip (शिप नहीं किया गया)Payload अविश्वसनीय CTF malware-आकार का कोड है। GateX इसे केवल इन शर्तों के तहत exec करता है:
--platform linux/amd64--network none--read-only + unpack के लिए tmpfs--cap-drop ALL --security-opt no-new-privileges:true65532, 2 GiB RAM, 1 CPU, 256 pidsgit clone [email protected]:abraxas/GateX.git
cd GateX
python3 -m venv .venv
.venv/bin/pip install -r requirements.txt
चुनौती zip (या inner ELF) को वहाँ रखें जहाँ GateX उसे देख सके:
mkdir -p files
cp /path/to/7350FH.zip files/7350FH.zip
TUI:
.venv/bin/python -m gatex --target files/7350FH.zip
TUI के अंदर:
/probe          # static zstd unpack + assemble the Argon2id hash (no exec)
/sandbox up     # start Docker, build gatex-cage:noble
/bypass         # re-key to FH_PASS=gatex and exec list in the cage
/cmd --help     # argv against the patched inner ELF
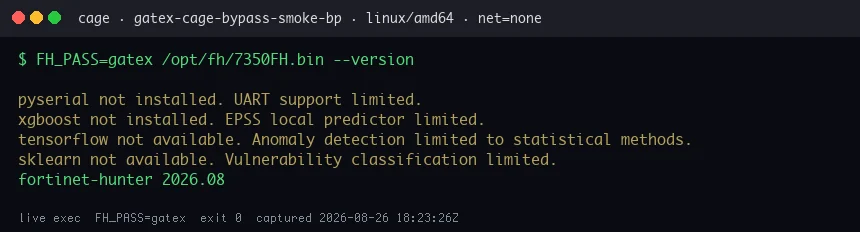
/cmd --version
/cmd score --ml
Headless:
# unpack + print the assembled argon2id hash (no TUI, no exec)
.venv/bin/python -m gatex --target files/7350FH.zip --probe

# re-key + exec list in the cage
.venv/bin/python -m gatex --target files/7350FH.zip --bypass
वैकल्पिक --session name state को ~/.gatex/sessions/ (mode 0600) के अंतर्गत रखता है।
| Command | What it does |
|---|---|
/help | Command list |
/probe | Static unpack + assemble Argon2id hash (no exec) |
/bypass [password] | Re-key gate blobs (default gatex) and exec in the cage |
/cmd [args…] | argv passed to the patched ELF (list, --help, --version, …) |
/sandbox /sandbox up /sandbox down | Docker status / build / destroy |
/target <zip|elf> | Switch binary |
/session name | Switch reusable session |
/timeout <seconds> | Cage exec timeout |
/quit | Save and leave |
F1 = help.
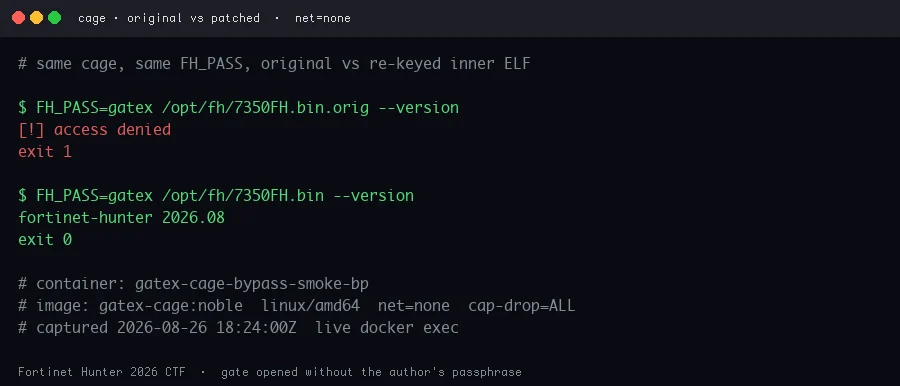
KAY + zstd) है। Inner image 7350FH.bin है।BYTES constant c + fh-slim-hardened-v2 के सामने बैठे हैं।utf-8(xor(b64decode(ct), cycle(b64decode(key)))) है। तीन fragments असली PHC को assemble करते हैं। binary में एक plaintext Argon2 string argon2-cffi doctest decoy है — उसे अनदेखा करें।fh-slim-v2-salt-2026 / fh-slim-v2-core) → एक 79-byte banner का AES-256-GCM। फिर cli.main()। Exploits ciphertext में नहीं हैं।/bypass आपके जानने वाले पासवर्ड का एक नया PHC लिखता है, AAD b"fh-slim-hardened-v2" (bytes value, नहीं कि on-disk cfh-… needle) के अंतर्गत एक replacement banner encrypt करता है, और patched inner को /opt/fh/7350FH.bin के रूप में LD_LIBRARY_PATH=$ORIGIN के साथ चलाता है।Original inner + FH_PASS=gatex अभी भी [!] access denied प्रिंट करता है। यही प्रयोग है।
Re-keyed inner के विरुद्ध live docker exec, linux/amd64, net none, caps dropped, uid 65532। 2026-08-26 को कैप्चर किया गया।
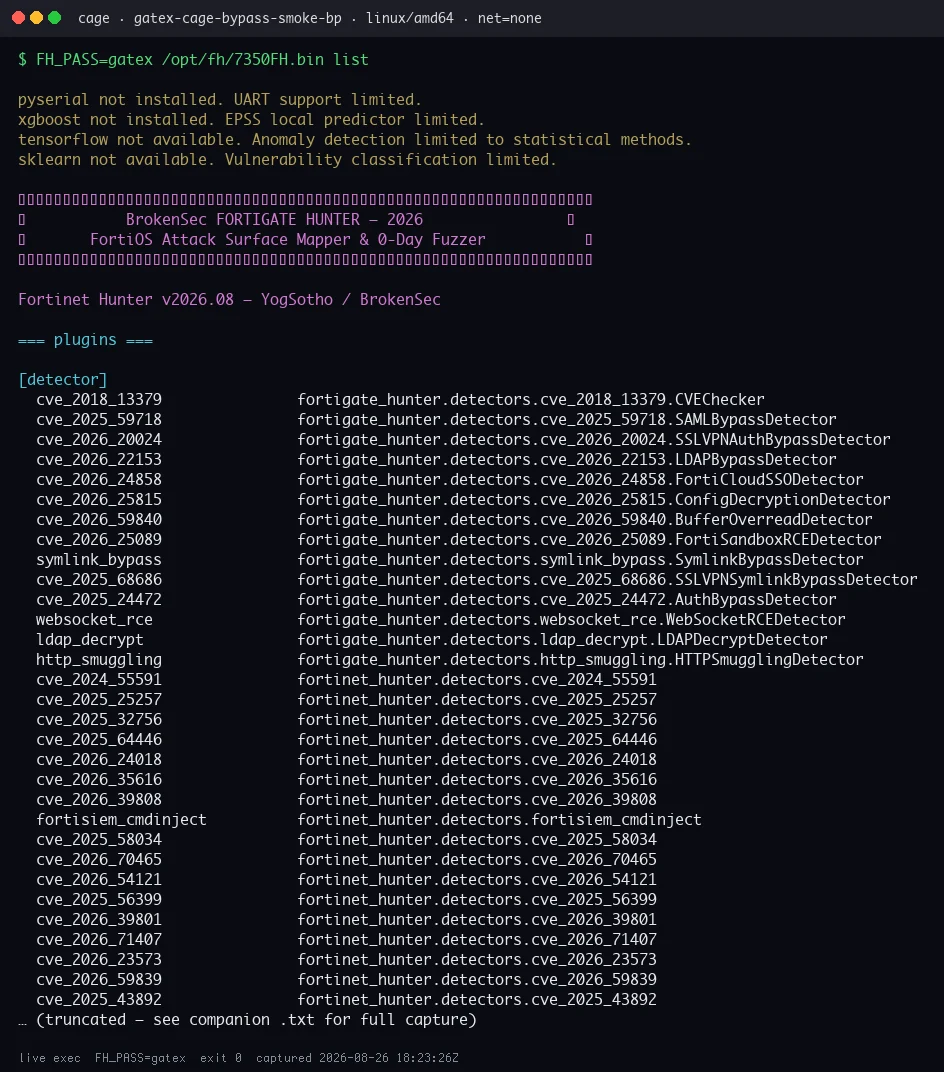
पूर्ण transcripts: files/evidence/*.txt और files/hunter-cli/।
.venv/bin/pip install pytest
.venv/bin/python -m pytest tests/test_offline.py -q
Patch/unpack परीक्षण जिन्हें files/7350FH.zip चाहिए, यदि zip अनुपस्थित है तो skip हो जाते हैं।
एक CTF के लिए लिखा गया जिसकी लेखक ने अनुमति दी थी। इसे उन सिस्टमों पर न लक्षित करें जो आपके नहीं हैं। GateX कोई exploits और 7350FH की कोई प्रति शिप नहीं करता।
हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।
अभी तक कोई लोकप्रियता डेटा नहीं है।


