
xalgorix v4.6.72
स्वायत्त AI पेंटेस्टिंग एजेंट — वास्तविक समय टोही, भेद्यता पहचान, और एक्सप्लॉइटेशन ऑर्केस्ट्रेशन। Go + TypeScript।

Xalgorix — Open-source AI pentester that proves vulnerabilities
Most scanners detect. Xalgorix proves. An autonomous LLM agent works a full pentest methodology, then an independent verifier re-exploits every finding before it's reported — so you get proof, not a pile of maybes to triage. Self-hosted, private, and bring-your-own-LLM. Built in Go + TypeScript.
🚀 Quick Start · 💡 Why Xalgorix · ✨ Features · 🎯 Use Cases · ☁️ Self-host or Cloud · 📖 Docs · 💬 Discussions
| 🖥️ Self-host — this repo | ☁️ Xalgorix Cloud — nothing to install |
|---|---|
| Free and Apache-2.0. Runs on your machine with your own LLM key, or fully local with Ollama. Findings and reports stay on your infrastructure. | The same exploit-verified engine in your browser. Model, out-of-band callbacks and scheduling are managed for you. Packs from $10; credits never expire. |
| Install in two commands ↓ | Compare self-hosted vs Cloud → |
🤖 Only need PR reviews? The free Xalgorix GitHub App comments a security review on every pull request — no account, no API key.
📸 Screenshots
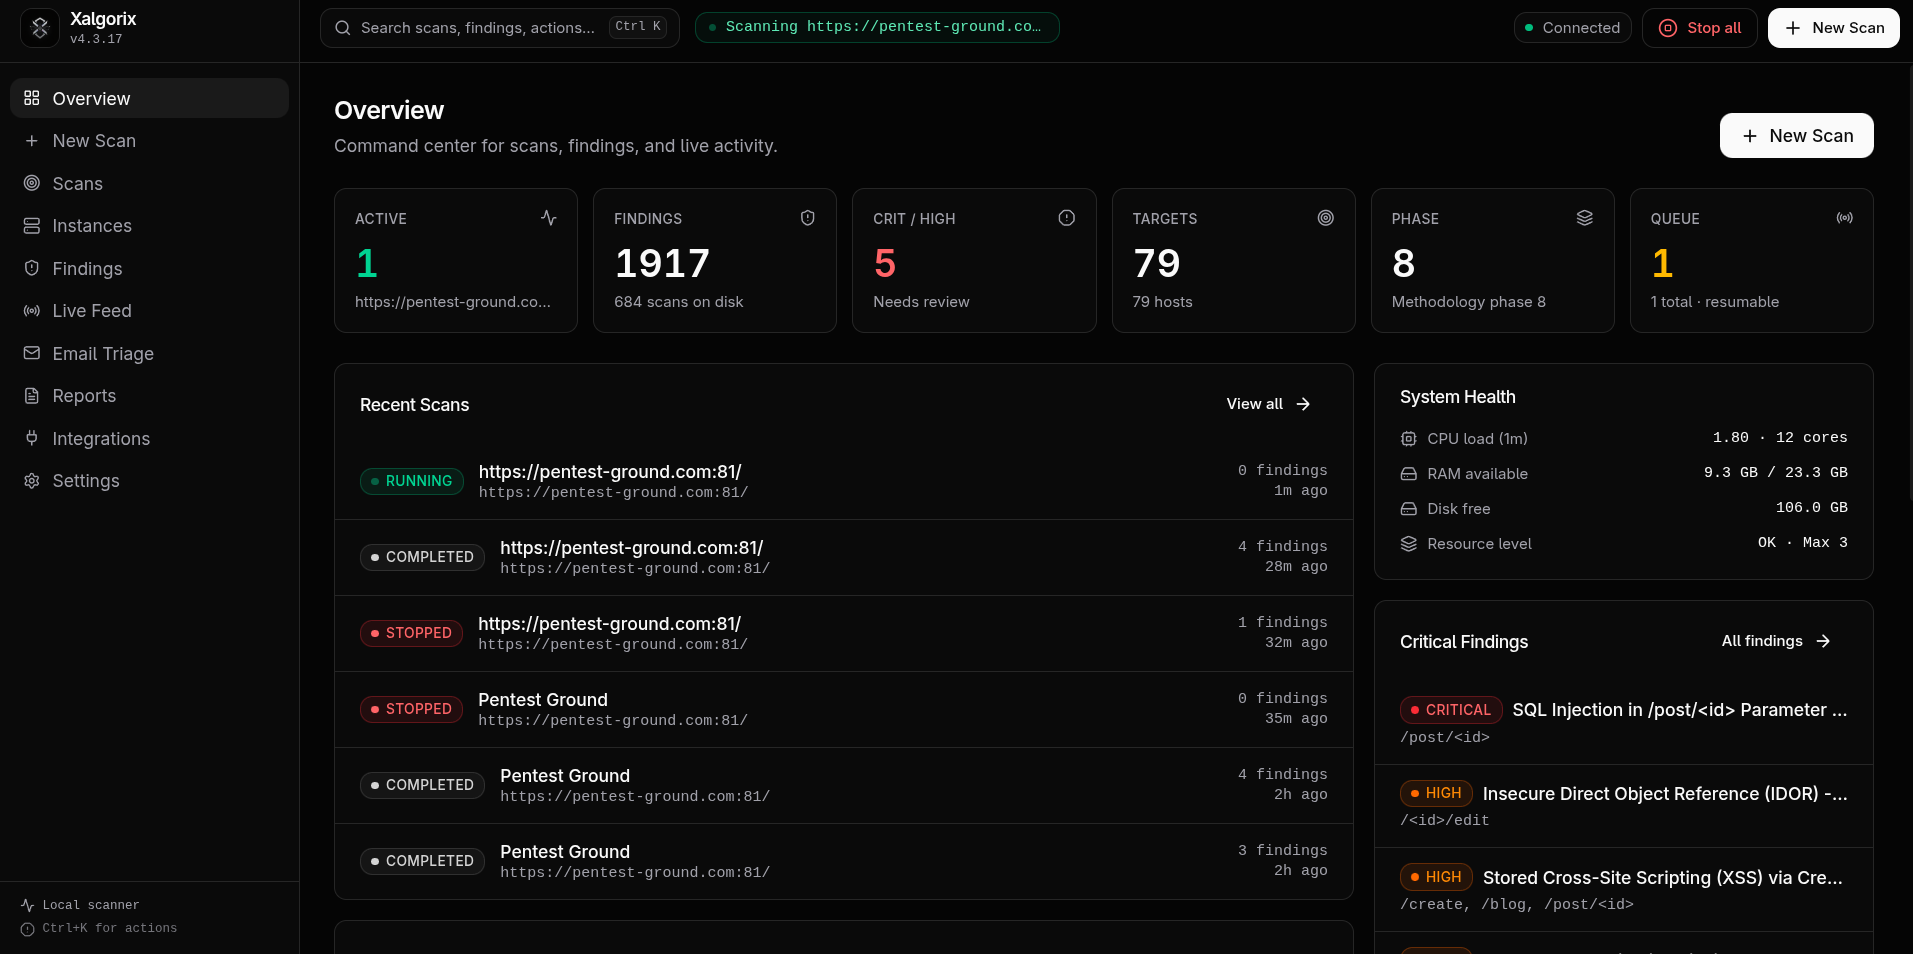
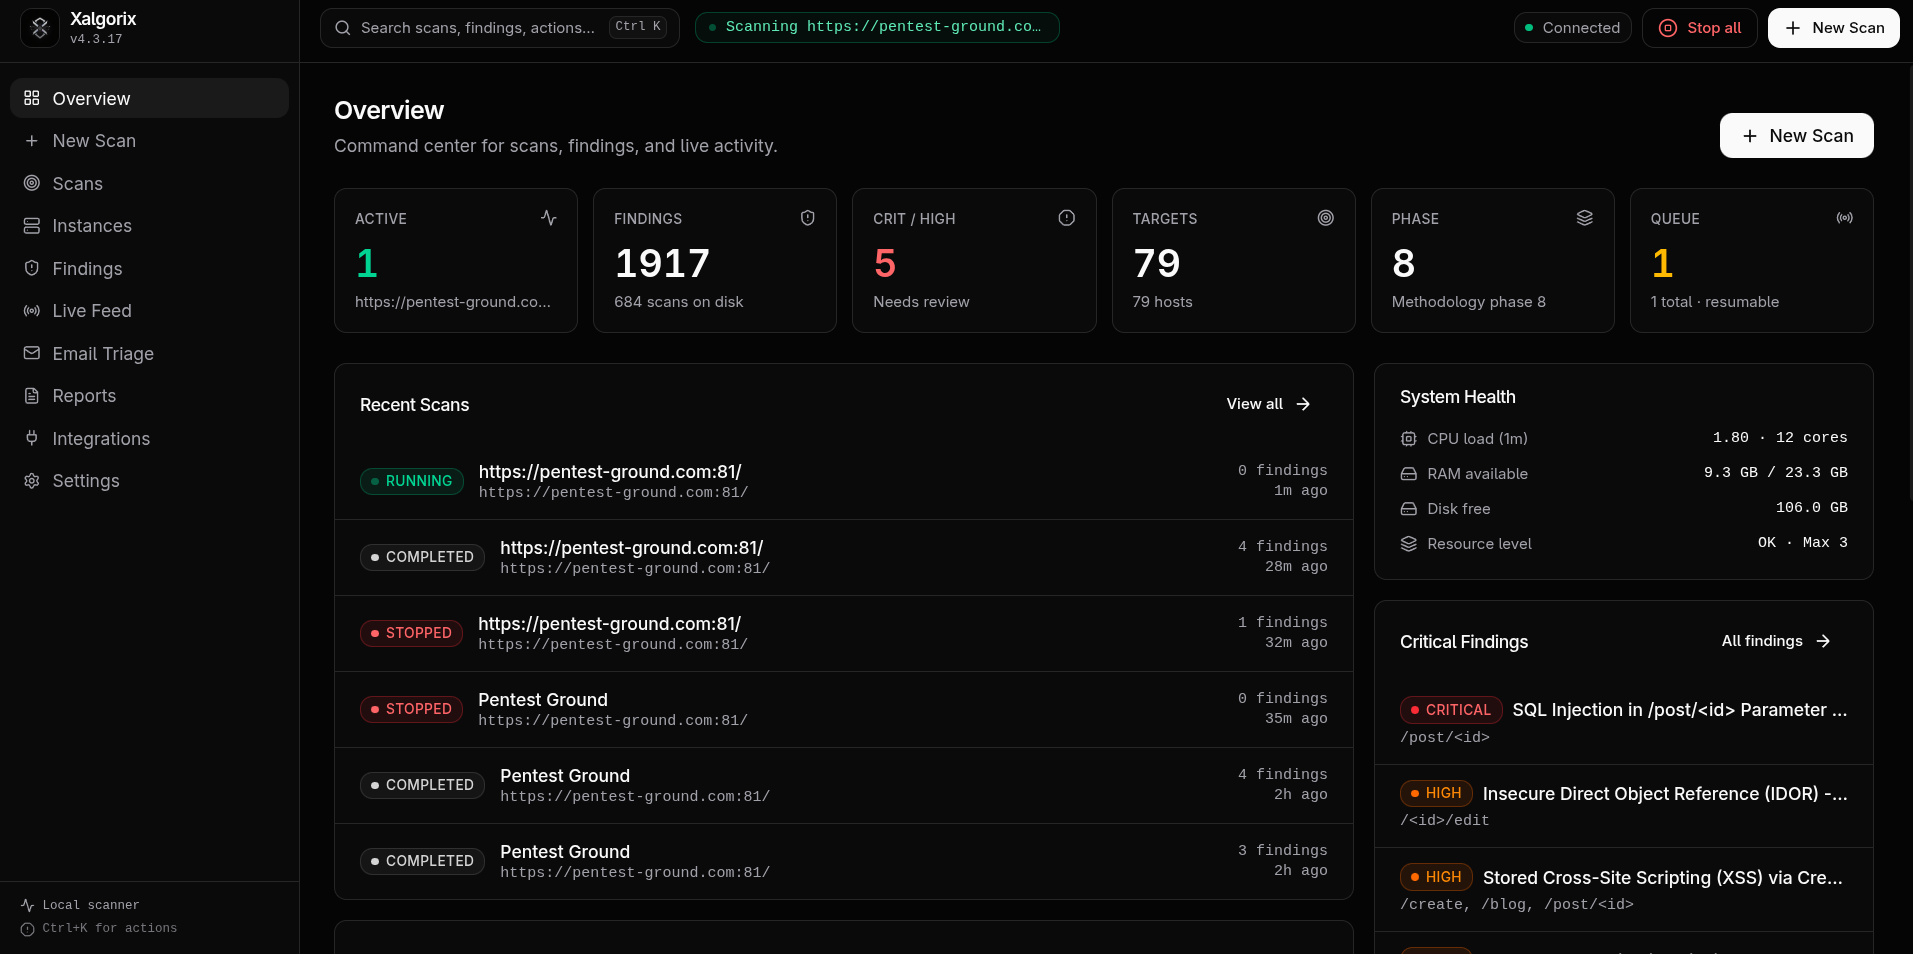
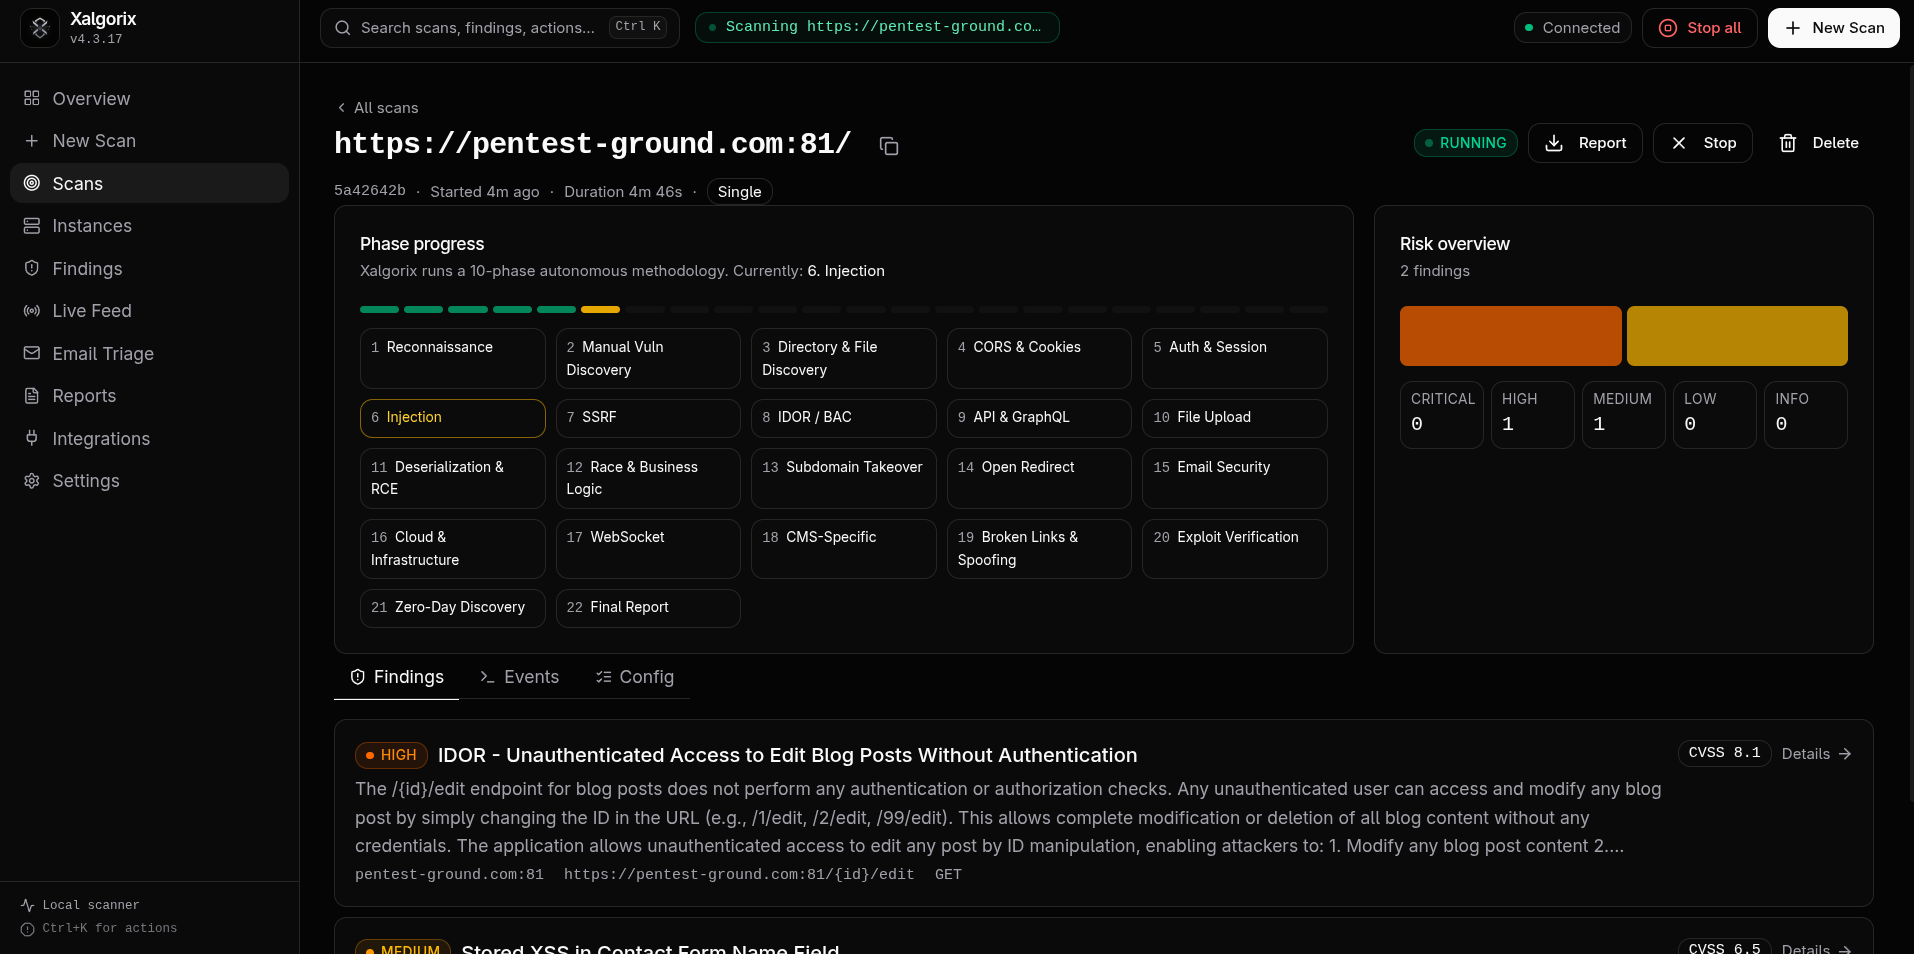
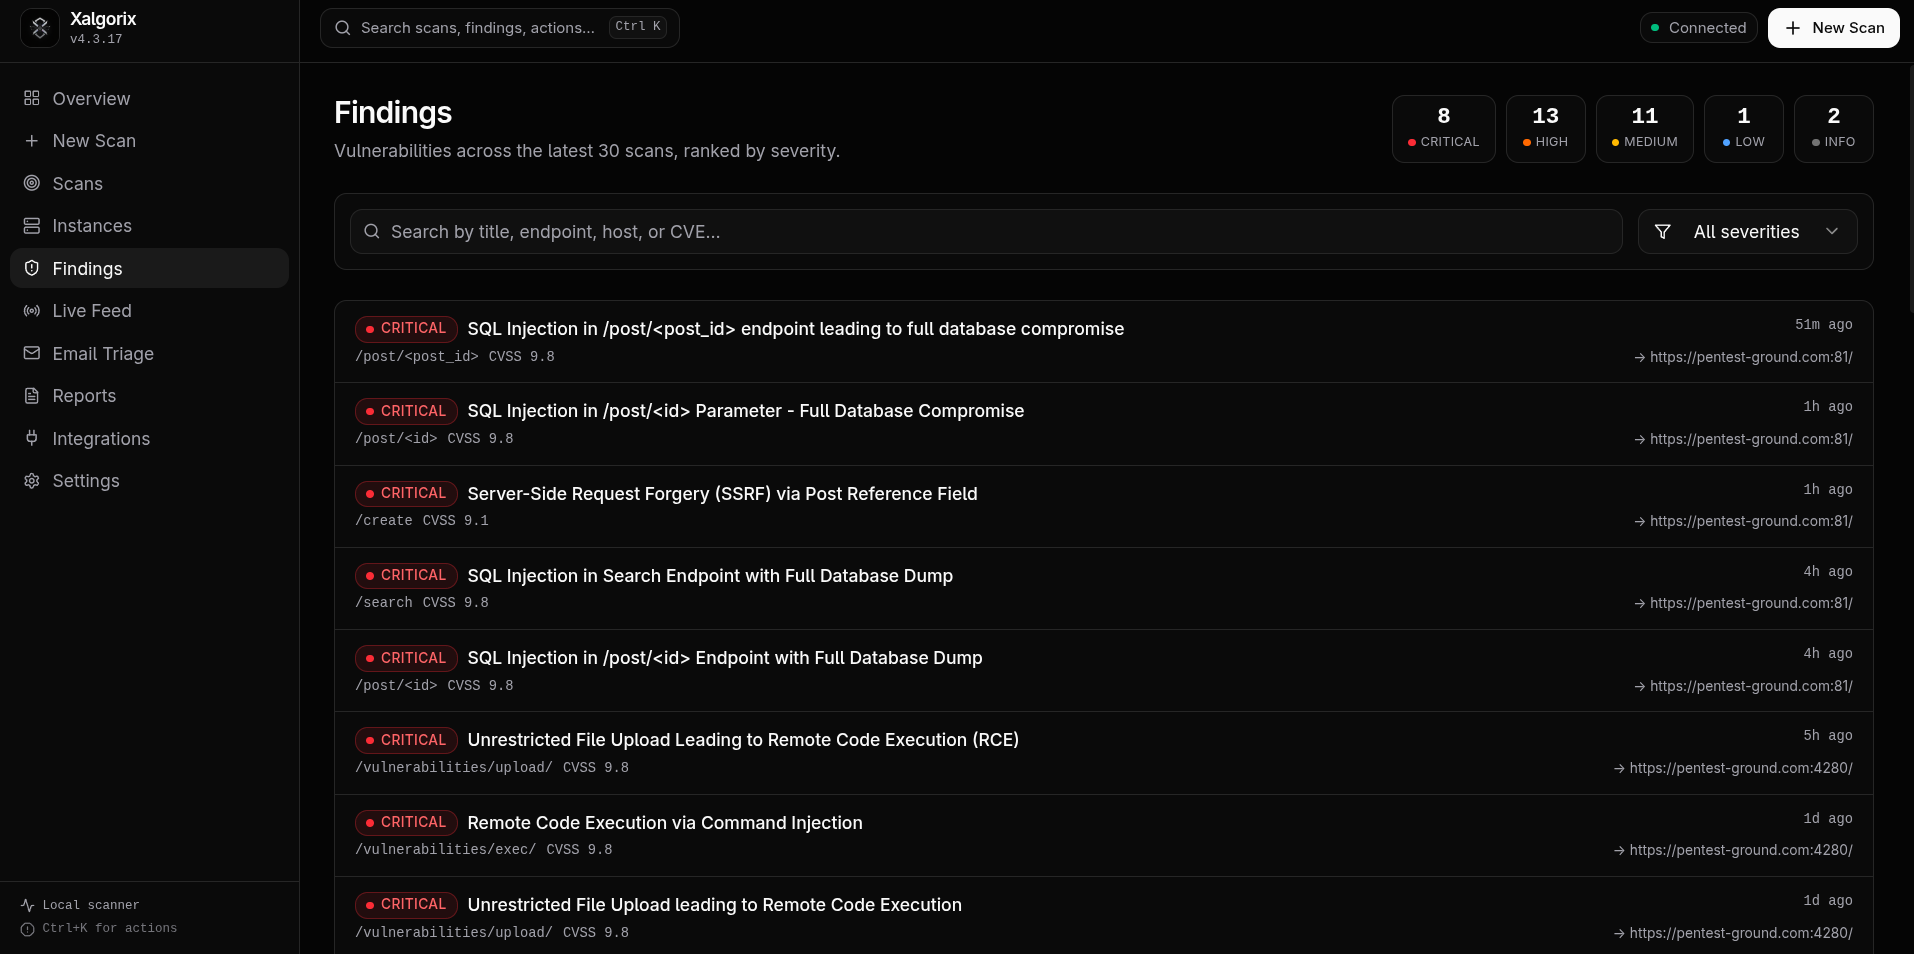
🖥️ Self-hosted dashboard — runs locally on 127.0.0.1:9137
| Overview dashboard | Scan detail | Findings |
|---|---|---|
 |  |  |
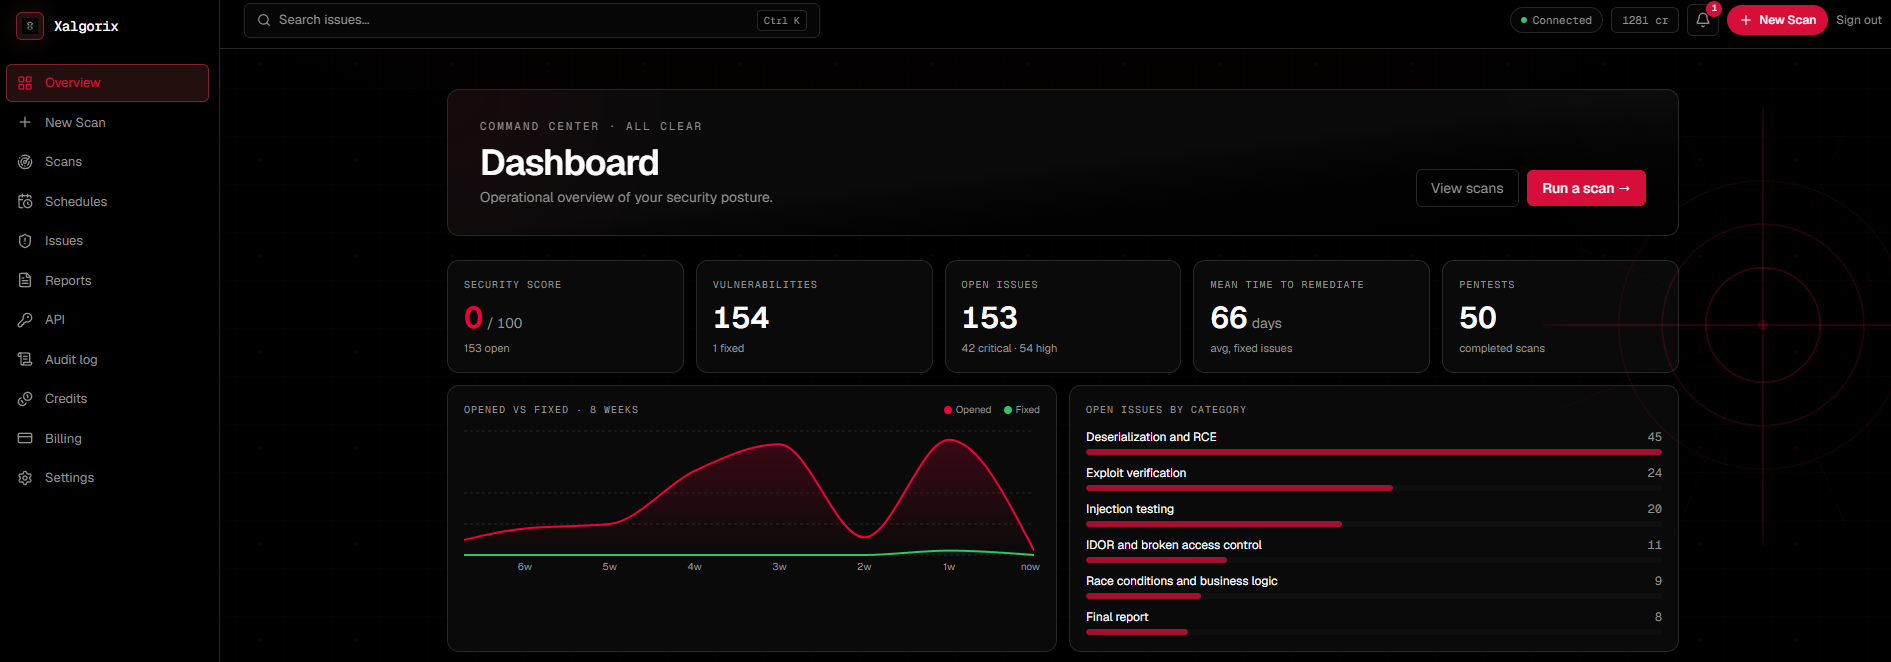
☁️ Xalgorix Cloud dashboard — the managed version at www.xalgorix.com
🤝 Sponsors
Thanks to Swiftproxy for sponsoring Xalgorix.
Your app can behave differently depending on where a request comes from. For Xalgorix users checking their own applications across regions, Swiftproxy offers location targeting to review regional behavior and sticky sessions to help keep a consistent IP during a test session. It supports HTTP(S) and SOCKS5, the same proxy protocols Xalgorix supports.
Residential proxies from $0.70/GB. Free testing is available, and Xalgorix users get 10% off with code PROXY90.
Explore Swiftproxy and request a free test →
🚀 Quick Start
Install (one line):
curl -sSL https://www.xalgorix.com/install | bash
This downloads the prebuilt binary for your platform (Linux or macOS, amd64/arm64) from the latest release.
Or install with Go 1.26 or newer:
go install github.com/xalgord/xalgorix/v4/cmd/xalgorix@latest
Ensure $(go env GOPATH)/bin (or your GOBIN) is on your PATH before running xalgorix.
Then run the interactive setup wizard:
xalgorix --setup
Choose your provider, confirm a model, and enter the API key when prompted. For best results, use a current frontier model with strong reasoning, long-context performance, and reliable tool calling—such as the latest capable GPT, Claude, or Gemini model available to you. Smaller or local models remain supported, but may require more supervision during long autonomous scans. Xalgorix stores the key privately in ~/.xalgorix.env (mode 0600) and can launch the dashboard for you. Local Ollama needs no API key.
If you choose not to launch immediately, start later with xalgorix --web and open http://127.0.0.1:9137. You can change providers or advanced options at any time under Settings → LLM, or rerun xalgorix --setup.
Or run with Docker — batteries included, no toolchain needed:
docker run --rm -p 9137:9137 \
  --privileged \
  -v xalgorix-data:/data \
  xalgord/xalgorix:latest
--privileged gives the toolset the same host-like access it has when run natively as root. Docker's default sandbox drops capabilities (like NET_ADMIN) and applies a seccomp filter, which breaks low-level tools (iptables/route changes, ARP-spoof/MITM, tun/tap VPNs, ptrace-based debuggers, masscan interface tuning). Since an image can't grant itself these, they must be set at run time. The container is a disposable, network-isolated scanning sandbox running as root — privileged is the intended posture; never expose the dashboard publicly without auth. Prefer least-privilege? Swap --privileged for --cap-add=NET_ADMIN --cap-add=NET_RAW --cap-add=SYS_PTRACE --security-opt seccomp=unconfined.