

Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
श्रेणियाँ

उपयोगिताएँ और फ्रेमवर्क

विभिन्न साइबर सुरक्षा कार्यप्रवाहों और कार्यों का समर्थन करने वाले सामान्य-उद्देश्यीय उपकरण, फ्रेमवर्क और वातावरण।

Kitploit अनुशंसित

शीर्ष उपकरण

10 चयनित
CyberChef preview#1

CyberChef

GitHubgchq/cyberchef
35.6k14 दिन पहले
SecLists preview#2

SecLists

GitHubdanielmiessler/seclists
72.8k0 दिन पहले
gf preview#3

gf

GitHubtomnomnom/gf
2.1k6 साल पहले
qsreplace preview#4

qsreplace

GitHubtomnomnom/qsreplace
8844 साल पहले
anew preview#5

anew

GitHubtomnomnom/anew
1.7k4 साल पहले
unfurl preview#6

unfurl

GitHubtomnomnom/unfurl
1.3k4 साल पहले
httprobe preview#7

httprobe

GitHubtomnomnom/httprobe
3.1k4 साल पहले
httpx preview#8

httpx

GitHubprojectdiscovery/httpx
10.3k39 मिनट पहले
nuclei preview#9

nuclei

GitHubprojectdiscovery/nuclei
30.4k13घं 55मि पहले
scapy preview#10

scapy

GitHubsecdev/scapy
12.5k15घं 28मि पहले
नवीनतमप्रासंगिकतासबसे लोकप्रियहाल ही में अपडेट किया गया
3567 परिणाम
joro preview

joro

GitHubbishopfox/joro

एक सहयोगी वेब शोषण फ्रेमवर्क।

penetration-testing-frameworksexploit-frameworkspayload-generation+5
3019 दिन पहले
owasp-ctf-in-a-box preview

owasp-ctf-in-a-box

GitHubowasp/owasp-ctf-in-a-box

Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies

container-securityvulnerability-analysissecurity-virtualization+6
2420घं 59मि पहले
chef-mysql-hardening preview

chef-mysql-hardening

GitHubdev-sec/chef-mysql-hardening

यह chef cookbook mysql के लिए सुरक्षा कॉन्फ़िगरेशन प्रदान करता है।

defensive-toolsscripting-automationconfiguration-auditing+3
271 महीना पहले
Remote-BOF-Runner preview

Remote-BOF-Runner

GitHubpard0p/remote-bof-runner

Remote BOF Runner, Beacon Object Files (BOFs) के दूरस्थ निष्पादन के लिए Crystal Palace के साथ बने PIC लोडर का उपयोग करने वाला एक Havoc विस्तार ढांचा…

penetration-testing-frameworksprivilege-escalationexploit-frameworks+8
10210 महीने पहले
cve-2026-85706 preview

cve-2026-85706

GitHubguneykabel/cve-2026-85706

CVE-2026-85706 के लिए Python PoC exploit, जो Workhorse path-encoding bypass के माध्यम से GitLab CE/EE में unauthenticated arbitrary file read है, साथ…

vulnerability-analysisexploitationweb-application-exploitation+4
452 महीने पहले
mythic_ornn preview

mythic_ornn

GitHubn0qword/mythic_ornn

LLM-संचालित जनरेटर Mythic Agents, Payload-Type और C2 Profiles के लिए।

penetration-testing-frameworksexploit-frameworkscommand-and-control+3
562 महीने पहले
c2 preview

c2

GitHubaveragesecurityguy/c2

एक सरल, विस्तारणीय C&C बीकनिंग प्रणाली।
exploit-frameworksnetwork-securitypenetration-testing+3
1048 साल पहले
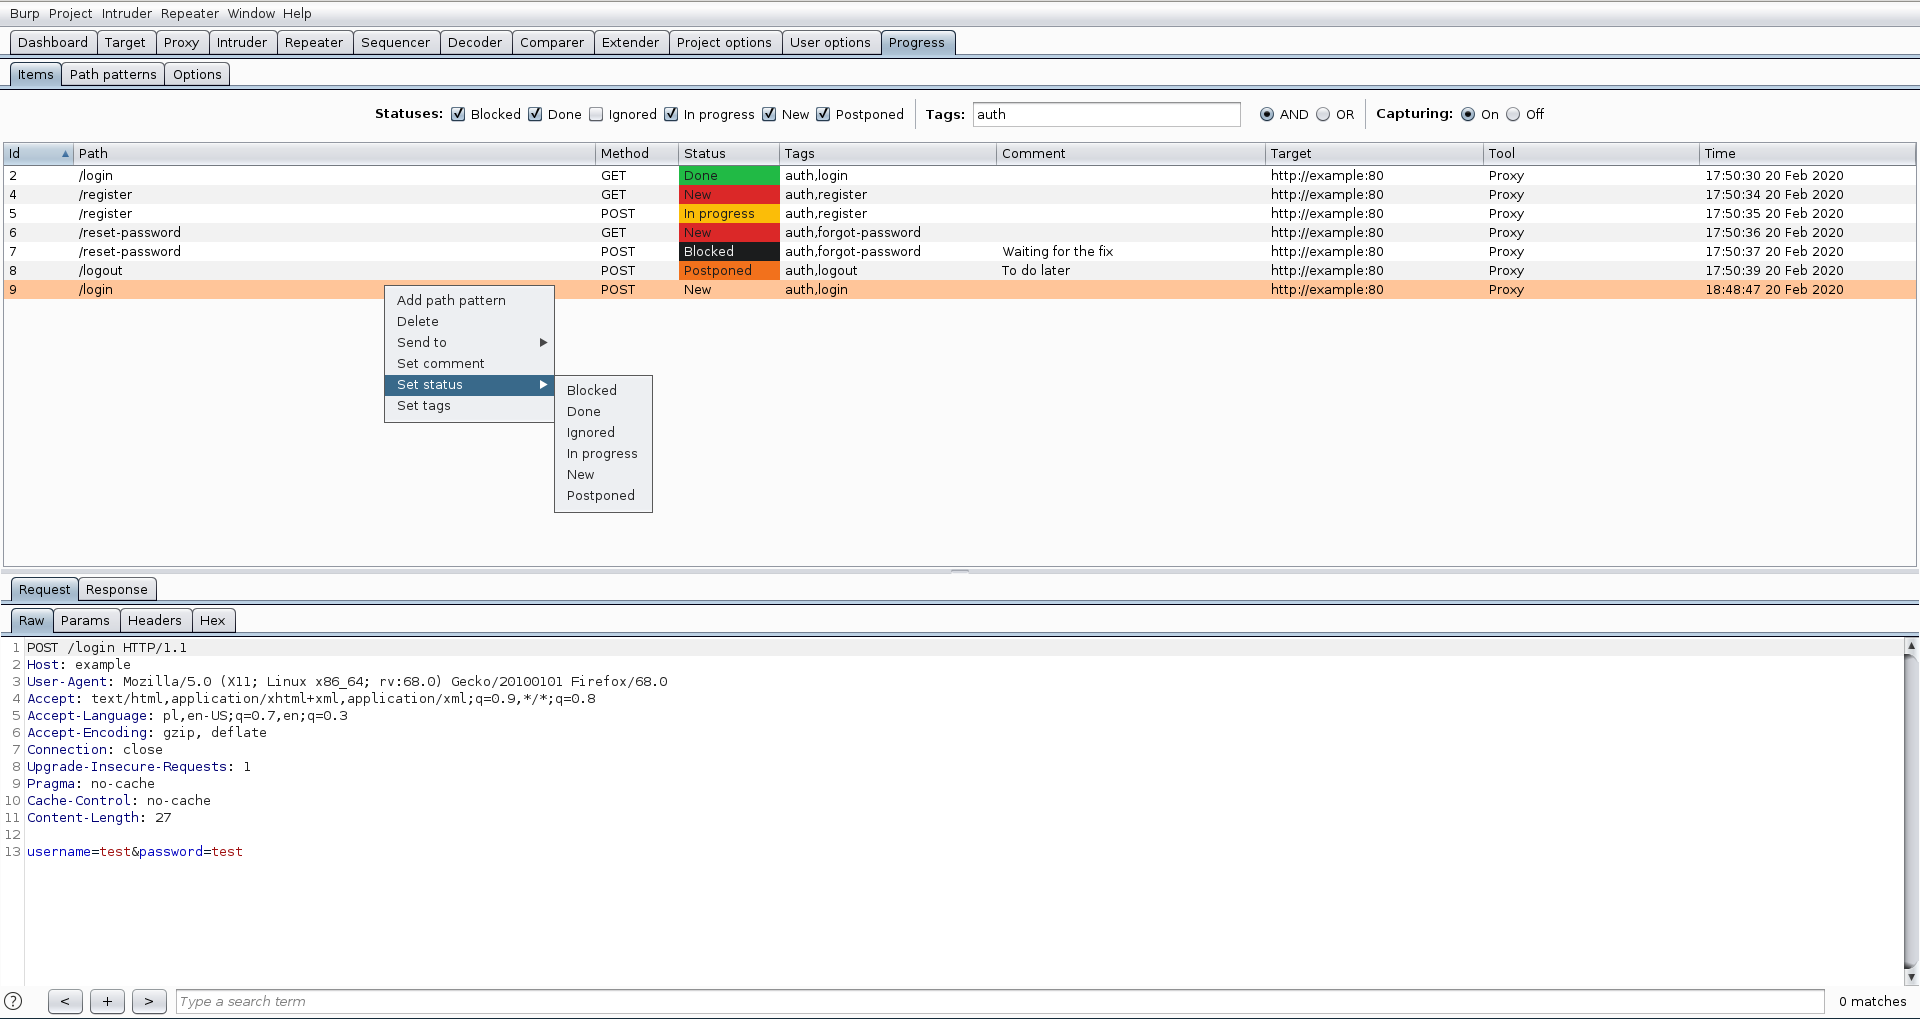
progress-burp preview

progress-burp

GitHubdariusztytko/progress-burp

Burp Suite एक्सटेंशन जो भेद्यता मूल्यांकन प्रगति को ट्रैक करता है

vulnerability-analysisweb-securitypenetration-testing+1
596 साल पहले
WmiExec preview

WmiExec

GitHubonescripter/wmiexec

WMI और PowerShell (रिमोटिंग नहीं) का उपयोग करके दूरस्थ रूप से Windows कमांड निष्पादित करें और आउटपुट कैप्चर करें।

lateral-movementscripting-automationpost-exploitation+5
662 साल पहले
envy preview

envy

GitHubxenoncyber/envy

टर्मिनल आधारित उपकरण जो रहस्यों के प्रबंधन के लिए है और इसमें tui और cli दोनों का समर्थन है।

authentication-authorizationencryption-decryption-toolscloud-security+3
718 महीने पहले
Red-Team-GOAD-Lab-Proxmox preview

Red-Team-GOAD-Lab-Proxmox

GitHubpho5nix/red-team-goad-lab-proxmox

Red Teaming होम लैब के लिए बिल्ड गाइड। Proxmox और pfSense में GOAD लैब सेटअप, Operator/C2 और Redirectors।

defensive-toolspost-exploitationsecurity-virtualization+7
521 महीना पहले
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

यूनिवर्सल विंडोज़ एक्सट्रैक्शन टूल जो अज्ञात फ़ाइलों का पता लगाता है और उन्हें सही बंडल किए गए एक्सट्रैक्टर तक पहुँचाता है।

disk-forensicsmemory-forensicsreverse-engineering+8
3516 दिन पहले
Uchihash preview

Uchihash

GitHubn1ght-w0lf/uchihash

मैलवेयर एम्बेडेड हैश से निपटने के लिए एक छोटी उपयोगिता।

hash-analysisreverse-engineeringscripting-automation+2
523 साल पहले
AgrusScanner preview

AgrusScanner

GitHubnybaywatch/agrusscanner

Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…

defensive-toolsreconnaissancevulnerability-scanners+6
411 दिन पहले
LazyPorts preview

LazyPorts

GitHubv9mirza/lazyports

lazyports एक टर्मिनल UI उपकरण है जो नेटवर्क पोर्ट्स को देखने और प्रबंधित करने के लिए है। यह listening प्रक्रियाओं का निरीक्षण करने और उन्हें आसानी से…


general-purpose-utilitiesnetwork-mappingport-scanning+1
957 महीने पहले
kali-packer preview

kali-packer

GitLabkalilinux/build-scripts/kali-packer

हल्के, पुनरुत्पादनीय और पोर्टेबल विकास वातावरण बनाएँ और कॉन्फ़िगर करें Kali के HashiCorp Packer कॉन्फ़िगरेशन, Kali HashiCorp Vagrant बॉक्स बनाने के…

general-purpose-utilitiessecurity-virtualizationpenetration-testing
477 महीने पहले
CVE-2024-3094-checker preview

CVE-2024-3094-checker

GitHubfabiobaroni/cve-2024-3094-checker

यह जांचने के लिए एक त्वरित और सरल PoC कि xz-utils का कोई असुरक्षित संस्करण स्थापित है या नहीं (CVE-2024-3094)

vulnerability-scannersvulnerability-analysisscripting-automation+2
722 साल पहले
PyStegosploit preview

PyStegosploit

GitHubcharmve/pystegosploit

PoC - स्टेग्नोग्राफी और पॉलीग्लॉट्स के माध्यम से शोषण वितरण, CVE-2014-0282

exploit-frameworksweb-application-exploitationsteganography+5
532 साल पहले
पिछला1…838485…100अगला








