#1
लक्ष्यों के बारे में जानकारी इकट्ठा करने और हमले के सतहों की पहचान करने के उपकरण।
Kitploit अनुशंसित

 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 mandiant/goresym
Go बाइनरीज़ को पार्स करके सिंबल्स, फ़ंक्शन मेटाडेटा, टाइप्स, फ़ाइल पाथ्स और एम्बेडेड स्ट्रिंग्स को पुनः प्राप्त करता है, जिसमें स्ट्रिप्ड या…
 oscerd/cve-2026-84180
CVE-2026-84180 के लिए रन करने योग्य Spring Boot और Quarkus रिप्रोड्यूसर, जो camel-knative HTTP कंज़्यूमर अपवाद लीकेज को प्रदर्शित करते हैं और…
 oscerd/cve-2026-85246
CVE-2026-85246 के लिए रन करने योग्य Spring Boot रिप्रोड्यूसर, जो सॉकेट पर camel-mina कंज़्यूमर अपवाद प्रकटीकरण का प्रदर्शन करता है और muteException…
 emrekybs/veiled-eye
OSINT पहचान जाँच उपकरण। किसी ई-मेल, उपयोगकर्ता नाम, फ़ोन या वॉलेट से 46 स्रोतों में एक प्रोफ़ाइल और संबंध ग्राफ़ में पिवट करें।
 tridents10/vader-pro-vdr
AI-सहायता प्राप्त भेद्यता पहचान और निवारण प्लेटफ़ॉर्म, जिसमें एक Go एंडपॉइंट एजेंट, केंद्रीकृत डैशबोर्ड और भेद्यता इंटेलिजेंस इंजन शामिल है।
 abraxas/openmeetings-calendar-save-idor
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - LOGIN calendar save overwrites appointment and closes public room
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 gmh5225/mirage
Rust में माइक्रोसर्विस OSINT प्लेटफ़ॉर्म जो खतरे की खुफिया जानकारी और हमले की सतह मैपिंग के लिए खुफिया जानकारी एकत्र करने, सहसंबंधित करने और…
 abraxas/jellyfin-playlist-itemids
Jellyfin Server 12.2 - उच्च - रिमोट - IDOR - सार्वजनिक प्लेलिस्ट ItemIds GHSA-9x85 का अवशेष, फिर अनधिकृत स्ट्रीम
 abraxas/jellyfin-suggestions-idor
Jellyfin Server 12.2 - उच्च - रिमोट - IDOR - GET /Items/Suggestions omit-userId छिपी हुई लाइब्रेरी Path और IDs को डंप करता है
 abraxas/jellyfin-svg-gzip
Jellyfin Server 12.2 - उच्च - रिमोट - SSRF - gzip data:image/png GHSA-cf3c का अवशेष अभी भी http और file प्राप्त करता है
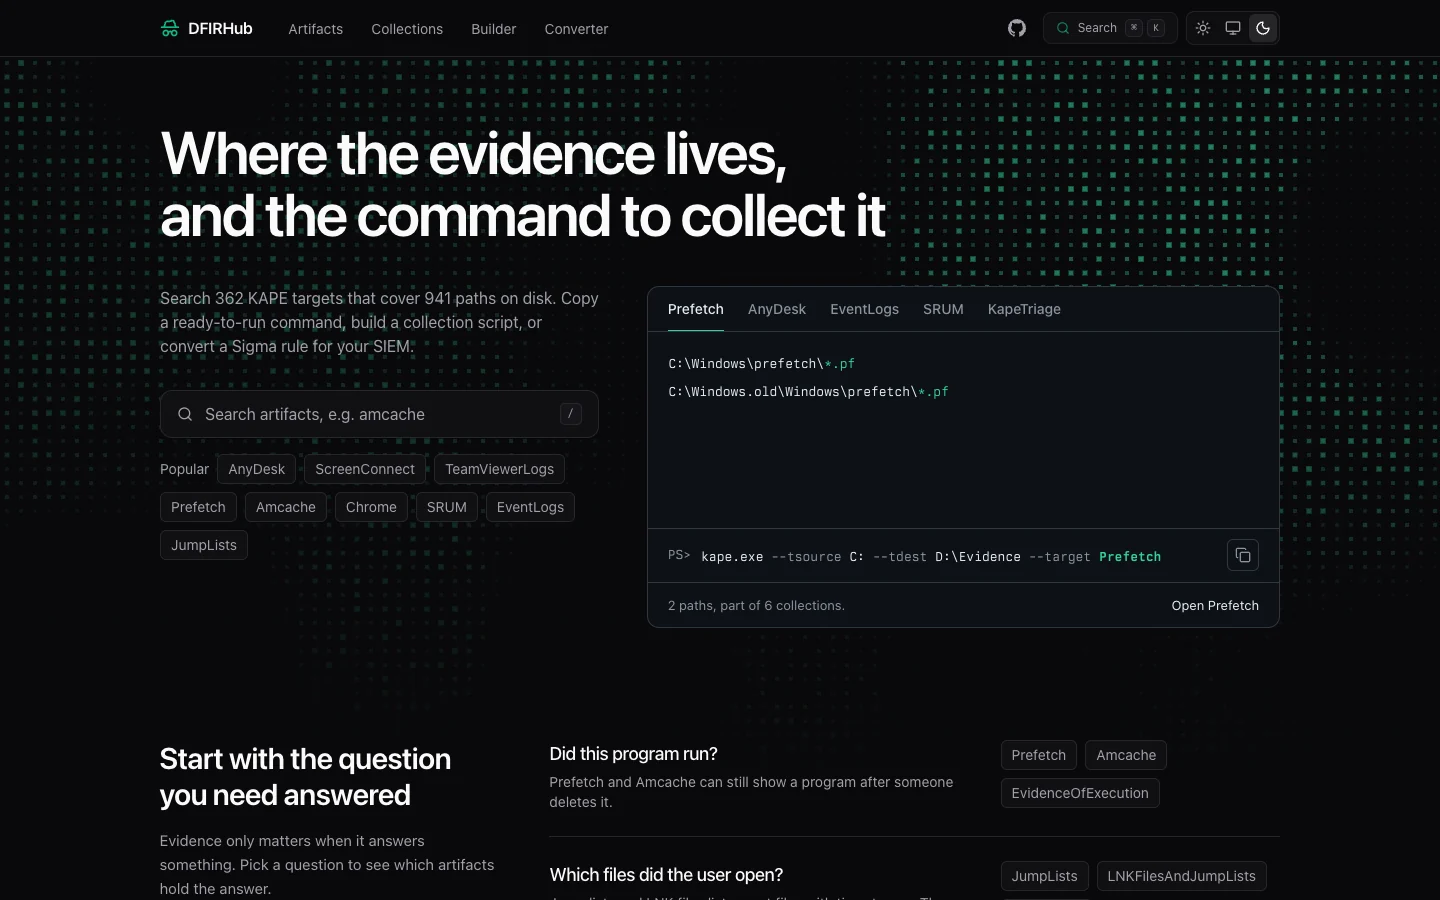 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
x64dbg के साथ Amadey Loader का रिवर्स इंजीनियरिंग: डायनामिक API रिज़ॉल्यूशन, टोकन विशेषाधिकार वृद्धि, कीलॉगर हुक, क्लिपबोर्ड कैप्चर, और स्टीलर…
 abraxas/openmeetings-invite-recording-acl
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - Type.USER invitation recording MP4 ACL
 abraxas/openmeetings-kms-unauth
Apache OpenMeetings 9.1.0 - High - Remote - Unauth KMS - docs docker publishes Kurento JSON-RPC on 8888
 abraxas/openmeetings-wb-fileid-idor
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - WHITEBOARD fileId plant then room file resource serves bytes
 oscerd/cve-2026-78164
CVE-2026-78164 के लिए रन करने योग्य प्रूफ-ऑफ-कॉन्सेप्ट, जो यह प्रदर्शित करता है कि Apache Camel HTTP प्रोड्यूसर द्वारा हमलावर-आपूर्ति किए गए…